

INTRODUCTION
The Grandstream GWN781x, GWN782x, and GWN783x series include managed network switches designed for scalable, secure, and high-performance business networks. The series covered by this manual provide the following capabilities:
- GWN781x Series: Layer 3 managed switches, providing enhanced routing capabilities for medium-to-large enterprises.
- GWN782x Series: Layer 3 multi-gigabit switches, suited for medium-to-large businesses requiring high data throughput and advanced network management.
- GWN783x Series: Aggregation switches, designed for enterprises needing high-capacity, scalable infrastructure for large network environments.
All models covered by this manual support advanced VLAN for flexible traffic segmentation, QoS for network traffic prioritization, IGMP/MLD Snooping for performance optimization, and comprehensive security capabilities. PoE models are available to power IP phones, IP cameras, Wi-Fi access points, and other PoE endpoints.
These switch series can be managed through multiple methods, including a local web user interface, command-line interface (CLI), and integration with Grandstream’s GDMS Networking and GWN Manager platforms, providing complete end-to-end network management options.
Whether deployed in small-to-medium businesses, larger enterprises, or as part of aggregation networks, the GWN781x, GWN782x, and GWN783x series deliver enterprise-grade performance and reliability for diverse network needs.
PRODUCT OVERVIEW
Technical Specifications
Select a switch series below to open its Technical Specifications guide. These guides provide model-specific interfaces, performance, PoE, power, environmental, physical, and compliance information.
| Series | Models | Technical Specifications |
|---|---|---|
| GWN781x | GWN7811(P), GWN7812P, GWN7813(P), GWN7816(P) | GWN781x Series Technical Specifications |
| GWN782x | GWN7821P, GWN7822P | GWN782x Series Technical Specifications |
| GWN783x | GWN7830, GWN7831, GWN7832 | GWN783x Series Technical Specifications |
INSTALLATION
Select the applicable switch model below to open its Quick Installation Guide. Each guide provides package contents, port and LED information, power and network connections, and mounting instructions.
| Series | Models | Quick Installation Guide |
|---|---|---|
| GWN781x | GWN7811(P), GWN7812P, GWN7813(P) | GWN781x(P) Quick Installation Guide |
| GWN7816(P) | GWN7816(P) Quick Installation Guide | |
| GWN782x | GWN7821P, GWN7822P | GWN782xP Quick Installation Guide |
| GWN783x | GWN7830 | GWN7830 Quick Installation Guide |
| GWN7831 | GWN7831 Quick Installation Guide | |
| GWN7832 | GWN7832 Quick Installation Guide |
GETTING STARTED
LED Indicators
The front panels of the GWN781x, GWN782x, and GWN783x switches have LED indicators for power and interface activities, the table below describes the LED indicators’ status.
LED Indicator | Status | Description |
System Indicator | Off | Power off |
Solid green | Booting | |
Flashing green | Upgrade | |
Solid blue | Normal use | |
Flashing blue | Provisioning | |
Solid red | Upgrade failed | |
Flashing red | Factory reset | |
Port Indicator | Off |
|
Solid green | Port connected and there is no activity | |
Flashing green | Port connected and data is transferring | |
Solid yellow | Ethernet port connected, and there is no activity and PoE powered | |
Flashing yellow | Ethernet port connected, data is transferring and PoE powered | |
Alternately flashing yellow and green | Ethernet port failure | |
PWR/RPS Indicator | Off | Uninserted or failure |
Solid Green |
| |
LED Indicators
Access & Configure
Login Using the Console Port
- Use the console cable to connect the console port of switch and the serial port of PC.
- Open the terminal emulation program of PC (e.g. SecureCRT), enter the default username and password to login. (The default administrator username is “admin” and the default random password can be found at the sticker on the switch).
Login Remotely Using SSH
- Enter “cmd” in PC/Start.
- Enter ssh <switch_IP> in the cmd window.
- Enter the default username and password to login. (The default administrator username is “admin” and the default random password can be found at the sticker on the switch).
GWN Switches support also Web CLI.
Configure Using GDMS Networking
Type https://www.gdms.cloud in the browser, and enter the account and password to login the cloud platform. If you don’t have an account, please register first or ask the administrator to assign one for you.
Login Using the Web UI
The switch’s embedded web server responds to HTTPS GET/POST requests. Embedded HTML pages allow users to configure the device through a Web browser such as Microsoft Edge, Mozilla Firefox, or Google Chrome.
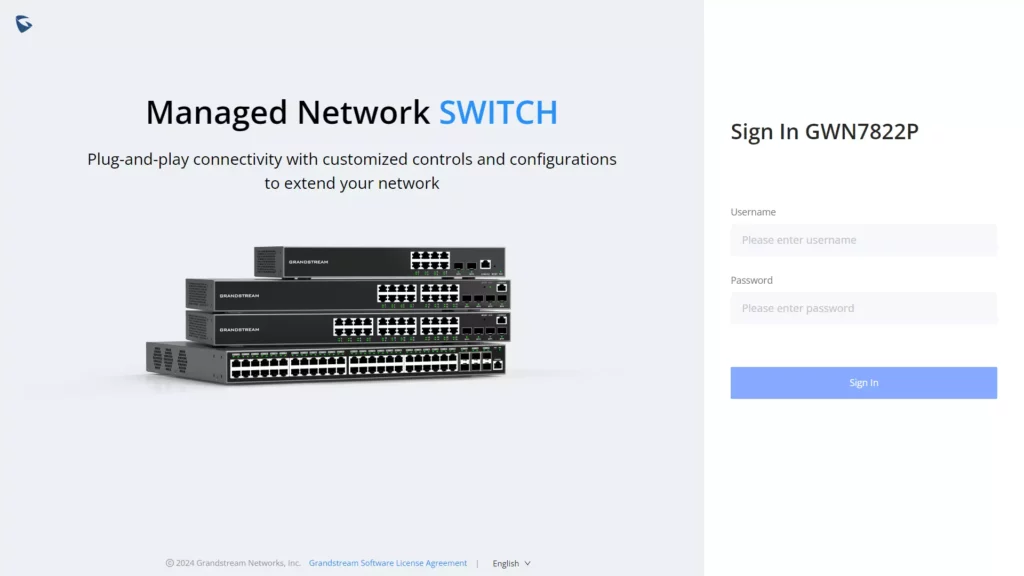
- A PC uses a network cable to correctly connect any RJ45 port of the switch.
- Set the Ethernet (or local connection) IP address of the PC to 192.168.0.x (“x” is any value between 1-253), and the subnet mask to 255.255.255.0, so that it is in the same network segment with switch IP address. If DHCP is used, this step could be skipped.
- Type the switch’s default management IP address https://<switch_IP> in the browser, and enter the username and password to log in. (The default administrator username is “admin” and the default random password can be found at the sticker on the switch).
CLI Access
In addition to the web-based configuration, the switch can also be configured using a Command Line Interface (CLI). For detailed instructions on using the CLI, please refer to the GWN78xx CLI User Guide.
Web GUI Languages
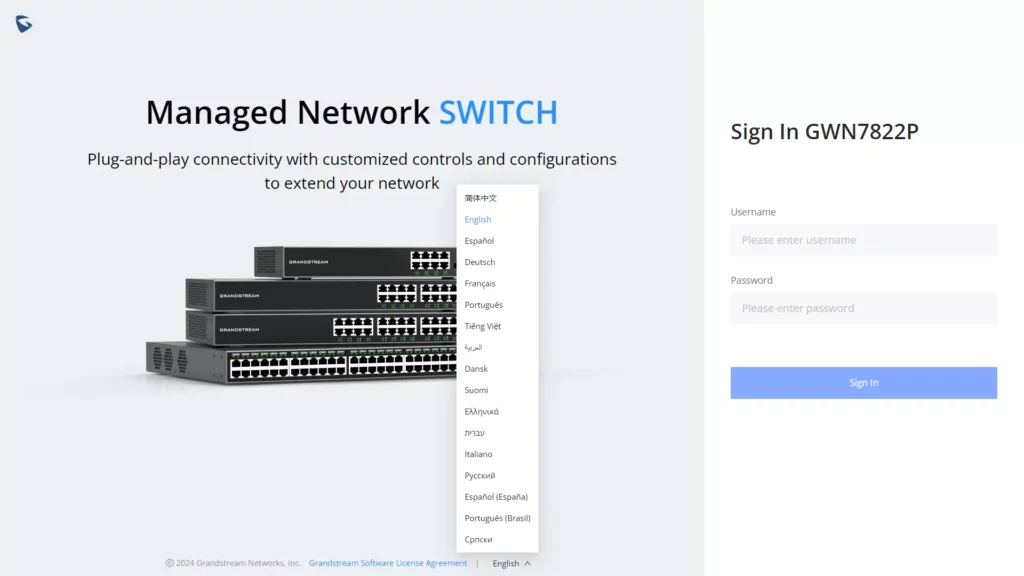
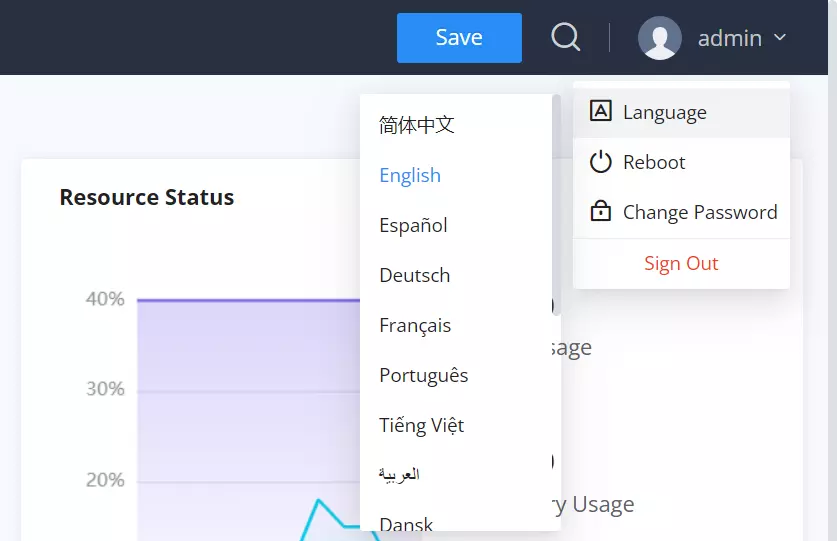
The switch’s web UI supports many languages including English, Simplified Chinese, Spanish, French etc.
To change the default language, select the displayed language at the bottom of the web GUI either before or after logging in.
Search
Use the search function in the switch’s web UI to quickly find configuration pages, settings, and parameters.
On the top of the page, there is a search icon, the user can click on it and then enter the keyword relevant to his search, then he will get all the possible locations of that keyword.
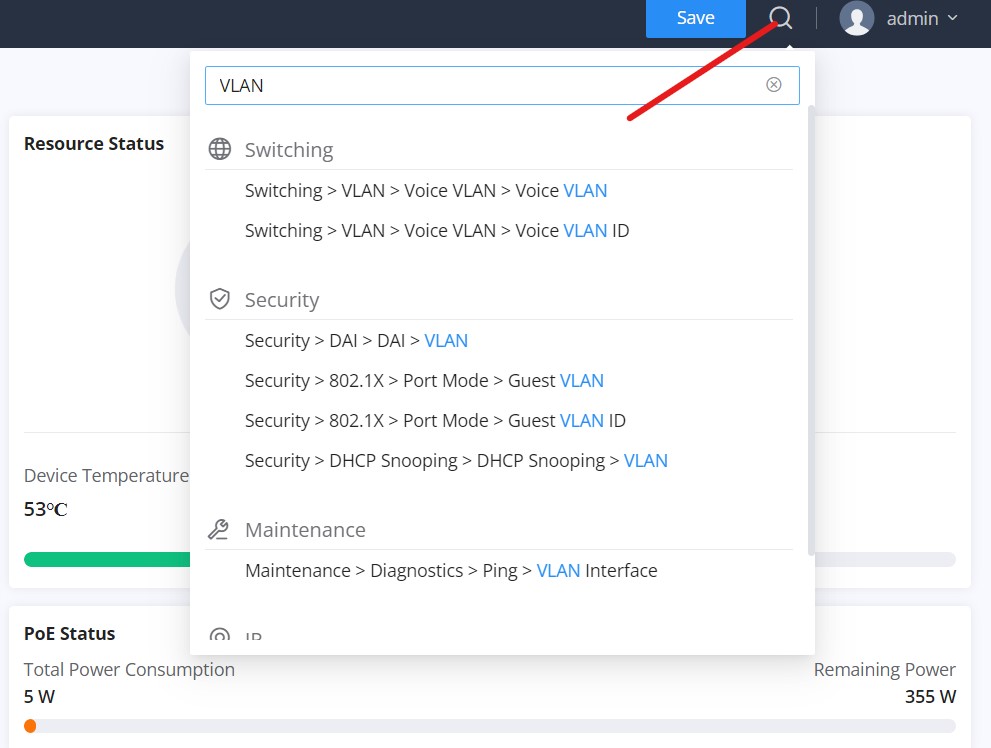
It’s also possible to search through menus and sub-menus, and once the user clicks on the search result, they will jump directly to the specified page, please see the figure below:

OVERVIEW
Overview is the first section that displays System information in the first page “System Info” and Port status on the second page “Port Info”. This section provides an overall view of the switch’s system and port status for easy monitoring.
System Info
System Info is the first page after a successful login to the switch’s web interface. It provides a dashboard view of general switch information, resource status, PoE status, and system events.

To name the device please click on  , then enter the desired name.
Basic Info | Displays Device and System general information that includes (Device name, MAC Address, Default Gateway, System Time, System Version etc.) |
Resource Status | Displays in real time the usage of CPU and Memory. |
PoE Status | Shows the Total Power Consumption and the remaining Power in mA. |
System Events | Diplays the total number of events for each category (Emergency, Alert, Warning etc). Note: Clicking on any events category will redirect you to the Diagnostics page for further details. |
Fan | Displays the fans operation status and speed. |
Power Supply | Shows the status of the built-in power supply as well as the RPS (Redundant Power Supply). |
System Info page
Port Info
This page on the GWN switches provides comprehensive port statistics, PoE power supply information, and detailed port and neighbor information. It helps users monitor network performance and manage connected devices efficiently.
- Port Info
The “Port Info” section visually displays the status and speed of each port, using different colors for speeds and states. Users can quickly identify active, inactive, or problematic ports and their PoE power status.
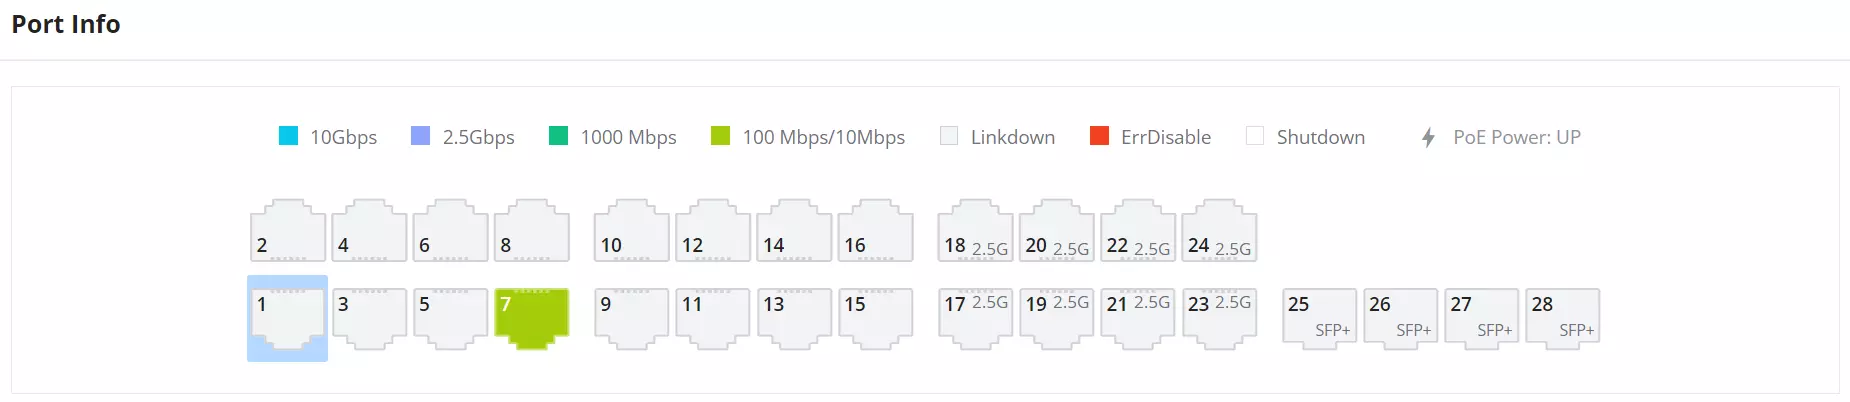
- Basic Info and Neighbor Info
The “Basic Info” section shows specific details for a selected port, including its status and settings. The “Neighbor Info” section provides information about the device connected to the port, such as hostname and current traffic rates.
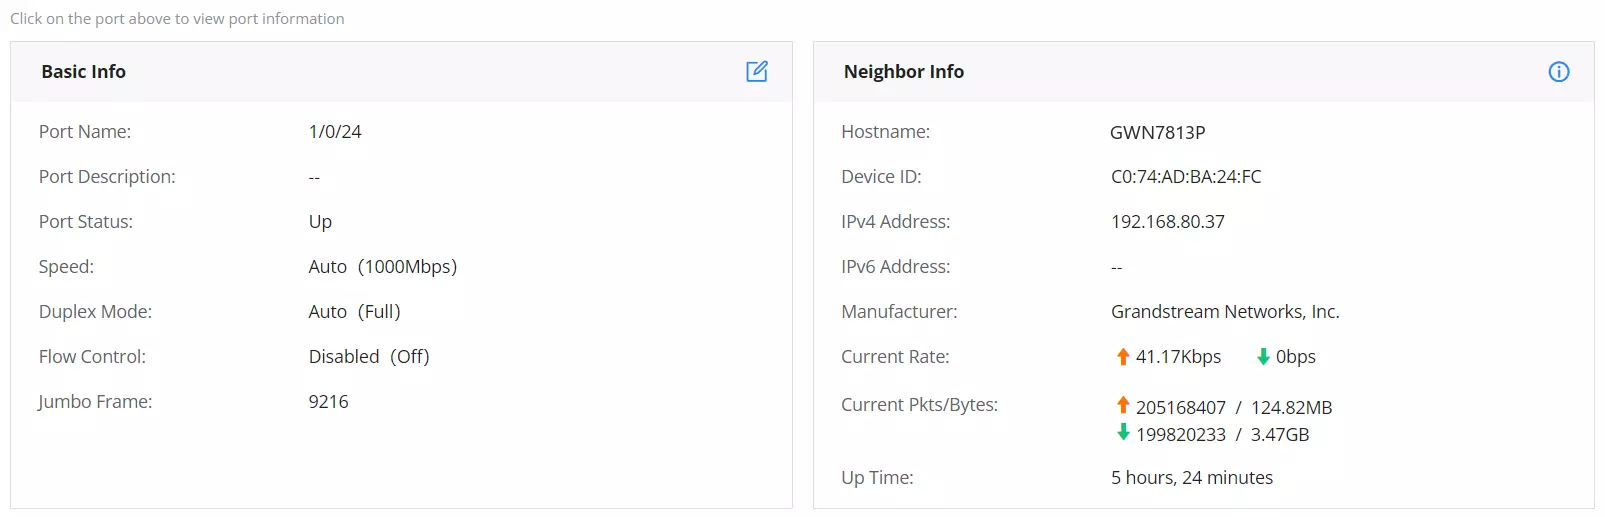
- Statistics
The “Statistics” section offers detailed metrics on network traffic through the switch. It includes data on octets, packets, and discards, which is crucial for monitoring performance and troubleshooting.
- PoE Power Supply / Fiber Info
If the selected port is PoE-capable, the “PoE Power Supply” section shows power supply status and usage. If the port is SFP, the “Fiber Info” section displays details like signal loss, temperature, RX, and TX power.

The following table explains the color mode and the symbols used:
 | Grey: Linkdown |
 | White: shutdown |
 | Green: Ethernet RJ45 port with 1000 Mbps speed |
 | Light green: Ethernet RJ45 port with 100 Mbps/10 Mbps speed |
 | Red: ErrDisable |
 | Green: SFP/SFP+ Port set to 1000Mbps |
 | Purple: SFP Port set to 2.5Gbps |
 | Blue: SFP+ port set to 10Gbps |
 | Symbol: PoE Power is enabled. |
Port Info
Note: a PoE symbol and color code combination is also possible. Ex:  in this case, the port is using 1000 Mbps speed and also using PoE at the same time.
Icons Description:
- Basic Info: The edit icon forwards users to the Port Basic Settings page, where they can modify the port settings such as Description, Speed, Duplex Mode, and Flow Control, or enable/disable the port.
- Neighbor Info: The details icon forwards users to the LLDP/LLDP-MED Neighbor Info page. Here, users can view additional information about the connected devices, including chassis ID, port ID, device name, system description, and survival time.
- PoE Power Supply / Fiber Info: The details icon forwards users to the respective detailed pages. For PoE, it forwards to the PoE Interface page showing detailed information about PoE settings for each port. For Fiber, it forwards to the Fiber Module page, displaying comprehensive fiber details such as signal loss, temperature, RX, and TX power.
- Statistics: The clear icon clears the displayed statistics.
SWITCHING
Switching section is used to configure ports settings, link Aggregation, VLAN, Spanning Tree etc.
Port Basic Settings
On this page, you can configure basic switch-port parameters, including enabling or disabling a port, adding a description, selecting the speed and duplex mode, and configuring flow control. Use the filter to display only copper (Gigabit Ethernet) or fiber (SFP+) ports.
To configure a port, please navigate to Web UI → Switching → Port Basic Settings.
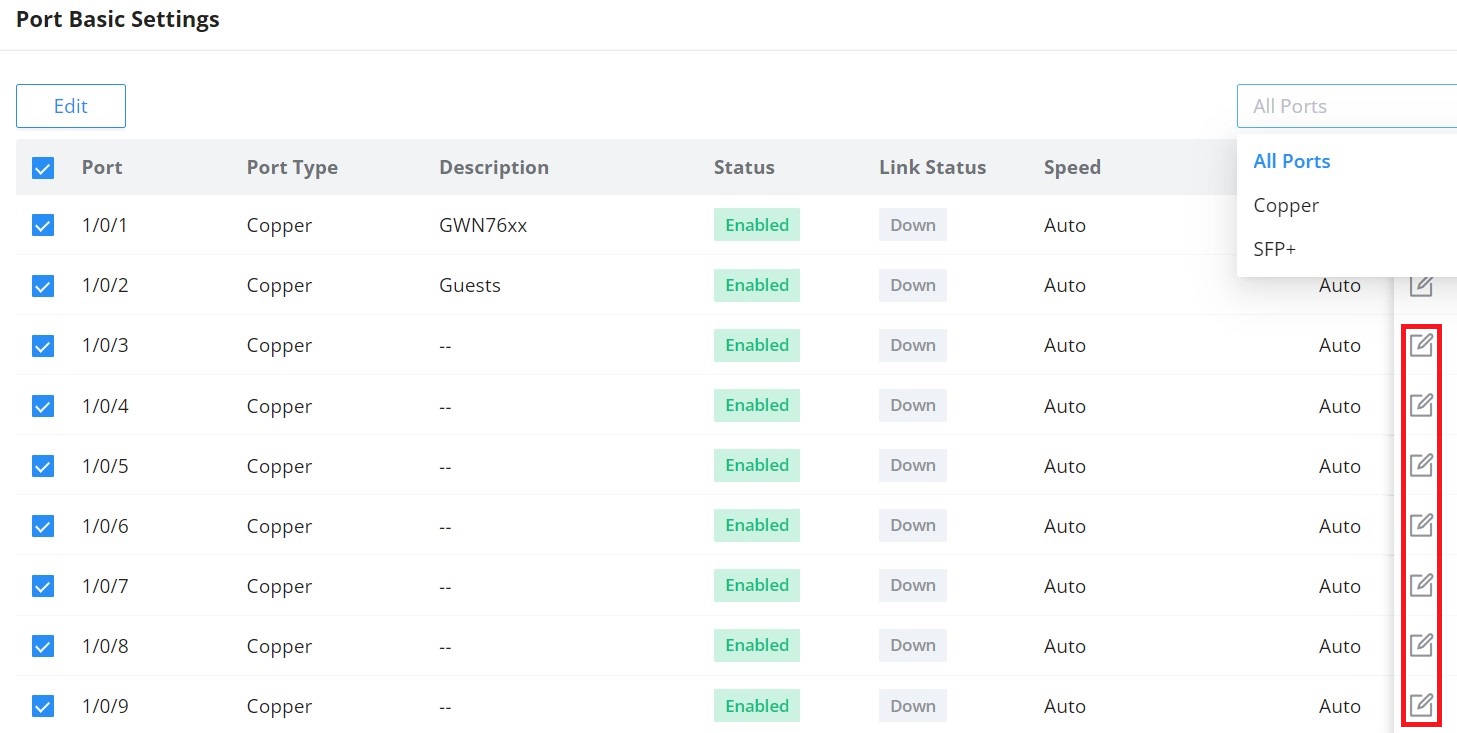
To configure a port, click on the “Edit” icon under the operation column.

Users can define schedules for specific ports, this is to enable precise control over when configurations are applied. These schedules dictate the exact times during which port settings will take effect.
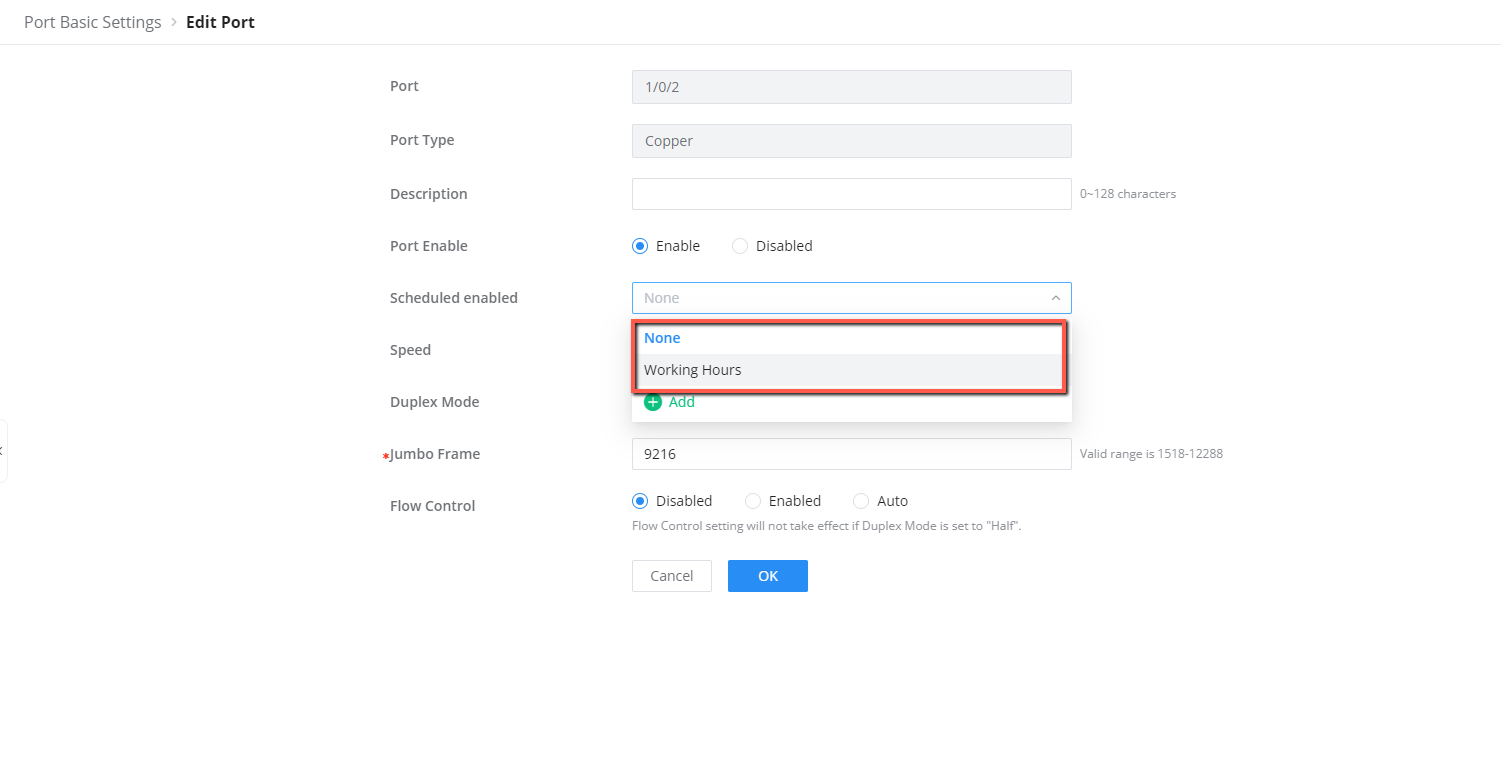
| Setting | Description |
|---|---|
| Port | The selected port to configure. It can be a Gigabit Ethernet port or an SFP port. |
| Port Type | Displays the port type, Copper or SFP. |
| Description | Configures a description for the interface, such as its purpose or connected device. The maximum length is 128 characters. |
| Port Enable | Enables or disables the interface. Enabled by default. |
| Scheduled enabled | Selects the schedule during which the physical port or LAG port is enabled. |
| Speed |
Sets the interface rate.
Notes:
|
| Duplex Mode |
Sets the interface duplex mode. Gigabit Ethernet port options are Auto-negotiation, Full-duplex, and Half-duplex. The default is auto-negotiation.
Notes:
|
| Jumbo Frame | Sets the Jumbo Frame size. The valid range is 1518 to 12288 bytes. The default is 9216 bytes. |
| Flow Control | Sets flow control to Disabled, Enabled, or Auto. The default is Disabled. When flow control is enabled and congestion occurs, the device can notify its peer to pause packet transmission temporarily to help prevent packet loss. Note: Optical ports do not support auto-negotiation mode. |
Port Group
The port group feature allows administrators to logically bundle specific ports together under one group with a corresponding group ID, this can be useful when classifying the switch ports for identifying the usage of each set of ports, for example, ports 1 to 8 can be set with ID 20, these will be the ports connecting Security devices.
Port group settings can facilitate quick batch settings for port group ports.
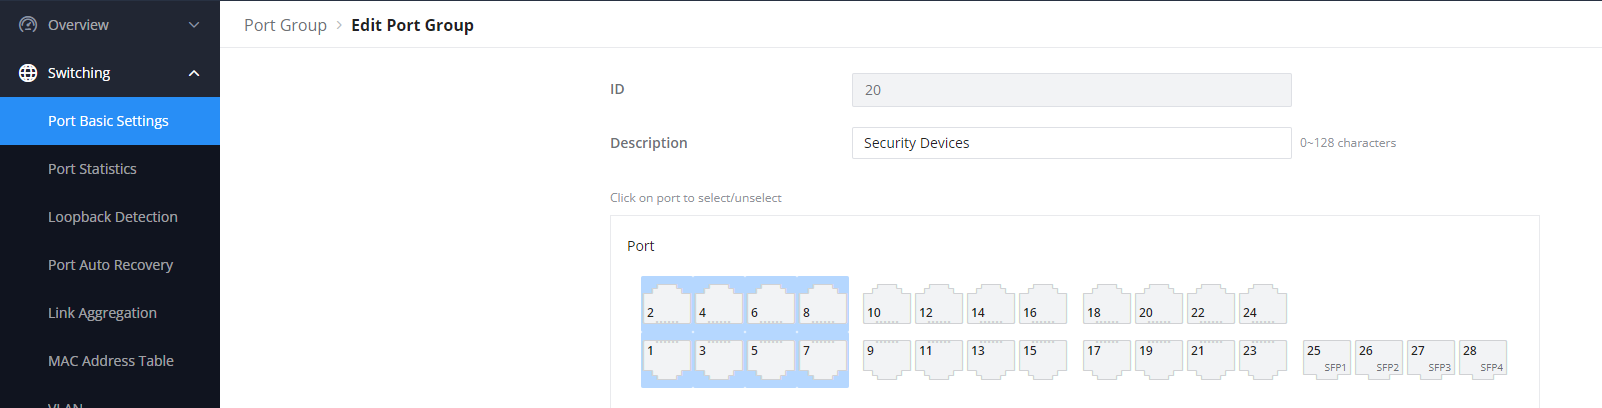
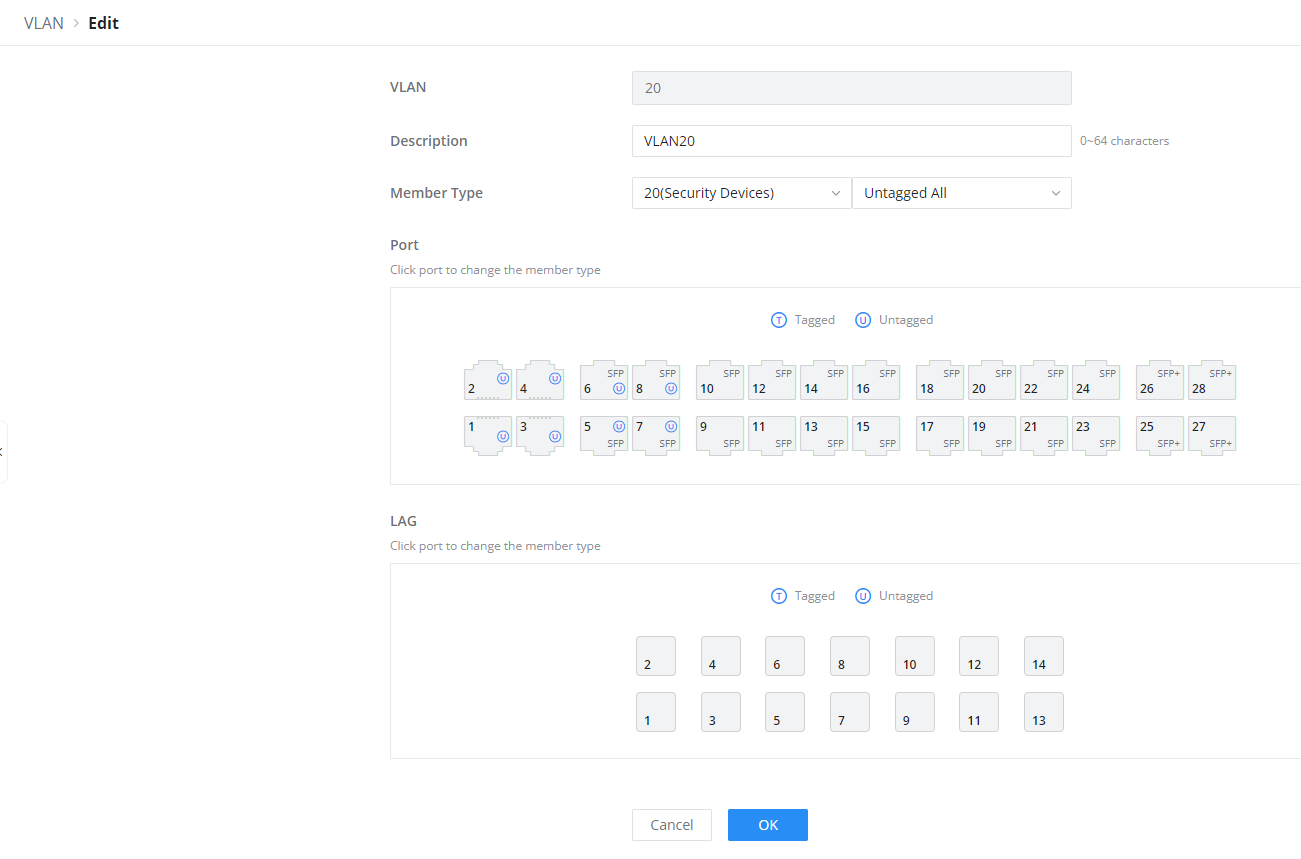
Once the Port Group is created, it can ease up the process of selecting and tagging/untagging VLAN ports individually, Under Switching → VLAN, select the port group to be used for your VLAN
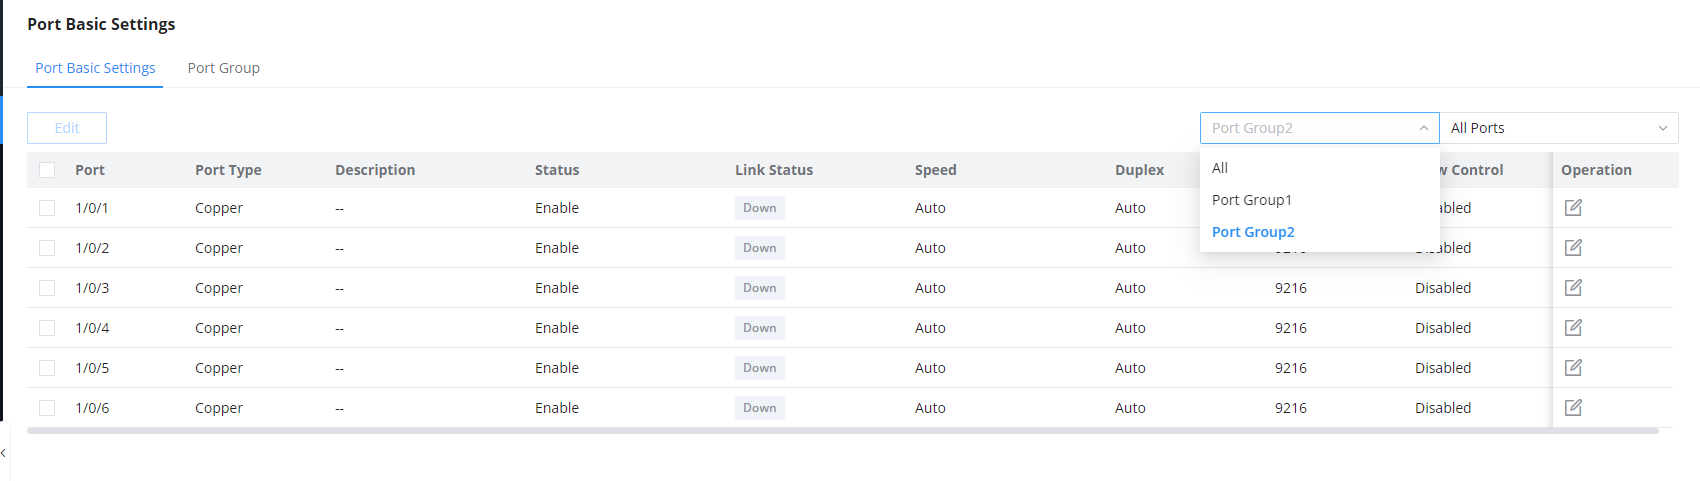
In addition, users can disable/enable specific ports based on the port group created, instead of going through each individual port selection separately:
Port Statistics
For monitoring or even sometimes troubleshooting, the Port Statistics displays in real time the flow of data with different units like Octets, Packets, Transmission Rate, and OurErrPackets. The option to clear all the statistics or a specific port is supported as well.

To view even more details like Etherlike (SNMP), RMON, and port Private MIB information.

Loopback Detection
By enabling the loop detection function of the interface, the interface periodically sends detection packets to check whether the packets are returned to the device, and then determines whether there is a loop in the device. If a loop is detected, the port is automatically shut down to eliminate the loop and ensure the normal operation of the network environment.
Open Switching → Loopback Detection. When Loopback Detection is enabled, Protocol Type accepts 0x0 to 0xFFFF and defaults to 0x8999. Detect Interval (s) accepts 1 to 1000 seconds and defaults to 30 seconds. A shorter interval detects loops sooner but increases detection traffic.

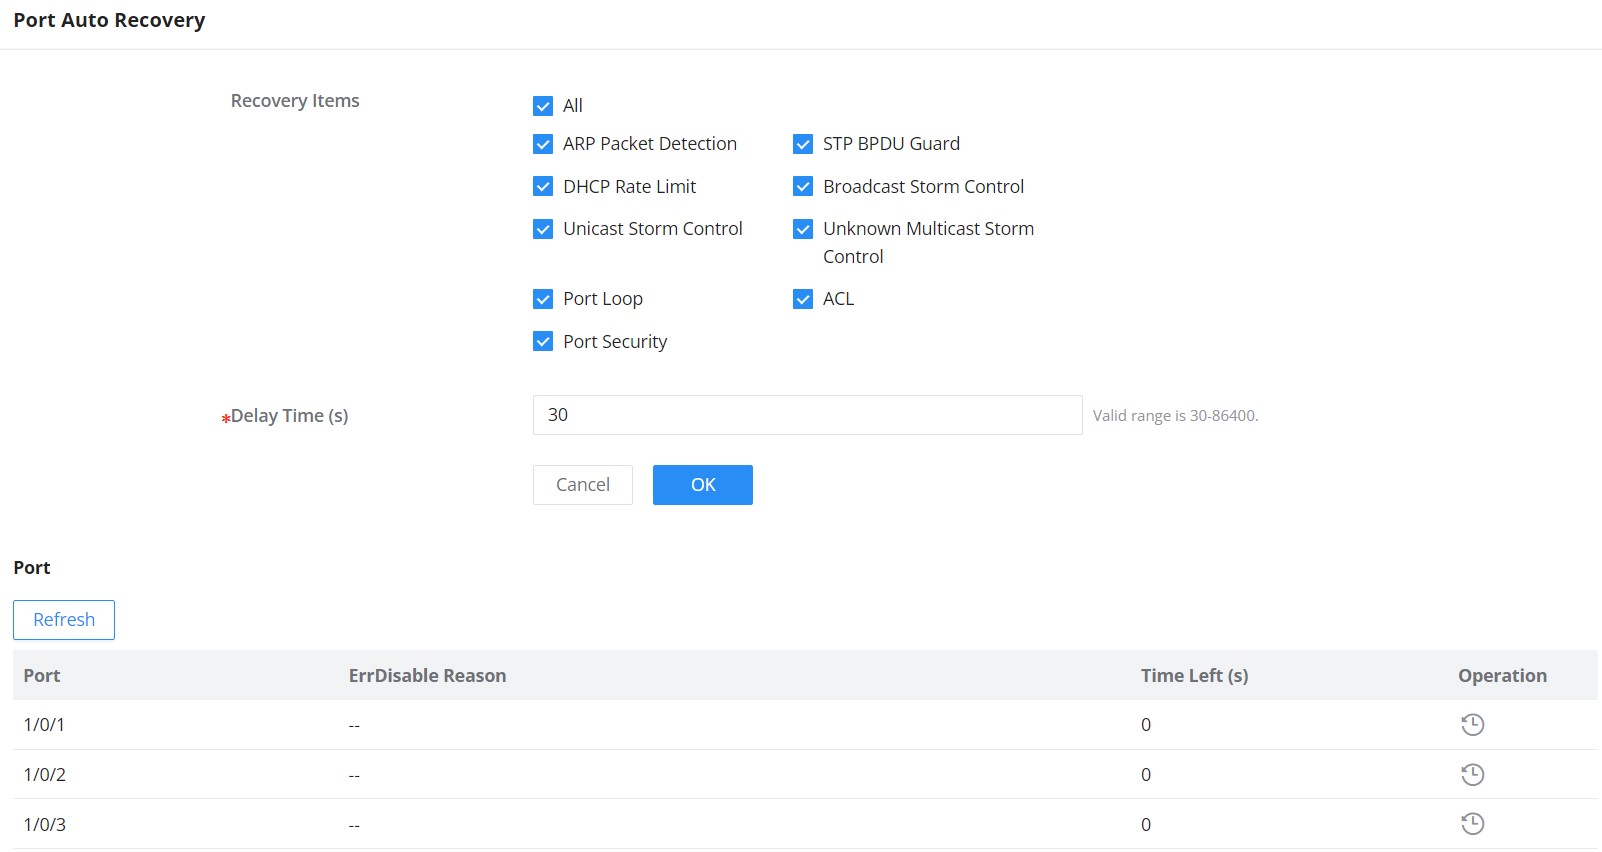
Port Auto Recovery
Port Auto Recovery helps recover a port after a specific delay that can be specified by the user. When the following functions of the port trigger the port down, the port automatically returns to the up state after the delay time:
Examples:
- ARP packet detection: If the ARP rate in DAI exceeds the set value, the current port will be shut down.
- STP BPDU Guard: In spanning tree, the port enables BPDU Guard. When this function is triggered, the port will be shut down.
- Port Loop: When the port is self-looping and spanning tree is enabled, the port will be shut down.
- ACL: When the ACL rule is matched and the action is shutdown, the port will be shut down.
- Port Security: When the number of port MAC addresses exceeds the set number, the port will be shut down.
Link Aggregation
LAG means Link Aggregation Group which groups some physical ports together to make a single high-bandwidth data path. Thus it can implement traffic load sharing among the member ports in a group to enhance the connection reliability.
Link Aggregation Group
There are two load balance modes on these switches, either based on the MAC Address or based on the IP – MAC Address. And in terms of the type of LAG, there are either the static option or to use the LACP or Link Aggregation Control Protocol both of them are supported.
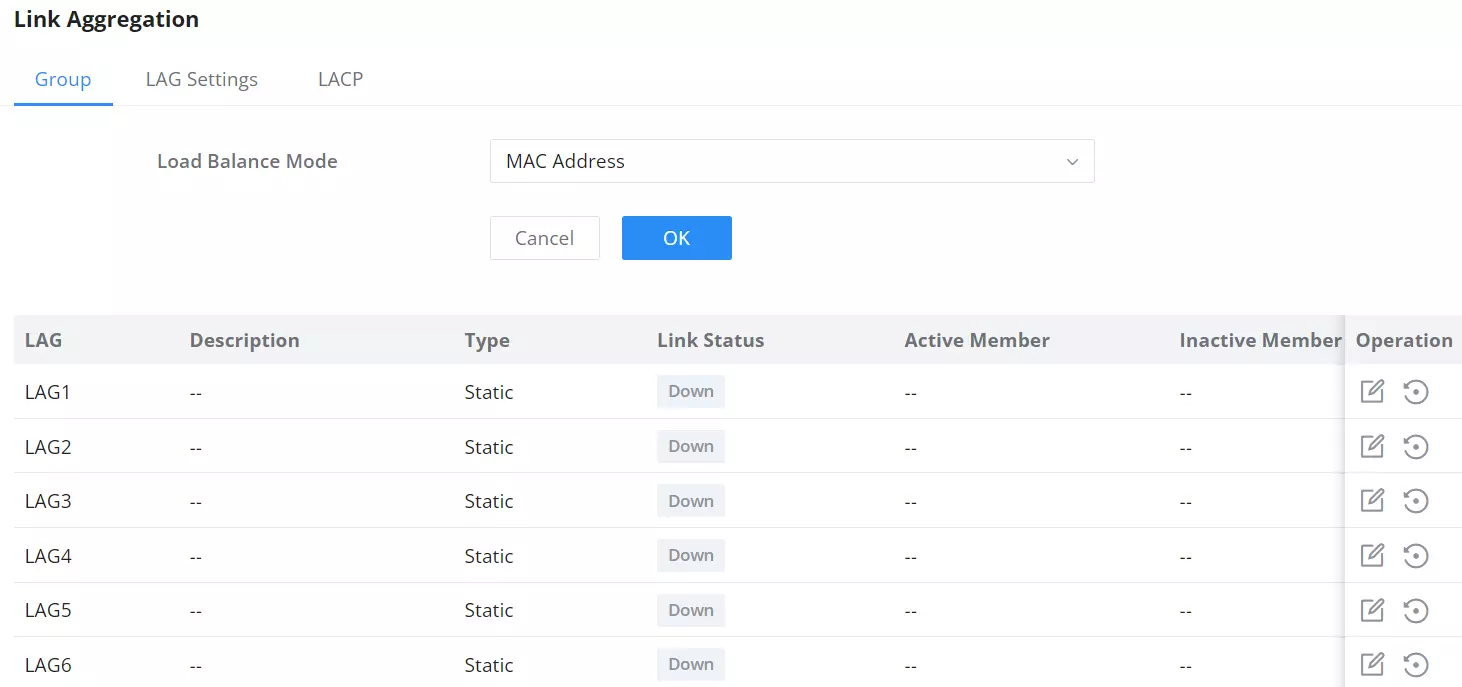
Load Balancing Mode | Select your Load balance mode. MAC address – Aggregated group will balance the traffic based on different MAC addresses. Therefore, the packets from different MAC addresses will be sent to different links. IP/Mac Address – Aggregated group will balance the traffic based on MAC addresses and IP addresses. Therefore, the packets from same MAC addresses but different IP addresses will be sent to different links. |
Edit Group | Name: Enter the name of the LA Group. Type: Use the drop down menu to specify the type for LAG.
GE: Click on port to check / uncheck which ones will be part of this LAG. |
Link Aggregation Port
LAG Port Settings
On this page, the user can Enable the Link Aggregation Group and add a Description as well as specify the speed and the flow control for LAG.
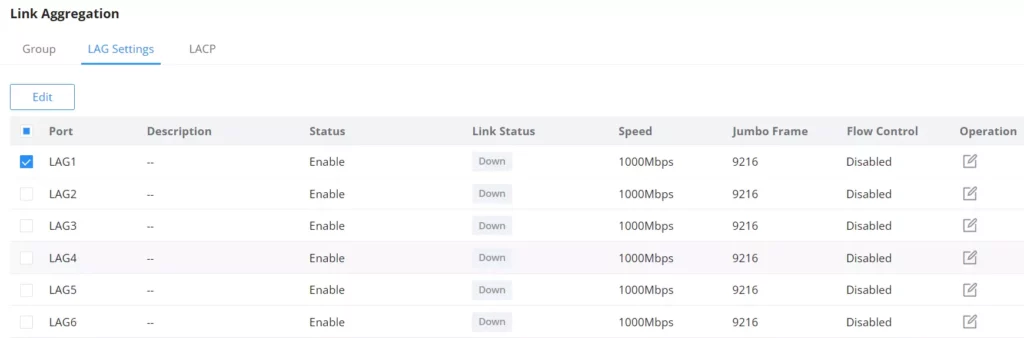
Port | The selected LAG to be configured. |
Description | It is used to configure the information description for this LAG , which can be a description of usage, etc., with a maximum of 128 characters, and the characters limited to input are numbers 0-9 , letters az / AZ and special characters. |
Port Enable | Set whether to enable the interface. it is enabled by default. |
Speed | Set the rate of the interface, the options are {Auto, 10Mbps, 100Mbps, 1000Mbps}. The default is auto-negotiation. Note: When set to Auto, the rate of the interface is automatically negotiated between the interface and the peer port . |
Jumbo Frame | Specify the jumpo frame, valid range is 1518-12288. Default value is 9216 |
Flow Control | Set the flow control on the interface, the options are { Disabled, Enabled, Auto}. The default is Disabled After enabling it, if the local device is congested, it will send a message to the peer device to notify the peer device to temporarily stop sending packets, after receiving the message, the peer device will temporarily stop sending packets to the local and vice versa. Thus, the occurrence of packet loss is avoided. |
Link Aggregation Settings
LACP
LACP or Link Aggregation Control Protocol is based on the priority, and the user can enable a system priority or even specify the the priority for each port individually.
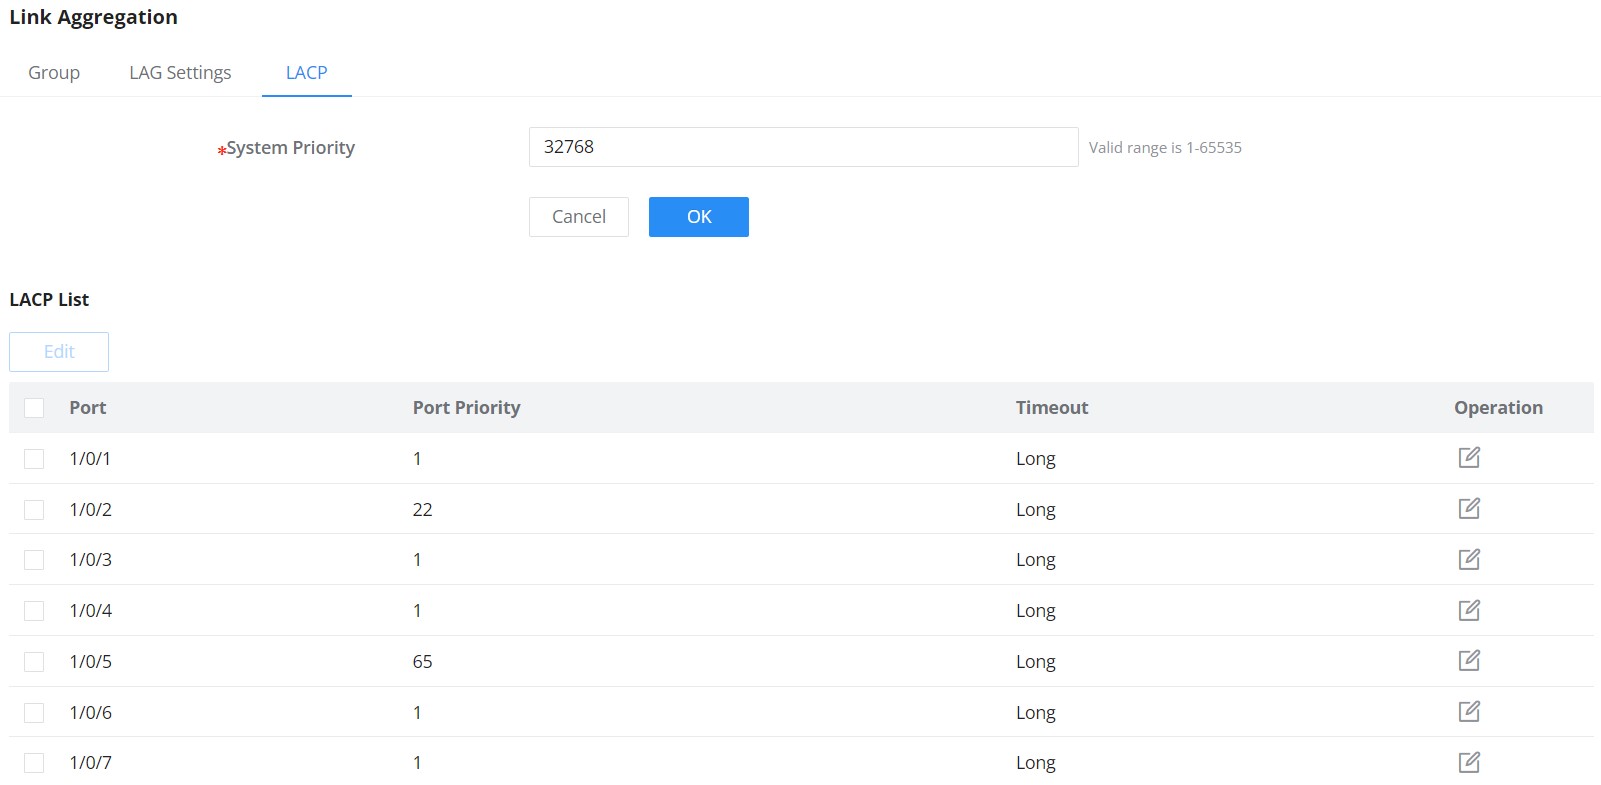
System Priority | Set the system priority of LACP, the value range is an integer from 1-65535, the default is 32768. |
Edit LACP | Port: Select the switch LAG interface to be configured Port Priority:Set the LACP protocol priority of the port , the value range is an integer from 1 to 65535 , the default is 1. Note: The smaller the priority value of the port , the higher the LACP priority of the port. Timeout: Set the timeout time for receiving LACP packets, the options are { Short, Long} , the default is Short.
|
Link Aggregation – LACP
MAC Address Table
The MAC address table records the correspondence between the MAC addresses of other devices learned by the switch and the interfaces, as well as information such as the VLANs to which the interfaces belong. When forwarding a packet, the device queries the MAC address table according to the destination MAC address of the packet. If the MAC address table contains an entry corresponding to the destination MAC address of the packet, it directly forwards the packet through the outbound interface in the entry. If the MAC address table does not contain an entry corresponding to the destination MAC address of the packet , the device will use broadcast mode to forward the packet on all interfaces in the VLAN to which it belongs except the receiving interface.
The entries in the MAC address table are divided into Dynamic Address, Static MAC Address, Black hole Address and Port Security Address.
Dynamic Address
the MAC address table is established based on the automatic learning of the source MAC address in the data frame received by the device. If the MAC address entry does not exist in the MAC address table, the device adds the new MAC address and the interface and VLAN corresponding to the MAC address as a new entry into the MAC address table. The switch updates the entry by resetting the aging time.
Aging Time (s):
Dynamic MAC address entries have a lifetime measured in seconds. An entry is removed if it is not refreshed before the timer expires. The verified range is 0 or 60 to 1000000 seconds, and the default is 300 seconds. Setting the value to 0 disables aging for dynamic entries.
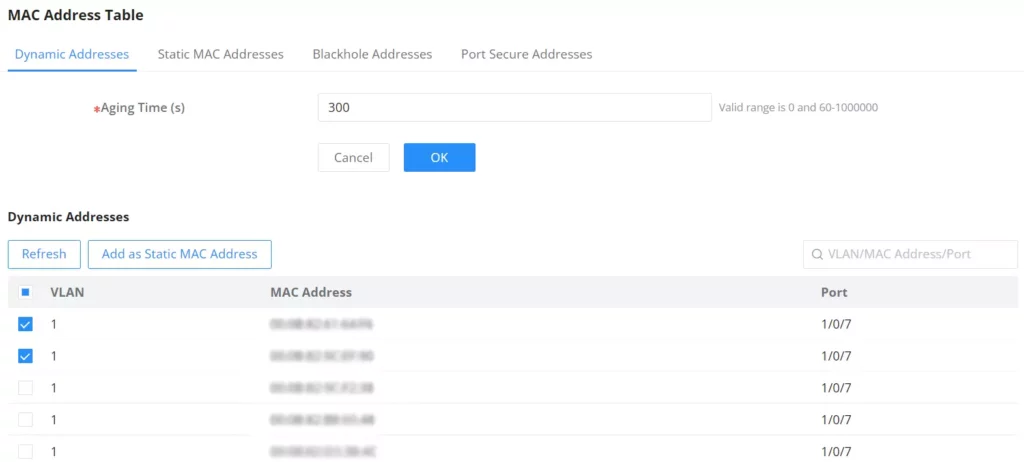
Click on the “Refresh” button to update the table, or click on the “Add Static MAC Address” button to add the entry to the static MAC address.
Static MAC Address
This section allows the user to manually assign a MAC address to the MAC table. The configuration
result will be displayed on the table listed on the lower side of this web page.
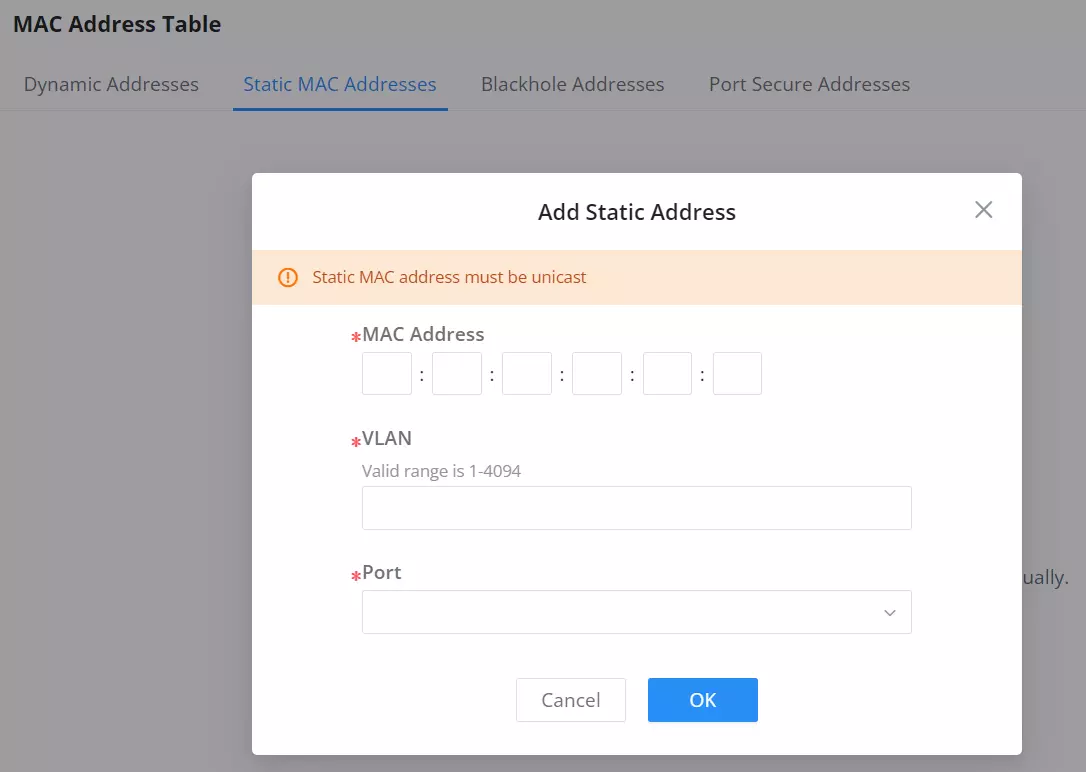
MAC Address | Enter the MAC address that will be forwarded |
VLAN | This is the VLAN group to which the MAC address belongs. |
Port | Select the port where received frame of matched destination |
Static MAC Address
Black Hole Address
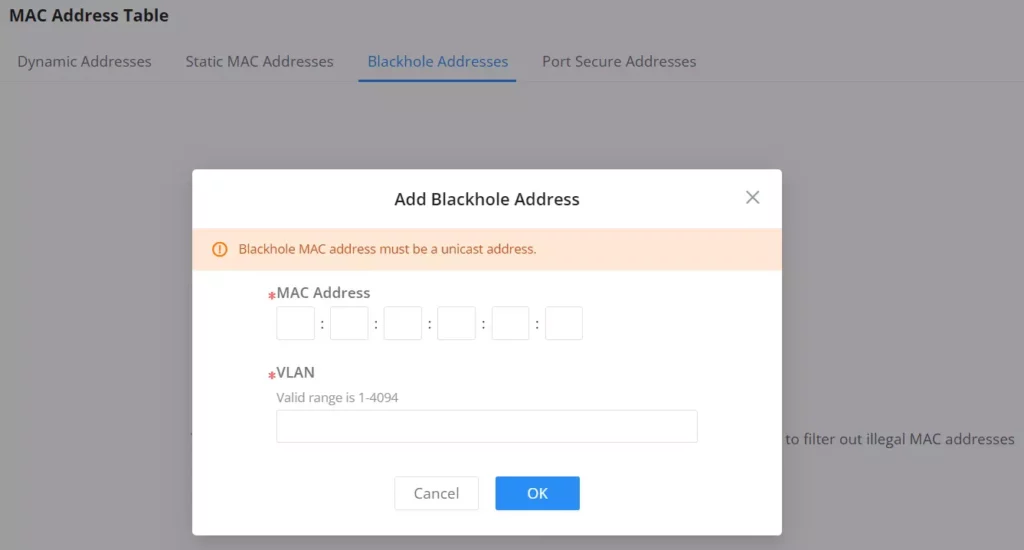
If a MAC address is not trusted or insecure, The user can block the traffic of certain MAC Addresses and discard them by adding them to the Black Hole Address Table.
Click on the “Add” button then enter the MAC Address and the VLAN.
Port Security Address
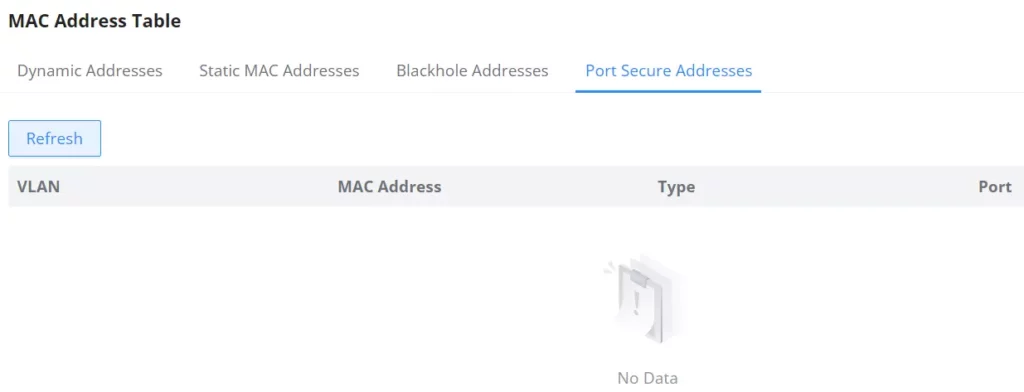
After enabling port security in Security → Port Security, the addresses will be displayed in the MAC Address Table → Port Security Address synchronously.
The list shows the interface name, VLAN, and MAC address.
VLAN
A virtual local area network, virtual LAN or VLAN, is a group of hosts with a common set of requirements that communicate as if they were attached to the same broadcast domain, regardless of their physical location. A VLAN has the same attributes as a physical local area network (LAN), but it allows for end stations to be grouped together even if they are not located on the same network switch. VLAN membership can be configured through software instead of physically relocating devices or connections.
A user can click on “Add” button to add a new VLAN, also it’s possible to create many VLANs at the same time by specifying a range, for example (7-9) will create VLAN 7,8 and 9, or create different separated VLANs, for example (11,89) will create VLAN 11 and 89.


If the VLAN is already created there is also the option to modify it by clicking on modify button for more options and settings like Description, Tagged and Untagged ports and LAGs.
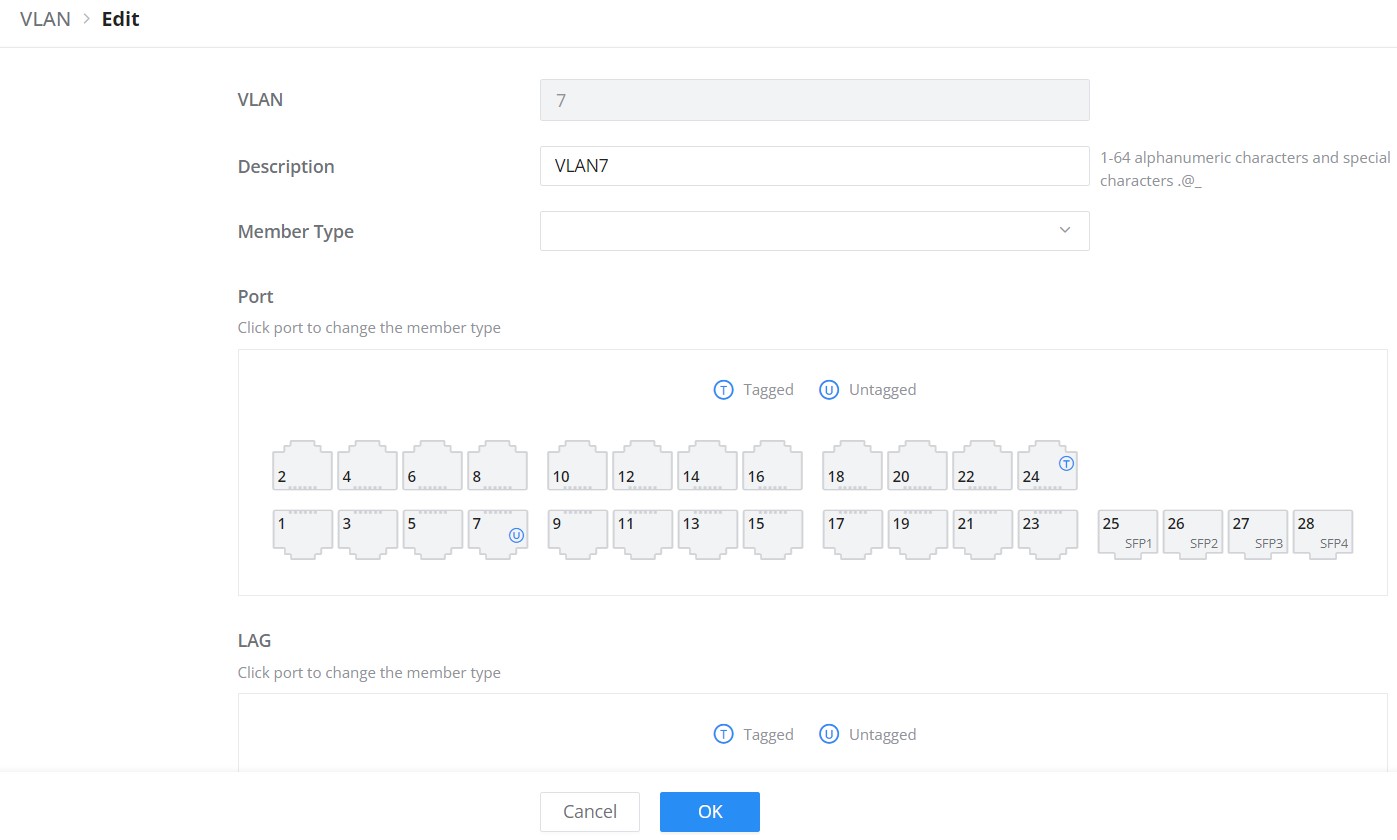
VLAN | The specified VLAN ID |
Description | Enter a brief comment for the VLAN ID. |
Member Type | Select from the drop-down list:
|
GE | Select individually which ports are tagged, untagged or unselected. Note:
|
LAG | Select individually which LAGs are tagged, untagged or unselected. |
Edit VLAN
Please refer to the table below for more details about Tagged and Untagged Ports.
Port Type | Receiving Packets | Forwarding Packets | |
Untagged Packets | Tagged Packets | Tagged Packets | |
Untagged | When untagged packets are received, the port will add the default VLAN tag, i.e. the PVID of the ingress port, to the packets. | If the VID of packet is allowed by the port, the packet will be received. If the VID of packet is forbidden by the port, the packet will be dropped. | The packet will be forwarded after removing its VLAN tag |
Tagged | The packet will be forwarded with its current VLAN tag | ||
VLAN Tagged and Untagged
VLAN Port Settings
The Port Settings page allows for configuring VLAN on each port and LAG by specifying the Link Type (Trunk, Access, Hybrid, or QinQ) as well as the default VLAN or PVID, the user can also enable Ingress Filtering for the selected port, also the accepted Frame Type (All, Tag Only and Untag only) and more.

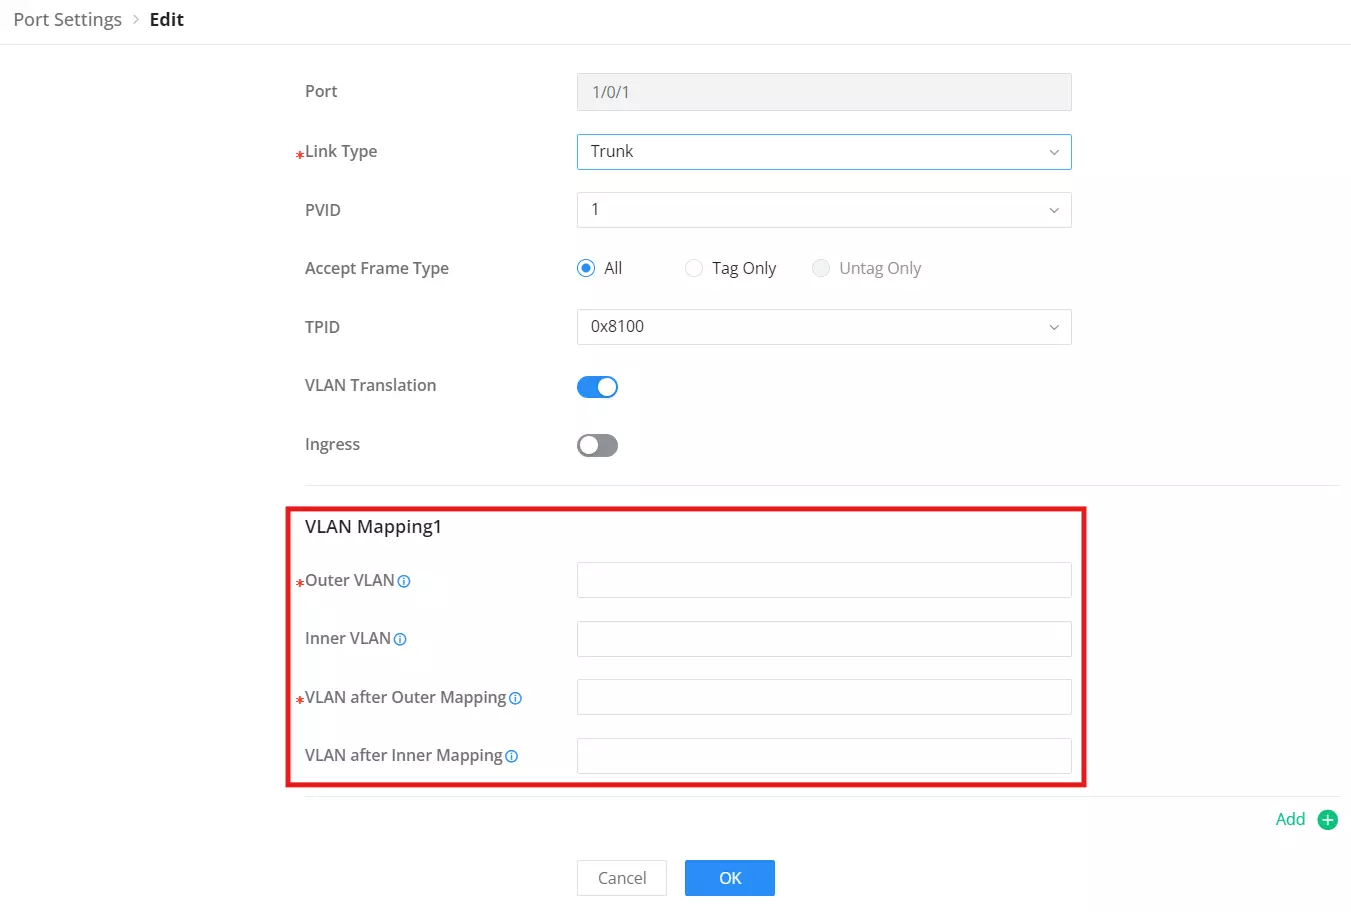

Port | Shows the selected Port. |
Link Type | Select the Link Type:
|
PVID | Enter the default VLAN ID. |
Accept Frame Type | Specifies which types of Ethernet frames are accepted by the port. Options vary depending on the selected Link Type: Hybrid:
Access:
Trunk:
QinQ:
Note: Setting Tag Only is the recommended method to disable native VLAN behavior on trunk and hybrid ports, providing better traffic control and increased security. |
Ingress Filtering | Set whether to enable the inbound filtering function of the interface. Ingress Filtering is only available for Hybrid port, and it’s enabled by default. Note: Ingress filtering is a method used by enterprises and internet service providers (ISPs) to prevent suspicious traffic from entering a network. |
VLAN Translation | Allows translating one VLAN ID to another at the port level. It’s useful for scenarios where different parts of the network use different VLAN IDs but need to communicate with each other. |
MAC VLAN | Allows the switch to assign VLANs based on the MAC address of the incoming traffic. It can be used for more dynamic VLAN assignment, where devices can be automatically placed into specific VLANs based on their MAC addresses. |
Protocol VLAN | Allows VLAN assignments based on the protocol type in the frame, such as IP or ARP. It enables grouping traffic from certain protocols into specific VLANs for easier network management. |
VLAN Port Settings
VLAN Port Members
On this page, the user can define both Tagged and Untagged VLANs (members) for each port individually.

Trunk Allowed VLANs allow the configuration of VLANs that do not yet exist on the switch and are only effective for configured VLANs.


Voice VLAN
A voice VLAN (virtual local area network) is a dedicated VLAN specifically designed to carry voice traffic, such as IP phone calls. By isolating voice traffic from other types of network traffic, voice VLANs help ensure that voice calls are prioritized and experience minimal latency or jitter. This is critical to maintaining clear and uninterrupted voice communications.
Voice VLAN advantages:
- Improved voice quality: By isolating voice traffic from other types of network traffic, voice VLANs help reduce the latency and jitter that can cause choppy or distorted audio during voice calls.
- Reduced congestion: By prioritizing voice traffic, voice VLANs help prevent other types of network traffic from interfering with voice calls, even during periods of heavy network usage.
- Simplified network management: Voice VLANs can simplify network management by making it easier to troubleshoot and resolve voice-related issues.
For example, when an IP phone is connected to a switch port, the switch can prioritize traffic in the voice VLAN so voice packets are forwarded according to the configured priority.
The user can select more than one way to set up the voice VLAN:
- Auto Voice VLAN
- Tagged OUI
- Tagged OUI using VLAN Tag
- Untagged OUI
For more details, please visit this guide: GWN78xx(P) – Voice VLAN Guide.
To configure Voice VLAN, please navigate to Web UI → Switching → VLAN page → Voice VLAN tab.
| Field or action | Description |
|---|---|
| Mode | Select Disabled, Auto Voice VLAN, Tagged OUI, or Untagged OUI. |
| Voice VLAN ID | Specifies the VLAN used for recognized voice traffic when Auto Voice VLAN is selected. VLAN 1 cannot be used as the Voice VLAN. |
| CoS/802.1p Priority | Sets the Layer 2 priority from 0 to 7. The default is 6. |
| DSCP | Sets the IP-layer voice priority from 0 to 63. The default is 46. |
| CoS Remarking | Available when Tagged OUI or Untagged OUI is selected. Enable it to apply the configured CoS value to recognized voice traffic. |
| Aging Time | Available when Tagged OUI or Untagged OUI is selected. Sets how long a learned voice-device entry remains valid. The range is 30 to 65536 minutes, and the default is 1440 minutes. |
| Port Settings | Configure Voice VLAN Status and Mode for the selected port. Status is disabled by default, and the default mode is Manual. In Manual mode, add the port to the Voice VLAN manually. |

OUI
An OUI address is a unique identifier assigned by IEEE (Institute of Electrical and Electronics Engineers) to a device vendor. It comprises the first 24 bits of a MAC address. You can recognize which vendor a device belongs to according to the OUI address. The following table shows the OUI addresses of several manufacturers. There is also the option to add a custom one based on user needs.

MAC VLAN
MAC VLAN is a networking technique where each VLAN is based on the source MAC address of incoming frames. Devices with the same MAC address share a VLAN. This segmentation enables isolated communication between devices within the same VLAN based on MAC addresses.
VLANs are divided according to the source MAC address of the data frame. Through the configured MAC address and VLAN mapping table, when the switch receives an untagged frame, it adds the specified VLAN Tag to the data frame based on the mapping table.
To add a MAC address to VLAN mapping, click on “Add” button then specify the MAC Address, Mask Length, VLAN and the priority (802.1p).

Protocol VLAN
VLANs are divided according to the protocol (family) type and encapsulation format to which the data frame belongs. Through the configured protocol domain and VLAN mapping table in the Ethernet frame, when the switch receives an untagged frame, it adds the specified VLAN Tag based on the mapping table.

PVLAN
Private VLAN (PVLAN) is supported on the switches covered by this guide, offering enhanced traffic isolation within the same VLAN domain. This allows more granular segmentation and security, especially useful in shared environments like data centers, hotels, or enterprise access layers.
VLAN Settings
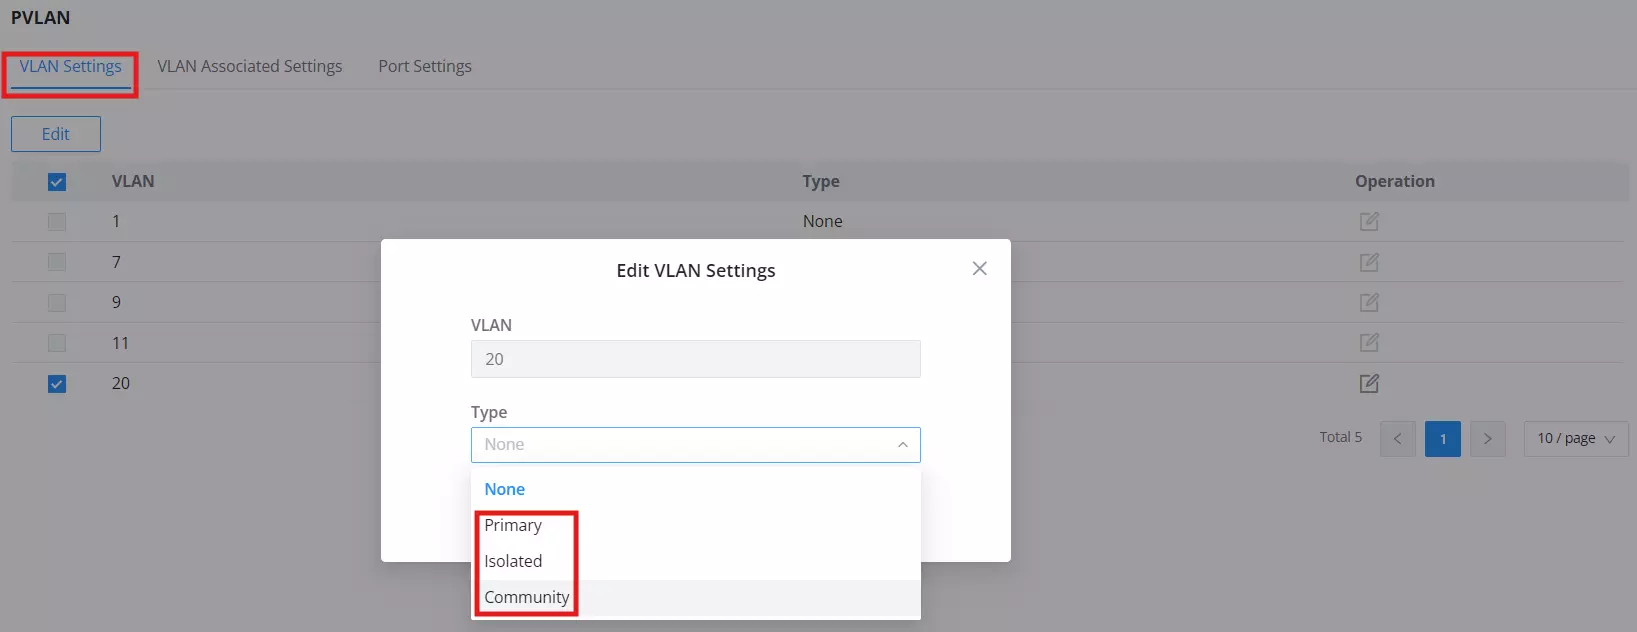
This tab allows assigning a PVLAN type to each VLAN.
- Go to Switching > PVLAN > VLAN Settings.
- Select a VLAN and click Edit.
- Choose the VLAN type from:
- Primary: Communicates with all other PVLAN types.
- Isolated: Can only talk to Primary VLAN.
- Community: Can talk to Primary and other VLANs in the same Community.
- Click OK then Save.
VLAN Associated Settings
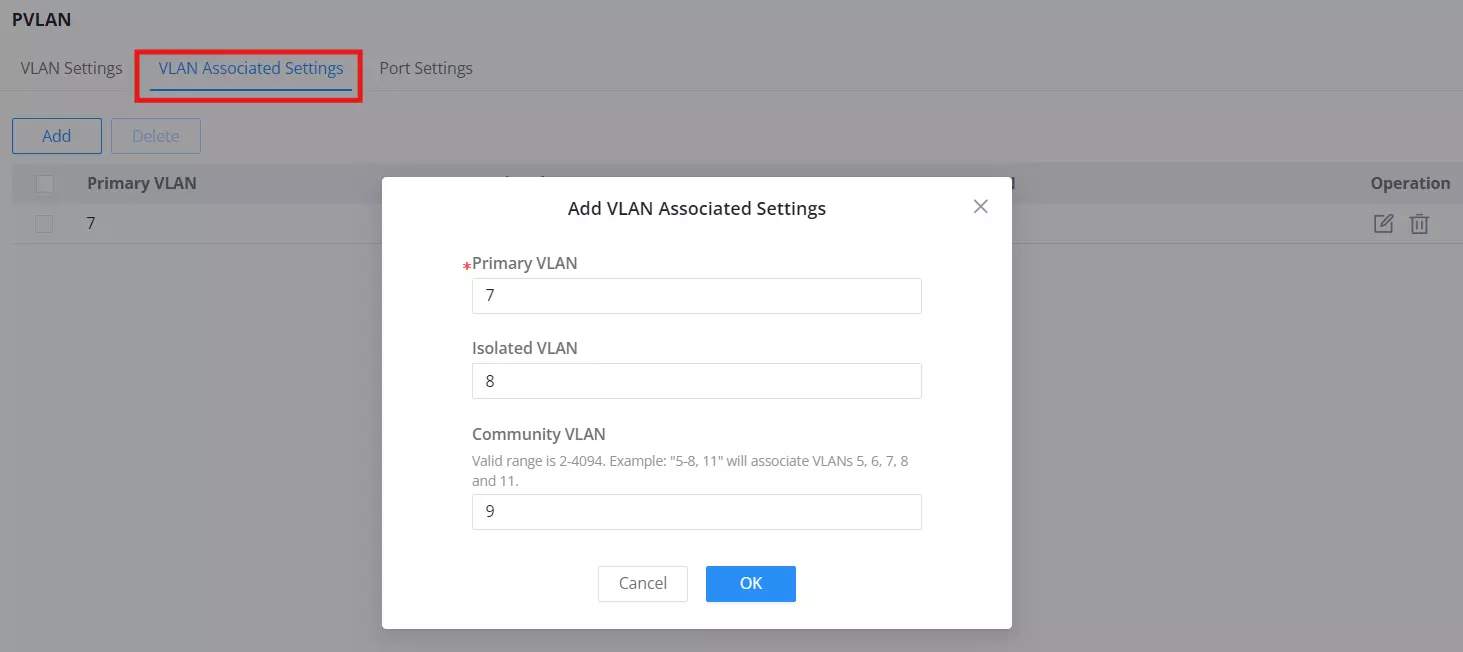
This section allows linking VLANs together in a PVLAN structure.
- Go to Switching > PVLAN > VLAN Associated Settings.
- Click Add, then set:
- Primary VLAN: The main VLAN in this association.
- Isolated VLAN: VLAN(s) that only communicate with the Primary.
- Community VLAN: VLAN(s) that communicate with Primary and each other.
- Use comma-separated lists (e.g.,
11,12) or ranges (20-24) as needed. - Click OK to apply.
Port Settings (PVLAN)
Here you bind switch ports to PVLAN roles.
- Go to Switching > PVLAN > Port Settings.
- Select a port and click Edit.
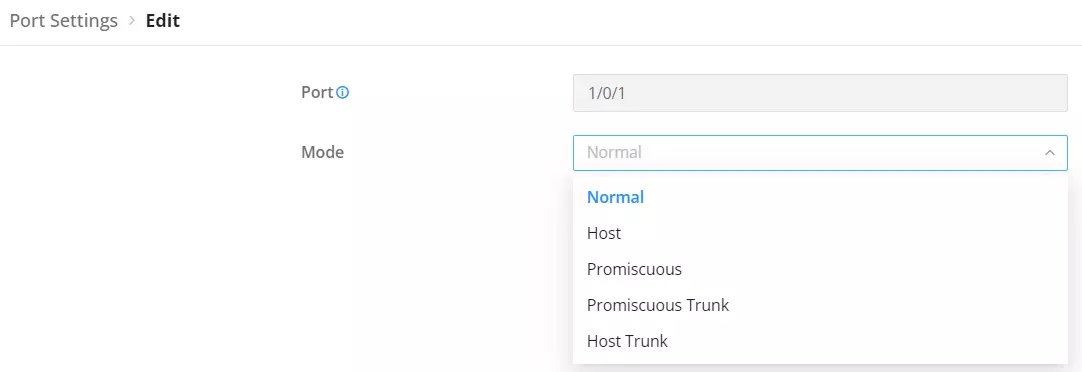
- Choose the Mode:
- Promiscuous: Communicates with all other PVLAN port types.
- Host: Communicates only with Promiscuous ports.
- Community: Communicates with Promiscuous and other Community ports in the same VLAN.
- Trunk Variants: Used to forward tagged PVLAN traffic.
- Click OK and then Save.
Spanning Tree
STP (Spanning Tree Protocol), Devices running STP discover loops in the network and block ports by exchanging information, in that way, a ring network can be disbranched to form a tree-topological ring-free network to prevent packets from being duplicated and forwarded endlessly in the network.
BPDU (Bridge Protocol Data Unit) is the protocol data that STP, RSTP and MSTP use. Enough information is carried in BPDU to ensure the spanning tree generation. STP is to determine the topology of the network via transferring BPDUs between devices.
This page allows a user to configure and display Spanning Tree Protocol (STP) property configuration including the STP Mode (STP, RSTP or MSTP), Path Cost, Bridge Priority, Max Hops, Hello and Max Aging time and Forward Delay Time.
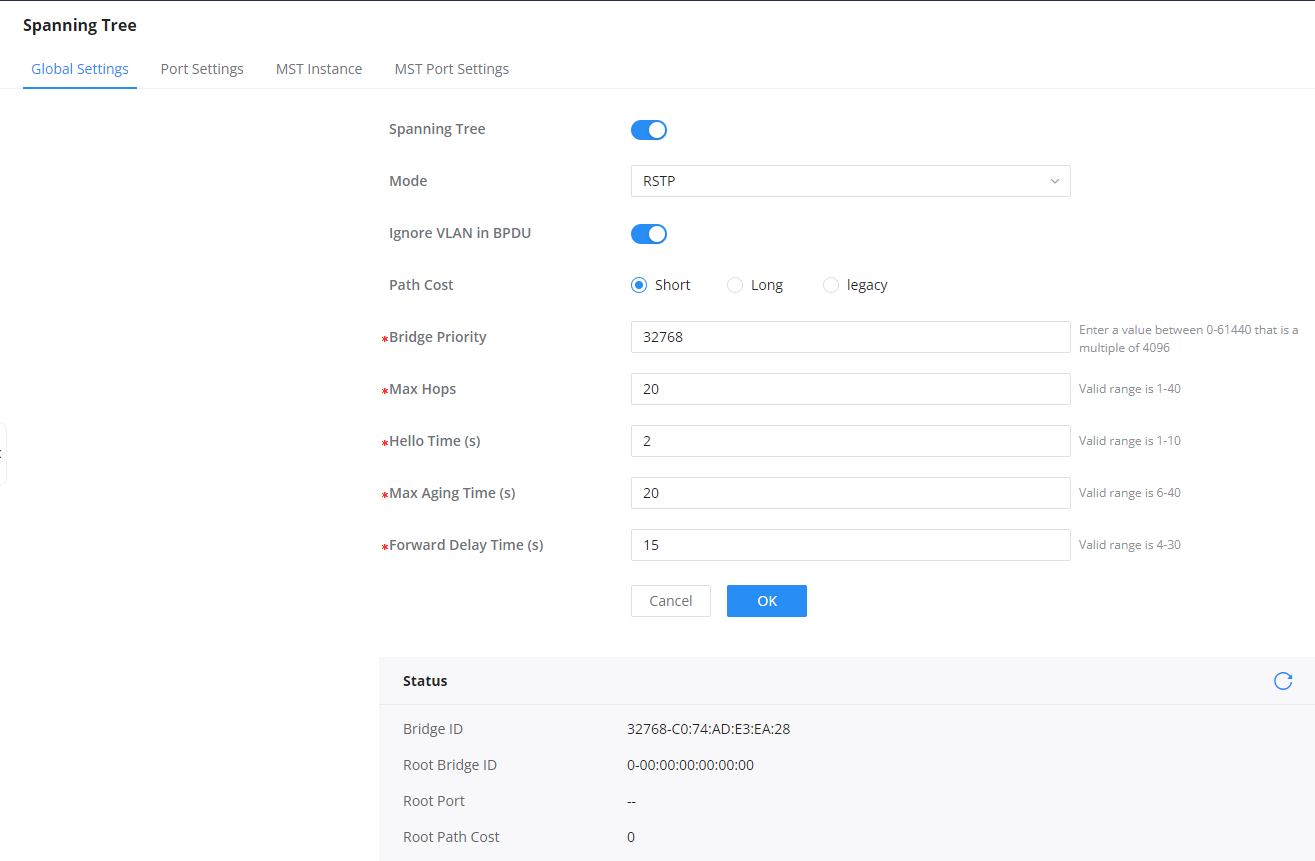
Spanning Tree | Set whether to enable Spanning Tree. |
Mode | Set the operating mode of Spanning Tree (STP).
|
Ignore VLAN in BPDU | This feature allows the switch to ignore VLAN-specific information in Bridge Protocol Data Units (BPDUs). This prevents VLAN configurations from influencing Spanning Tree Protocol (STP) decisions across multiple VLANs. |
Path Cost | Specify the path cost method (Short, Long, or Legacy). Default is Short. |
Bridge Priority | Select the Bridge Priority, In an STP network, the device with the smallest bridge ID is elected as the root bridge. Default is 32768. Note: The valid range is 0~61440, which must be a multiple of 4096 |
Max Hops | Select the Max Hops (the range is 1 – 40). Default is 20 |
Hello Time (s) | Specify the Hello Time in seconds (the range is 1 -10). Default is 2. Note: The time interval at which the device running the STP protocol sends the configuration message BPDU , which is used by the device to detect whether the link is faulty. |
Max Aging Time (s) | Select The aging time of BPDU packets of the port (the range is 6 – 40). Default is 20. |
Forward Delay Time (s) | Specify the Forward Delay Time in seconds (the range is 4 -30). Default is 15. |
STP Global Settings
STP Port Settings
To configure STP on each port and LAG then navigate to WEB UI → Spanning Tree → Port Settings, then click on “Edit” button.
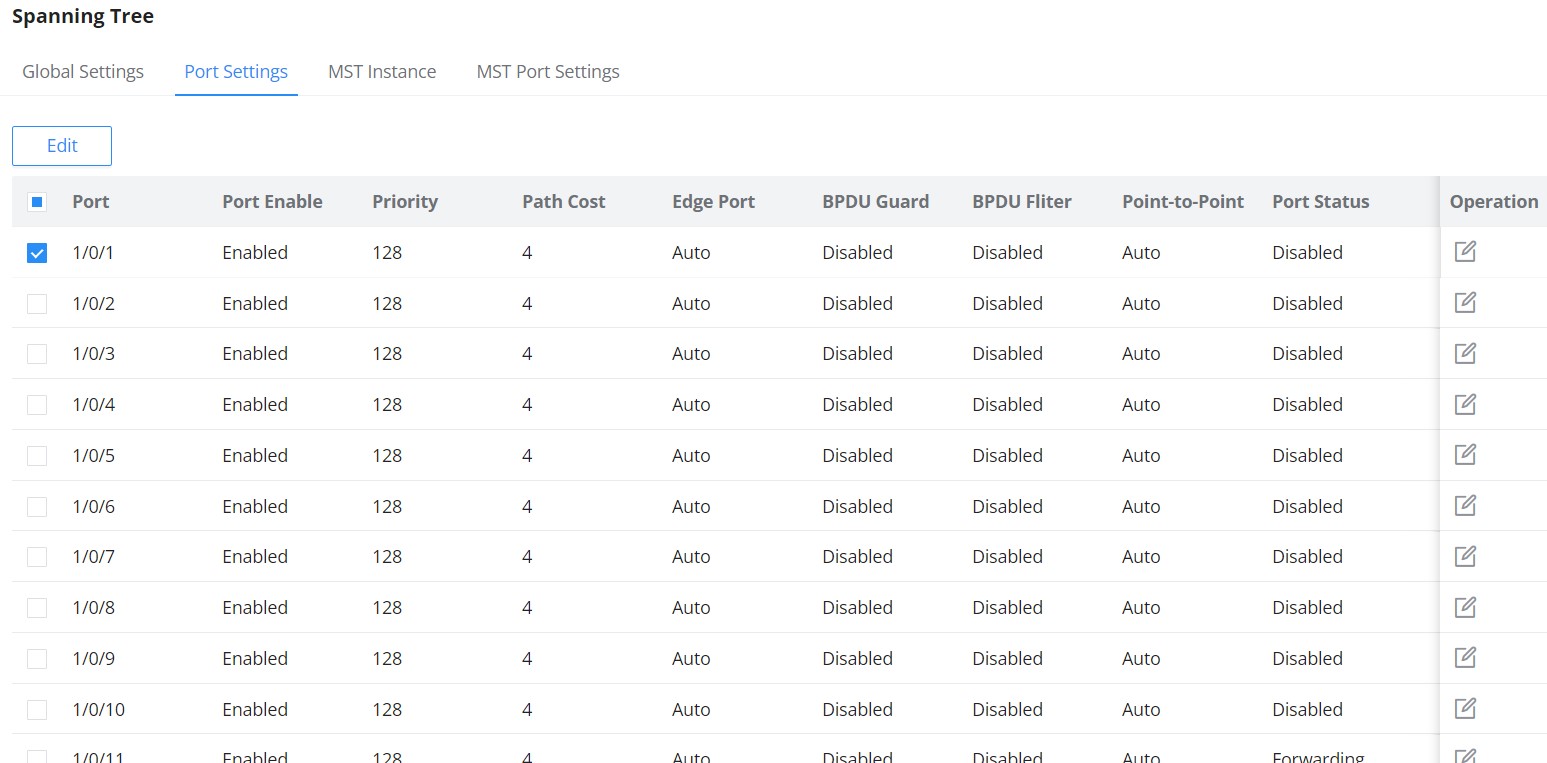
For each port or LAG, the user can enable STP and specify the priority, Path Cost, Edge port, BPDU Guard and Filter and Point-To-Point.
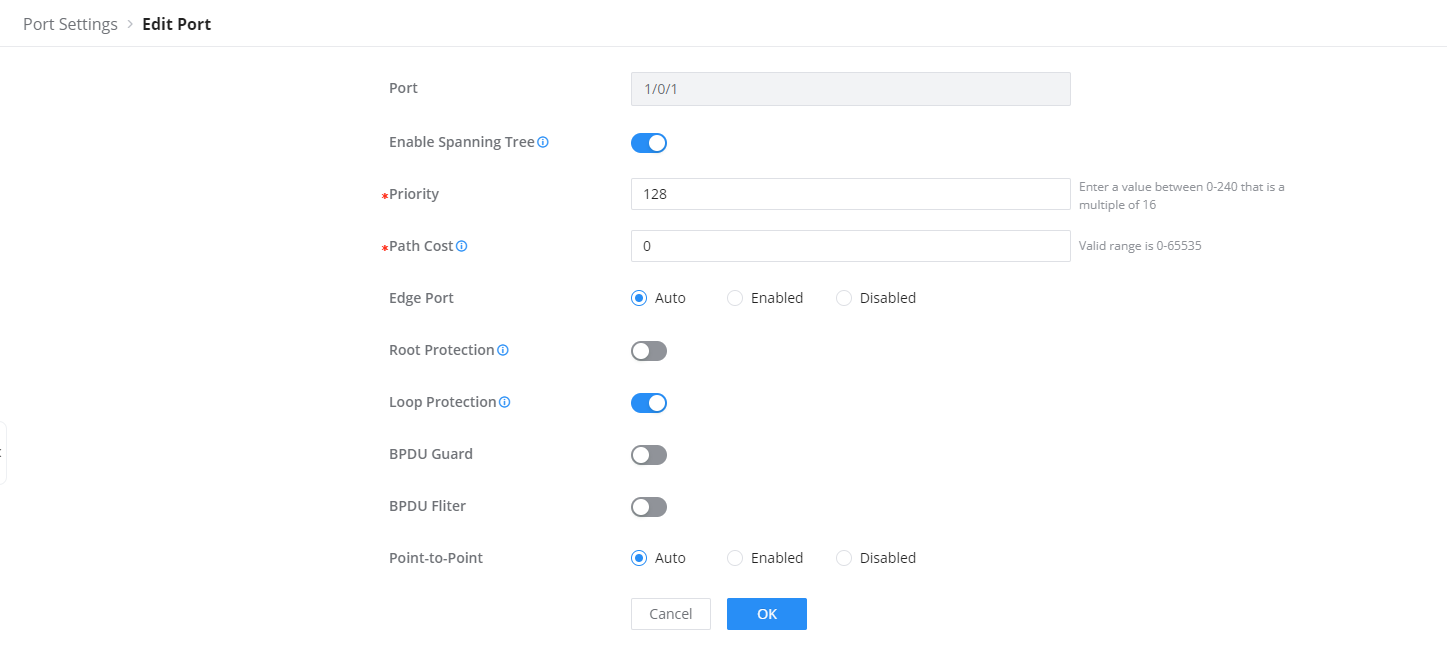
Port | Displays the selected GE/LAG Port. |
Enable STP | Set whether to enable STP on this port. |
Priority | Priority is an important basis for determining whether the port will be selected as the root port. The port with higher priority under the same conditions will be selected as the root port . The smaller the value , the higher the priority . An integer in the range of 0-240, with a step size of 16, and a default of 128 . Note: The valid range is 0~240, which must be a multiple of 16 |
Path Cost | Set the path cost of the port on the specified spanning tree. The default value is 0, which means that path cost calculation is performed automatically. Note:The valid range of path cost depends on the path cost settings in Global Settings.If set to “Short” in Global Settings, the valid range is 0-65535; if set to “Long”, the valid range is 0-200000000; if set to “legacy”, the valid range is 0-200000. |
Edge Port | Set whether to enable Edge Port or disable it, by default it’s on auto. Notes:
|
Root Protection | Safeguards the root bridge by preventing designated ports from becoming the root port, thus protecting the current root bridge from being displaced by lower-priority BPDUs. |
Loop Protection | Prevents Layer 2 loops by ensuring a blocking state on ports that stop receiving BPDUs, avoiding the formation of network loops. |
BPDU Guard | Set whether to enable BPDU Guard. Note: BPDU Guard further protects your switch by turning this port into error state and shutdown if any BPDU received from this port. |
BPDU Filter | Set whether to enable BPDU Filter. Note: Drop all BPDU packets and no BPDU will be sent. |
Point-to-Point | Select Point-to-Point option (Auto, Enabled or Disabled). Default is Auto. Note: determines the STP of link type for this port automatically if set to Auto. |
STP Port Settings
Multiple Spanning Tree Instances
MST, or Multiple Spanning Tree, maps VLAN traffic to separate spanning-tree instances. The MSTI value supports instances 0 to 31. A region is identified by its Region Name and Revision Level, and switches must use matching region parameters to participate in the same MST region.
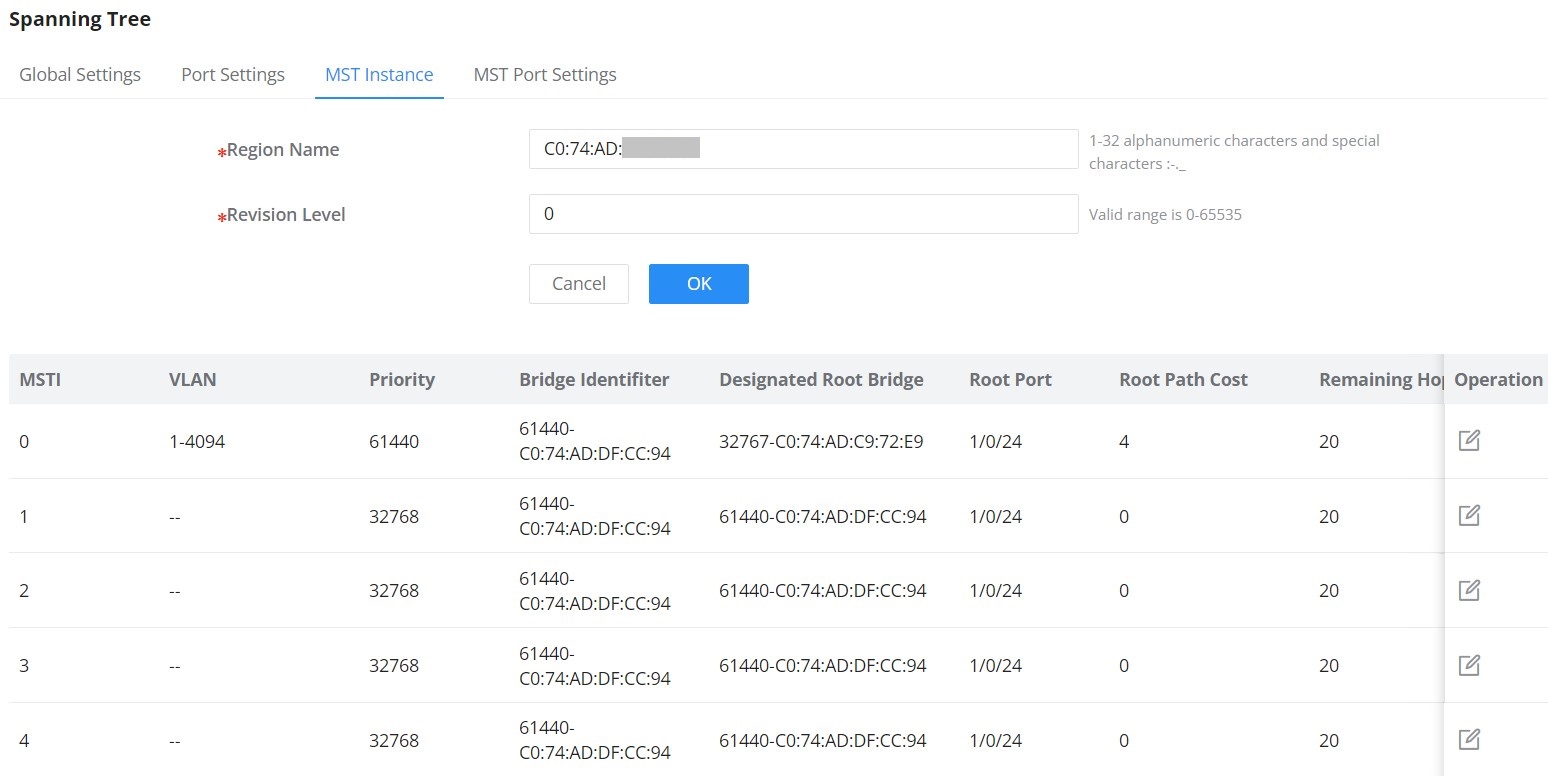
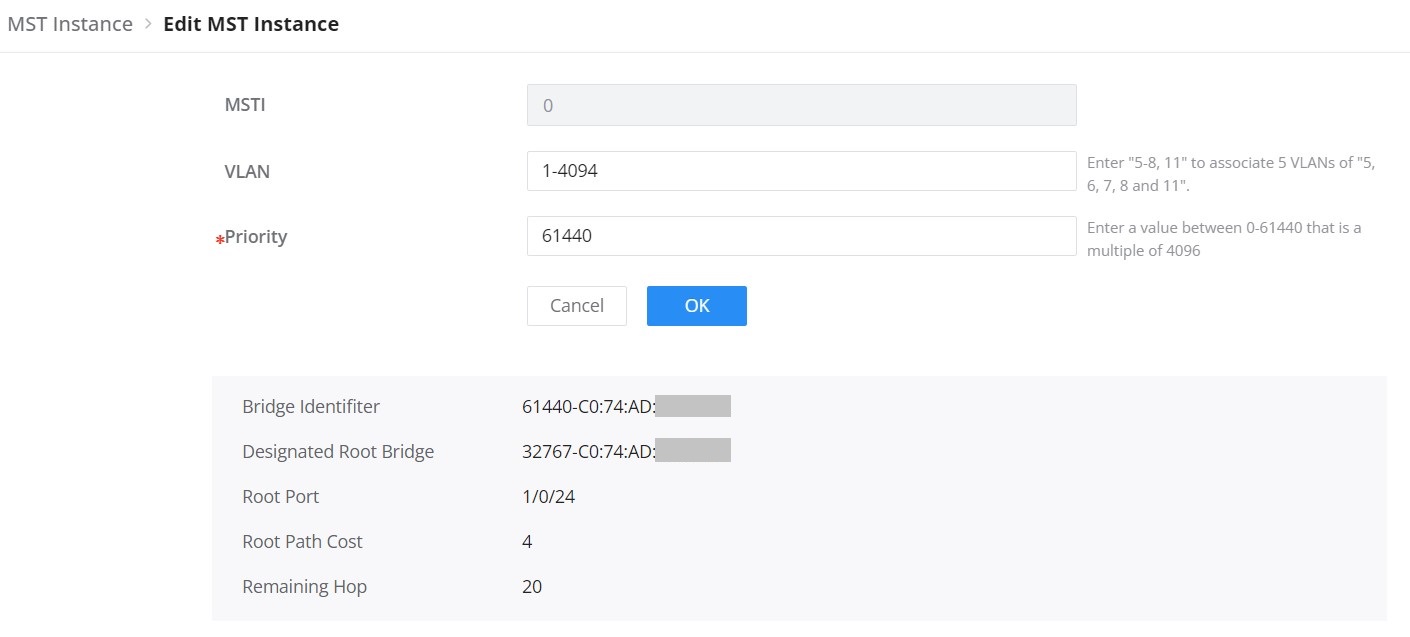
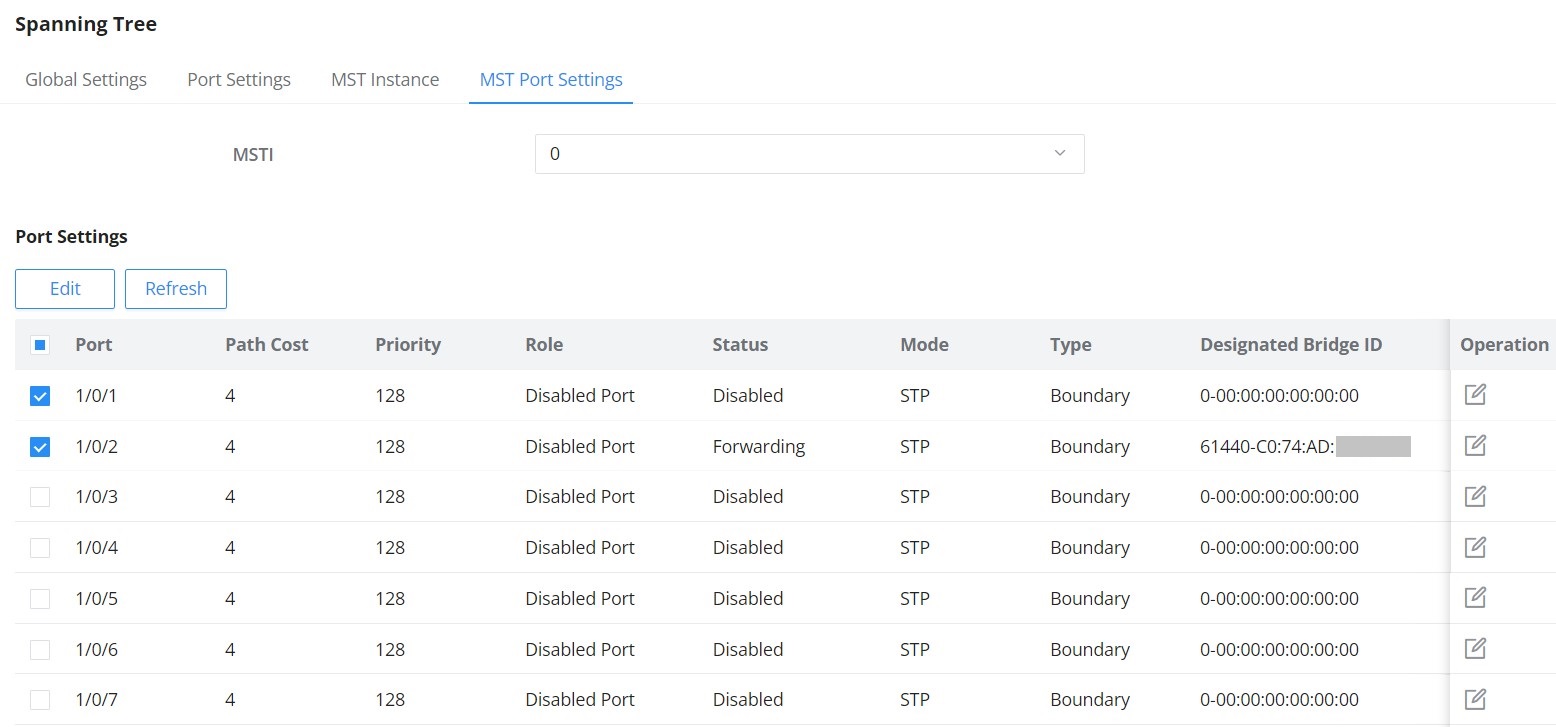
MST Port Settings is used to configure the GE port / LAG group settings for each MST instance.
The table displays the MST parameters for each port.
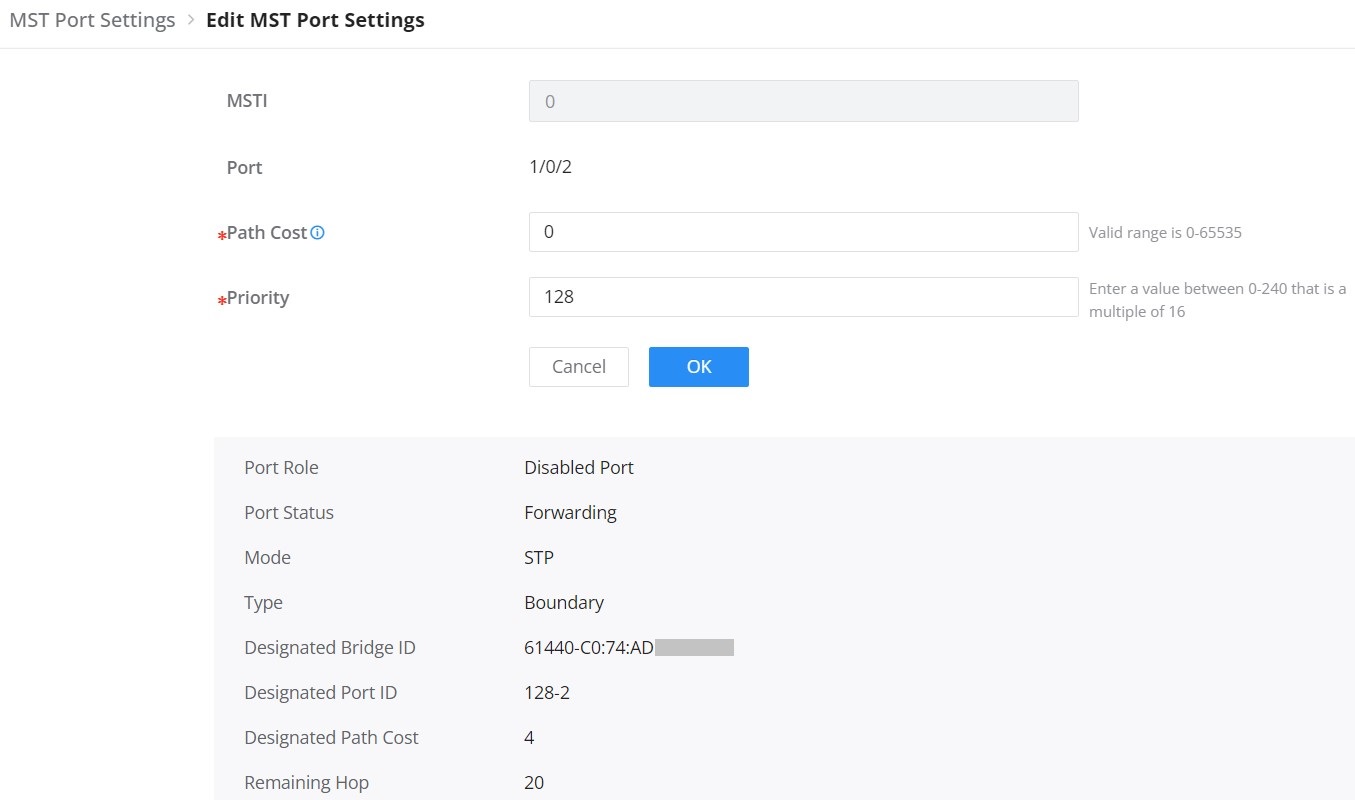
Click on “Edit” button to edit the MST Port Settings for each Port/LAG individually and also the user can even specify the Path Cost and Priority per Port/LAG as well.
PVST VLAN Settings
When Per VLAN Spanning tree protocol is selected as the STP protocol to be used, then the VLAN settings can be defined.
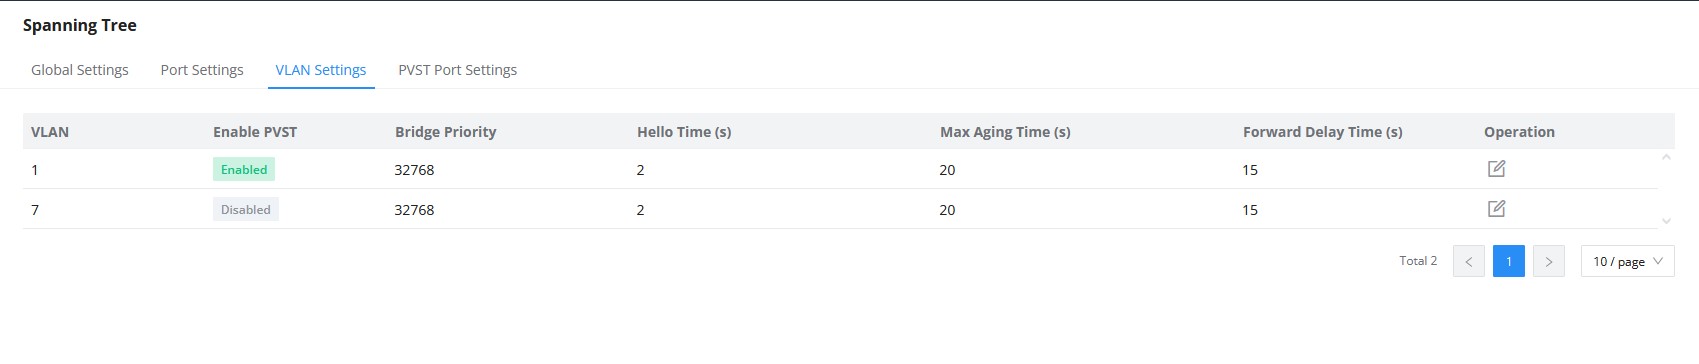
The below parameters are to be configured:
VLAN | Disaplays the VLAN on which the PVST rule will PVST protocol will be applied |
Enable PVST | Enables/disables PVST per VLAN |
Bridge Priority | Defines the bridge priority for the VLAN, valid range is 0-61440, default value is 32768. |
Hello Time (s) | Specify the Hello Time in seconds (the range is 1 -10). Default is 2. |
Max Aging Time (s) | Select The aging time of BPDU packets of the port (the range is 6 – 40). Default is 20. |
Forward Delay Time (s) | Specify the Forward Delay Time in seconds (the range is 4 -30). Default is 15. |
PVST Port Settings
The PVST Port settings defines the priority and path cost for each port of the switch , per each vlan,
It also displays, for each port, its role, designated Bridge ID, designated Port ID, and designated Path Cost.
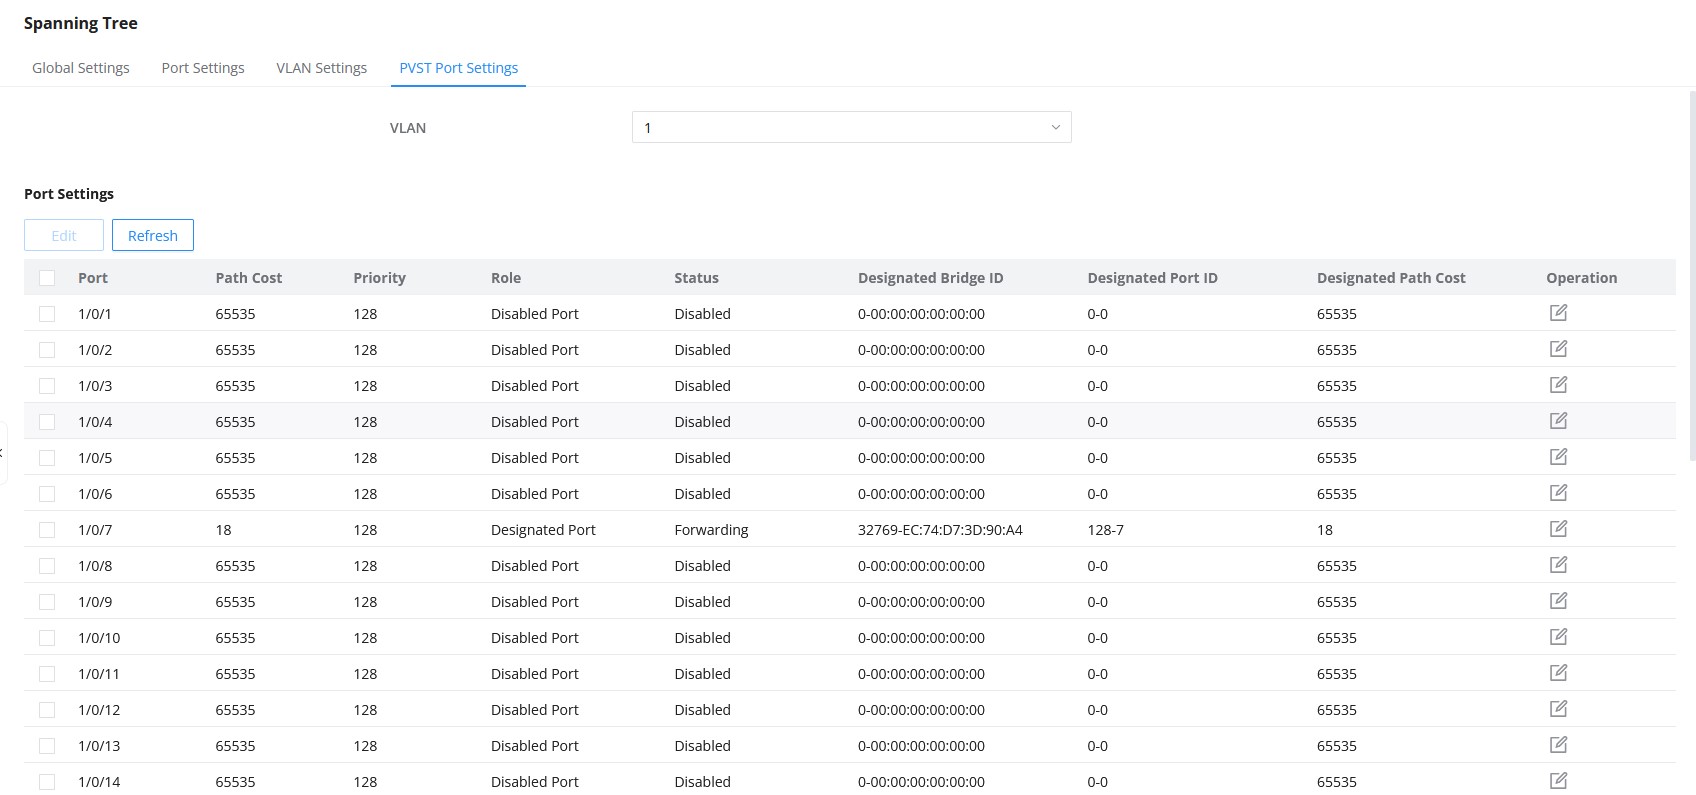
The parameters to be defined are
Port | Displays the port, or ports that the settings will be applied on. |
Priority | Displays the single port priority. valid range is 0-240 and the default value is 18. |
Path Cost | Configures the port path cost for the port on the specified spanning tree. The value must be an integer between 0-65535. The default value is 0, which means the path cost calculation will be performed automatically. |
IP
VLAN IP Interface
Hosts in different VLANs cannot communicate directly and need to be forwarded through routers or layer 3 switching protocols.
A VLAN interface is a virtual interface in Layer 3 mode and is mainly used to implement Layer 3 communication between VLANs, it does not exist on the device as a physical entity. Each VLAN corresponds to an interface by configuring an IP address for it, it can be used as the gateway address of each port in the VLAN so that packets between different VLANs can be forwarded to each other on Layer 3 routing through the VLAN interfaces. GWN switches support IPv4 interfaces as well as IPv6.
IPv4/IPv6 Interface
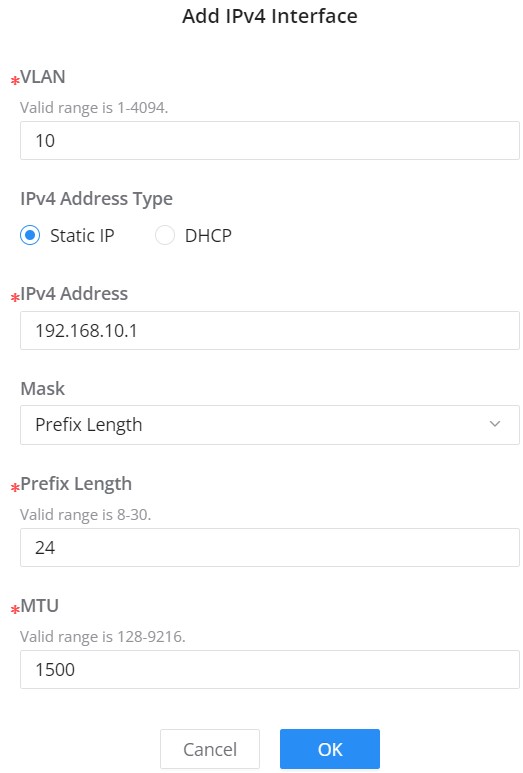
To add an IP Interface, please click on the “Add” button, refer to the figure below:
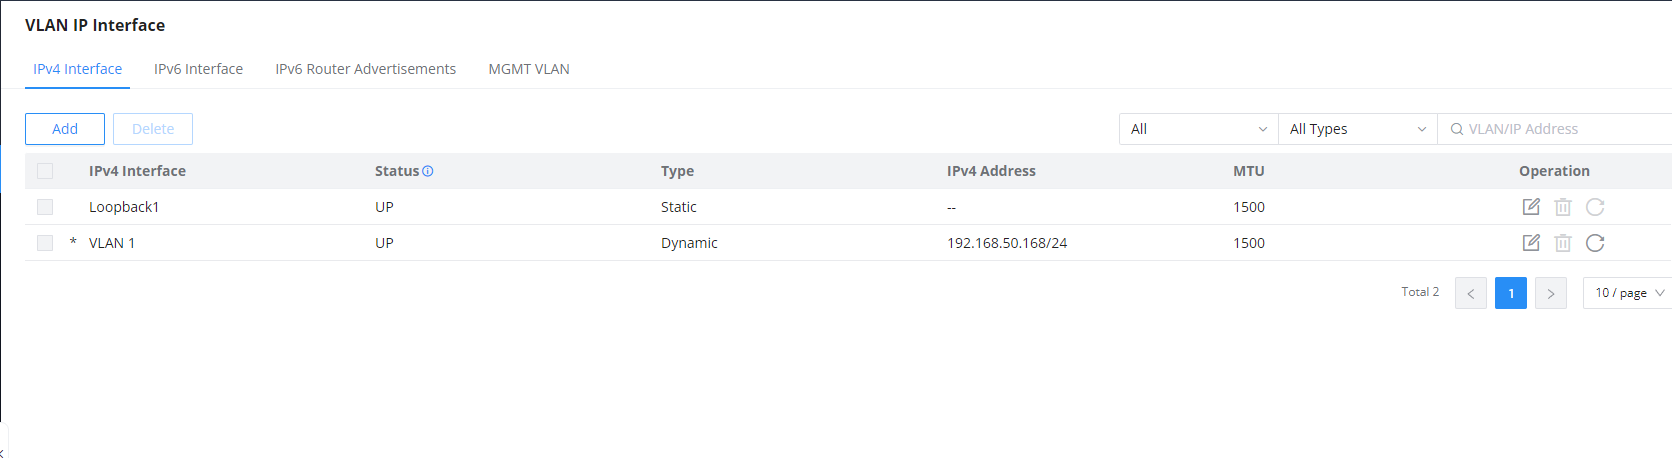
Use the “refresh icon” to request a new IP address from the DHCP server. This action will prompt a confirmation dialog; clicking “OK” will obtain a new IP address, which may change upon successful retrieval.

Address Type:
| Field or action | Description |
|---|---|
| IPv4 Address Type | Select Static IP to enter an address and mask, or DHCP to obtain the IPv4 settings automatically. |
| Gateway Priority | Displayed when DHCP is selected. Accepts 2 to 255; a lower value has higher priority. |
| MTU | Accepts 1280 to 9216 bytes. |
| Static mask length | When Mask Length is selected, the accepted range is 8 to 30. |
- If DHCP is selected: hosts will obtain IP addresses automatically from whatever DHCP pool configured from example like a router.
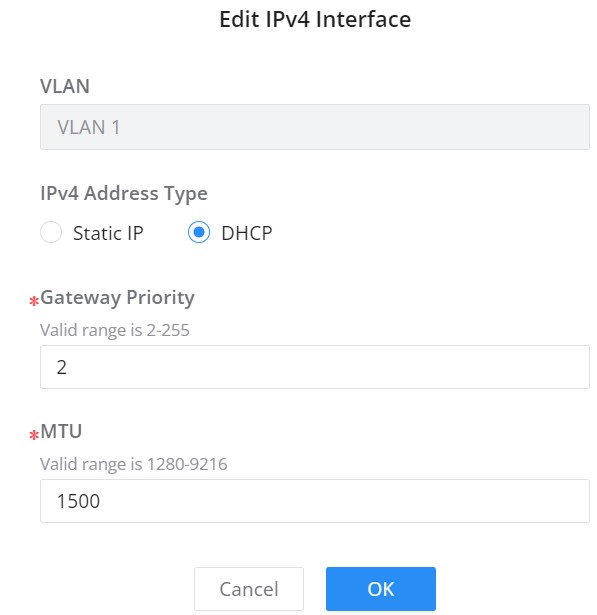

Gateway Priority: valid range from 2 [very important] to 255 [least important],
MTU (Maximum Transmission Unit): valid range is 1280-9216.
- If Static IP is selected: the user can specify the IPv4 or IPv6 manually.
IPv6 Router Advertisements
IPv6 Router Advertisements (RAs) are messages sent by routers to provide information to devices on the network, such as the default gateway, DNS servers, and network prefixes. These advertisements help devices configure their IP addresses and routing automatically without the need for manual configuration. In the VLAN IP Interface section, you can configure RAs for each VLAN to manage IPv6 network settings.

In the Edit IPv6 Router Advertisements screen, you can customize settings for a specific VLAN. This includes enabling or disabling the interface, setting route information, and configuring timeouts and lifetimes for the advertisements. You can also define IPv6 addresses and prefixes, adjust flags for additional configurations, and set the priority of the default route. This allows for fine-tuning the behavior of the advertisements to suit your network requirements.

MGMT VLAN
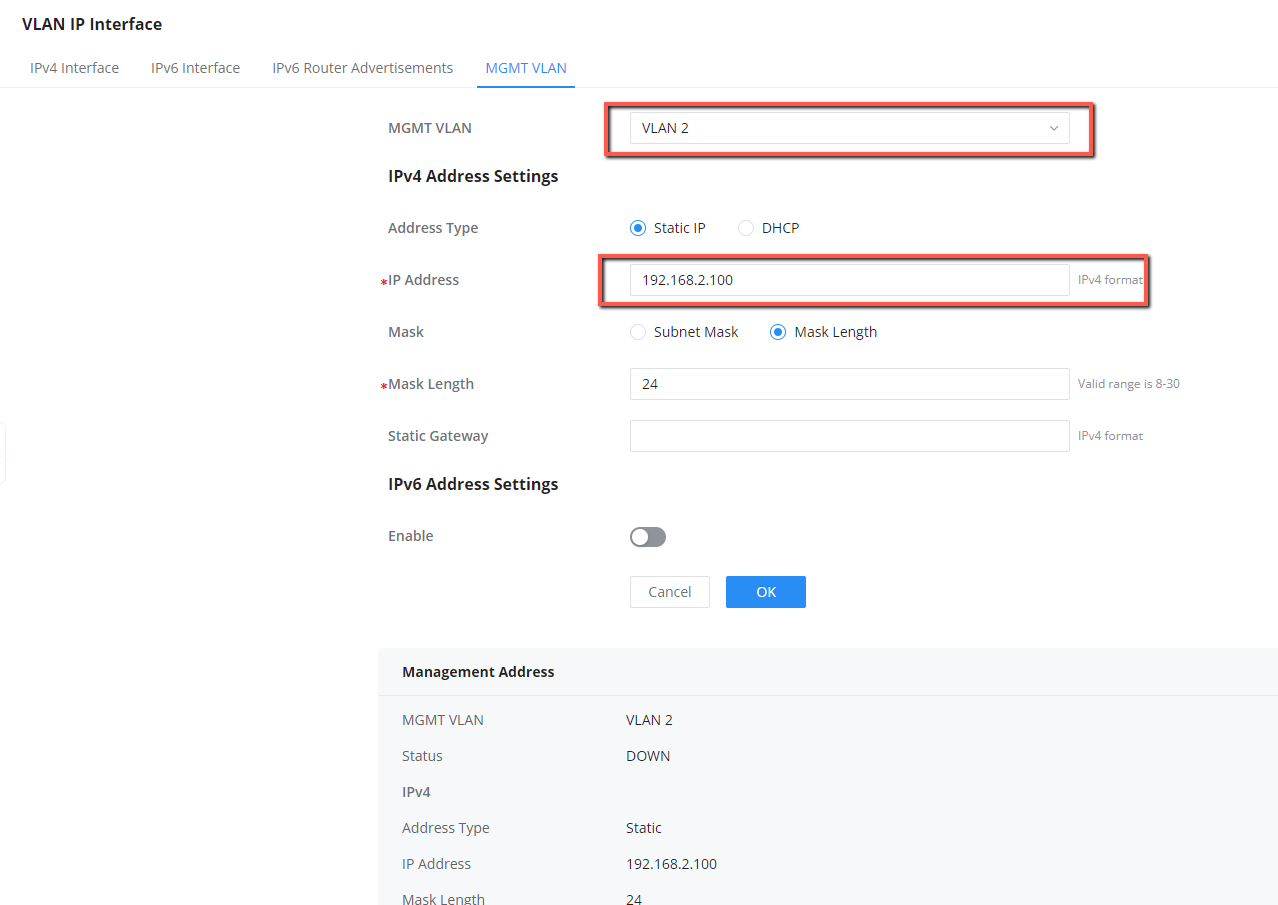
When you assign an IP address to the management VLAN interface, the system synchronizes this IP configuration with the corresponding VLAN interface in the device’s Layer 3 IP interface configuration. This ensures that the IP address used for managing the device is consistent with the VLAN’s routing and switching setup.
For example, if you configure the management VLAN with an IP address 192.168.2.100 on VLAN 2, this IP will also be reflected in the IP interface configuration for VLAN 2, ensuring both management and routing functions are aligned.
DHCP Server
When creating a VLAN IP Interface with a static IP, the user can link it with a DHCP Server for hosts to obtain IP addresses.
Please navigate to the Web UI → IP → DHCP Server page.
Step 1: Enable DHCP Server.

Step 2: on Address Pool Settings section, click on “Add” button to add a new address pool.
Add a pool range for the DHCP Server, then select the interface (VLAN).

In this section, the user can configure DHCP Options like the type, Service (for option 43), and option content. It’s also possible to add more DHCP Options by clicking on the “Add” icon as shown below:

The address table will displays the hosts (devices) MAC Addresses and the IP addresses when using the DHCP Server. Also it’s possible make a entry a static one by clicking on “Add as Static Binding IP” button.
| Field or action | Description |
|---|---|
| Address pool | Set Address Pool Name, enable state, and Type. Global pools use IP Pool Subnet and Mask Length; Interface pools use an interface and an IPv4 Pool range. |
| Lease and client settings | Configure Gateway, Duration (min) from 1 to 11520, DNS Server, WINS Server, and Netbios Node Type. |
| DHCP Option / Type / Option Content | Enter the option code, choose the content type, and enter Option Content. Hex content accepts 0 to 256 characters and must contain an even number of characters. |
| Address Table search | Use IPv4 Address/Client Name/Client MAC Address to filter leases. The table identifies the client MAC address, IPv4 address, lease type, remaining lease, and available operation. |

DHCP Relay
DHCP relay allows the switch to pass DHCP messages between clients and servers on different networks. Use it when one DHCP server must serve clients on multiple subnets or VLANs. A DHCP relay agent is a network device that can route between the client’s subnet and the server’s subnet. The relay agent gets the broadcast request from the client and sends it to the server, putting its own interface address as the gateway address (giaddr) field in the packet. This way, the server can tell which subnet the client is on and assign a suitable IP address. The server then sends the reply back to the relay agent, which passes it to the client.
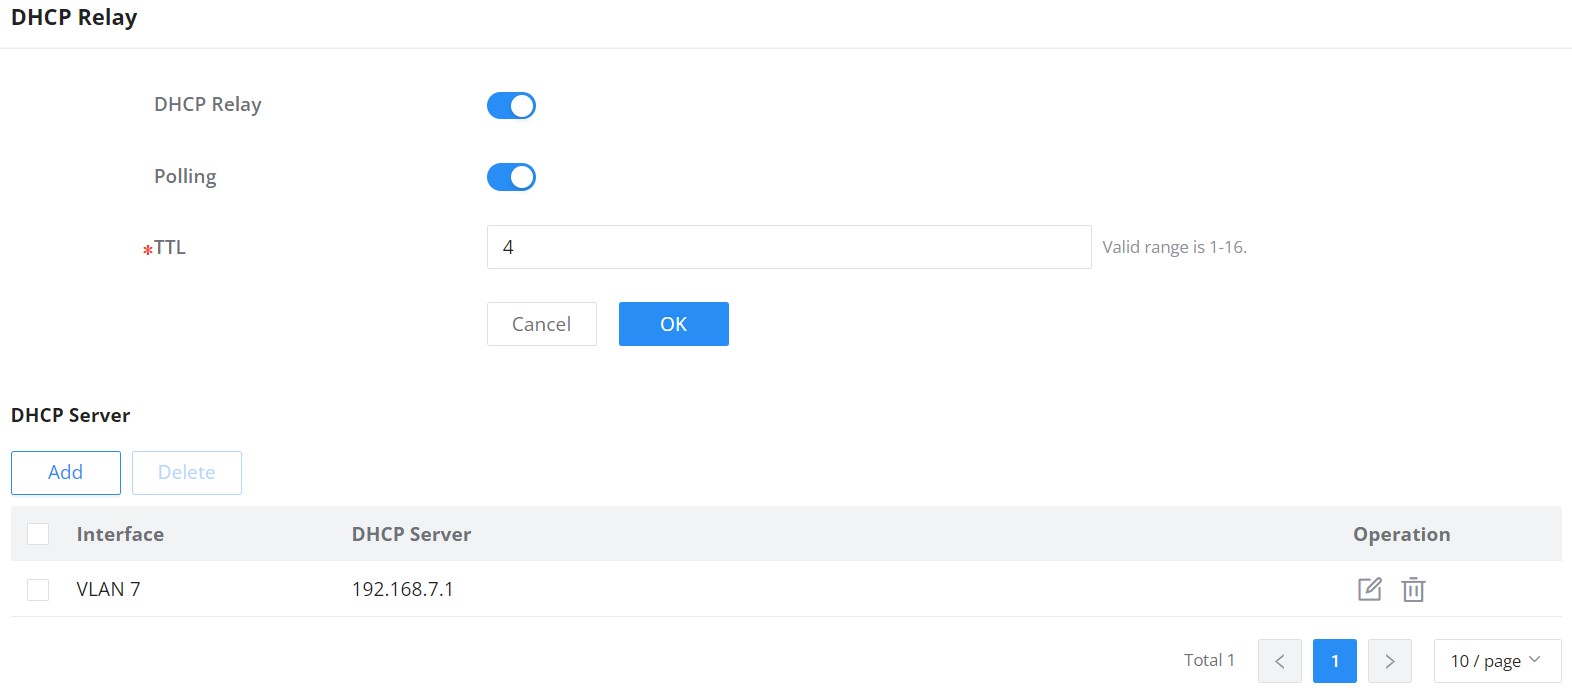
DHCP Relay | Set whether to enable the global DHCP relay function the default is off. |
Polling | Set whether to enable the polling function of the DHCP relay disabled by default. |
TTL | Set the TTL value of the DHCP request message after being forwarded by the DHCP relay layer 3. the value is an integer from 1 to 16 , and the default is 4 . |
DHCP Server | |
Interface | Select from the existing VLAN interfaces. |
DHCP Server | Set the address of the DHCP server. Note: The DHCP server address cannot be the interface IP address of the DHCP relay gateway , otherwise the DHCP client cannot obtain an IP address. |
DHCP Relay
ARP Table
Address Resolution Protocol ARP is a protocol used to resolve IP addresses to MAC addresses. In a local area network, when a host or three-layer network device has data to send to another host or three-layer network device, it needs to know the other party’s network layer address (IP address) because IP addresses must be encapsulated into frames to be sent over the physical network, the sender also needs to know the receiver’s actual physical address (MAC address), which requires a mapping from IP to MAC address. ARP implements the resolution of IP addresses into MAC addresses. A host or Layer 3 network device maintains an ARP table to store the relationship between IP addresses and MAC addresses. ARP entries include dynamic ARP entries and static ARP entries.
Dynamic ARP entry: It is automatically generated and maintained by the ARP protocol through ARP packets, can be aged out, can be updated by new ARP packets, and can be overwritten by static ARP entries. When the aging time is reached and the interface is down, the device immediately deletes the dynamic ARP entry in response.
Static ARP entry: A fixed mapping relationship between IP addresses and MAC addresses manually established by the network administrator, which will not be aged out and will not be overwritten by dynamic ARP entries, which can ensure the security of network communication. Static ARP entries can restrict the local device to use only the specified MAC address when communicating with the peer device with the specified IP address, in this case, the attack packet cannot modify the mapping relationship between the IP address and the MAC address in the ARP table of the local device thus the normal communication between the local device and the peer device is protected.
To configure the ARP Table, please navigate to Web UI → IP → ARP Table.
| Field or action | Description |
|---|---|
| Aging Time (s) | Sets dynamic-entry aging from 60 to 21600 seconds. |
| Table actions | Use Add, Refresh, Add as Static ARP, or Delete. Select a learned entry before converting it to a static entry. |
| Filter and search | Filter by All Types or use VLAN/IP Address/MAC Address search. |
| Add Static ARP | Select the VLAN, enter the IP Address, and enter a unicast MAC Address. |
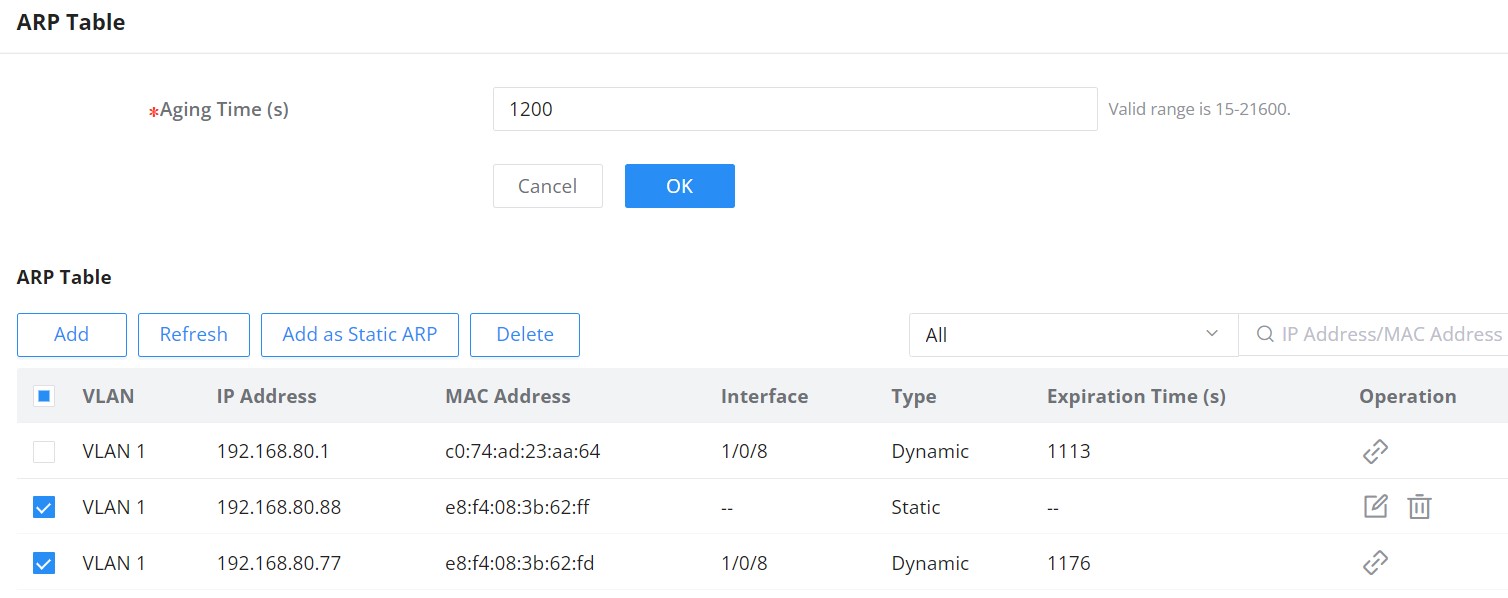
Aging time (seconds): Set the aging time of dynamic ARP entries. After the aging time expires, dynamic ARP entries are automatically deleted. The value range is an integer from 15 to 21600, and the default is 1200 seconds.
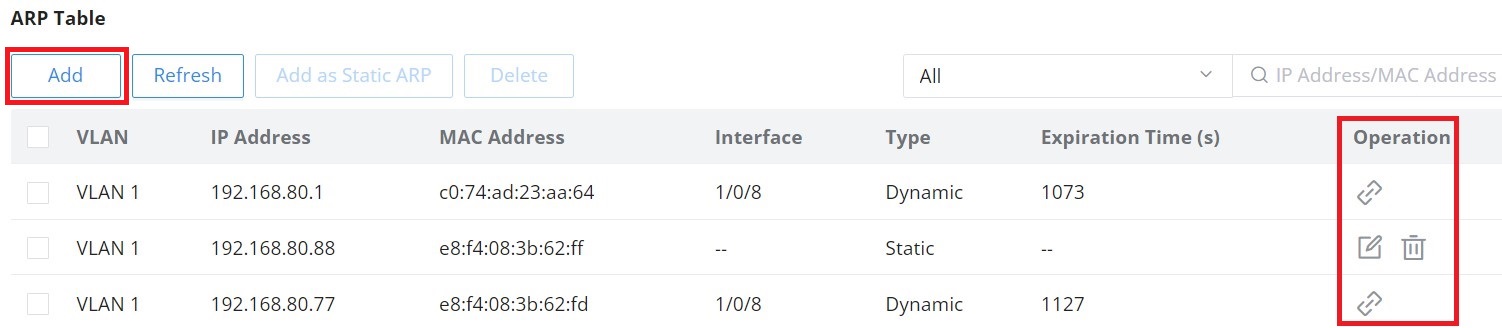
- Click on “Link” icon to make the dynamic entry as a static entry.
- Click on “Delete” icon to delete the static entry.
- Click on the “Modify” icon to modify the static entry
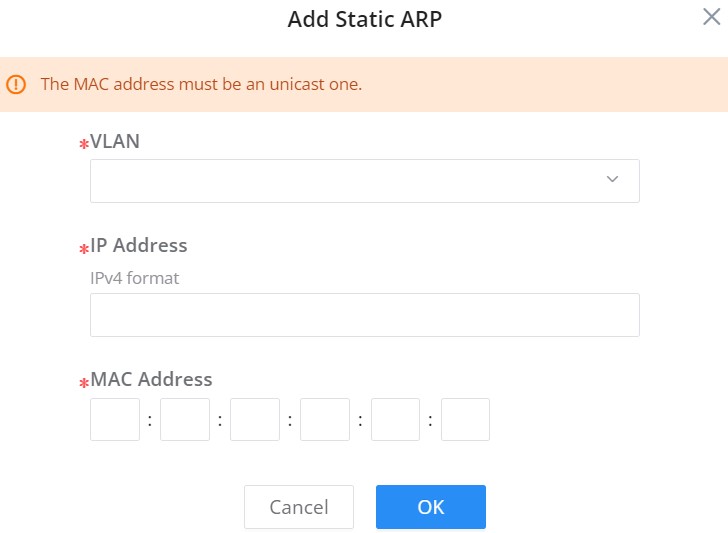
It’s also possible to add a static ARP entry manually by clicking on the “Add” button, then specify the VLAN, IP Address, and MAC Address combination.
Neighbor Discovery
Neighbor Discovery Protocol (NDP) is an important basic protocol in the IPv6 protocol system it replaces the ARP and ICMP router discovery of IPv4. It defines the use of ICMPv6 packets to achieve address resolution, neighbor unreachability detection, duplicate address detection, router discovery, redirection, ND proxy, and other functions.
IPv6 address auto-configuration and router discovery rely on two kinds of ICMPv6 messages: RS (Router Solicitation) and RA (Router Advertisement). Hosts send RS messages to ask routers on the same link to send RA messages right away. Routers send RA messages to let hosts know they are there and give them information like IPv6 prefixes, hop limit, MTU, and configuration flags.
To configure ND please navigate to Web UI → IP → Neighbor Discovery.
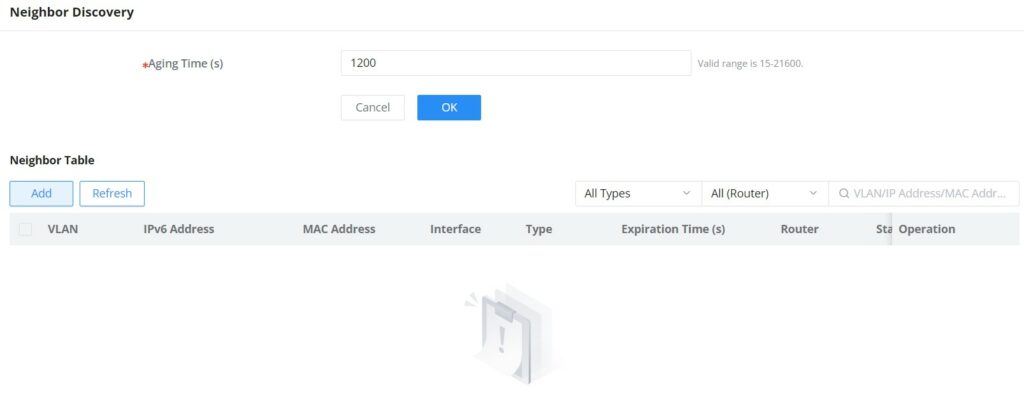
Aging time (seconds): Set the aging time of dynamic neighbor entries. After the aging time expires, the dynamic neighbor entry is automatically deleted. The value range is an integer from 15 to 21600, and the default is 1200 seconds.
Click on “Refresh” button to refresh the list for dynamic entries or click on “Add” button to add a static entry, refer to the figure below:
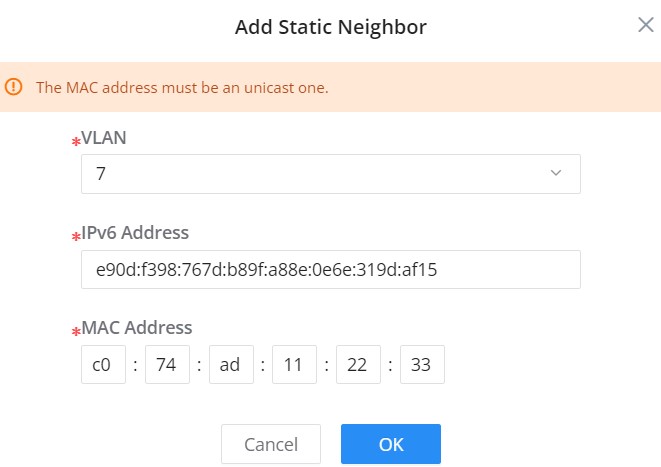
Select the VLAN from the drop-down list then enter the unicast IPv6 address and MAC address then click on “OK” button.
DNS
Domain Name System DNS provides translation services between domain names and IP addresses. Each switch acts as a DNS client. When users perform certain applications on the device (such as Telnet to a device or host), they can directly use a memorable and meaningful domain name, and resolve the domain name to the correct address through the domain name system.
DNS domain name resolution is divided into static domain name resolution and dynamic domain name resolution which can be used together when parsing domain names. If the static domain name resolution is unsuccessful, then dynamic domain name resolution will be used, since dynamic domain name resolution may take a certain amount of time and requires the cooperation of the domain name server, some commonly used domain names can be put into the static domain name resolution table, which can greatly improve the effect of domain name resolution.
Global Settings
On this page, the user can designate the switch as a DNS client to resolve DNS names to IP addresses through one or more configured DNS servers. It’s enabled by default.
To configure DNS on the switch, navigate to Web UI → IP → DNS, then click on the Global Settings tab.
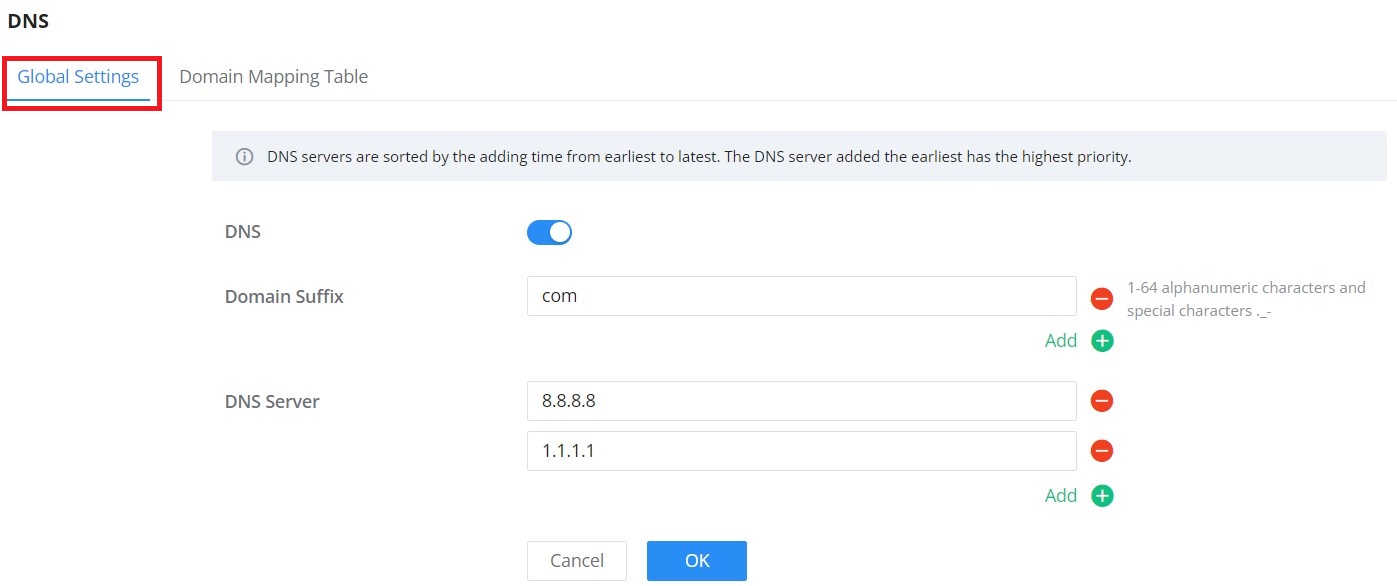
Up to 8 Domain Suffixes and 8 DNS Servers can be added. To add a Domain Suffex or DNS Server click on “+” icon and to delete click on “–” icon.
Domain Mapping Table
To add a static DNS or to view the Dynamic ones, click on the Domain Mapping Table tab.
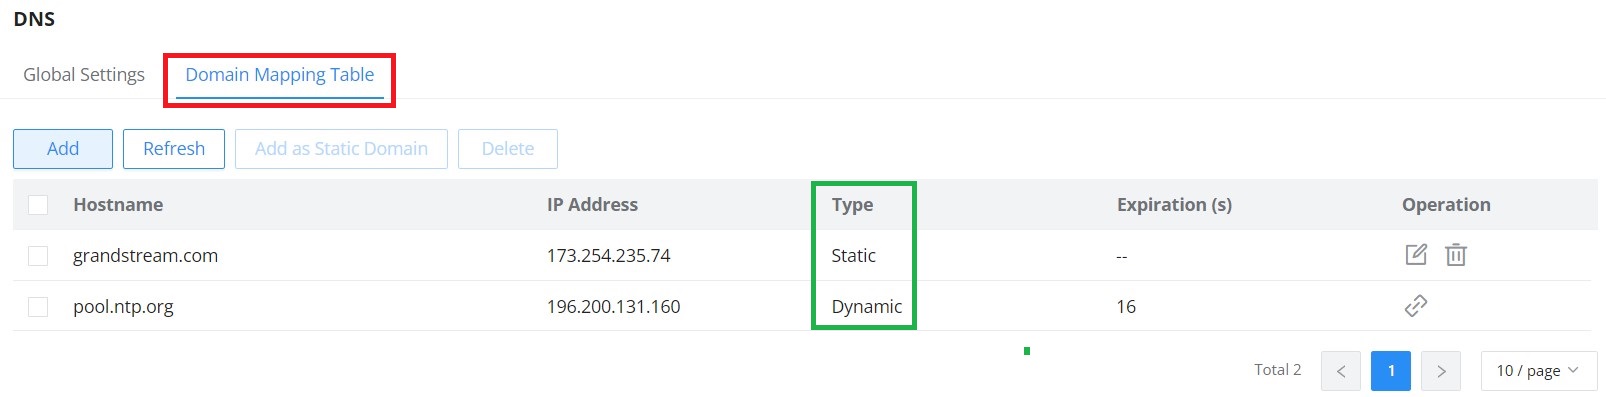
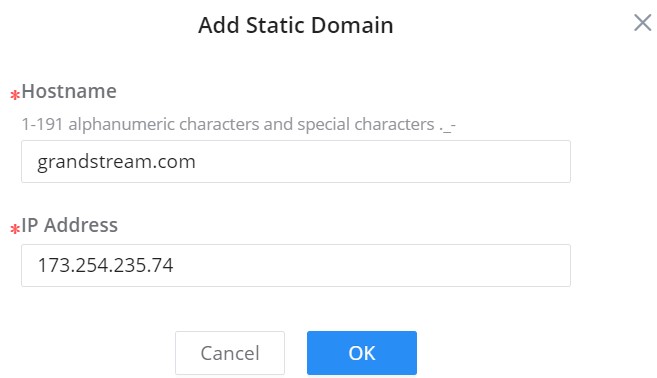
Click on “Add” button to add a new static DNS entry.
The user can also select the dynamic domains and then click on “Add as a static domain” button or icon to make them as static ones.
MULTICAST
IP multicast is a technique for one-to-many communication over an IP infrastructure in a network. To avoid the incoming data broadcasting to all GE/LAG ports, multicast is useful to transfer the data/message to specified GE/LAG ports for IGMP snooping or MLD Snooping. When the Switch receives a message “subscribed” by the client, it must decide to transfer the data to specified GE/LAG ports according to the location of the client (subscribed member).
IGMP Snooping
As an IPv4 Layer 2 multicast protocol, IGMP snooping is the process of listening to Internet Group Management Protocol (IGMP) network traffic. The feature allows a network switch to listen in on the IGMP conversation between hosts and routers. By listening to these conversations the switch maintains a map of which links need which IP multicast streams. Multicasts may be filtered from the links which do not need them and thus controls which ports receive specific multicast traffic.
IGMP Snooping Global Settings
Under IGMP Snooping → Global VLAN Settings, Add, Edit, and Delete are separate table actions for managing VLAN-specific snooping settings.
This page allows the user to enable/disable IGMP Snooping function, select snooping version, and enable/disable snooping report suppression also select the Multicast Forward Mode and what to do with Unknown Multicast Packet.
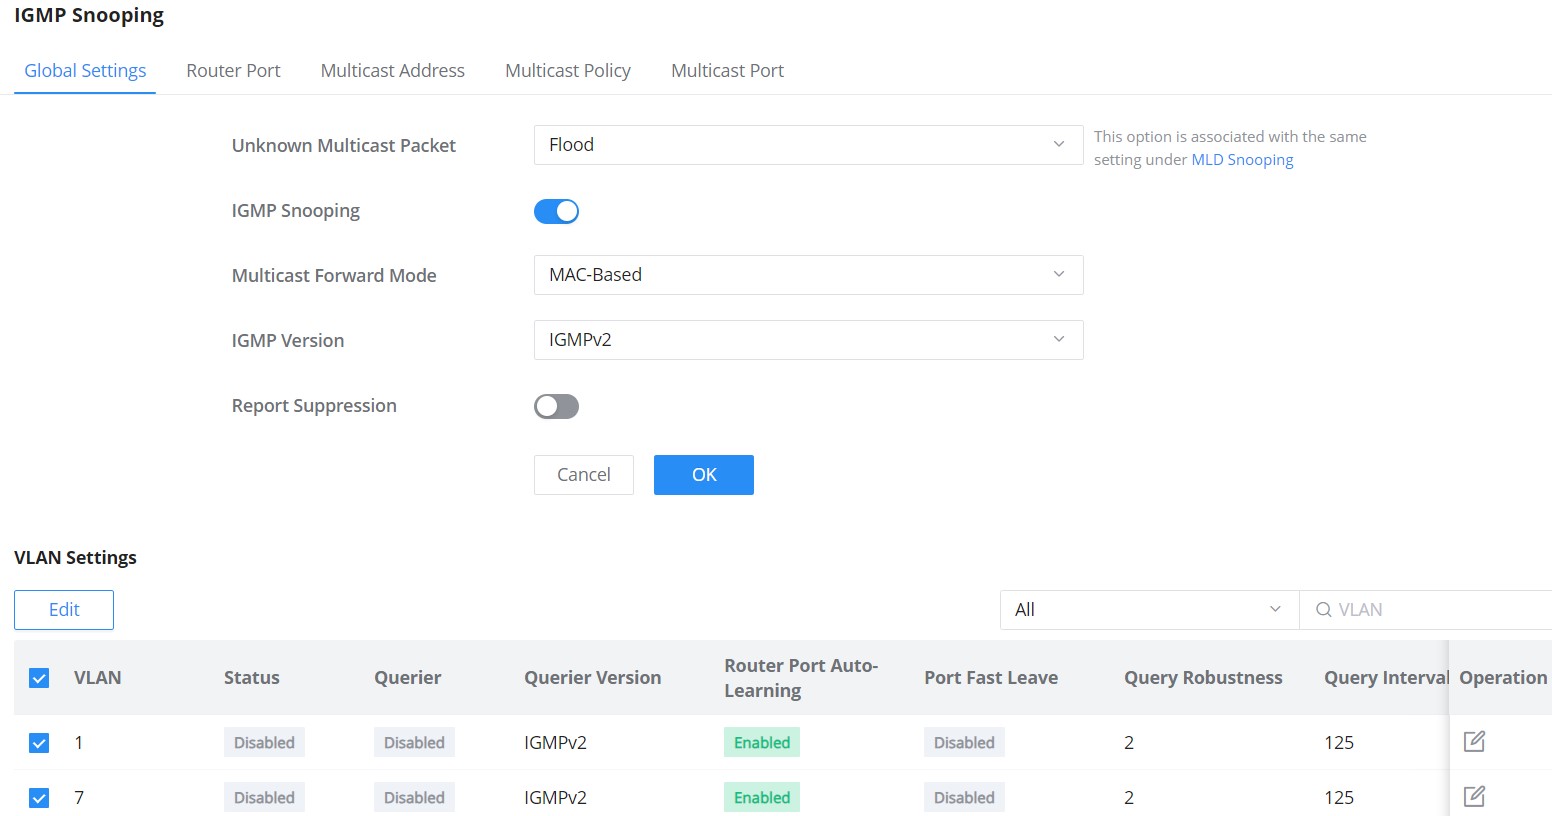
Unknown Multicast Packet | Select an action for switch to handle with unknown multicast
|
IGMP Snooping | Enable or disable GlobaI IGMP Snooping |
Multicast Forward Mode | Set the Multicast Forward Mode.
|
IGMP Version | Select the IGMP Version. |
Report Suppression | Enable or disable the switch to handle IGMP reports |
IGMP Snooping Global Settings
The user can also Enable/Disable IGMP Snooping and IGMP Snooping Querier per VLAN and much more.
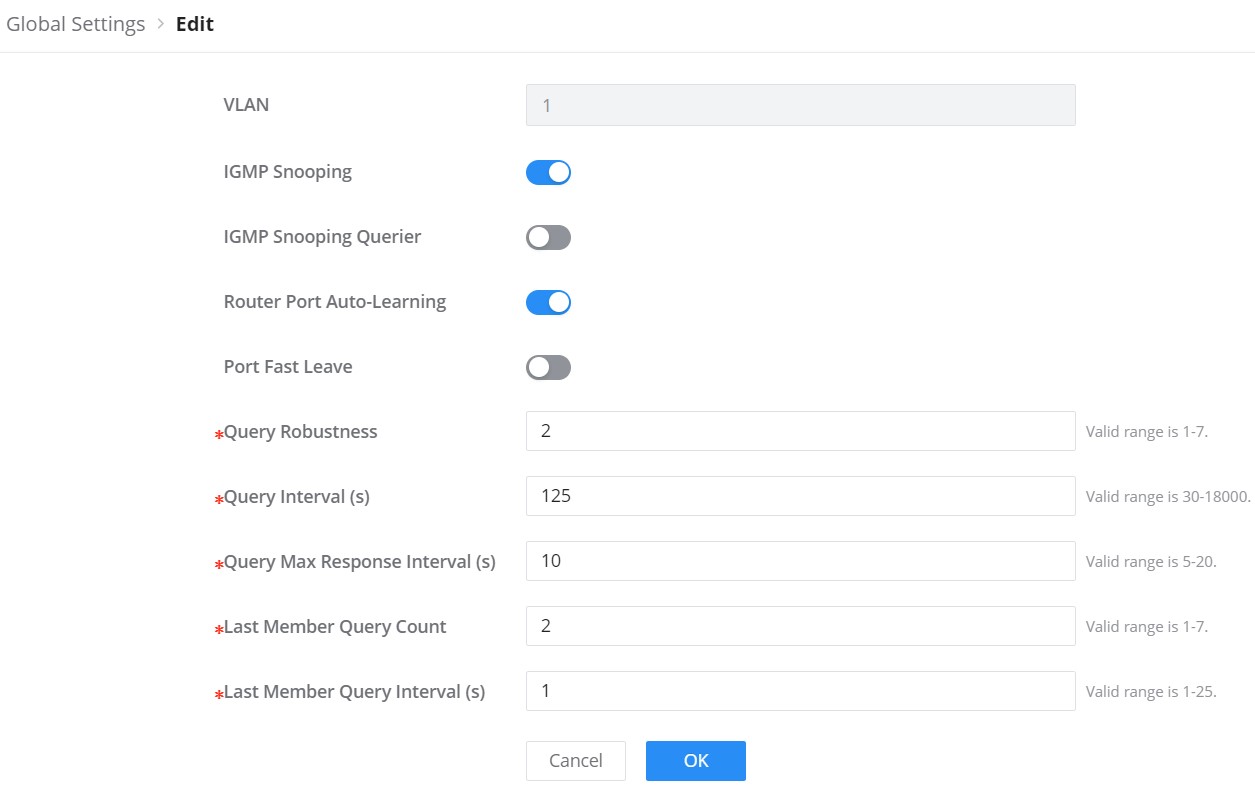
VLAN | Displays the selected VLAN |
MLD Snooping | Click on the toggle button to enable MLD Snooping for the selected VLAN. |
MLD Snooping Querier | Click the toggle button to enable the MLD Snooping Querier. |
MLD Snooping Querier Version | Select from the drop-down list the MLD Snooping Querier Version. |
Router Port Auto-Learning | Click on the toggle button to learn router port by MLD query. |
Port Fast Leave | Select Enable/Disable Fast Leave feature for the desired port. Note: If Fast Leave is enabled for a port, the switch will immediately remove this port from the multicast group upon receiving MLD leave messages. |
Query Robustness | Set a number which allows tuning for the expected packet loss on a subnet. The valid range is 1-7 |
Query Interval (s) | Set the interval of querier send general query. |
Query Max Response Interval (s) | It specifies the maximum allowed time before sending a responding report. Note: The valid range is 5-20 in seconds. |
Last Member Query Count | After quering for specified times and still not receiving any response from the subscribed member, GWN7806(P) series switches will stop transmitting data to the related GE port(s). Note: The valid range is 1-7 |
Last Member Query Interval (s) | Set The maximum time interval between counting each member query message with no responses from any subscribed member. Note: The valid range is 1-25 in seconds |
IGMP Snooping Edit VLAN
IGMP Snooping Router Port
This page shows the IGMP querier router known to this switch. Click on “Add” to add another one or Click on “Edit” icon to modify already created one.
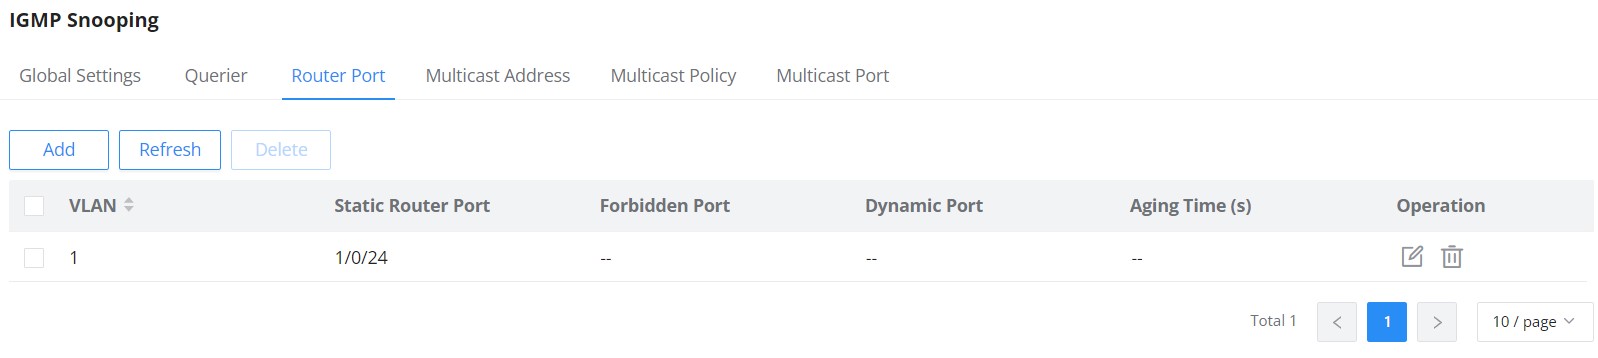
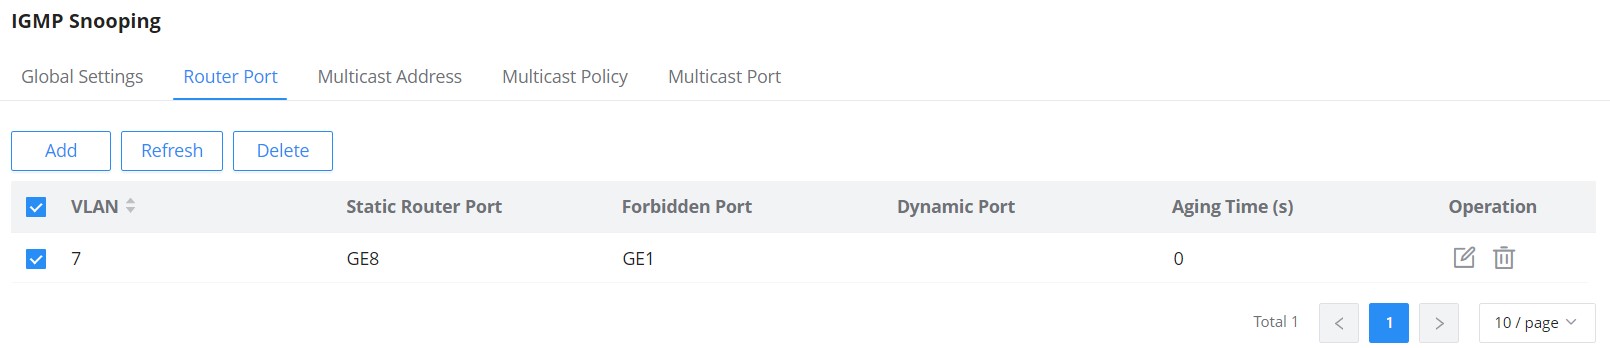
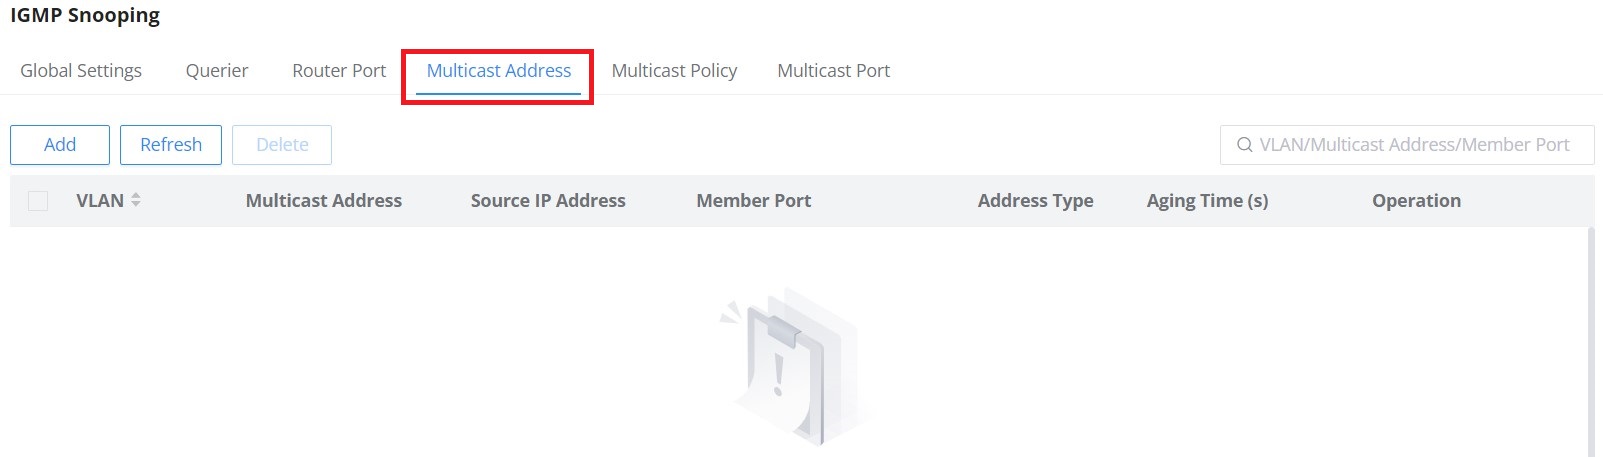
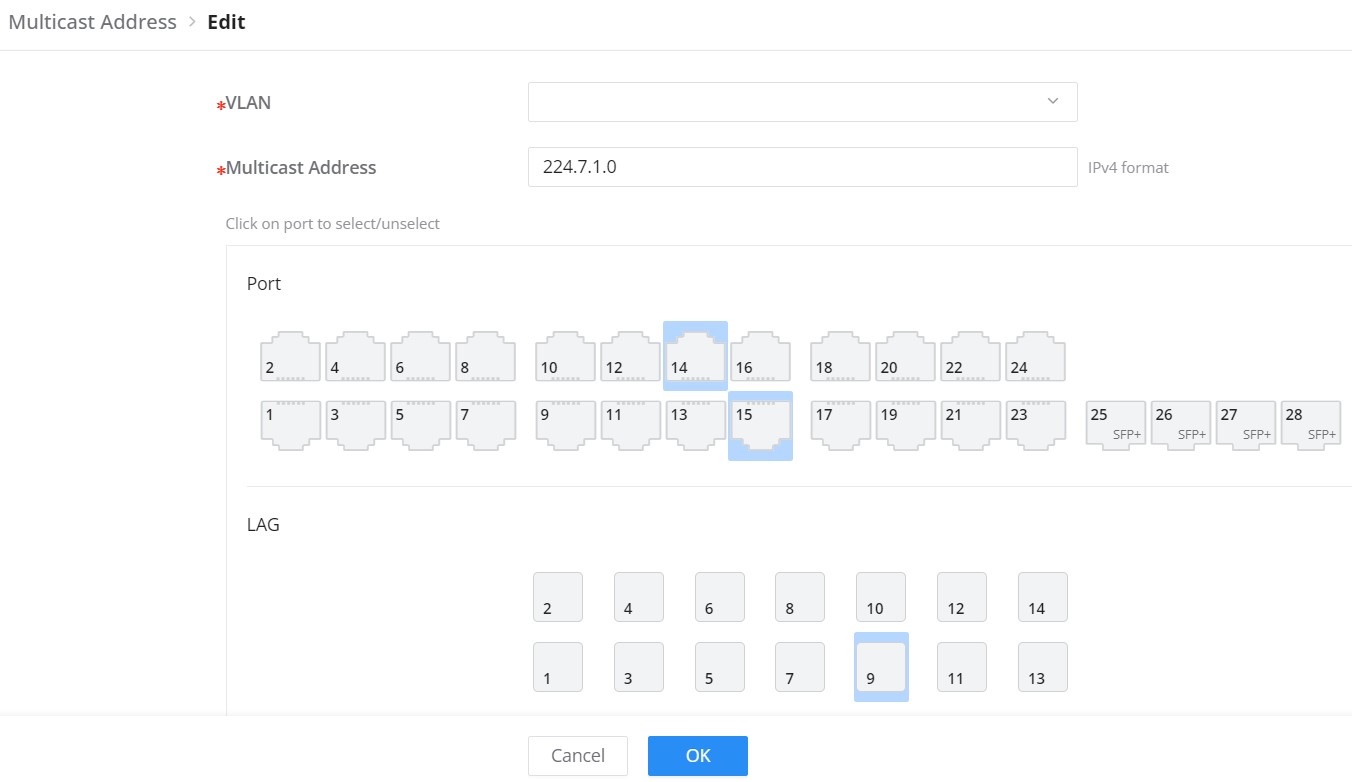
IGMP Snooping Multicast Address
Dynamic multicast addresses will be listed here and the user can also add static multicast address entries based on VLAN by clicking on “Add” button or click “Edit”
 icon to edit.
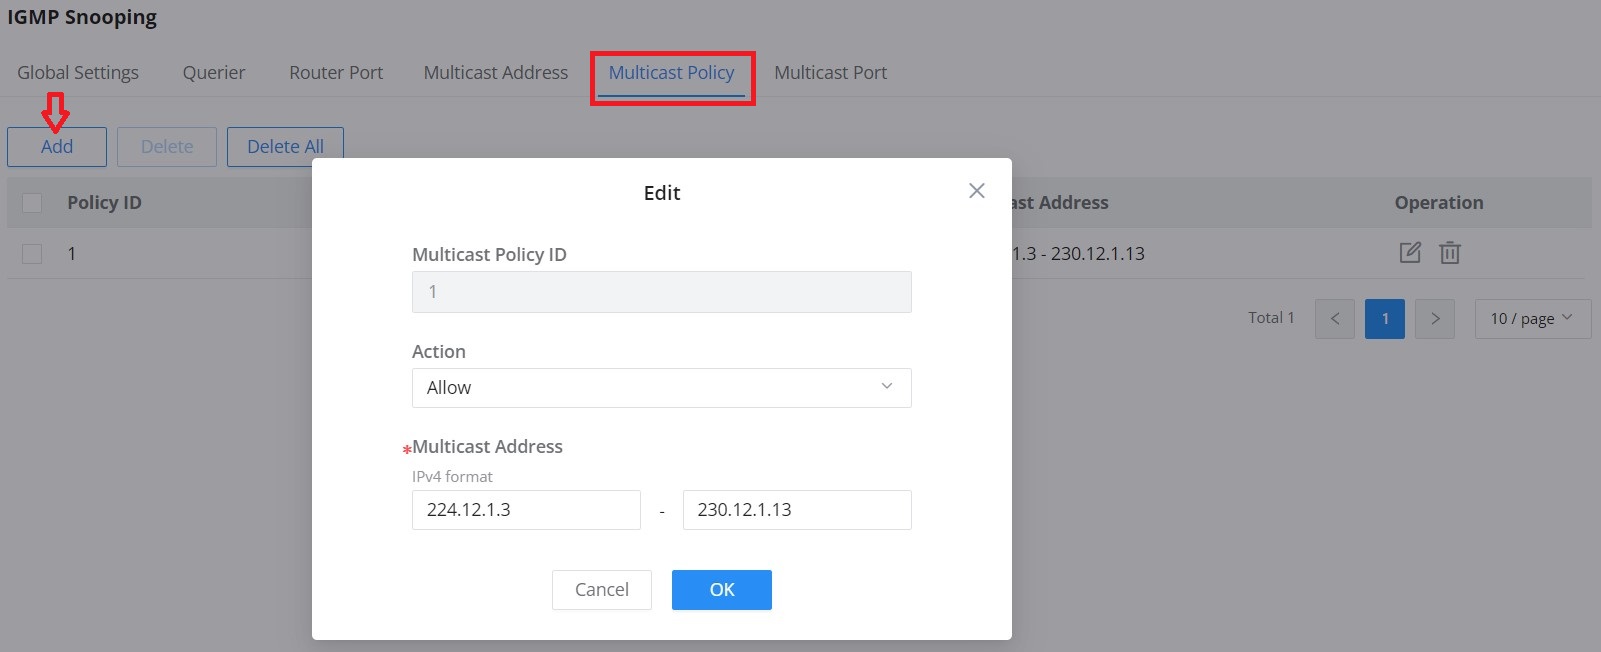
IGMP Snooping Multicast Policy
In this page, the user can add a Multicast Policy up to 128 Policy ID to Allow or Reject a range of Multicast Addresses.
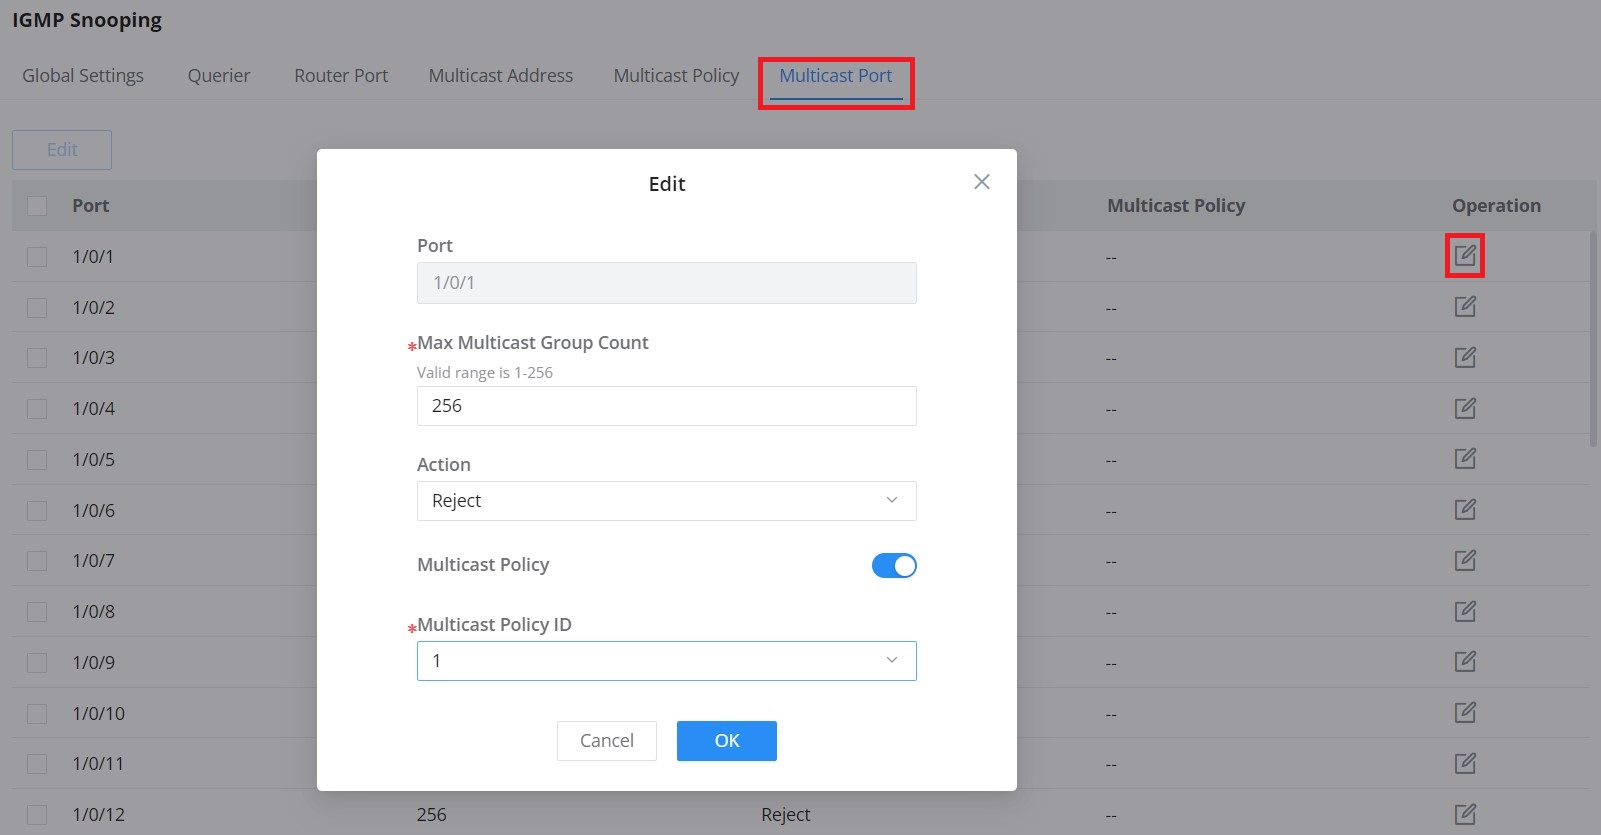
IGMP Snooping Multicast Port
Once the Multicast Policy is created, the user is able to apply this policy on a port.
MLD Snooping
| Field or action | Description |
|---|---|
| Global VLAN Settings | Use the separate Add, Edit, and Delete actions to manage VLAN-specific settings. |
| Multicast Address actions | Use Add, Refresh, and Delete. |
| Search | Use VLAN/Multicast Address/Member Port to filter the list. |
| Columns | The list shows VLAN, multicast address, source IP address, member port, address type, aging time, and operation. |
MLD Snooping Global Settings
As an IPv6 Layer 2 multicast protocol, MLD Snooping maintains the outgoing port information of multicast packets by listening to the multicast protocol packets sent between Layer 3 multicast devices and user hosts, so as to manage and control multicast data . Forwarding of packets at the data link layer. When an MLD protocol packet transmitted between a host and an upstream Layer 3 device passes through a Layer 2 device, MLD Snooping analyzes the information carried in the packet, establishes and maintains a Layer 2 multicast forwarding table based on the information, and guides multicast data in the data stream.
Global Settings page give the user the ability to enable MLD Snooping as well as selecting Multicast Forward Mode etc.

Unknown Multicast Packet | Select an action for switch to handle with unknown multicast
Note: This option is associated with the same one IGMP Snooping. |
MLD Snooping | Enable or disable GlobaI MLD Snooping |
Multicast Forward Mode | Set the Multicast Forward Mode.
|
MLD Version | Select the MLD Version. |
Report Suppression | Enable or disable the switch to handle MLD reports |
MLD Snooping Global Settings
Once Global MLD Snooping is enabled, then the user can enable more settings per VLAN.
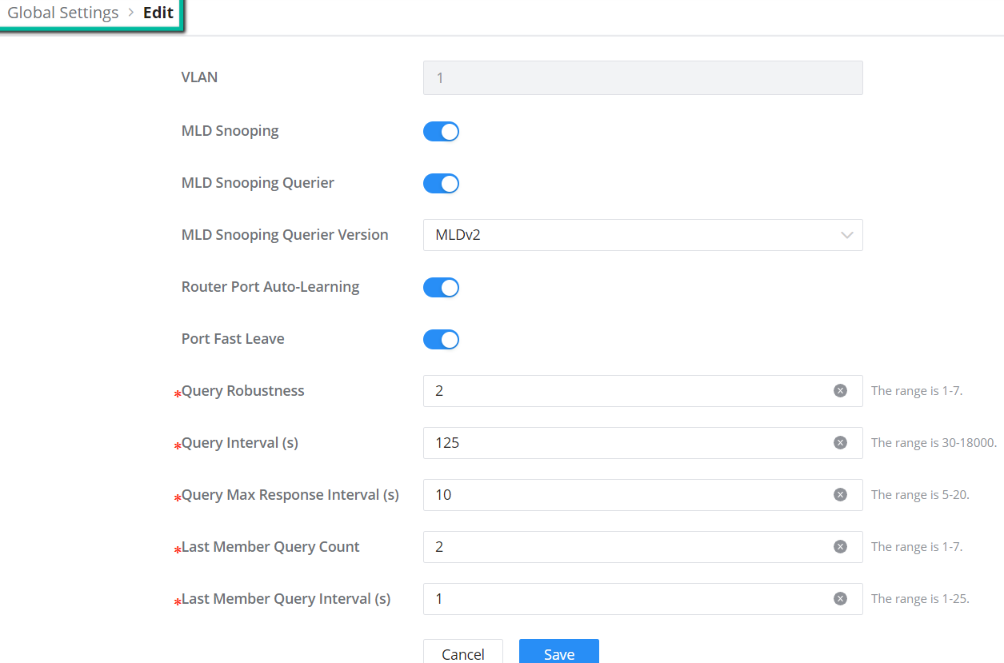
VLAN | Displays the selected VLAN |
MLD Snooping | Click on the toggle button to enable MLD Snooping for the selected VLAN. |
MLD Snooping Querier | Click the toggle button to enable the MLD Snooping Querier. |
MLD Snooping Querier Version | Select from the drop-down list the MLD Snooping Querier Version. |
Router Port Auto-Learning | Click on the toggle button to learn router port by MLD query. |
Port Fast Leave | Select Enable/Disable Fast Leave feature for the desired port. Note: If Fast Leave is enabled for a port, the switch will immediately remove this port from the multicast group upon receiving MLD leave messages. |
Query Robustness | Set a number which allows tuning for the expected packet loss on a subnet. The valid range is 1-7 |
Query Interval (s) | Set the interval of querier send general query. |
Query Max Response Interval (s) | It specifies the maximum allowed time before sending a responding report. Note: The valid range is 5-20 in seconds. |
Last Member Query Count | After quering for specified times and still not receiving any response from the subscribed member, the switch will stop transmitting data to the related GE port(s). Note: The valid range is 1-7 |
Last Member Query Interval (s) | Set The maximum time interval between counting each member query message with no responses from any subscribed member. Note: The valid range is 1-25 in seconds |
MLD Snooping – Edit VLAN
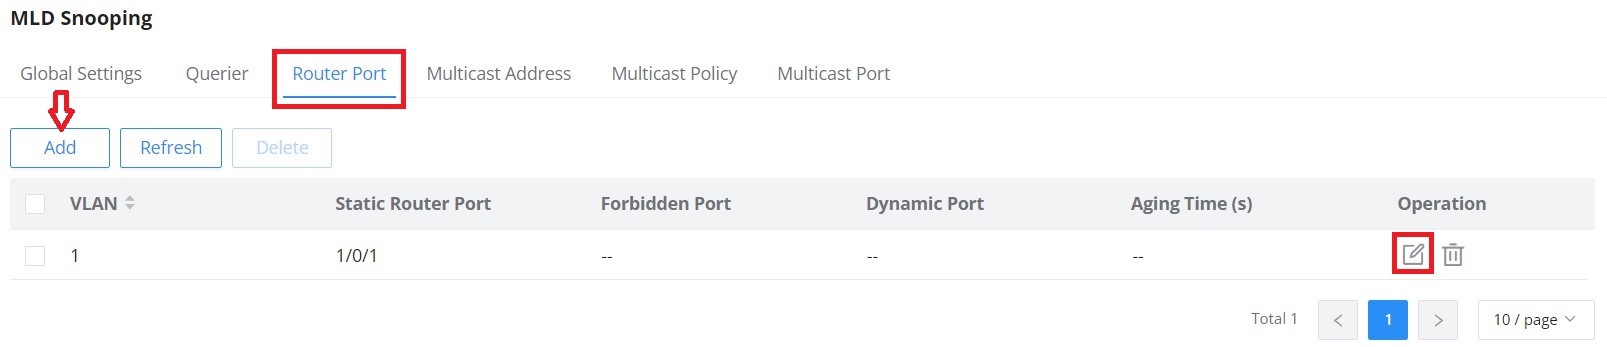
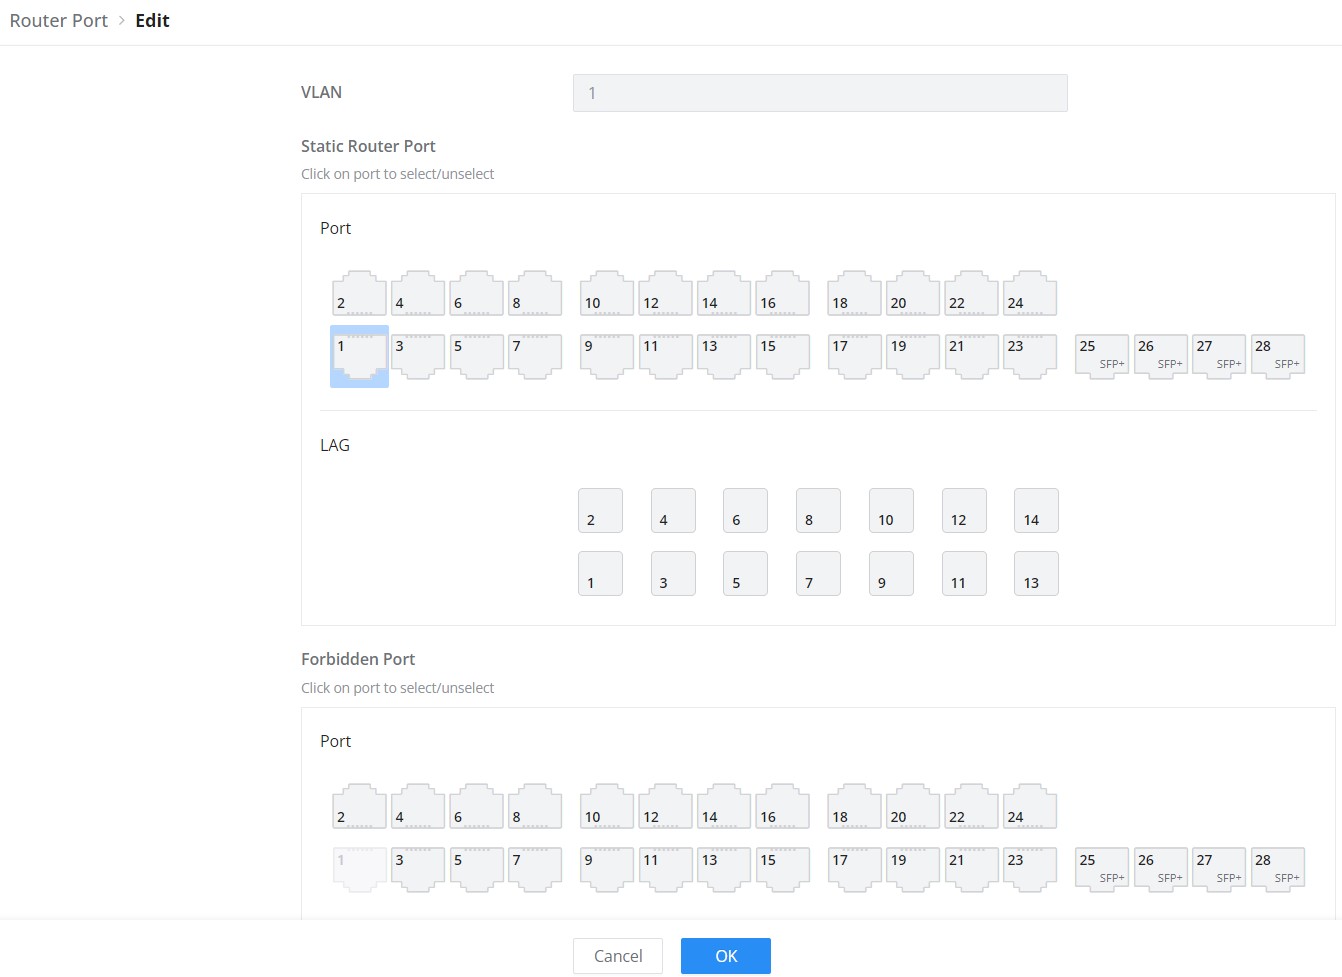
MLD Snooping Router Port
If the router port is statically configured, the Layer 2 device will also forward the MLD report and leave message to the static router port. If a static member port is configured, the interface will be added as the outgoing interface in the forwarding table. After a Layer 2 multicast forwarding table entry is established on a Layer 2 device, when the Layer 2 device receives a multicast data packet, it searches for the forwarding table according to the VLAN to which the packet belongs and the destination address of the packet (that is, the IPv6 multicast group address). Whether the item has the corresponding “outbound interface information”. If it exists, the packet is sent to all multicast group member ports; if it does not exist, the packet is discarded or broadcast in the VLAN.
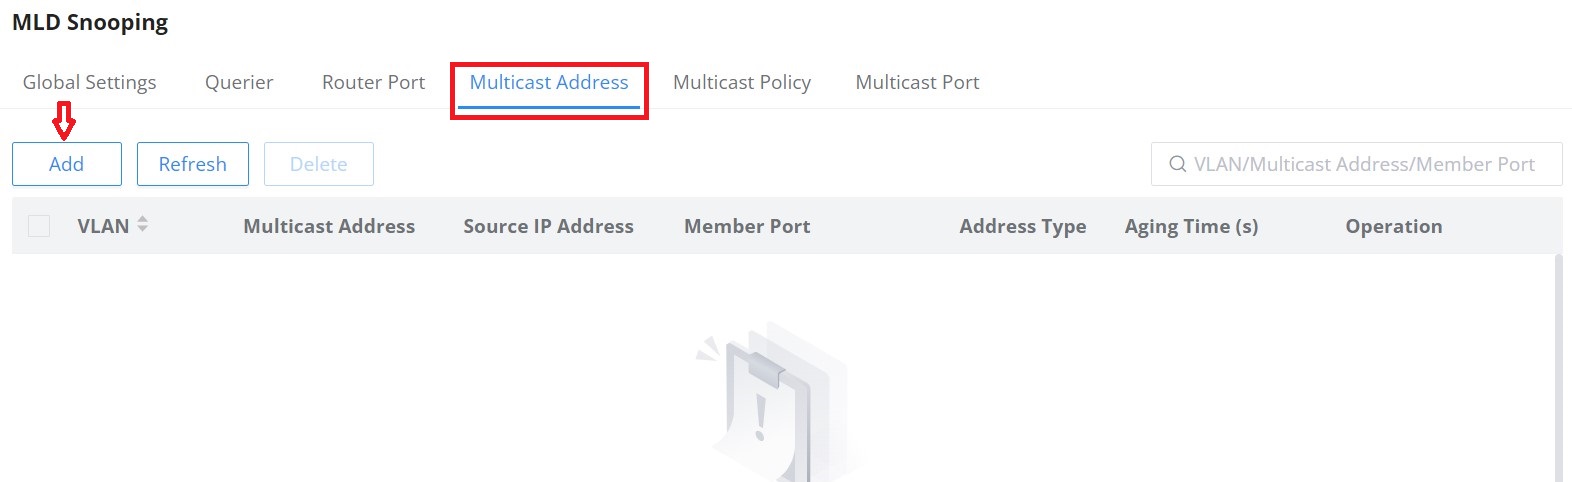
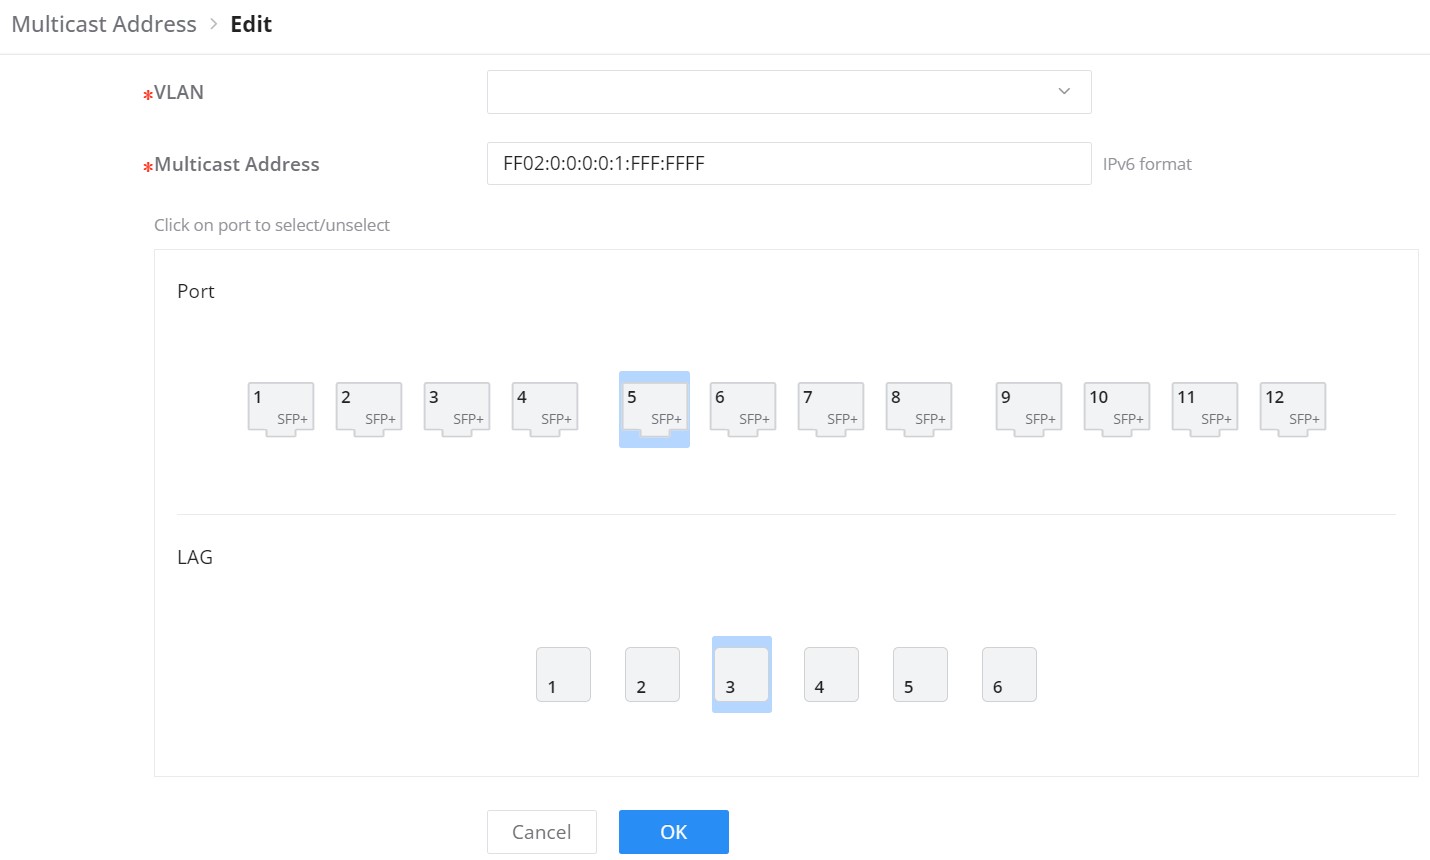
MLD Snooping Multicast Address
The switches also support adding static multicast addresses by specifying the VLAN and member port.
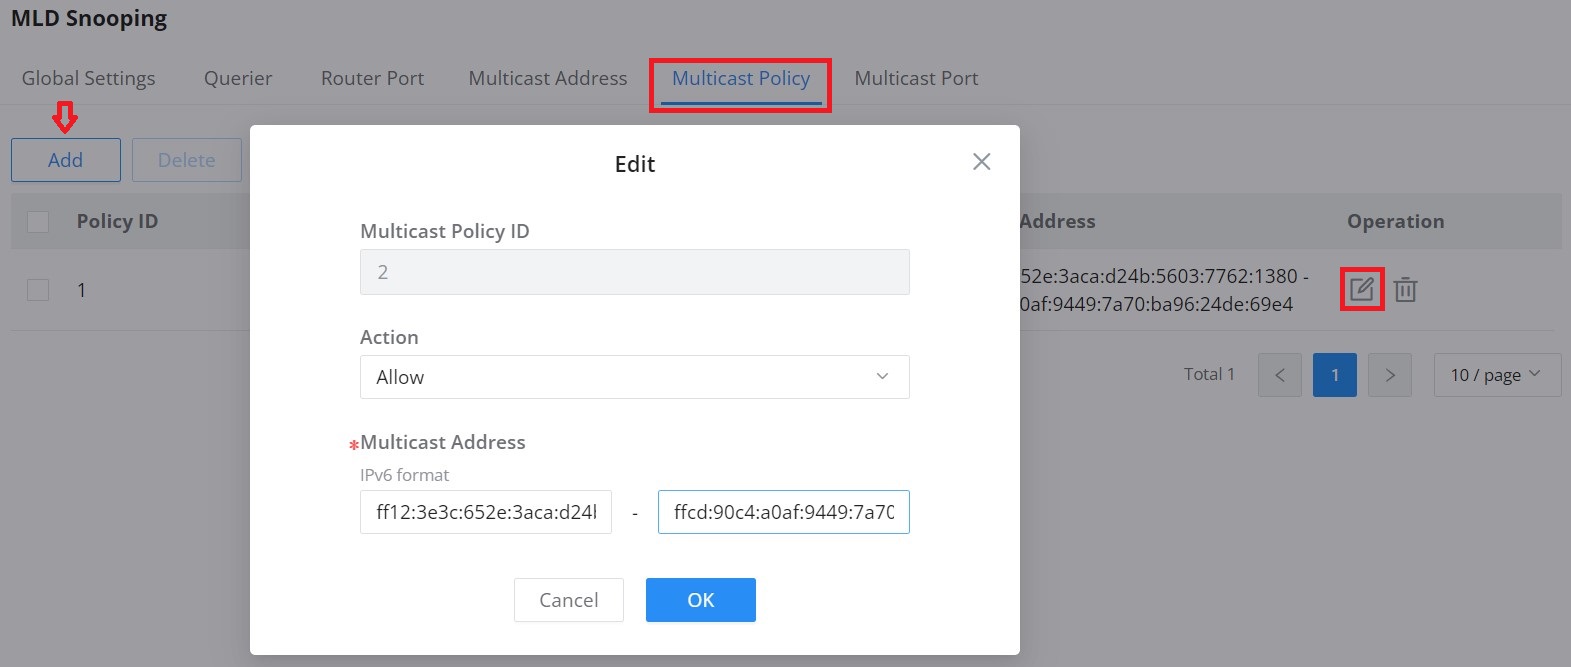
MLD Snooping Multicast Policy
Multicast Policy can be created in this page to allow or reject a range of IPv6 Multicast Addresses. Up to 128 Policy can be created.
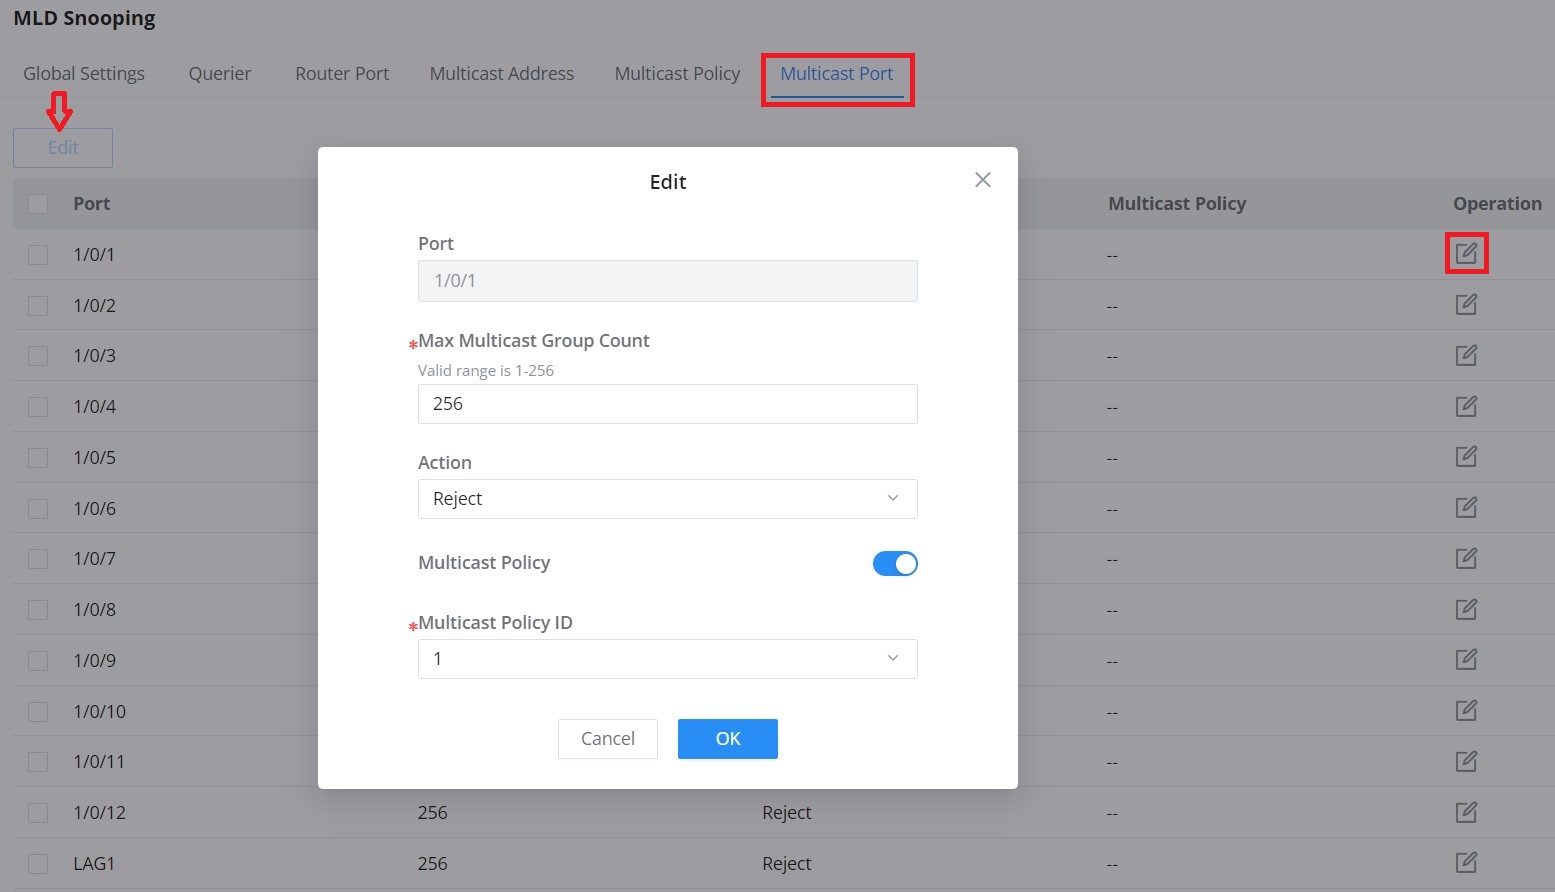
MLD Snooping Multicast Port
The multicast policy can be applied to the Gigabit Ethernet/LAG port, the user can also set the maximum number of multicast groups that the port is allowed to join and set the action when the port multicast exceeds the limit, the default is rejected.
ROUTING
Routing is a process in which the router selects the optimal path according to the destination address of the received data packet and forwards it to the next network node leading to the target network, and the last routing node under this path forwards the data to the target host. (Router refers to both a router in the traditional sense and an Ethernet switch running a routing protocol).
The switches support IPv4 and IPv6 static routing.
Routing Table
A routing table is like a map of the network that shows the best routes to each destination. It achieves this by storing information on how to reach different destinations on a network and with this table the router can decide where to forward packets that it receives from other devices.
To get to the Routing Table, please navigate to Web UI → Routing → Routing Table.
You cane enable/disable Routing Forwarding option, which allows the switch to act as a Layer 3 device, enabling it to forward packets between different networks or VLANs based on the routing table entries.
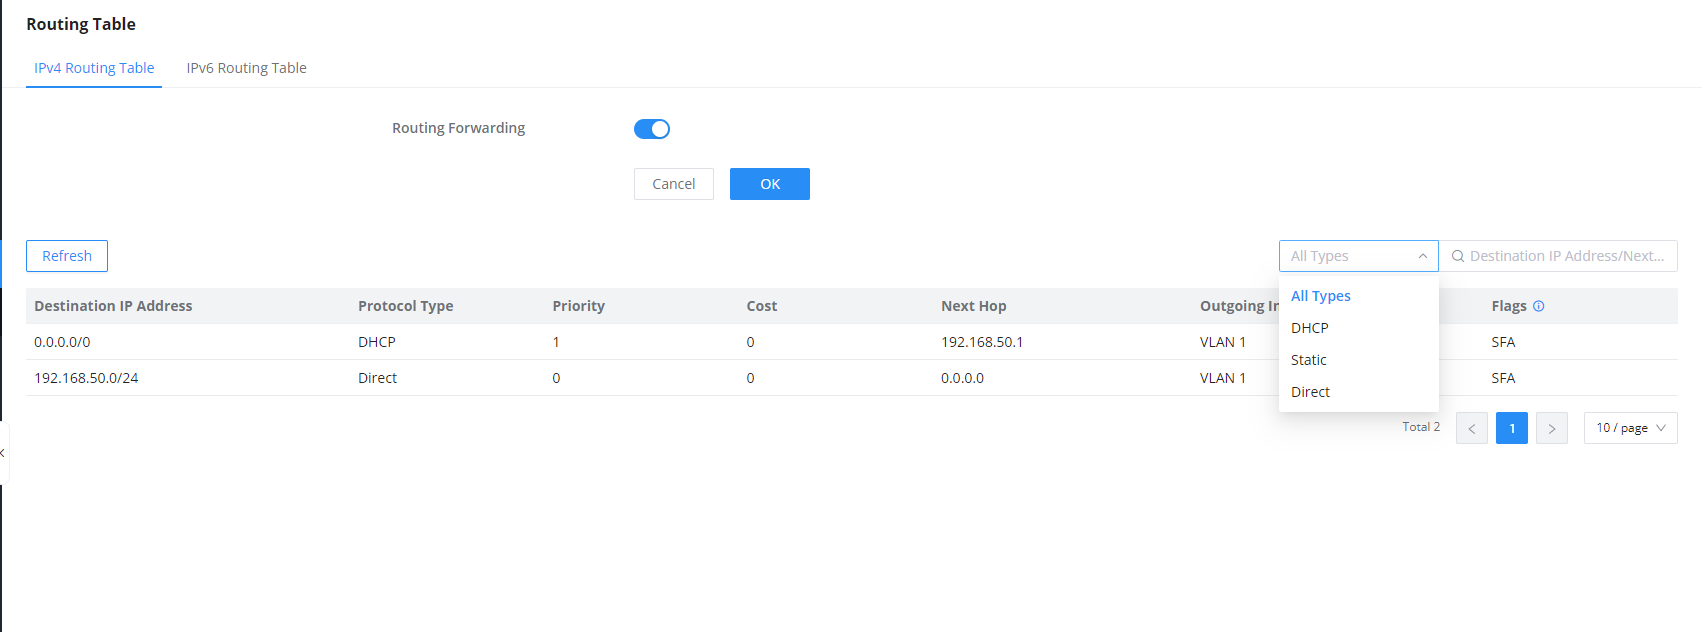
A routing table contains the following information for each entry: Destination IP address, Mask Length, Protocol Type, Priority, Next Hop, outgoing Interface and Flags.
A routing table gets populated over time with dynamic routing protocols like OSPF and RIP or static entries (manually configured by an administrator) or directly connected networks.
Static Routes
The static route is a special route that requires manual configuration by an administrator. Static routes have different purposes in different network environments:
- When the network structure is relatively simple, the network can work normally only by configuring static routes.
- In complex network environments, configuring static routes can improve network performance and ensure bandwidth for important applications, however, when the network fails or the topology changes, the static routes are not automatically updated and must be reconfigured manually.
To add a static route, please navigate to the Web UI → Routing → Static Routes page.
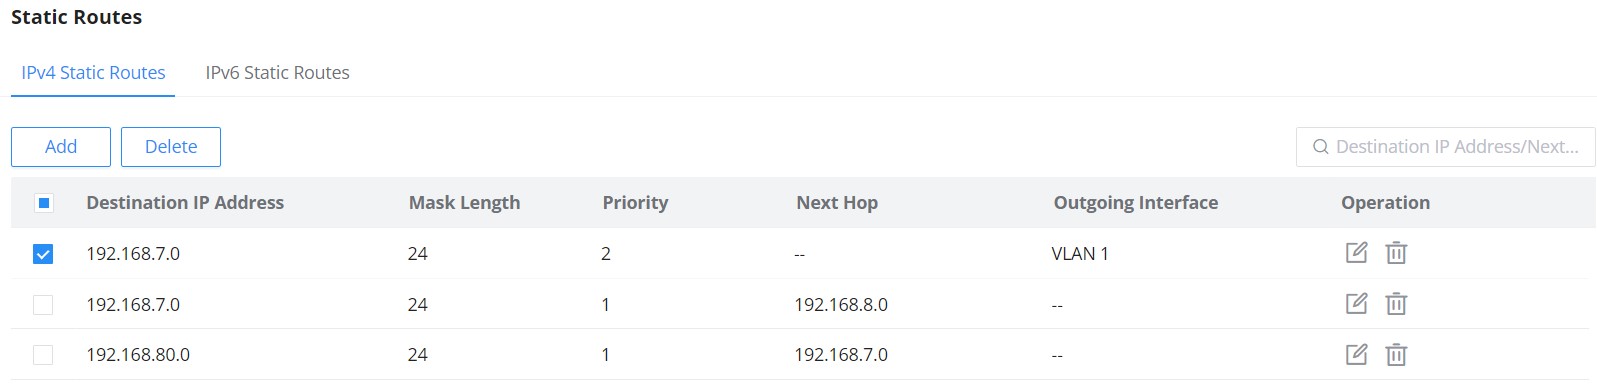
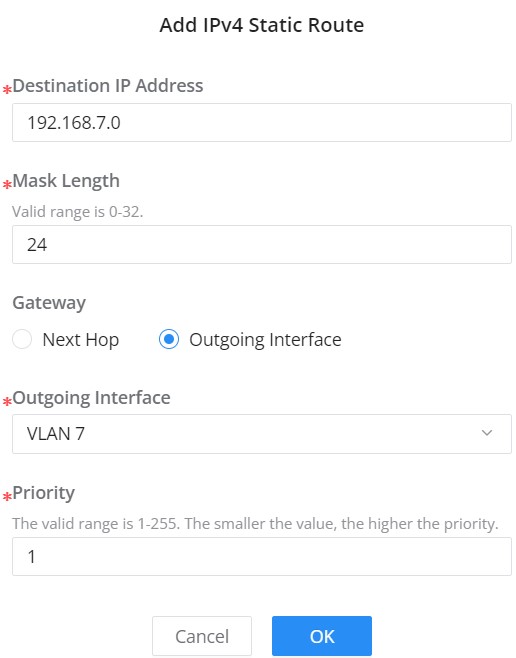
Click on “Add” button to add a new static route. then fill in the Destination IP Address with the mask length then select the next hop or the outgoing interface (VLAN) with specifying the priority.
Please refer to the figure below:
Routing Information Protocol (RIP)
The Routing Information Protocol (RIP) is a distance-vector routing protocol used for routing data in small to medium-sized networks. This guide will walk you through configuring RIP on the switch.
RIP – Global Settings
To configure global RIP settings, navigate to Routing → RIP → Global.
- Enable RIP: Toggle the switch to enable RIP.
- RIP Version: Choose between RIPv1 or RIPv2. RIPv2 is recommended for most modern networks.
- RIP Distance: Set the administrative distance for RIP. The default is 120.
- Timers:
- Update Timer (s): Sets the interval at which RIP updates are sent. The default is 30 seconds.
- Aging Timer (s): Determines how long a route remains valid before it is considered stale. The default is 180 seconds.
- Garbage Collection Timer (s): Defines the time to wait before deleting a stale route from the routing table. The default is 120 seconds.
- External Route Import: You can import routes from Direct, Static, and OSPF routes:
- Metric of Direct Route: Assign a metric for direct routes.
- Metric of Static Route: Assign a metric for static routes.
- Metric of OSPF Route: Assign a metric for OSPF routes.
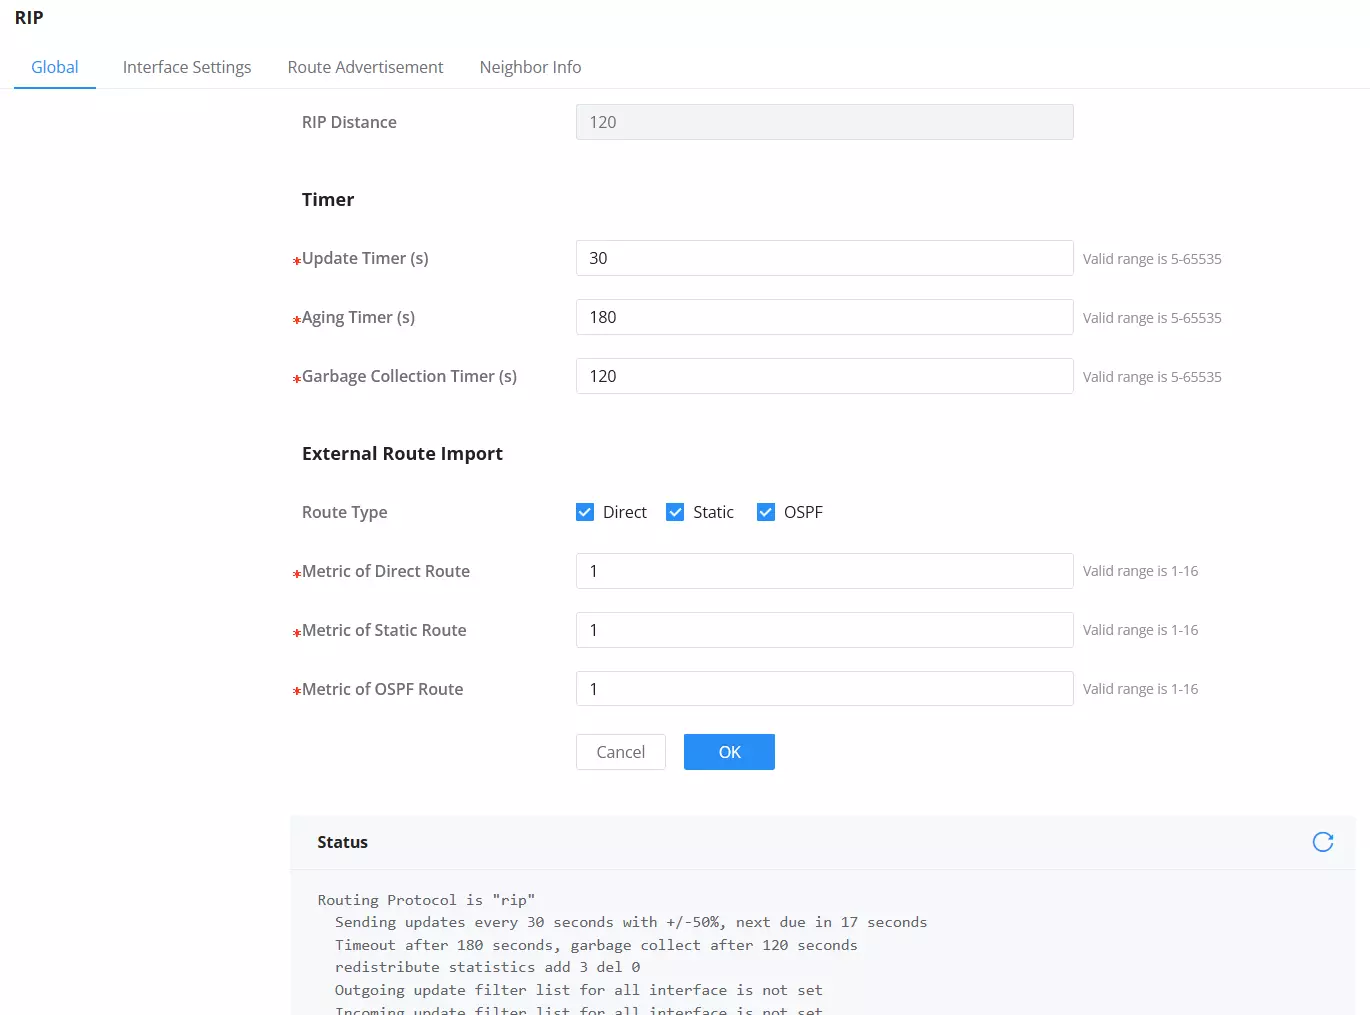
Once you’ve made your configurations, click OK to apply the settings.
RIP – Interface Settings
To configure RIP on specific interfaces or VLANs, navigate to Routing → RIP → Interface Settings.
- Select the Interface: You will see a list of VLANs or interfaces. Each interface shows its current status, IP address, RIP version, and other settings.
- To edit an interface, click on the Edit icon under the Operation column.
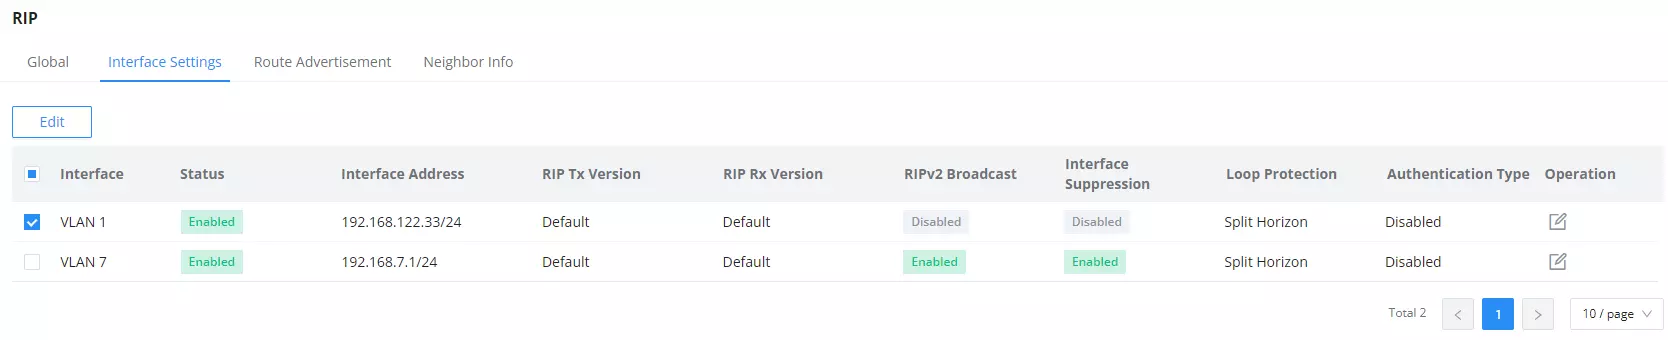
- Edit Interface: After clicking Edit, a new window will appear where you can configure the following settings:
- RIP: Toggle RIP on or off for this interface.
- RIP Tx Version: Select the version of RIP for outgoing messages (RIPv1 or RIPv2).
- RIP Rx Version: Select the version of RIP for incoming messages.
- RIPv2 Broadcast: Enable or disable broadcast for RIPv2.
- Interface Suppression: Enable or disable suppression of specific interfaces.
- Loop Protection: Choose between Split Horizon (to prevent loops by not sending updates back on the interface where they were received) or Poison Reverse (to mark a route as unreachable).
- Authentication Type: Set authentication for RIP packets to either Disabled, Simple (password-based), or MD5 (more secure).
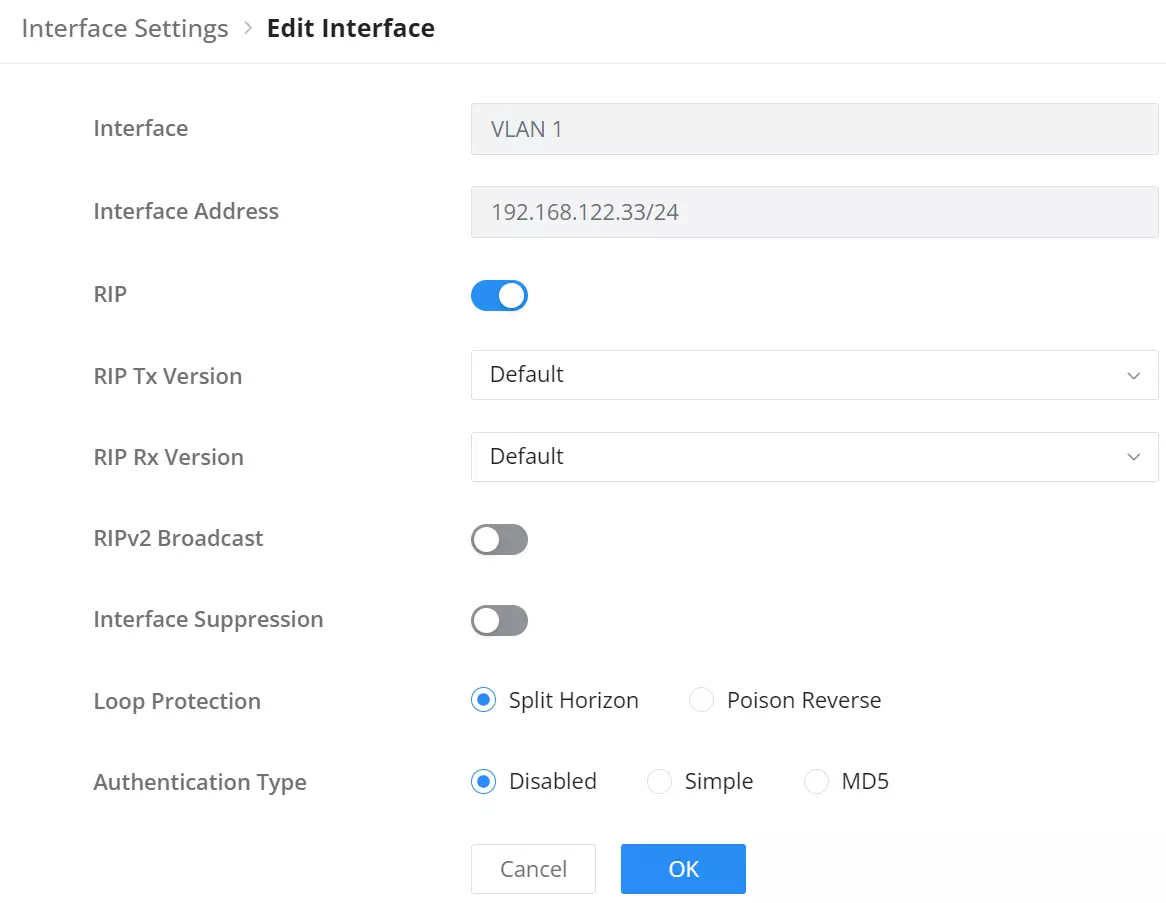
After making changes, click OK to save the settings.
RIP – Route Advertisement
To configure route advertisements, go to Routing → RIP → Route Advertisement.
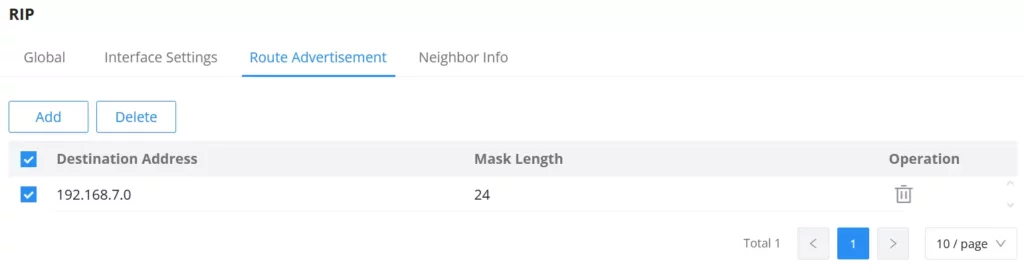
- Add a Route: Click Add to enter a new route.
- Destination Address: Specify the destination network address that will be advertised.
- Mask Length: Set the subnet mask length for the destination network.
- Delete a Route: To remove an advertised route, check the box next to the route and click Delete.
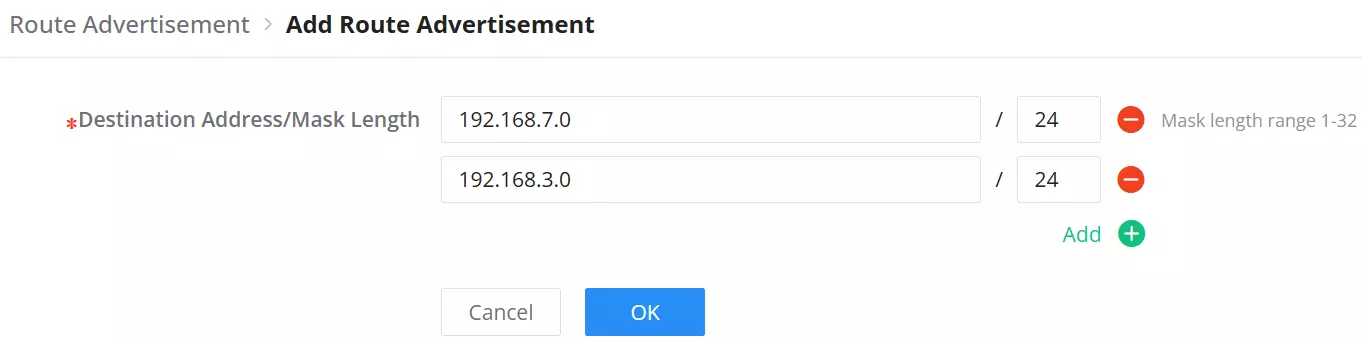
Click OK to apply the changes.
RIP – Neighbor Info
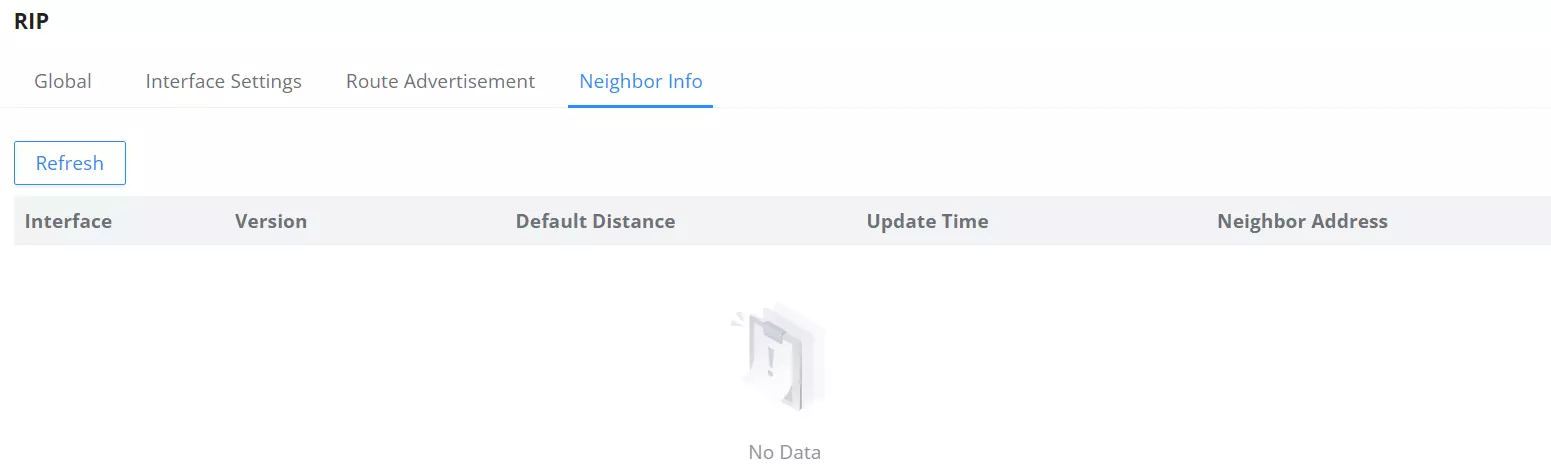
Navigate to Routing → RIP → Neighbor Info to view detailed information about neighboring devices that are participating in the RIP protocol. This section displays:
- Interface: The interface or VLAN participating in RIP.
- Version: The RIP version (RIPv1 or RIPv2).
- Default Distance: The default administrative distance for routes learned from neighbors.
- Update Time: The time of the last update from the neighbor.
- Neighbor Address: The IP address of the neighboring device.
Routing Information Protocol Next Generation (RIPng)
Just like RIP, RIPng (RIP Next Generation) is a distance-vector routing protocol, but it’s specifically designed for IPv6 networks. This section will guide you through configuring RIPng on the switch.
RIPng – Global Settings
To configure the global settings for RIPng, navigate to Routing → RIPng → Global.
- Enable RIPng: Toggle the switch to enable RIPng.
- RIPng Distance: Set the administrative distance for RIPng routes. The default is 120.
- Timers:
- Update Timer (s): Sets the interval at which RIPng updates are sent. The default is 30 seconds.
- Aging Timer (s): Determines how long a route remains valid before it is considered stale. The default is 180 seconds.
- Garbage Collection Timer (s): The interval before deleting a stale route from the routing table. The default is 120 seconds.
- External Route Import: You can import routes from Direct, Static, and OSPFv3 routes:
- Metric of Direct Route: Assign a metric for direct routes.
- Metric of Static Route: Assign a metric for static routes.
- Metric of OSPFv3 Route: Assign a metric for OSPFv3 routes.
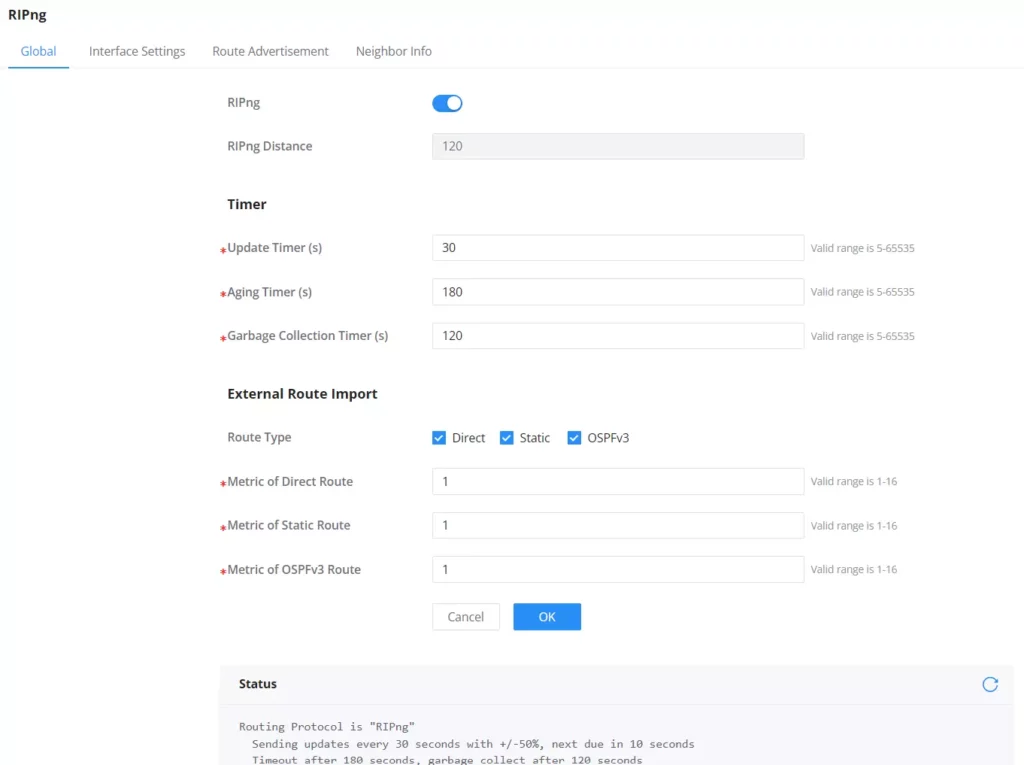
After making these configurations, click OK to apply the settings.
RIPng – Interface Settings
To configure RIPng on specific interfaces or VLANs, navigate to Routing → RIPng → Interface Settings.
- Select the Interface: You will see a list of VLANs or interfaces. Each interface shows its current status, interface address, and settings.
- To edit an interface, click the Edit icon under the Operation column.
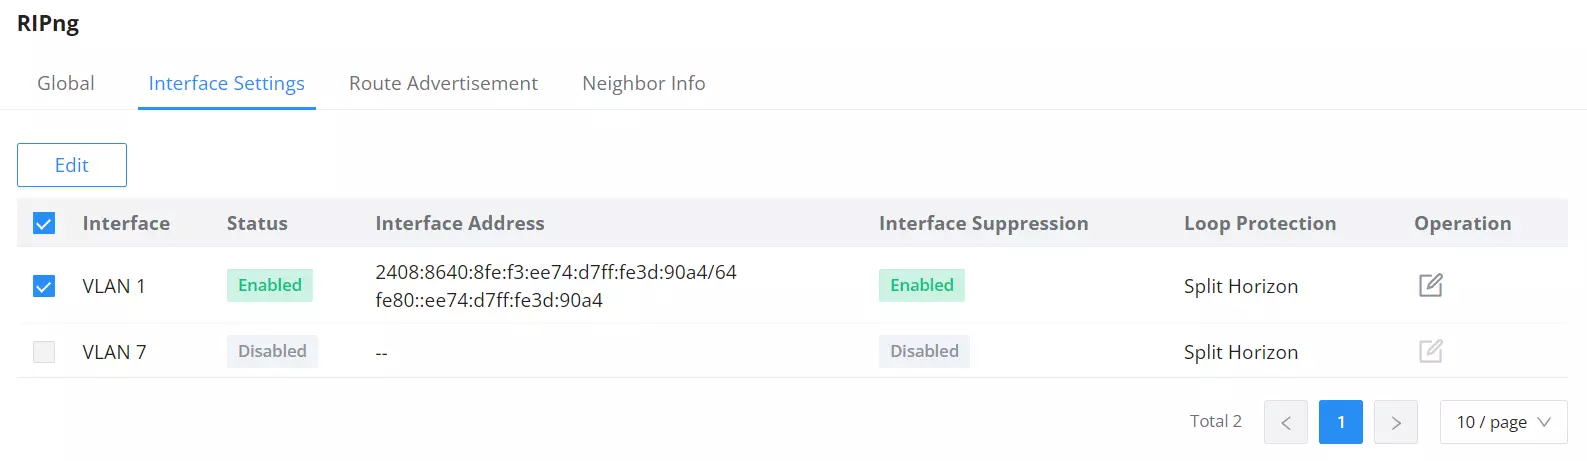
- Edit Interface: After clicking Edit, a new window will appear, allowing you to configure:
- RIPng: Toggle to enable RIPng on this interface.
- Interface Suppression: Enable or disable suppression of RIPng advertisements on the interface.
- Loop Protection: Select Split Horizon or Poison Reverse:
- Split Horizon: Prevents a router from sending routing information back on the interface from which it was received. This is useful to prevent routing loops.
- Poison Reverse: Marks a route as unreachable when it’s learned from a neighbor, which helps eliminate loops.
Explanation: Split Horizon is a simple technique to prevent loops by not advertising a route back to the neighbor that originally sent it. Poison Reverse takes this further by actively marking routes from the same source as unreachable, providing more robust loop prevention.
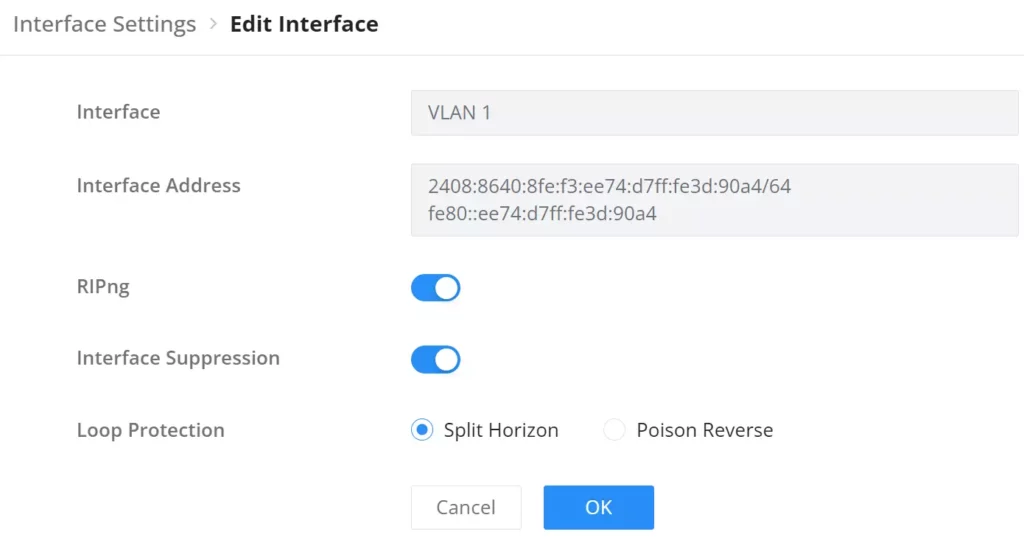
After making changes, click OK to save the settings.
RIPng – Route Advertisement
To configure route advertisements, go to Routing → RIPng → Route Advertisement.
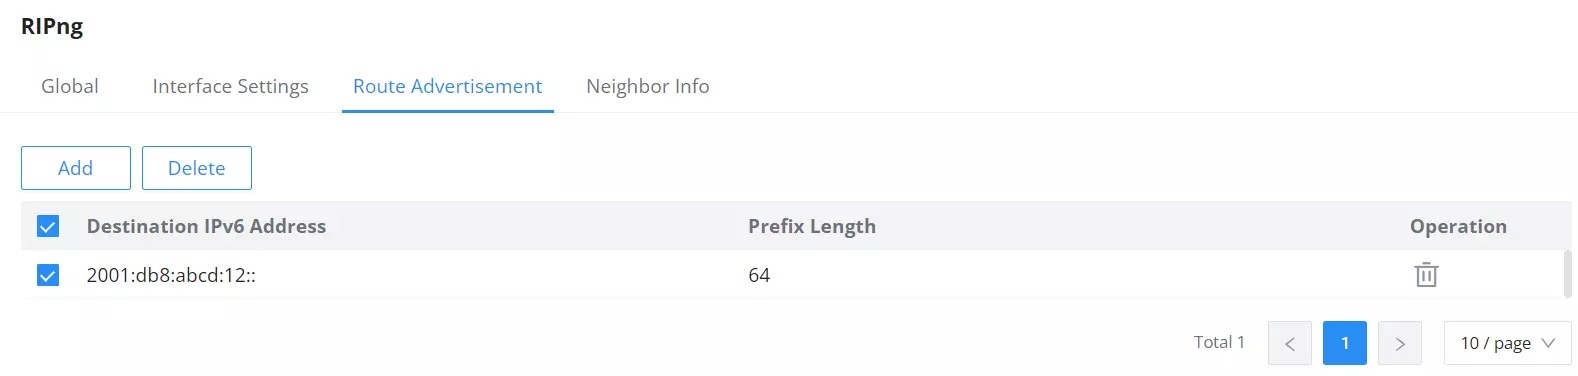
- Add a Route: Click Add to create a new route.
- Destination IPv6 Address: Specify the destination IPv6 network.
- Prefix Length: Set the prefix length for the IPv6 network (e.g.,
/64).
- Delete a Route: To remove an advertised route, check the box next to the route and click Delete.
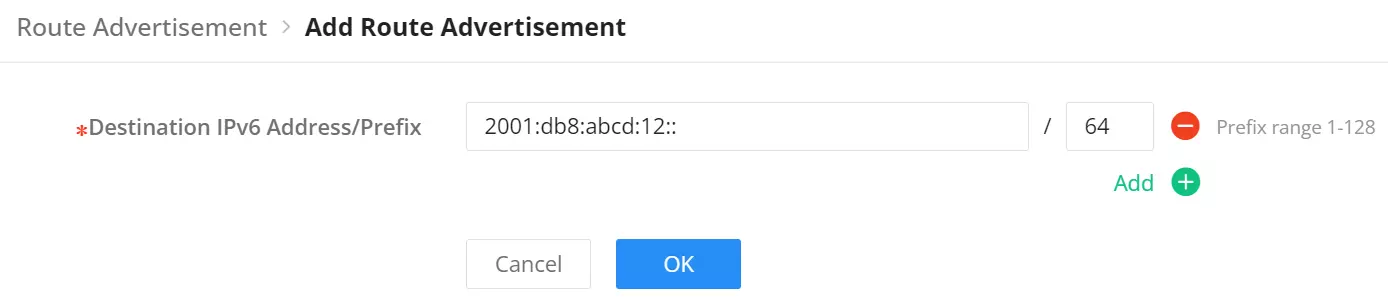
Click OK to apply the changes.
RIPng – Neighbor Info
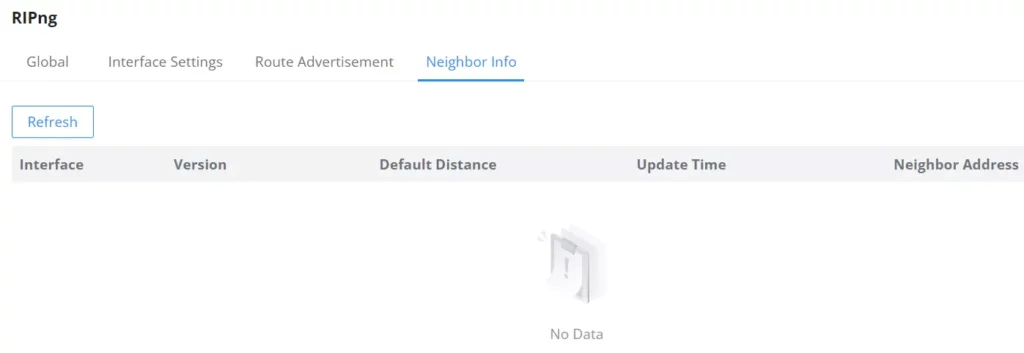
Navigate to Routing → RIPng → Neighbor Info to view detailed information about neighboring devices participating in RIPng routing. This section displays:
- Interface: The interface or VLAN participating in RIPng.
- Version: The RIPng version.
- Default Distance: The administrative distance for routes learned from neighbors.
- Update Time: The time of the last update from the neighbor.
- Neighbor Address: The IPv6 address of the neighboring device.
OSPF (Open Shortest Path First)
OSPF stands for Open Shortest Path First, it’s a routing protocol and uses a link state routing algorithm, in other words it collects information about the state of each link in the network to build an overall map about the whole network topology. OSPF is an interior gateway protocol (IGP) same as RIP (Routing Information Protocol), it’s a protocol based on distance vector algorithms. OSPF has many advantages over other routing protocols, such as RIP.
Some Advantages of OSPF protocol:
- OSPF can perform route summarization, which reduces the size of the routing table and improves scalability.
- OSPF supports IPv4 and IPv6.
- OSPF can split the network into areas, which are logical groups of routers that share the same link state information. This reduces the amount of routing information that needs to be exchanged and processed by each router.
- OSPF can use authentication to secure the exchange of routing information between routers.
- OSPF can deal with variable length subnet masks (VLSM), which allows for more efficient use of IP addresses and network design.
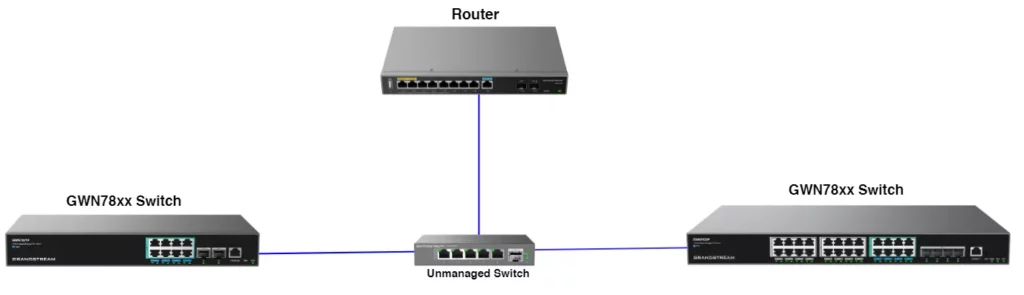
In this example, we will be using two switches directly connected (neighbors) and a router serving as a DHCP server. Please refer to the figure below:
OSPF Global
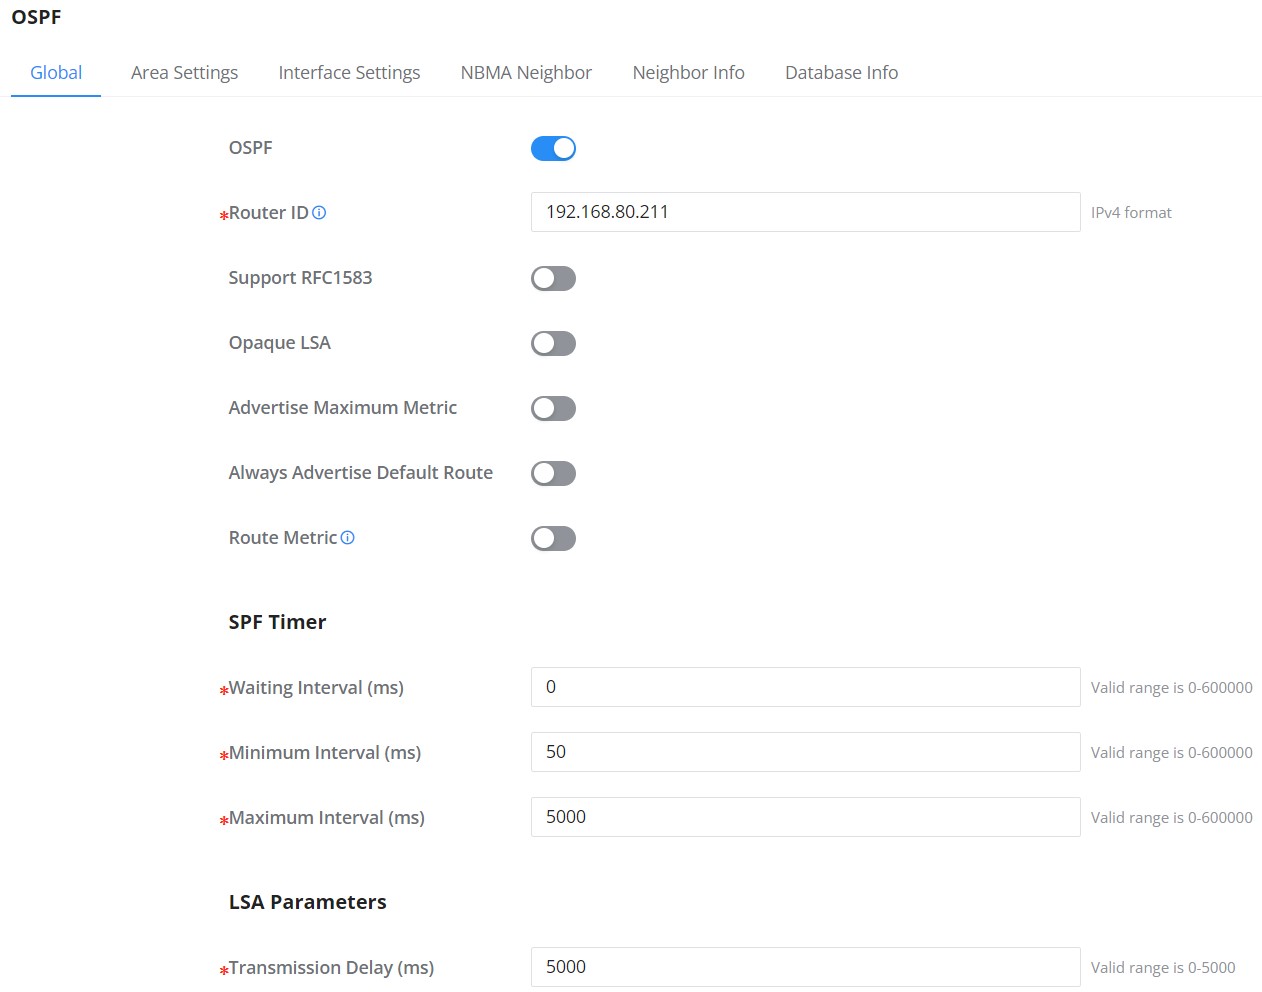
To start using OSPF, please navigate to Web UI → Routing → OSPF page → Global tab:
Toggle ON OSPF and enter the Router ID (it can be any IPv4 address) then scroll down to the bottom of the page and click the “OK” button, please refer to the figure below:
OSPF Area Settings
The Area Settings tab allows you to configure different OSPF areas. An OSPF area is a logical grouping of routers that exchange OSPF information.

To edit an Area Settings, click on the “Edit” button.
- Area ID: The unique identifier for the OSPF area. Area 0.0.0.0 is the backbone area and must be configured in every OSPF network.
- Area Type: Defines the type of the area. OSPF supports different area types, including:
- None: A normal OSPF area that supports all OSPF features.
- Stub Area: This does not allow external routes to be advertised into the area, reducing the size of the routing table.
- Not-So-Stubby Area (NSSA): Allows limited external routes, typically from an ASBR (Autonomous System Boundary Router) within the area.
- No Summary: (only for Stub and NSSA) disables the summarization of routes, forcing the router to advertise specific routes rather than aggregated routes. This may be useful in certain network designs where precise routing information is required.

OSPF Interface Settings
On the Interface Settings tab, click on the “Edit” icon to enable the VLAN IP Interface.
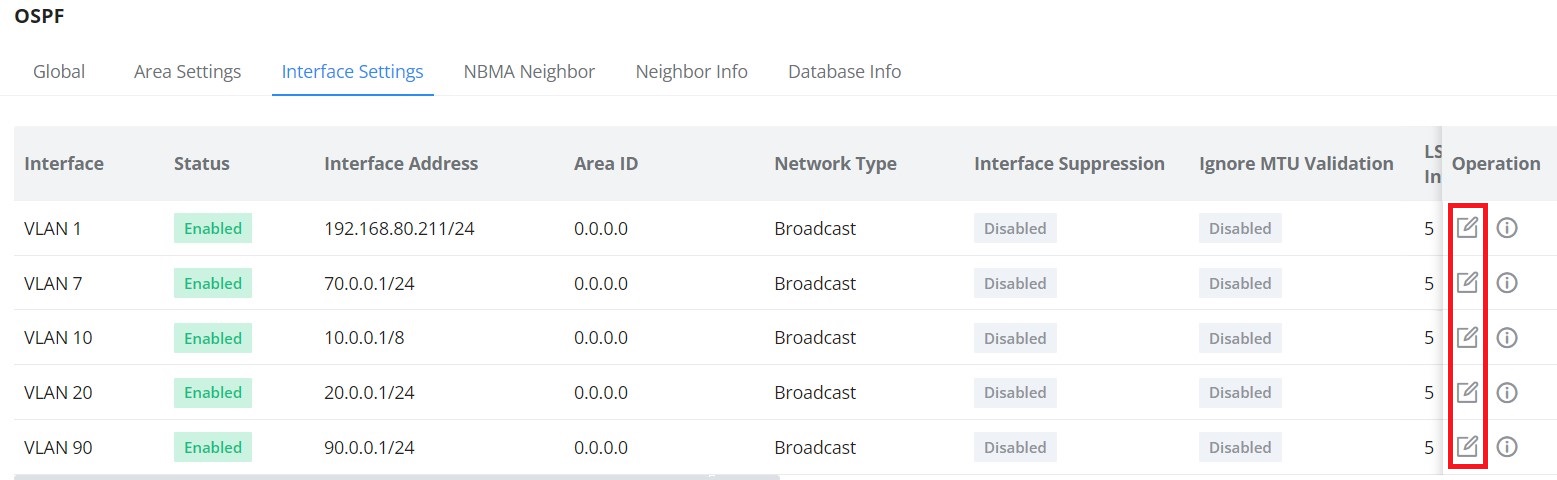
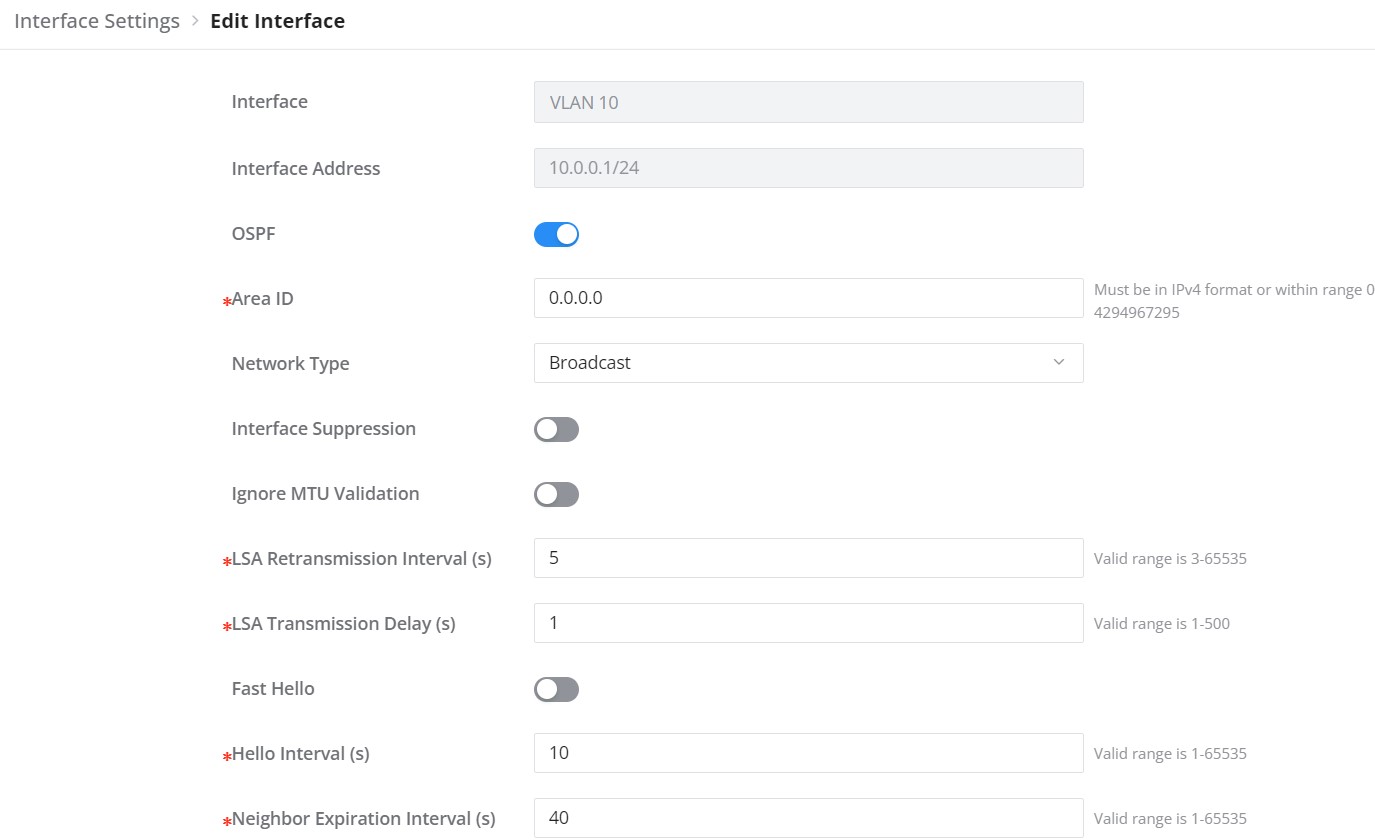
Toggle ON the OSPF on the selected interface then scroll down and click on the “OK” button.
OSPF NBMA Neighbor
In Non-Broadcast Multi-Access (NBMA) networks, OSPF cannot automatically discover neighbors as it does in broadcast networks. Therefore, you must manually configure the neighbors.
- Neighbor: The IP address of the neighbor OSPF router that you want to manually add.
- Hello Interval (s): The time interval between sending hello packets to this neighbor.
- Priority: The priority assigned to the neighbor. This value influences the selection of the Designated Router (DR) and Backup Designated Router (BDR).
- Interface Address: The local IP address of the interface that will communicate with the neighbor.
Click on the “Add” button to add a neighbor.

Then specify the Neighbor IP address (IPv4 format).

OSPF Neighbor Info
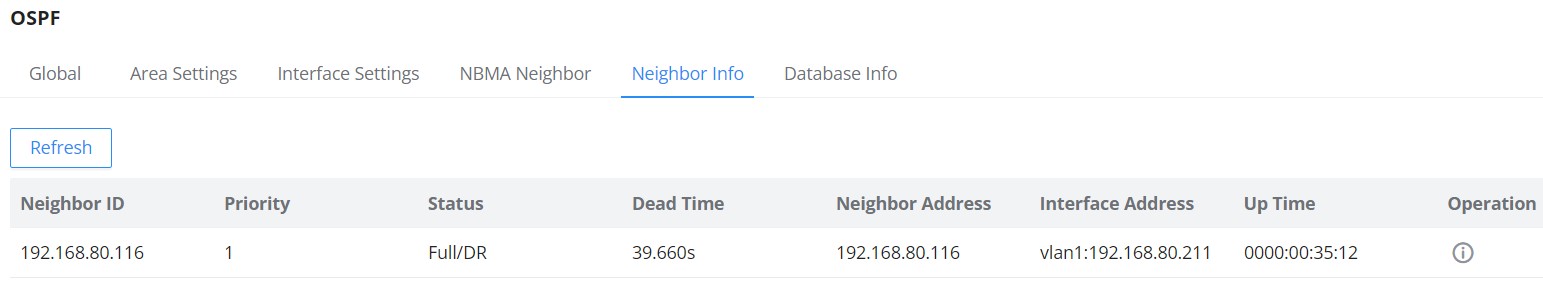
Please do the same steps on the second switch, then on the Neighbor Info tab, click on the “refresh” button for the adjacent (directly connected) switches to appear.
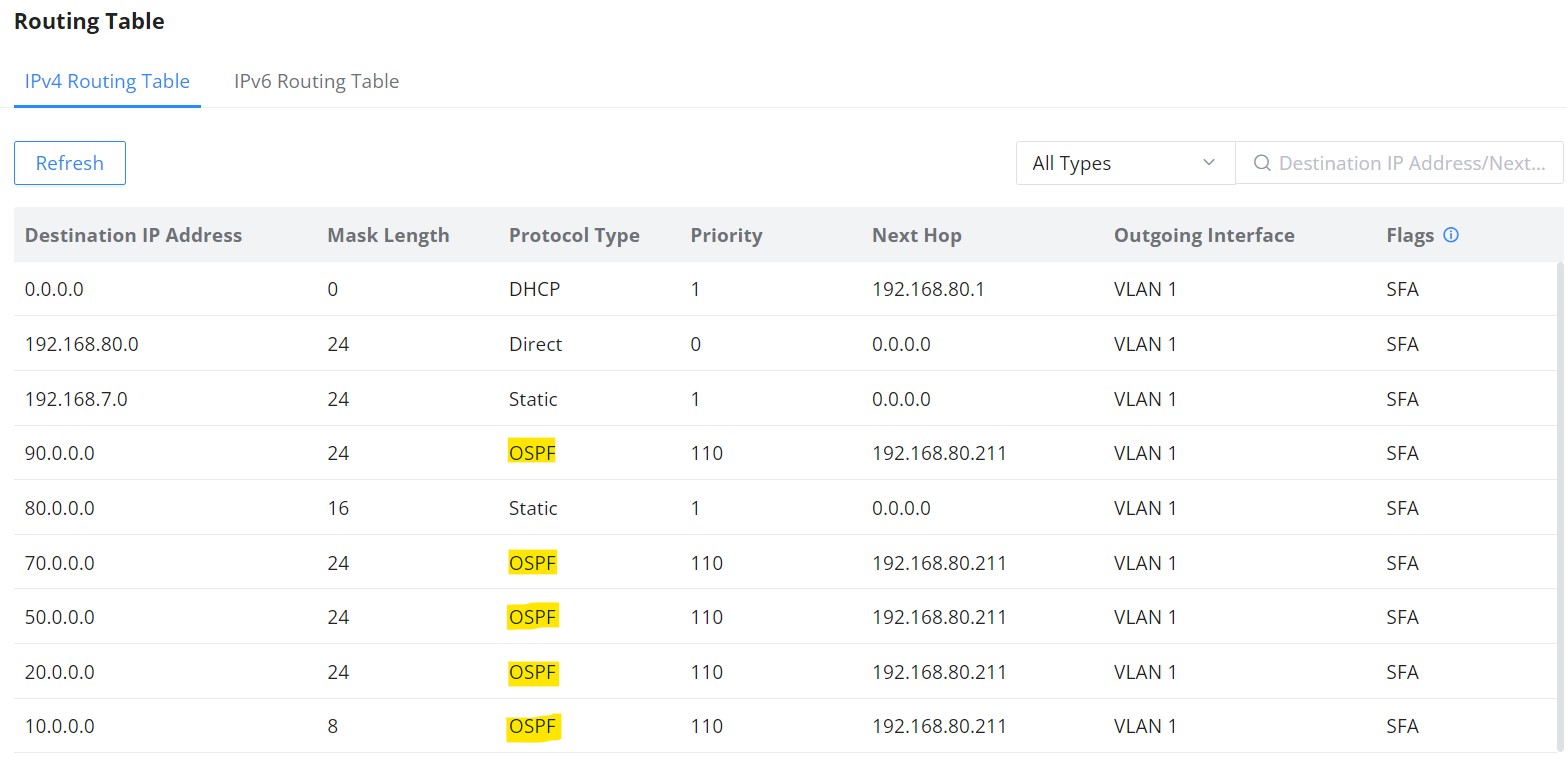
Navigate to the Routing table Web UI → Routing → Routing table to confirm that the routing table contains routes to the previously created VLAN IP Interfaces on the other switch. Please refer to the figure below:
OSPF Database Info
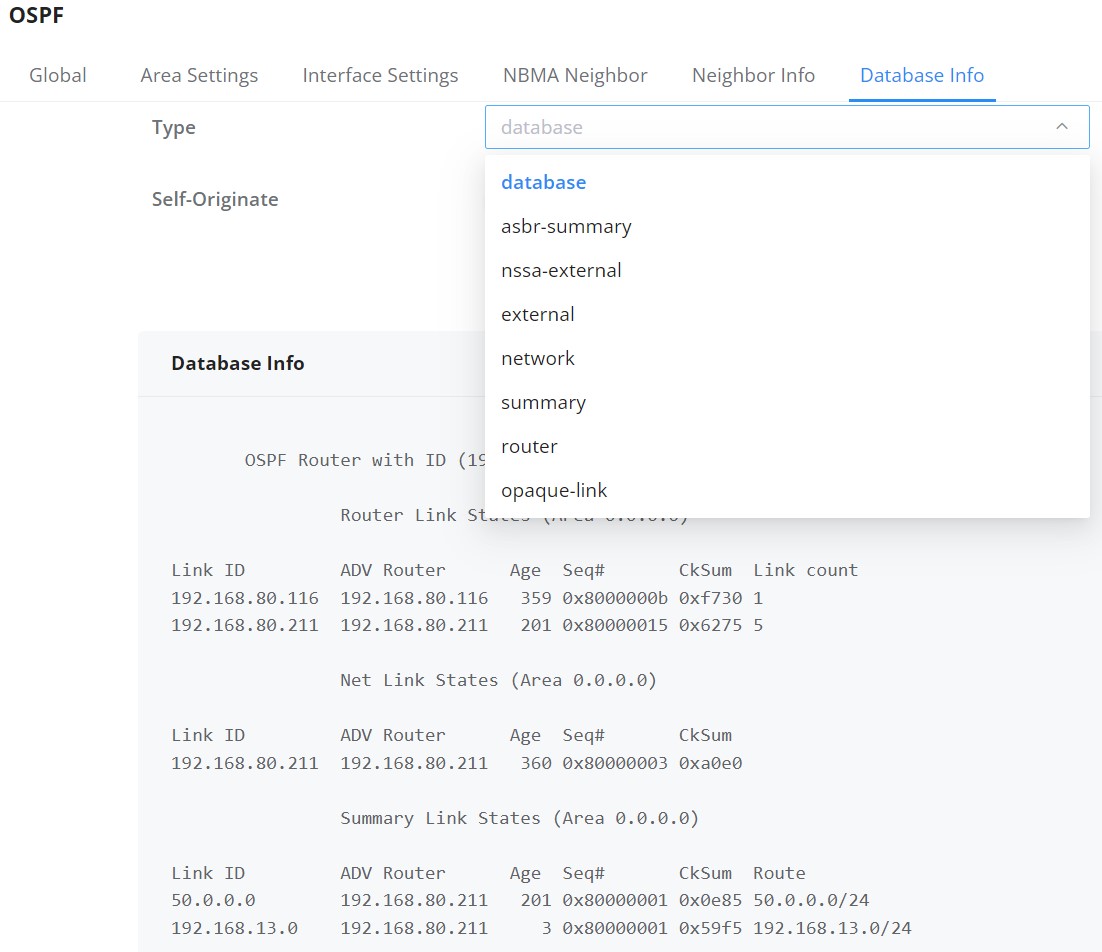
To check the LSDB (Link State DataBase), click on the Database Info tab, select the type (database) then click on the “Query” Button to see the Database info which is a list of all LSA (Link State Advertisements) that the OSPF routers use to get information about other routers running OSPF protocol and that is what helps to populate the routing table for the best route to each destination.
OSPFv3
Building upon OSPF, OSPFv3 (Open Shortest Path First Version 3) is specifically designed for IPv6 networks. While it shares many principles with OSPFv2, OSPFv3 introduces enhancements to accommodate IPv6 addressing and security features.
Key differences and advantages of OSPFv3 over OSPFv2:
- IPv6 Support: OSPFv3 is designed to support IPv6 natively, allowing for seamless integration into modern IPv6 networks.
- Authentication: OSPFv3 uses IPsec for authentication, providing enhanced security over OSPFv2, which uses built-in authentication methods like MD5.
- Address Family Separation: OSPFv3 separates the routing logic from the addressing, allowing for easier extension and support for multiple address families.
- Link-State Advertisements (LSAs): Introduces new LSAs to support IPv6 prefixes efficiently.
In this example, we will use two switches directly connected (neighbors) and a router serving as a DHCP server. Please refer to the figure below:
To start using OSPFv3, please navigate to Web UI → Routing → OSPFv3:
OSPFv3 Global
Toggle ON OSPFv3 and enter the Router ID (it can be any IPv4 address). Configure the SPF calculation intervals and LSA parameters as needed. Click the “OK” button to save the settings. Refer to the figure below:

OSPFv3 Area Settings
On the Area Settings tab, click the “Edit” icon to add and configure areas by specifying the Area ID and Area Type.

OSPFv3 Interface Settings
In the Interface Settings tab, click the “Edit” icon to enable the VLAN IP Interface.

Toggle ON OSPFv3 on the selected interface, then scroll down and click on the “OK” button.
Do the same steps on the second switch, then on the Neighbor Info tab, click on the “Refresh” button for the adjacent (directly connected) switches to appear.

OSPFv3 Database Info
To check the LSDB (Link State DataBase), click on the Database Info tab, select the type (database), then click on the “Query” Button to see the Database info, which is a list of all LSAs (Link State Advertisements) that the OSPFv3 routers use to get information about other routers running OSPFv3 protocol. This helps to populate the routing table for the best route to each destination.

BGP
Border Gateway Protocol (BGP) is a path-vector routing protocol used to exchange routing information between different networks, or Autonomous Systems (AS), across the internet. BGP is known as the protocol that powers the internet because it manages how packets are routed across large-scale, complex networks. It allows organizations to route traffic efficiently and ensures that data reaches its destination by selecting the most appropriate path.
Key Features of BGP:
- Scalability: BGP is capable of managing vast networks by sharing routing information across different autonomous systems.
- Policy-based Routing: BGP allows administrators to define policies and rules to control how routing decisions are made.
- Redundancy: BGP can provide multiple routes to the same destination, ensuring high availability.
BGP operates between routers within an Autonomous System (Internal BGP or IBGP) and between routers across different Autonomous Systems (External BGP or EBGP). BGP routers exchange routing information, which is used to build the routing tables that direct traffic between networks.
BGP – Global Settings
The Global Settings tab in BGP allows you to configure key parameters that control how the BGP process operates on the router. These settings include defining your Autonomous System (AS) Number, Router ID, and preferences for route selection and stability.
In the Global Settings, you can:
- Set your AS Number (AS ID), which identifies your network in BGP routing.
- Specify the Router ID, a unique identifier for the BGP router.
- Configure Local Preference to control route selection within your Autonomous System.
- Enable Route Dampening to stabilize the routing table by reducing the impact of route flapping.
For further details on how to configure each of these fields, please refer to the figure and table below.
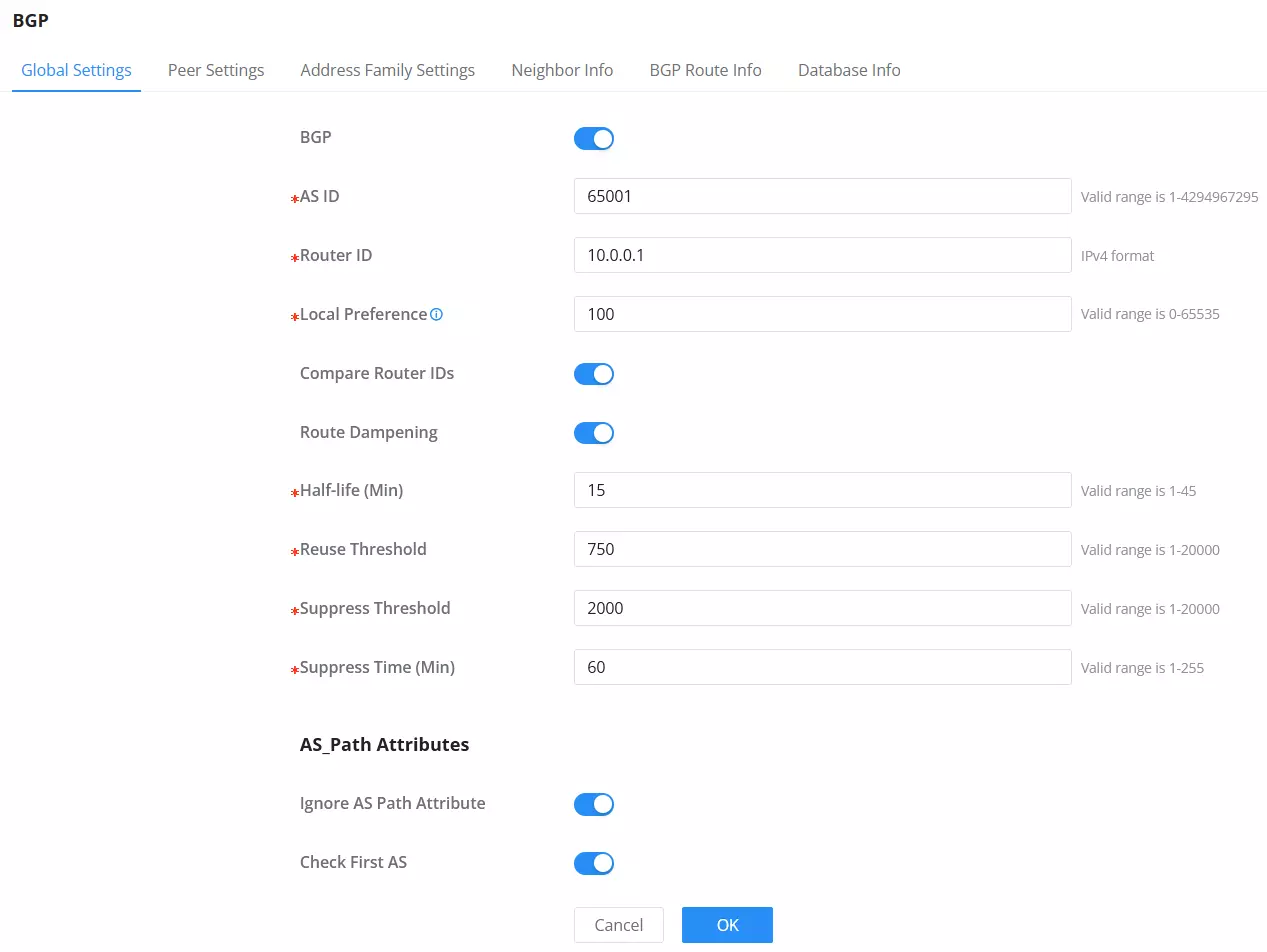
Field | Description | Example or Recommended Setting |
BGP | Enables or disables BGP on the router. | Enabled |
AS ID | Autonomous System (AS) number identifying your network. | Example: 65001 |
Router ID | Unique identifier for the router (typically an IP address). | Example: 10.0.0.1 |
Local Preference | Used to prefer one path over another within your AS. Higher values are preferred. If a BGP device obtains multiple routes with the same destination address but different next hops through different IBGP peers, the route with the higher local preference attribute value is preferred. Note: The local preference attribute is only valid between IBGP peers and is not advertised to other ASs. | Recommended: 100 |
Compare Router IDs | Compares router IDs when making routing decisions. | Enabled |
Route Dampening | Stabilizes the network by reducing route flapping. | Enabled |
Half-life (Min) | The time after which the penalty for route flapping is halved. | 15 (default) |
Reuse Threshold | The threshold at which a suppressed route can be reused. | 750 (default) |
Suppress Threshold | The penalty threshold at which a route is suppressed. | 2000 (default) |
Suppress Time (Min) | The time a route remains suppressed due to flapping. | 60 (default) |
AS_Path Attributes | ||
Ignore AS Path Attribute | Ignores the AS Path attribute when making routing decisions. | Enabled |
Check First AS | Ensures BGP checks the first AS in the path for validation. | Enabled |
BGP – Global Settings
BGP – Peer Settings
The Peer Settings tab allows you to configure peers for exchanging routing information with other BGP devices. These peers are critical for establishing communication between routers and sharing routing tables.
Navigate to Routing → BGP → Peer Settings, select IPv4 Peer or IPv6 Peer depending on your network configuration, and click Add to configure a new peer. In this tab, you can add, edit, or remove peers.
For detailed explanations of each field, refer to the figure and table below.
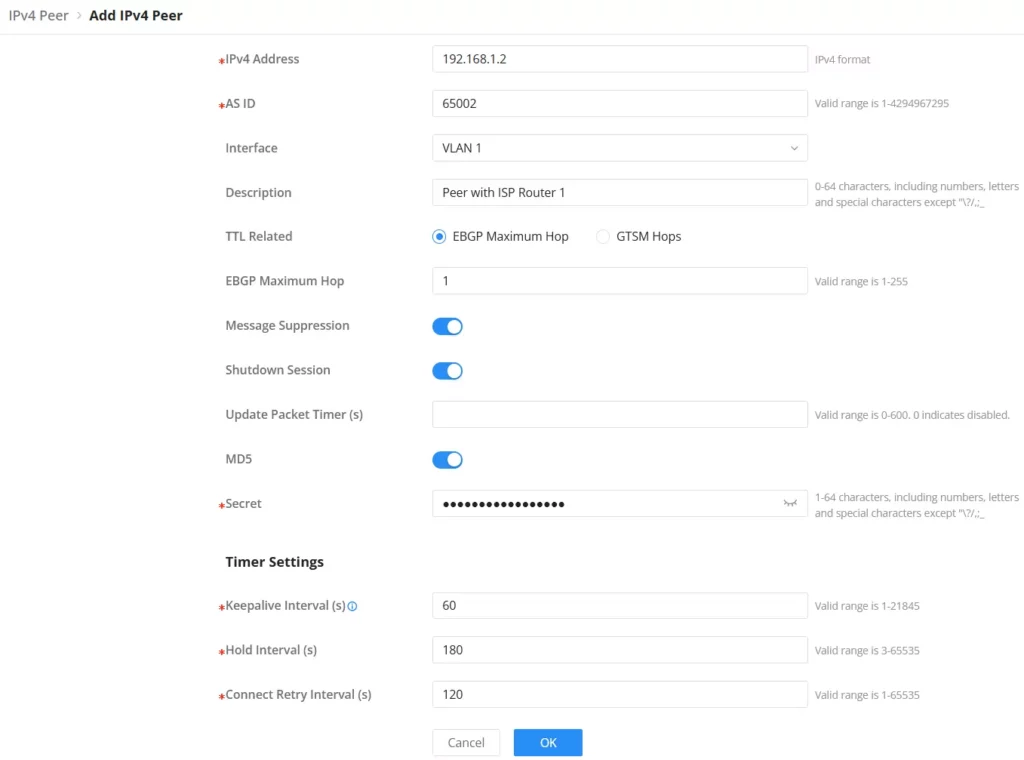
Field | Description |
IPv4 Address | Enter the IPv4 address of the BGP peer you are establishing a connection with. (Example: 192.168.1.2) |
AS ID | Enter the Autonomous System (AS) number of the peer. This is a unique identifier for a group of networks under a single administration. (Example: 65002) |
Interface | Select the interface (VLAN or Loopback) through which the BGP session will be established. (Example: VLAN 1) |
Description | Optional field to describe the peer for identification purposes. (Example: Peer with ISP Router 1) |
TTL Related | Select EBGP Maximum Hop for general EBGP connections or GTSM Hops for scenarios requiring security against certain types of attacks. (Default: EBGP Maximum Hop) |
EBGP Maximum Hop | Set the maximum number of hops allowed for EBGP neighbors. (Valid range: 1-255) (Example: 1) |
Message Suppression | When enabled, prevents BGP updates from being sent to the peer. Useful for maintenance scenarios. (Default: Disabled) |
Shutdown Session | Enables or disables the BGP session. When enabled, no updates are exchanged with the peer. (Default: Disabled) |
Update Packet Timer (s) | Configures the interval for sending BGP update packets in seconds. (Valid range: 0-600) (Default: Disabled) |
MD5 | Enable MD5 authentication for the peer. It is recommended for securing the BGP session. |
Secret | The MD5 key used for authentication with the peer. (Example: a password or shared secret, 1-64 characters long) |
Keepalive Interval (s) | Time interval in seconds for sending keepalive messages to ensure the peer is active. Note: If the keepalive interval is higher than the hold interval, the session will fail. (Valid range: 1-21845) (Default: 60) |
Hold Interval (s) | Time interval in seconds before the BGP session is terminated if no keepalive or update message is received from the peer. (Valid range: 3-65535) (Default: 180) |
Connect Retry Interval (s) | Time interval in seconds to wait before retrying a connection if the BGP session fails. (Valid range: 1-65535) (Default: 120) |
BGP – Add peer
BGP – Address Family Settings
The Address Family Settings tab allows you to configure routing for different address families (IPv4 and IPv6). You can aggregate routes or import routes using various routing protocols (RIP, OSPF, etc.). These configurations determine how the switch handles route advertisements and ensures efficient network communication.
Navigate to Routing → BGP → Address Family Settings. In this tab, users can select between IPv4 Unicast Routing and IPv6 Unicast Routing. You can also configure Route Aggregation and Import Route options to optimize routing policies.
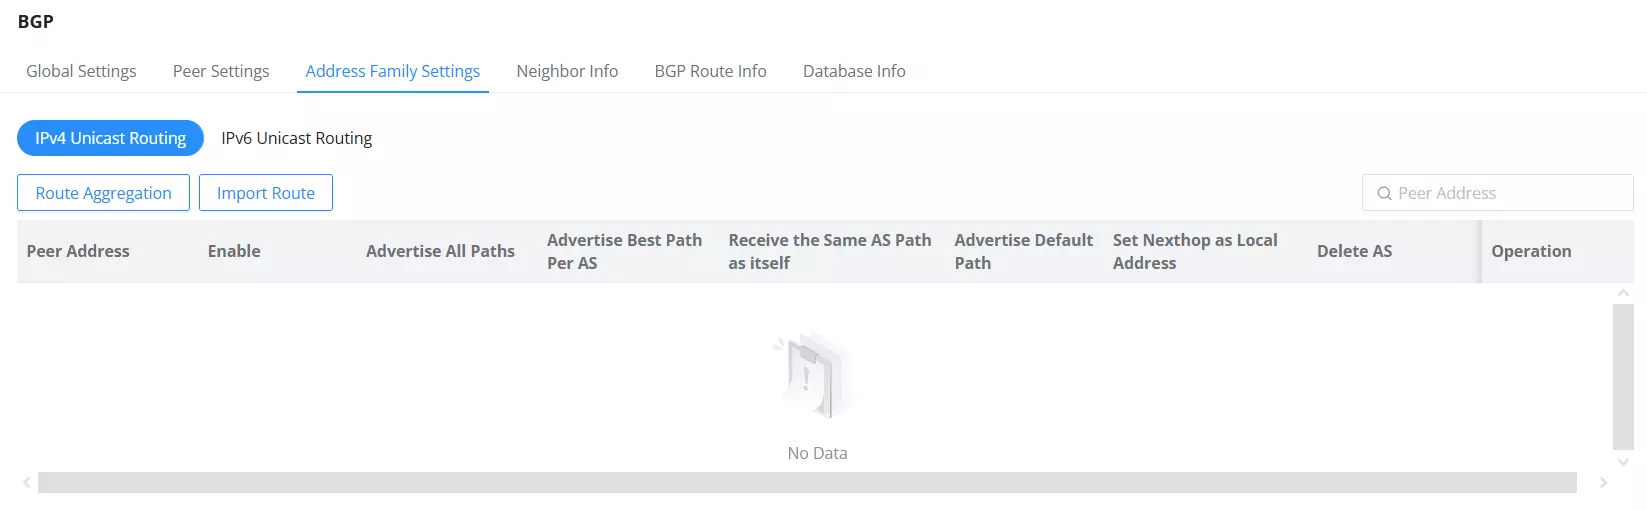
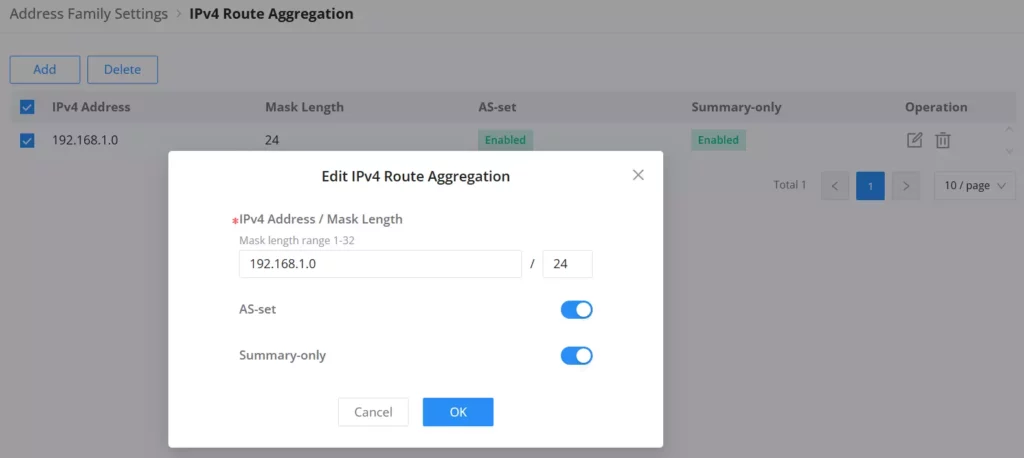
- Click on Route Aggregation, then click Add.
- Enter the following fields:
- IPv4 Address / Mask Length: Specify the IPv4 address and subnet mask length for the route to be aggregated. For example,
192.168.1.0/24where24represents the subnet mask.- Explanation: Route aggregation allows the BGP router to represent multiple smaller networks as a single larger network to other BGP peers. This reduces the size of routing tables.
- AS-set: Toggle this option if you want to aggregate the AS numbers from the original routes.
- Explanation: The AS-set option preserves the Autonomous Systems (AS) numbers from all the aggregated routes. This is helpful when you want to show all the AS paths through which the aggregated routes have passed.
- Summary-only: Toggle this option to advertise only the summary route (without advertising the more specific routes).
- Explanation: The Summary-only option ensures that only the aggregate route is advertised to the BGP peers, and the more specific routes are hidden. This helps simplify the routing information shared with other peers.
- IPv4 Address / Mask Length: Specify the IPv4 address and subnet mask length for the route to be aggregated. For example,
- Click OK to confirm and add the route aggregation.
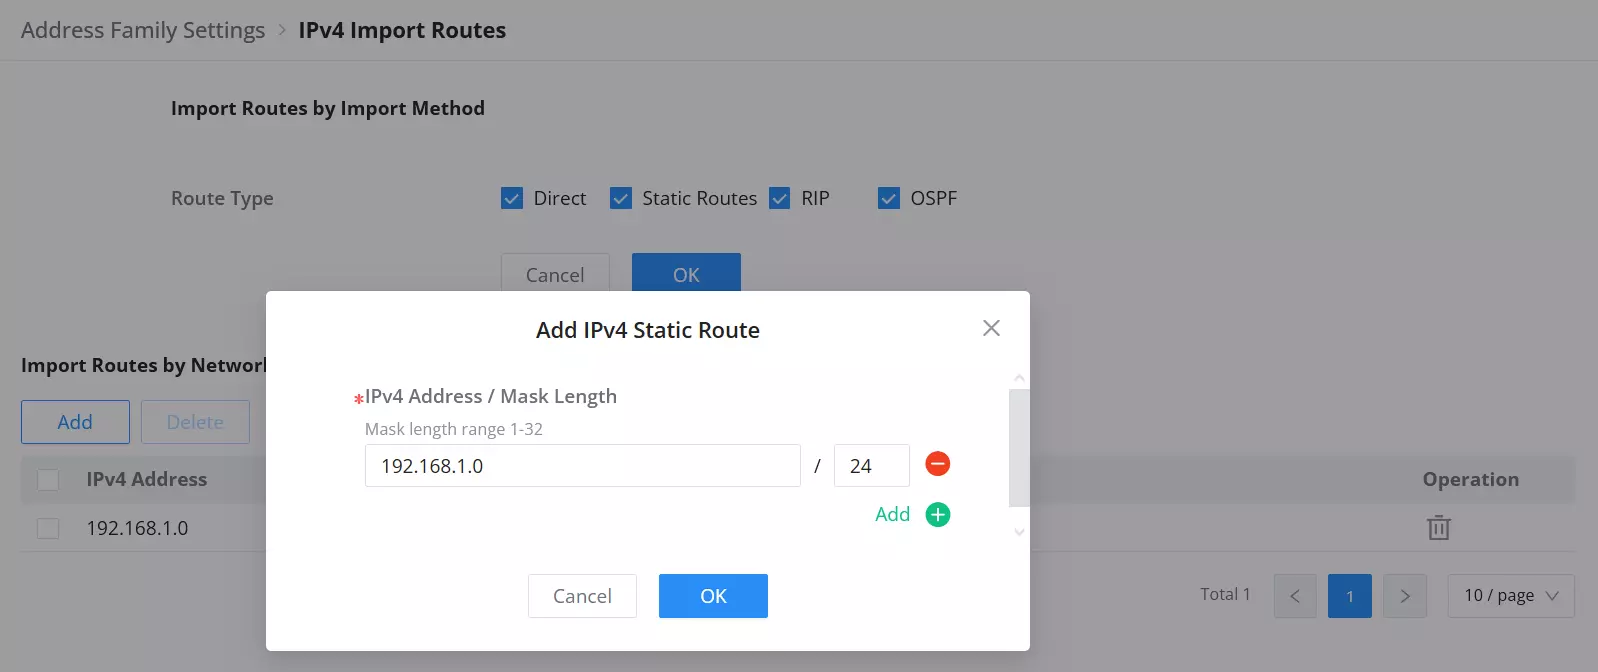
The IPv4 Import Routes section in the Address Family Settings allows you to import static routes, RIP, and OSPF routes into BGP. This is useful when you want to redistribute routes learned from other routing protocols or static routes into the BGP routing process.
To configure:
- Navigate to Routing → BGP → Address Family Settings → Import Route.
- Select the route types you want to import (Direct, Static Routes, RIP, OSPF).
- Click on Add to specify a new route to be imported.
- Enter the IPv4 Address / Mask Length for the static route. Example:
192.168.1.0/24. - Click OK to confirm and import the route into BGP.
This ensures that the specified routes from other protocols are redistributed within the BGP routing domain.
BGP – Neighbor Info
The Neighbor Info tab in BGP provides details about established BGP peers and their status. You can view information such as the neighbor’s IP address, BGP version, AS ID, received and sent messages, and the current state of communication between your device and its BGP peers.
To view BGP Neighbor Information:
- Navigate to Routing → BGP → Neighbour Info.
- Select either IPv4 or IPv6 Neighbor Info depending on the type of peer you have configured.
- Click Refresh to update the list of BGP neighbors and view their details.
This section helps you monitor and troubleshoot BGP connections by showing real-time updates on message exchanges with BGP peers.
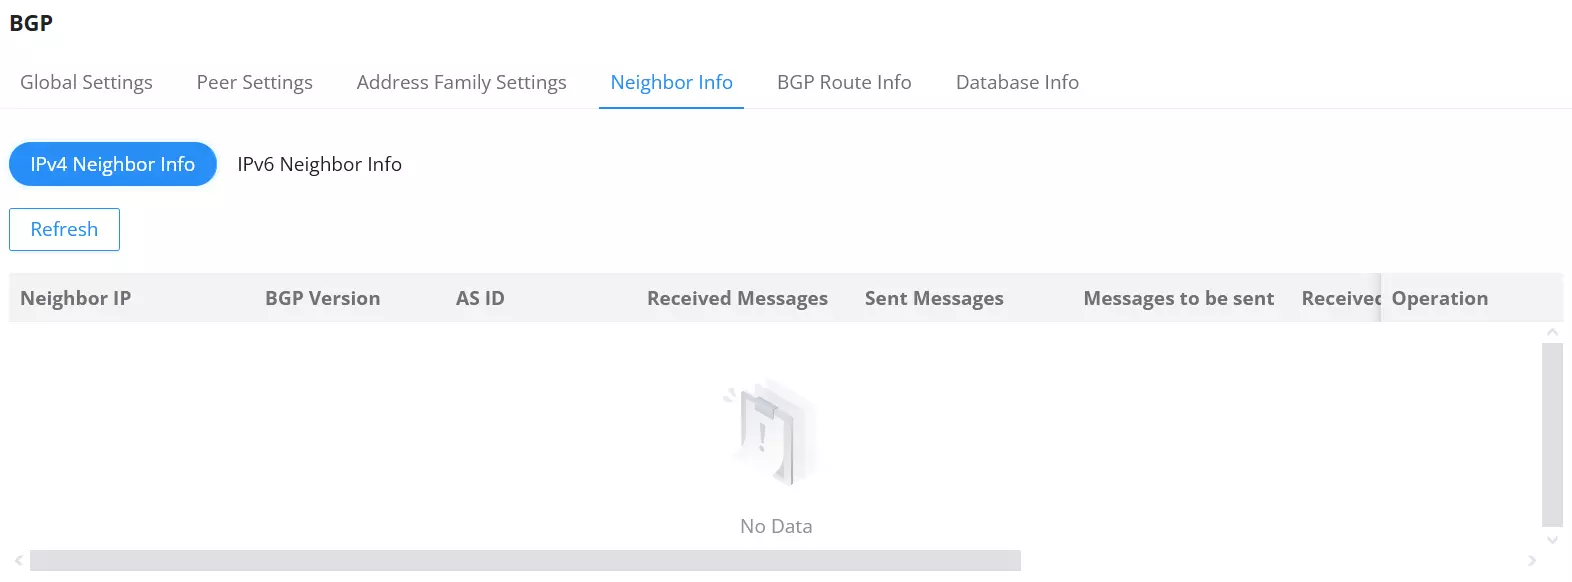
BGP – Route Info
The BGP Route Info tab displays detailed information about the routes that the BGP process has learned and is using. This information includes the network addresses, next hop addresses, and various metrics used to determine the best path for routing traffic.
To view BGP route information:
- Navigate to Routing → BGP → BGP Route Info.
- Select either IPv4 or IPv6 BGP Route Info depending on your routing configuration.
- Click Refresh to update and display the current routing table.
The table provides important details like:
- Network: The destination network address.
- Next Hop: The next-hop IP address for the route.
- Metric: A value that BGP uses to compare different paths.
- Weight and Path: These values help in determining the best available path for routing.
This tab is crucial for network administrators to monitor how routes are advertised, selected, and updated within the BGP environment.
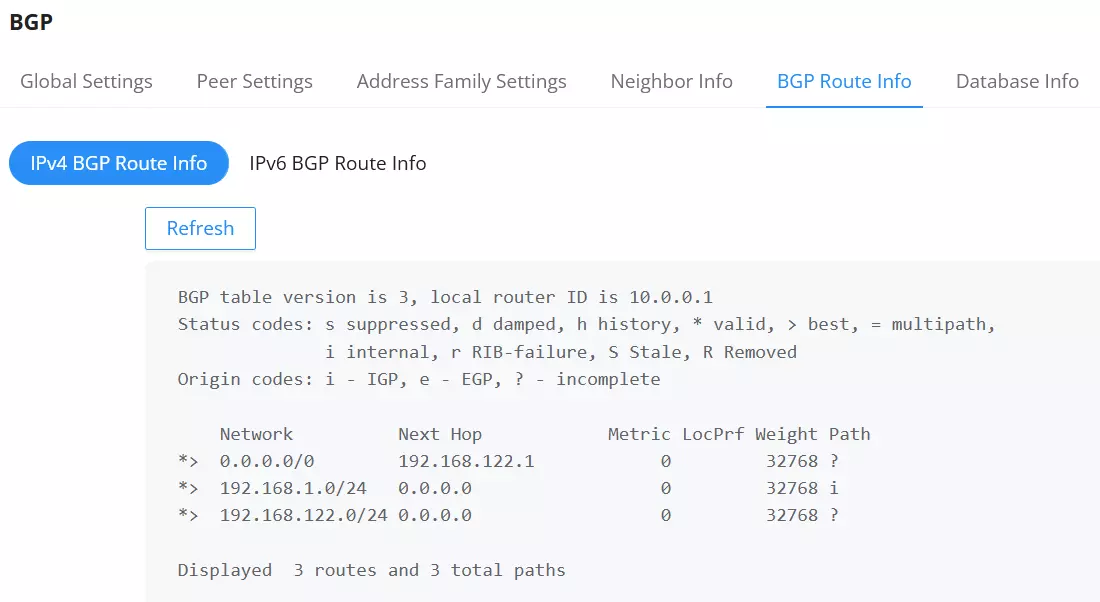
BGP – Database Info
The BGP Database Info tab provides detailed statistics and information about BGP neighbors, routes, and various metrics associated with BGP’s operation.
To view BGP Database Information:
- Navigate to Routing → BGP → Database Info.
- Select a Type from the drop-down menu. The options include:
- dampening-parameters: View information about dampening parameters used in BGP.
- dampening-paths: View the paths that are dampened.
- dampening-flap-statistics: View flap statistics to monitor route stability.
- nexthop-detail: Get details about the next hop.
- advertised-routes: View the routes advertised to other neighbors.
- prefix-counts: See a count of prefixes.
- flap-statistics: Additional route stability statistics.
- detail: General details about the selected IP address.
- Enter the IP Address of the neighbor for which you want to see the database information.
- Click OK to view the detailed information related to the selected type.
This tab is useful for in-depth BGP troubleshooting and monitoring, providing granular data on BGP operations and neighbors.
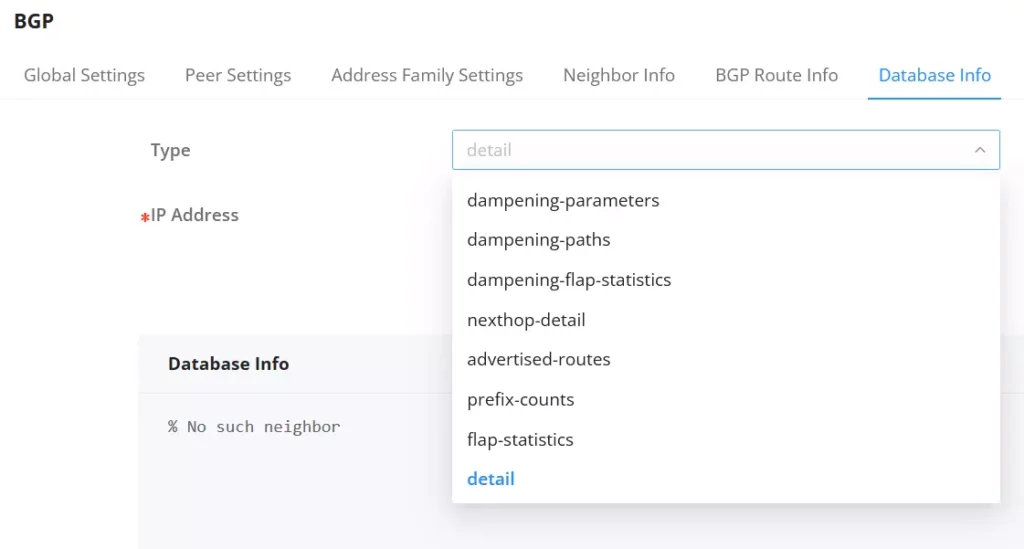
Route Policy
The Route Policy section is used to manage and apply filtering rules based on IPv4 and IPv6 Access Lists or Prefix Lists. BGP uses these rules to filter which routes are advertised or received from peers. This is essential for controlling routing behavior and ensuring only specific routes are allowed or denied according to network policies.
Based on IPv4 Access List
The IPv4 Access List option allows users to create rules that filter routes by permitting specific routes based on the IPv4 address and mask length. These rules help to control which routes are advertised or received from BGP peers.
Example Configuration:
- Name:
Allow-Routes-OfficeNetwork - Match Pattern: Allow (permits the specified routes).
- IPv4 Address/Mask Length:
192.168.1.0/24
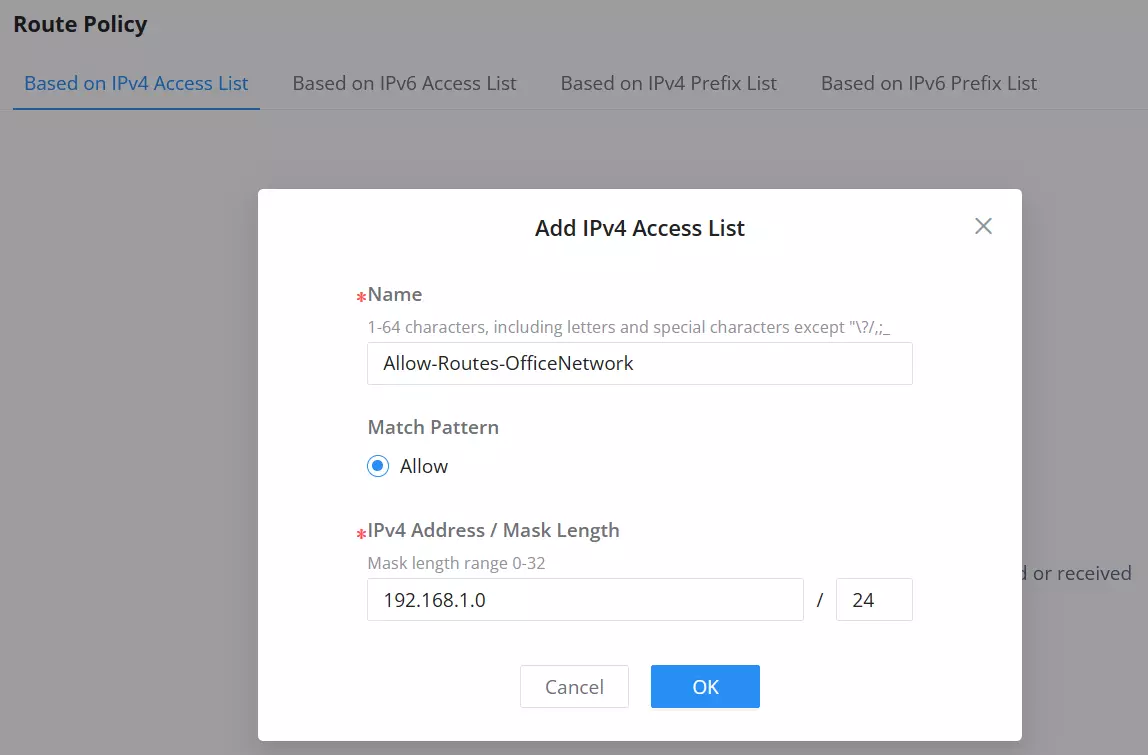
This configuration allows routes from the 192.168.1.0/24 network to be advertised or received by the BGP peer.
To configure:
- Navigate to Routing → Route Policy → Based on IPv4 Access List.
- Click Add.
- Specify the rule name (e.g., Allow-Routes-OfficeNetwork).
- Choose the Allow match pattern.
- Enter the IPv4 Address/Mask Length.
- Click OK to save.
Based on IPv6 Access List
The Based on IPv6 Access List section is used to create filtering rules that allow specific IPv6 routes to be advertised or received by BGP peers. This feature is useful for controlling the flow of IPv6 routing information in a network.
To configure an IPv6 Access List:
- Navigate to Routing → Route Policy → Based on IPv6 Access List.
- Click Add.
- Enter a Name for the rule (e.g., Allow-Routes-IPv6OfficeNetwork).
- Select the Allow match pattern (only available option).
- Enter the IPv6 Address/Prefix Length for the routes you want to match.
- Click OK to save the rule.
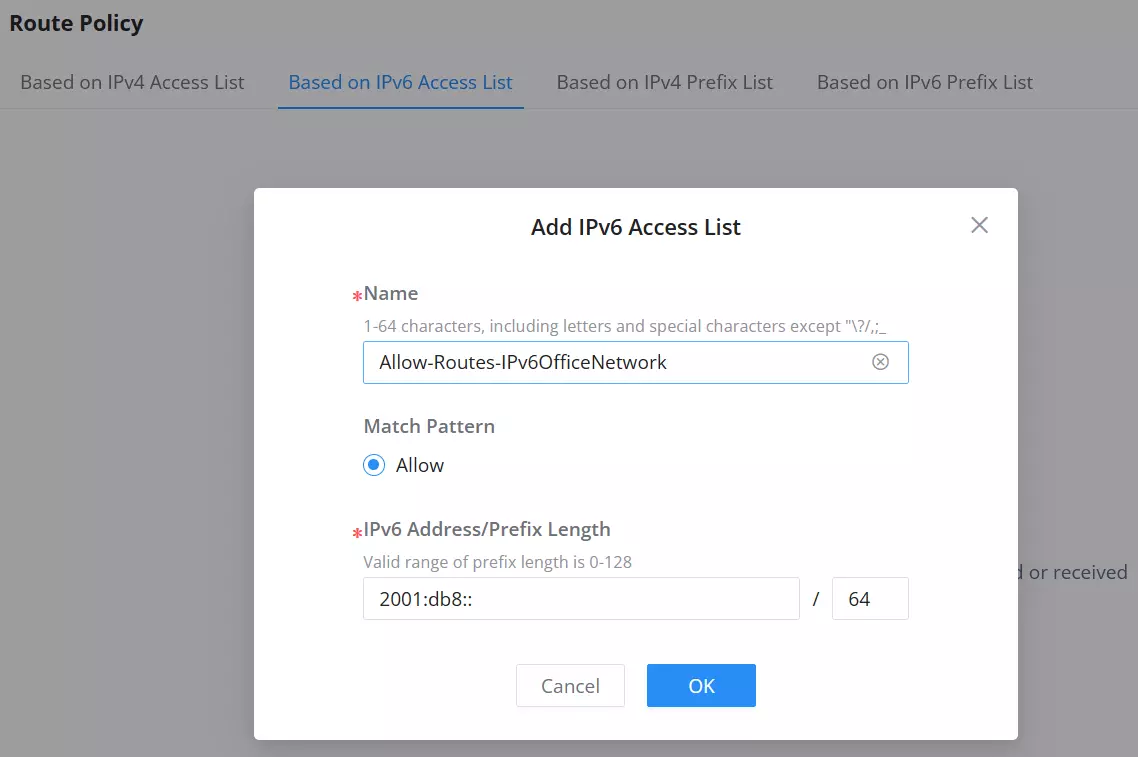
Example Configuration:
- Name: Allow-Routes-IPv6OfficeNetwork
- Match Pattern: Allow (this will permit routes that match the IPv6 address and prefix length).
- IPv6 Address/Prefix Length: 2001:db8::/64
This configuration allows routes from the 2001:db8::/64 network to be advertised or received by the BGP peer.
For more complex configurations, additional rules can be created similarly.
Based on IPv4 Prefix List
The Based on IPv4 Prefix List section allows you to create filtering rules for specific IPv4 prefixes that are either allowed or denied from being advertised or received by BGP peers. This gives you control over which prefixes are part of your BGP routing policies.
To configure an IPv4 Prefix List:
- Navigate to Routing → Based on IPv4 Prefix List.
- Click Add.
- Enter a Name for the rule (e.g., Allow-Prefixes-OfficeNetwork).
- Assign a Rule ID (the smaller the ID, the higher its priority in matching).
- Select the Allow match pattern.
- Specify the IPv4 Address Prefix and the corresponding prefix length (e.g., 192.168.1.0/24).
- Click OK to save the rule.
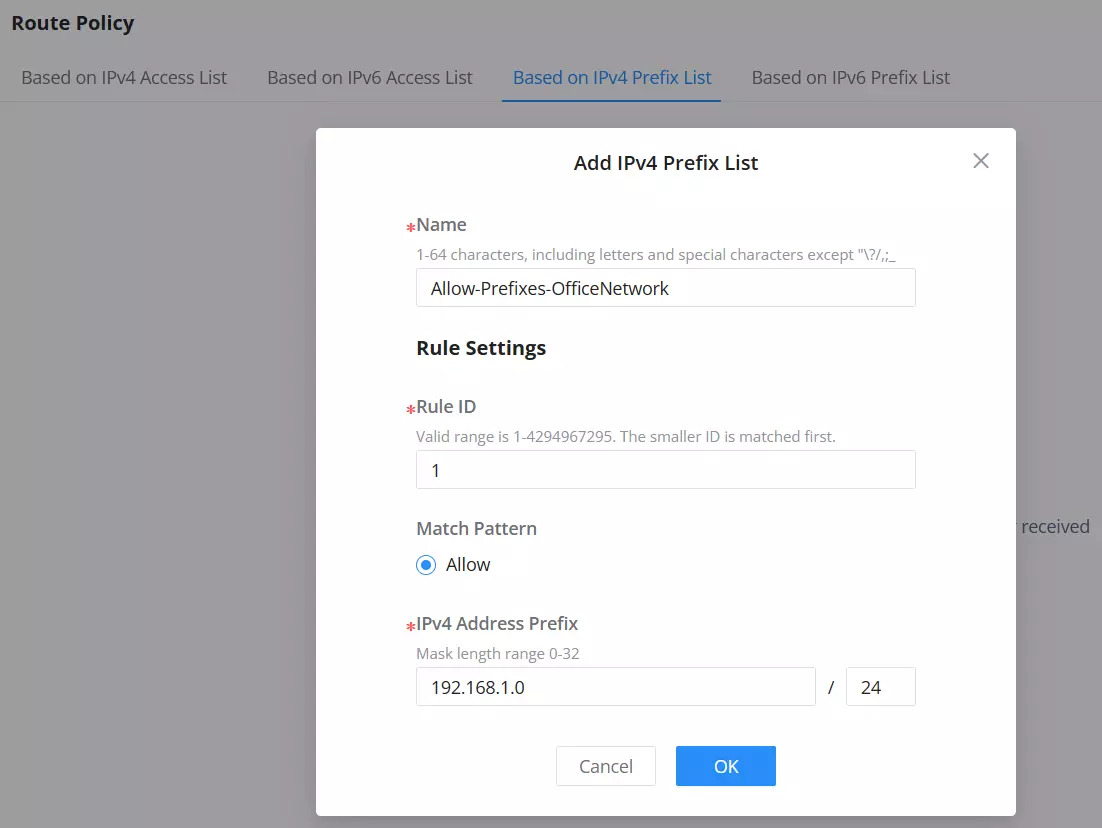
Example Configuration:
- Name: Allow-Prefixes-OfficeNetwork
- Rule ID: 1
- Match Pattern: Allow
- IPv4 Address Prefix: 192.168.1.0/24
This configuration allows prefixes from the 192.168.1.0/24 network to be advertised or received by the BGP peer.
Based on IPv6 Prefix List
The Based on IPv6 Prefix List section allows you to create filtering rules for specific IPv6 prefixes that are either allowed or denied from being advertised or received by BGP peers. This ensures that only certain IPv6 prefixes are part of your BGP routing policies.
To configure an IPv6 Prefix List:
- Navigate to Routing → Route Policy → Based on IPv6 Prefix List.
- Click Add.
- Enter a Name for the rule (e.g., Allow-Prefixes-IPv6Network).
- Assign a Rule ID (the smaller the ID, the higher its priority in matching).
- Select the Allow match pattern.
- Specify the IPv6 Address Prefix and the corresponding prefix length (e.g., 2001:db8::/64).
- Click OK to save the rule.
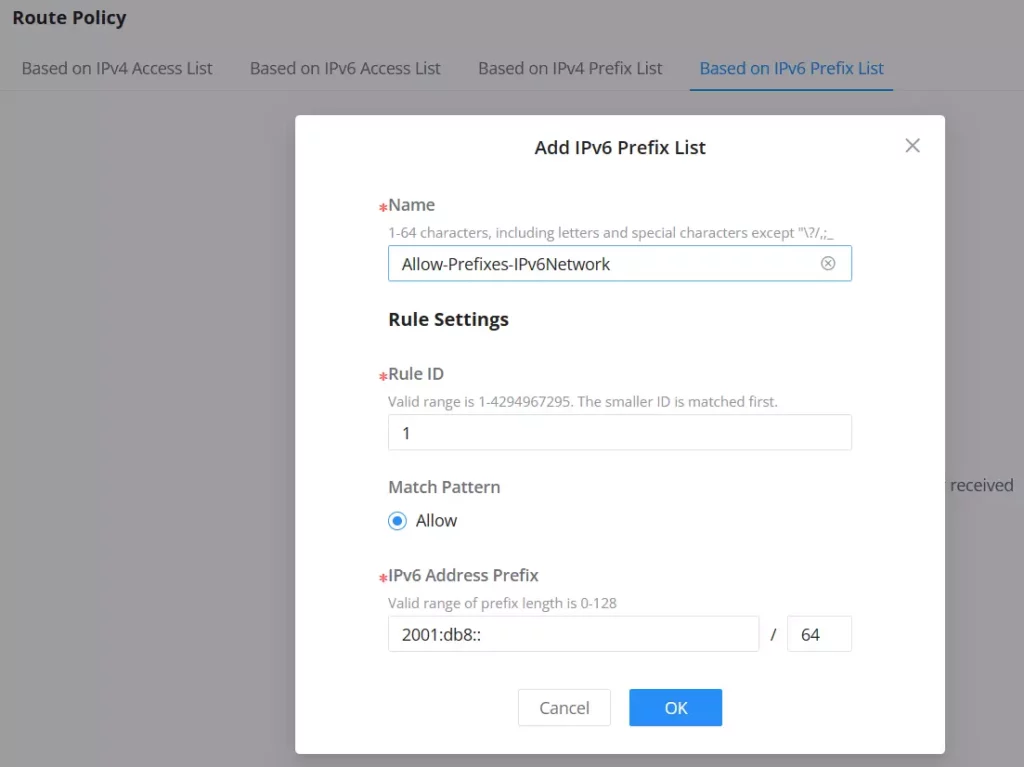
Example Configuration:
- Name: Allow-Prefixes-IPv6Network
- Rule ID: 1
- Match Pattern: Allow
- IPv6 Address Prefix: 2001:db8::/64
This configuration allows prefixes from the 2001:db8::/64 network to be advertised or received by the BGP peer.
POE
Power Over Ethernet (PoE) refers to supplying power over an Ethernet network, also known as a local area network-based power supply system PoL or Active Ethernet.
Usually, the terminal devices of the access point need to use a DC power supply, but due to insufficient wiring, these devices need unified power management. At this time, the switch interface provides the power supply function, which can solve the above problems and realize the precise control of the port PoE power supply.
Global
This page Displays the Power Supply Info like the number of PoE, Total and Remaining PoE Power, etc, and even the Supply Voltage.
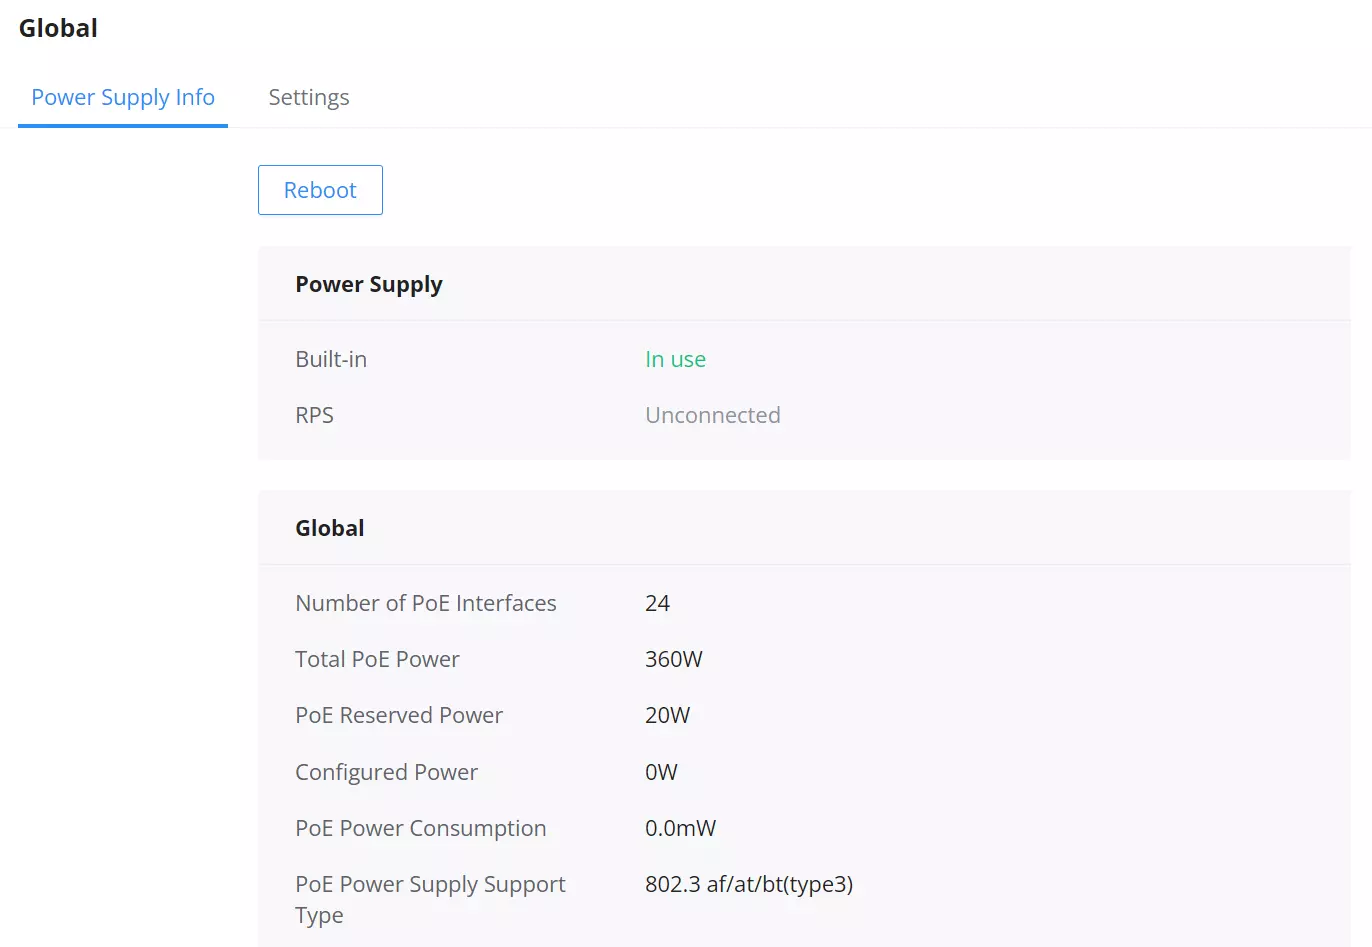
| Field or action | Description |
|---|---|
| PoE Reserved Power (W) | Reserves part of the PoE budget so it is not allocated to powered devices. The accepted range is 0 to 359 W; the observed value was 20 W. |
Click on button to soft restart the PoE module function.
PoE Remaining power
PoE Remaining power(W): specify the total reserved power of the PoE power supply, the default is 20 W.
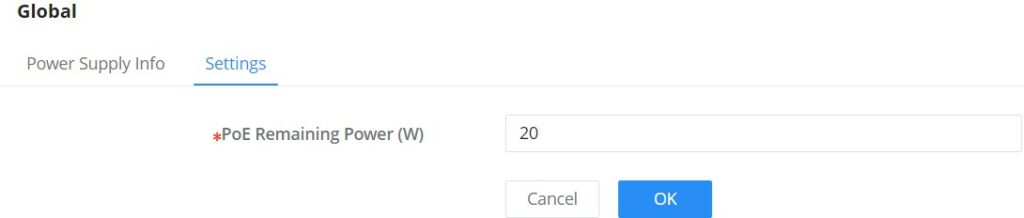
Application scenarios:
The device will dynamically allocate power to each interface according to the power consumed by each interface. During the running process of each PD device, its power consumption will continue to change, and the system will periodically calculate the total power required by all currently connected PDs. Whether the upper limit of the available PoE power is exceeded, if it exceeds, the system will automatically power off the PD device on the interface with lower priority to ensure the normal operation of other devices. However, sometimes there will be a sudden surge in power consumption, the remaining available power of the system cannot support this surge in demand, and the system has not yet had time to calculate the total power consumption exceeding the limit, to disconnect the power supply of the interface with lower priority. When the PoE power supply is overloaded, the overload protection will be powered off, and all PD devices will be powered off. Use the PoE power-reserved command to reasonably set the reserved power of the system. In the event of a sudden surge in power demand, the reserved power of the system can support the sudden demand and ensure that the system has time to power off the devices on the interfaces with low priority. method to ensure the stable operation of other equipment.
Interface PoE configuration
Select the switch interface that supports the PoE power supply to be configured. Multiple choices are possible.
Click on the “Edit” button or icon to change the configuration per port including Power Supply Standard, Power Mode, Power Limit Mode, and Power Supply Priority.
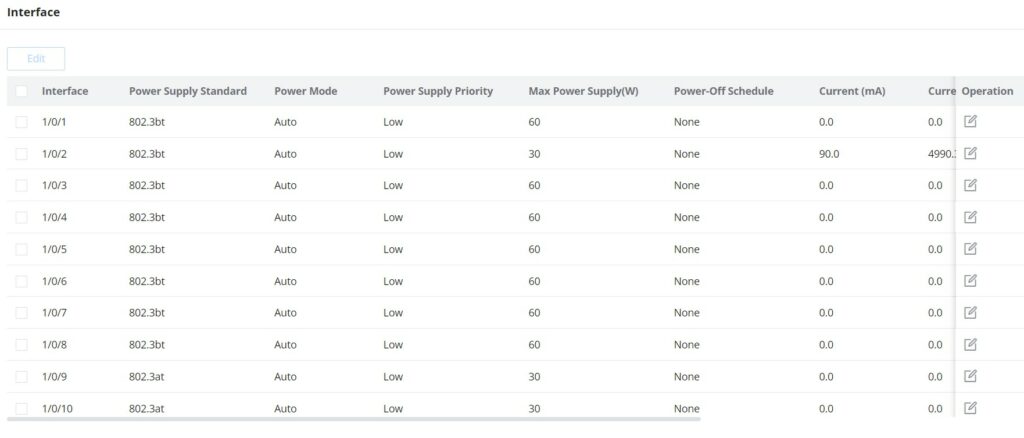
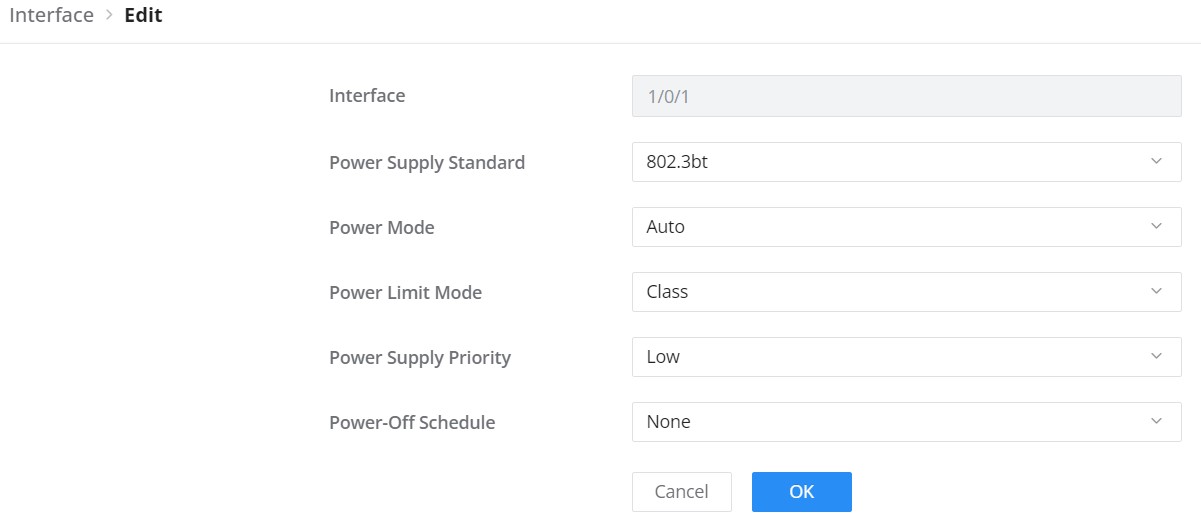
QOS
The popularity of the network and the diversification of services have led to a surge in Internet traffic, resulting in network congestion, increased forwarding delay, and even packet loss in severe cases, resulting in reduced service quality or even unavailability. Therefore, to carry out these real-time services on the network, it is necessary to solve the problem of network congestion. The best way is to increase the bandwidth of the network, but considering the cost of operation and maintenance, this is not realistic. The most effective solution is to apply a ” Guaranteed ” policies govern network traffic. QoS technology is developed under this background. QoS is quality of service, and its purpose is to provide end-to-end service quality assurance for various business needs. QoS is a tool for effectively utilizing network resources. It allows different traffic flows to compete for network resources unequally. Voice, video, and important data applications can be prioritized in network equipment.
Port Priority
On this page, the user can enable/disable port priority for each interface (port/LAG), supported modes are (CoS, DSCP, CoS-DSCP, or IP-Precedence).
Please navigate to Web UI → QoS → Port Priority page.
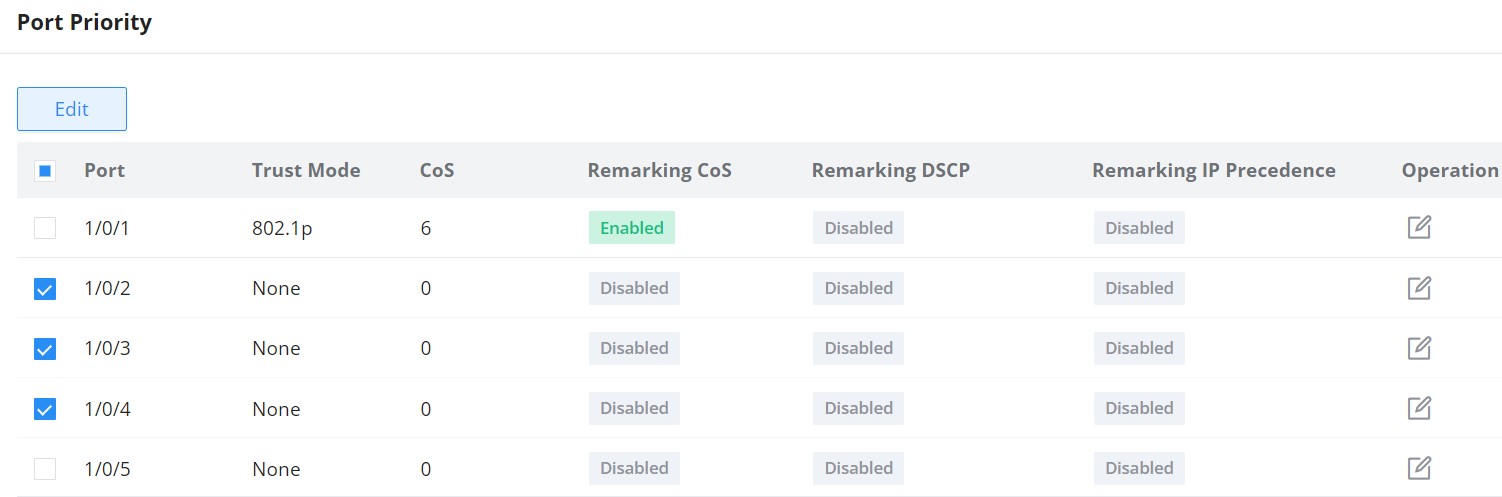
Then the user can click on the “Edit” button for further configuration per Port/LAG.
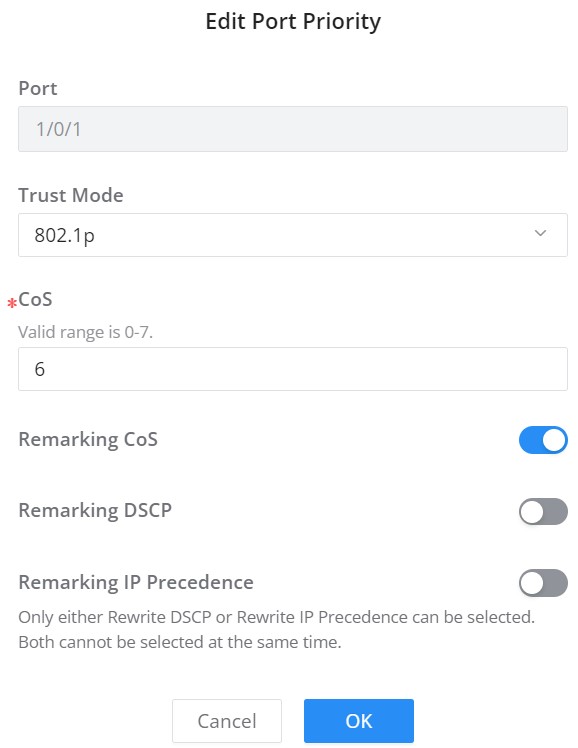
Port | Displays the selected port GE/LAG. |
Trust Mode | Select the QoS operation mode:
|
CoS | Set the CoS value of the interface, the value range is an integer from 0 to 7 (7 is the highest priority ), the default is 0. |
Remarking CoS | Set whether to enable Remarking CoS function of outgoing packets, which is disabled by default. |
Remarking DSCP | Set whether to enable Remarking DSCP function of outgoing packets, and it is disabled by default. |
Re-marking IP Precedence | Set whether to enable Remarking IP Precedence function of outgoing packets, and it is disabled by default. Note : Only one of DSCP and IP Precedence re-marking can be enabled. |
QoS Port Priority
Priority Mapping
Priority mapping is used to realize the conversion between the QoS priority carried in the packet and the internal priority of the device ( also known as the local priority, which is the priority used by the device to differentiate the service level of the packet ) so that the device provides the Differentiated QoS service quality. Users can use different QoS priority fields in different networks according to network planning.
- CoS Mapping
Shows the mapping relationship between queues and CoS remarking priorities.
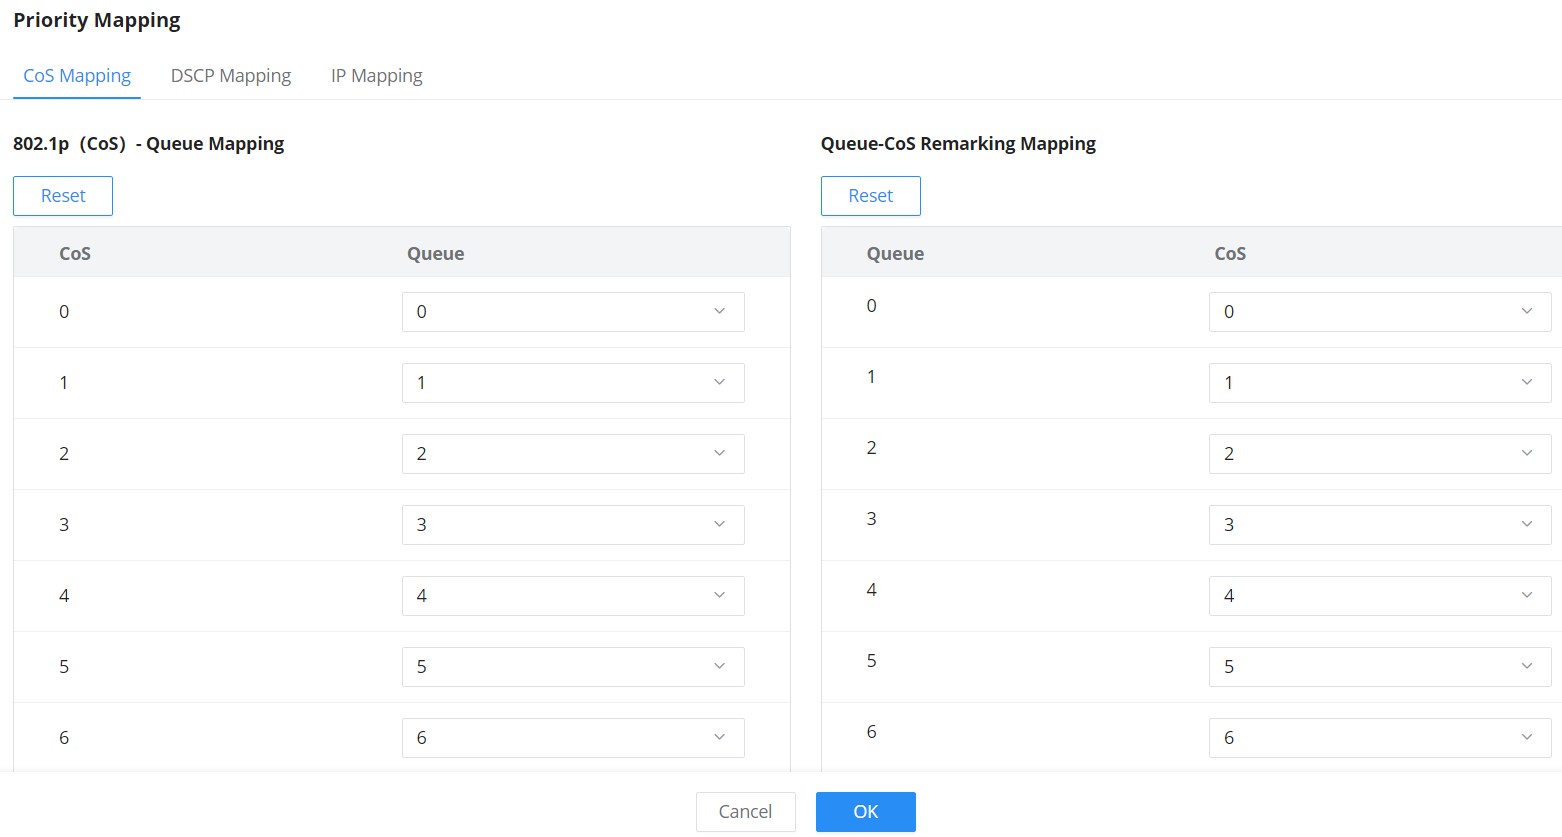
- DSCP Mapping
Shows the mapping relationship between DSCP values and queue priorities.
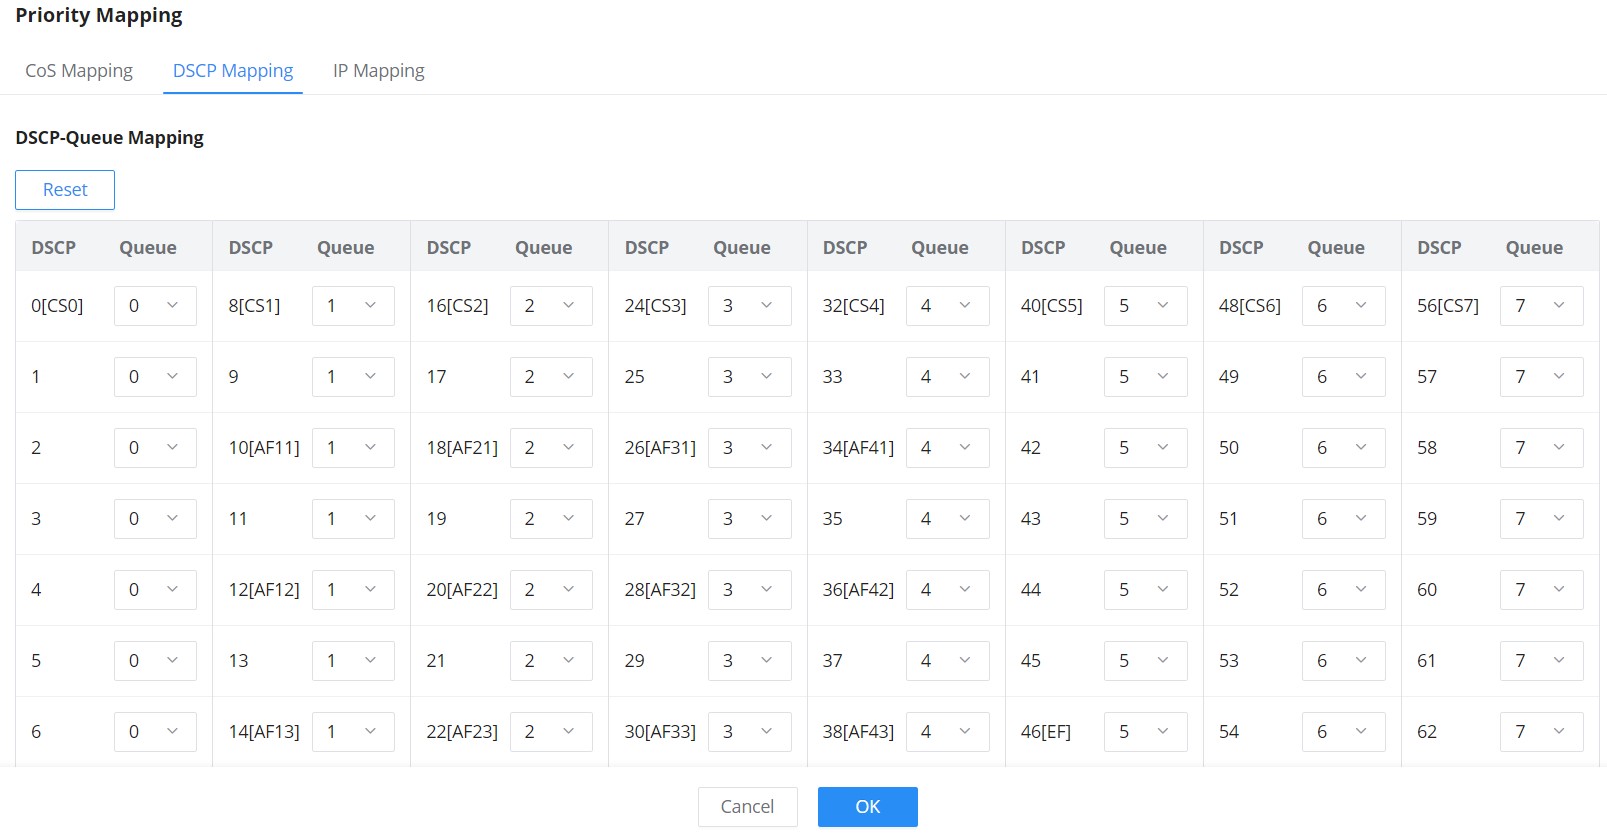
- IP Mapping
Shows the mapping relationship between IP priority and queue.
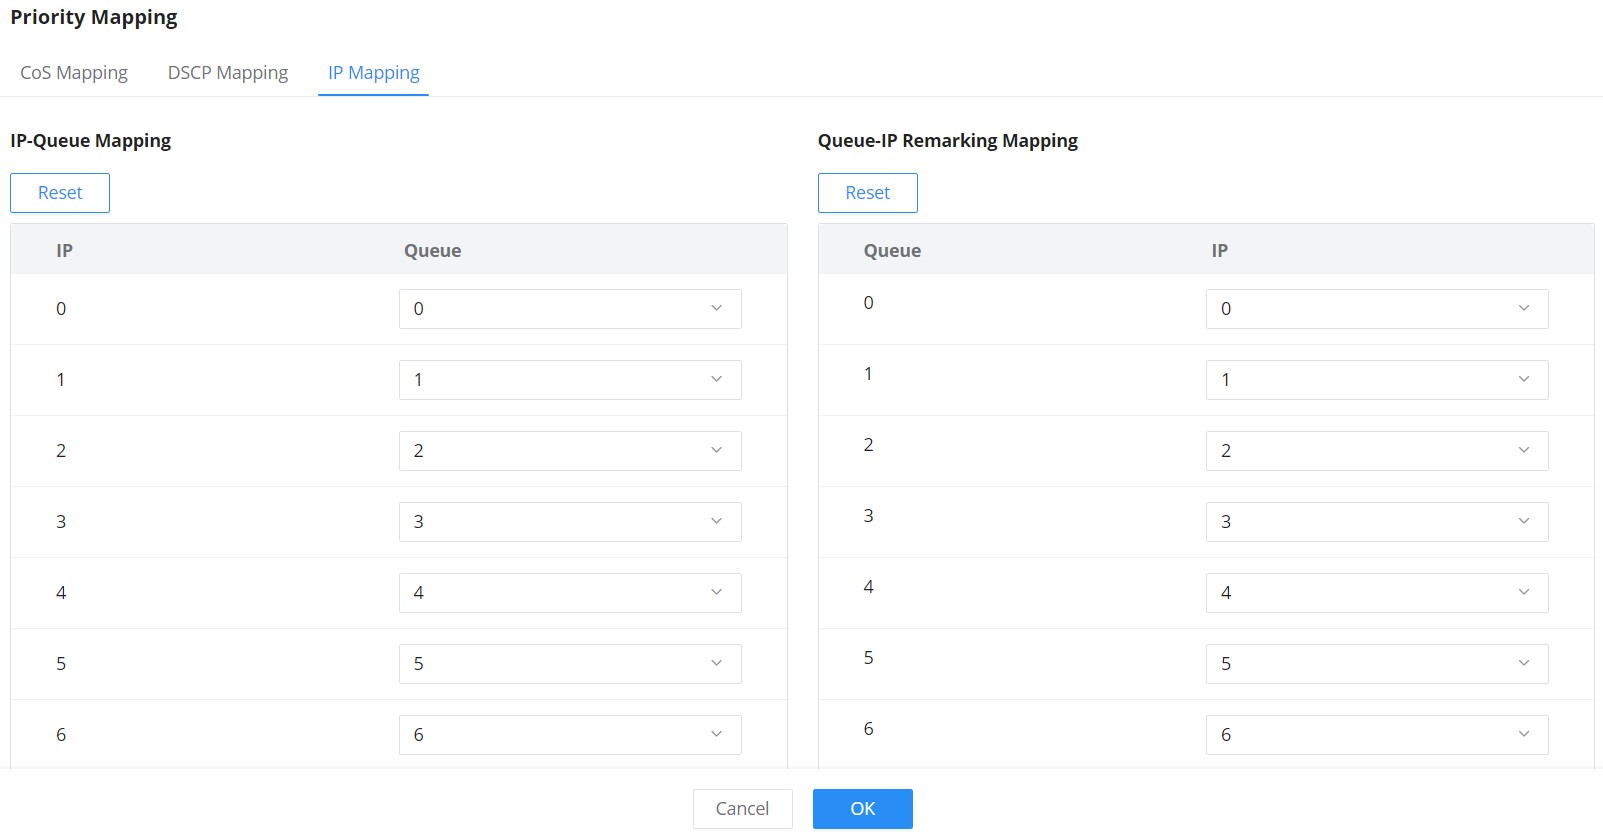
Queue Scheduling
When congestion occurs in the network, the device will determine the processing order of forwarding packets according to the specified scheduling policy, so that high-priority packets are preferentially scheduled.
Queue scheduling algorithm: queue scheduling according to the switch interface.
- Strict priority (SP, Strict Priority) scheduling: The flow with the highest priority is served first, and the flow with the second highest priority is served until there is no flow at that priority. Each interface of the switch supports 8 queues ( queues 0-7 ), queue 7 is the highest priority queue, and queue 0 is the lowest priority queue. Disadvantage: When congestion occurs, if there are packets in the high-priority queue for a long time, the packets in the low-priority queue cannot be scheduled, and data cannot be transmitted.
- Weighted Round Robin (WRR, Weighted Round Robin) scheduling: each priority queue is allocated a certain bandwidth, and provides services for each priority queue according to the priority from high to low. When the high-priority queue has used up all the allocated bandwidth, it is automatically switched to the next priority queue to serve it.
- Weighted Fair Queuing (WFQ): Based on ensuring fairness ( bandwidth, delay) as much as possible, priority considerations are added, so that high-priority packets have more opportunities for priority scheduling than low-priority packets. WFQ can automatically classify flows by their “session” information (protocol type, source and destination IP addresses, source, and destination TCP or UDP ports, priority bits in the ToS field, etc.) Place each flow evenly into different queues, thus balancing the latency of the individual flows as a whole. When dequeuing, WFQ allocates the bandwidth that each flow should occupy at the egress according to the flow priority (Precedence) . The smaller the priority value is, the less bandwidth is obtained; otherwise, the more bandwidth is obtained.
- SP-WRR: the switch schedules packets in the SP scheduling group preferentially, and when the SP scheduling group is empty, schedules the packets in the WRR scheduling group. Queues in the SP scheduling group are scheduled with the SP queue scheduling algorithm. Queues in the WRR scheduling group are scheduled with WRR.
- SP-WFQ: the switch schedules packets of queues in the WFQ group based on their minimum guaranteed bandwidth settings, then uses SP queuing to schedule the queues in the SP scheduling group, then uses WFQ to schedule the queues in the WFQ scheduling group in a round robin fashion according to their weights.
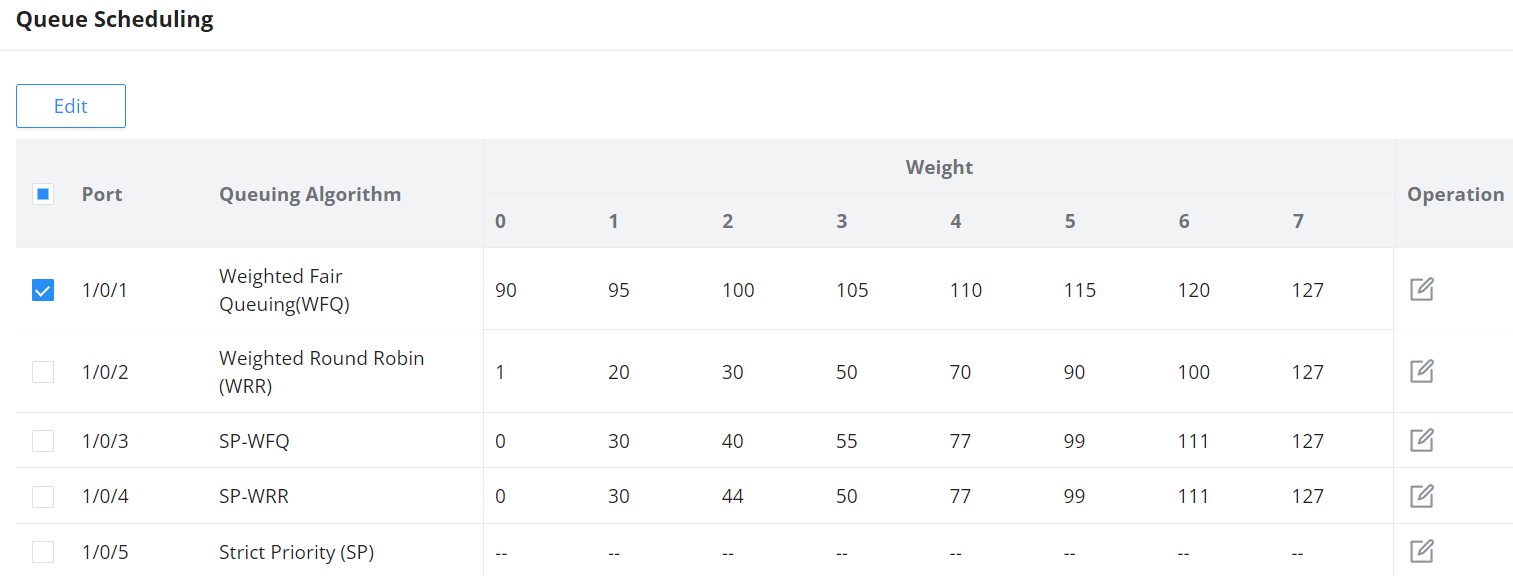
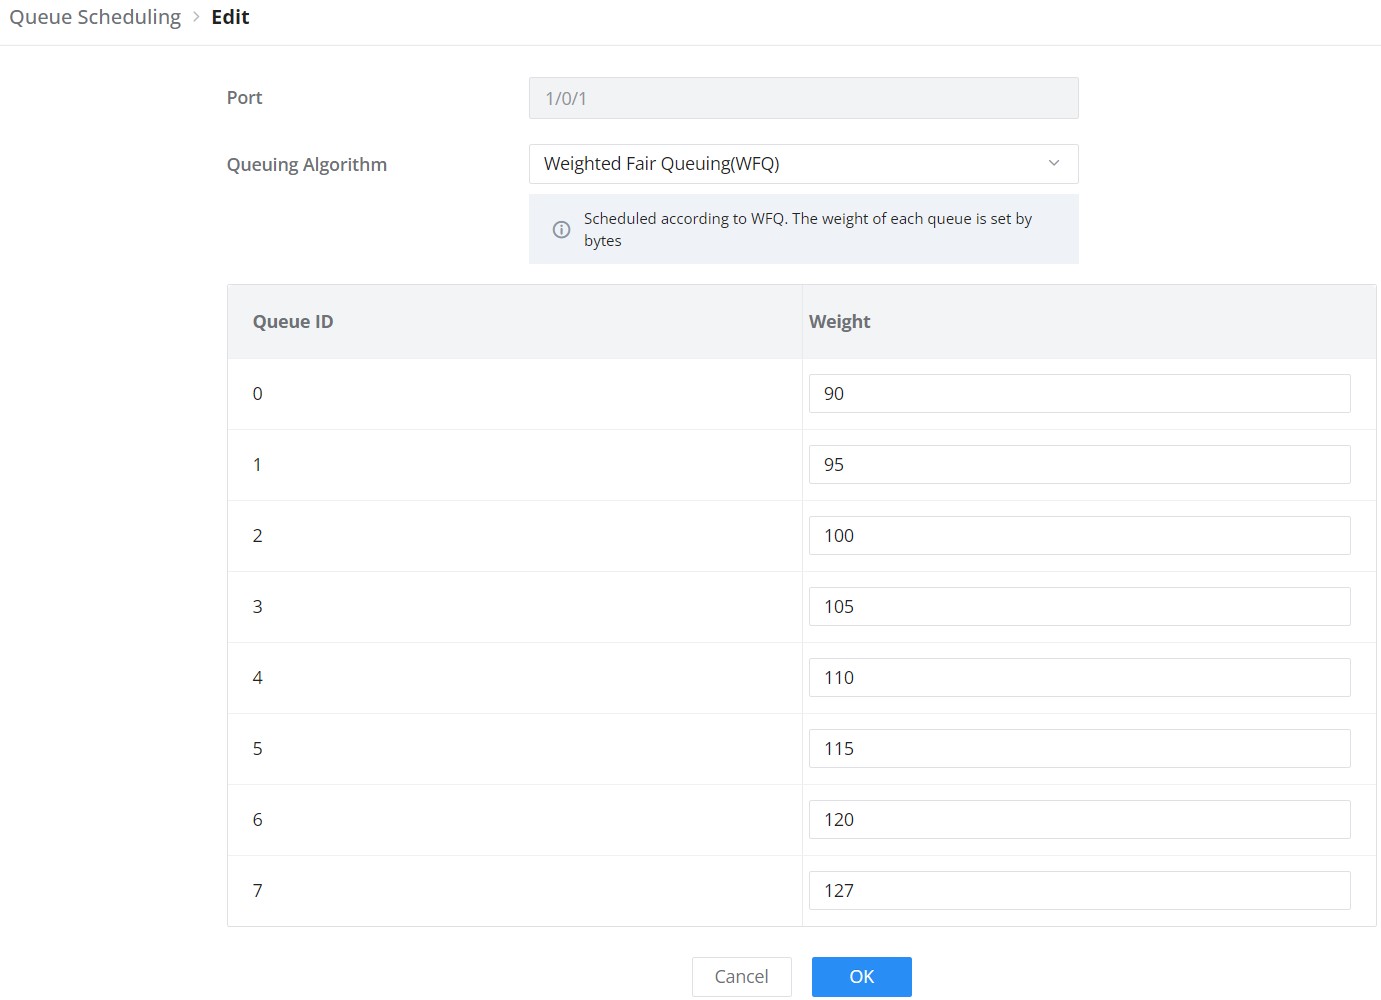
Queue Shaping
When the packet sending rate is higher than the receiving rate, or the interface rate of the downstream device is lower than the interface rate of the upstream device, network congestion may occur. If the size of the service traffic sent by users is not limited, the continuous burst of service data from a large number of users will make the network more congested. To make the limited network resources serve users more effectively, it is necessary to restrict the service flow of users.
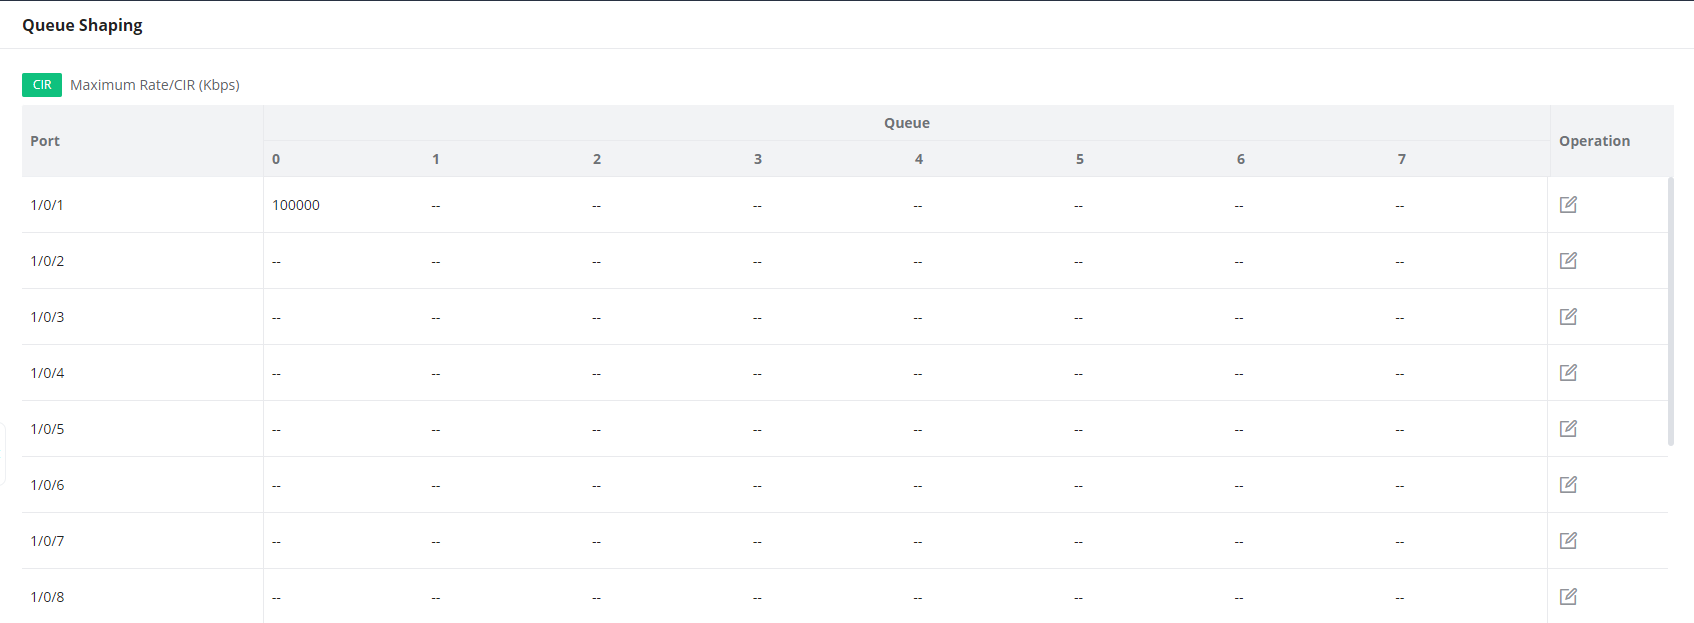
To configure a port, click on the “Edit” icon under the operation column.
Maximum Rate/CIR (Kbps): Configures the maximum rate of shaping. The value must be an integer between 16-1000000 Kbps and must be multiples of 16. By default, it’s the port rate.
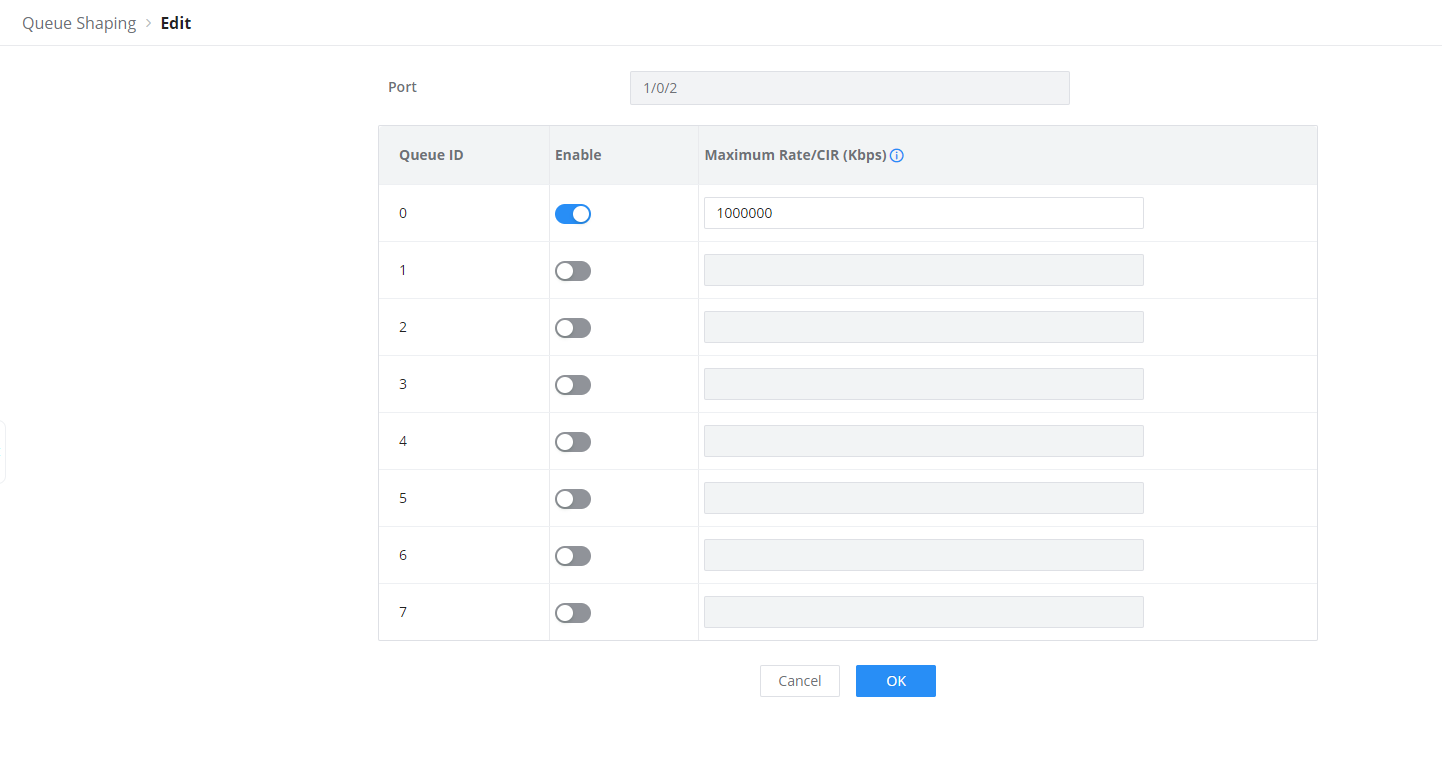
Rate Limit
Interface rate limit can limit the total rate of all packets sent or received on an interface. The interface rate limit also uses the token bucket to control the flow. If an interface rate limit is configured on an interface of the device, all packets sent through this interface must first be processed through the token bucket of the interface rate limiter. If there are enough tokens in the token bucket, the packet can be sent; otherwise, the packet will be discarded or cached.
To configure Rate Limit, please navigate to Web UI → QoS → Rate Limit.

To configure a port, click on the “Edit” icon under operation column, then set the CIR and CBS for both Ingress and Egress.
CIR (Committed Information Rate): the guaranteed average transmission rate or the minimum guaranteed traffic delivered in the network.
CBS (Committed Burst Size): the average volume of burst traffic that can pass through an interface.
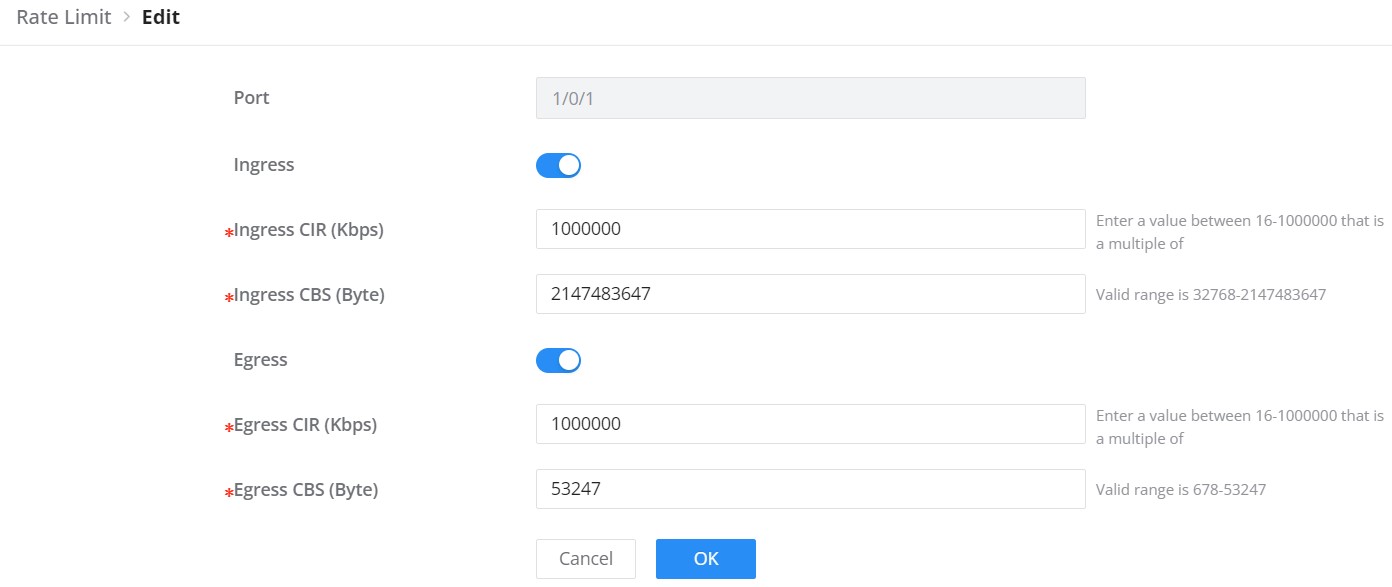
SECURITY
The switches support many tools and features to enhance the security of the device against misconfiguration or attacks.
Storm Control
Traffic suppression can limit the rate of broadcast, unknown multicast , unknown unicast, known multicast, and known unicast packets by configuring thresholds , preventing broadcast, unknown multicast packets, and unknown unicast packets from generating broadcast storms. Large traffic impact of known multicast packets and known unicast packets.
Storm control can block the traffic of broadcast, unknown multicast and unknown unicast packets by blocking packets or shutting down ports . The device supports storm control for the above three types of packets on the interface according to the packet rate, byte rate, and percentage . During a detection interval, the device monitors the average rate of three types of packets received on the interface and compares it with the configured maximum threshold. When the packet rate is greater than the configured maximum threshold , the device performs storm control on the interface and executes the Configured storm control actions. Storm control actions include blocking packets and shutting down / shutdown interfaces.
- If packets are blocked, when the average rate of receiving packets on the interface is less than the specified minimum threshold, storm control will release the blocking of the packets on the interface.
- If the action is to shut down / shutdown the interface, you need to manually run the command to bring up the interface, or enable the interface state to automatically return to UP, it’s also possible to use the Auto Recovery function to bring up the interface automatically.
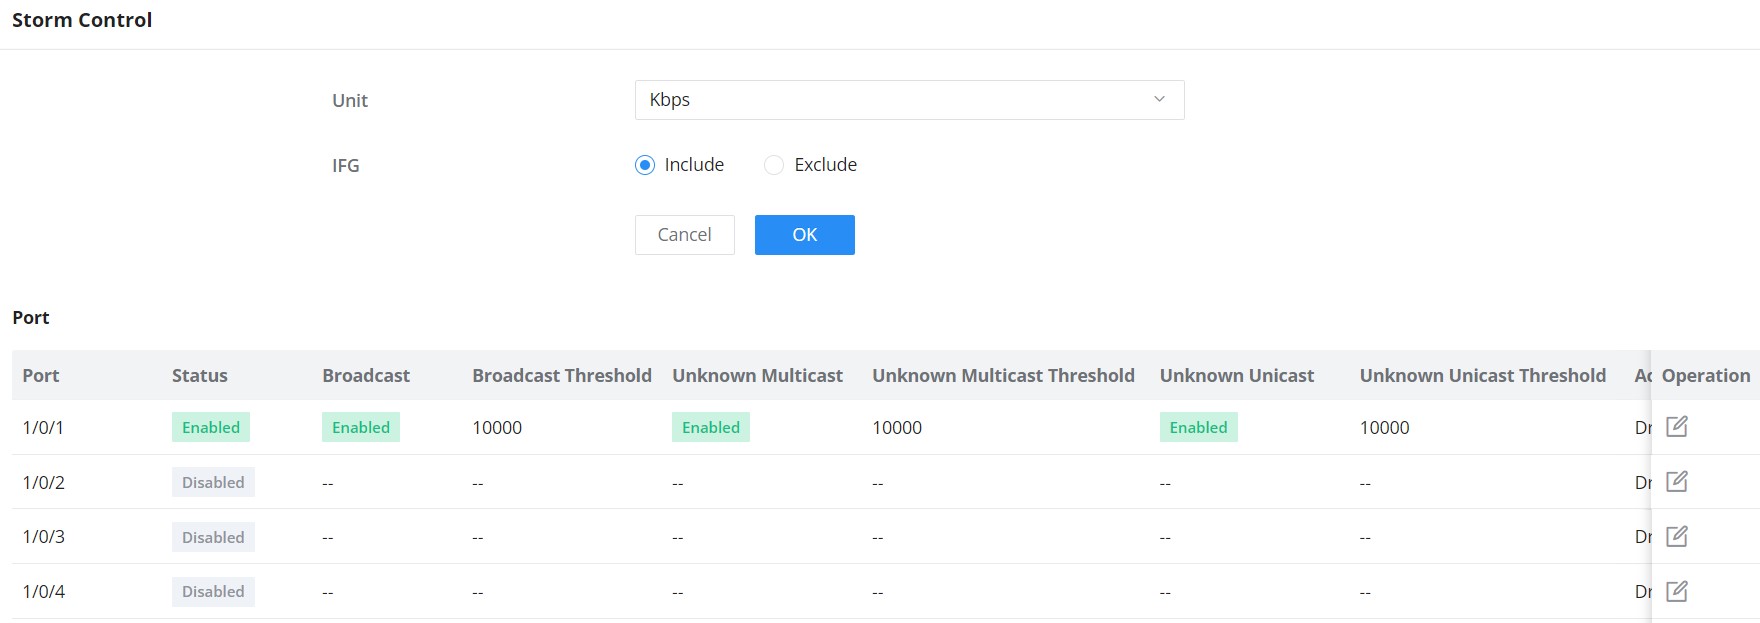
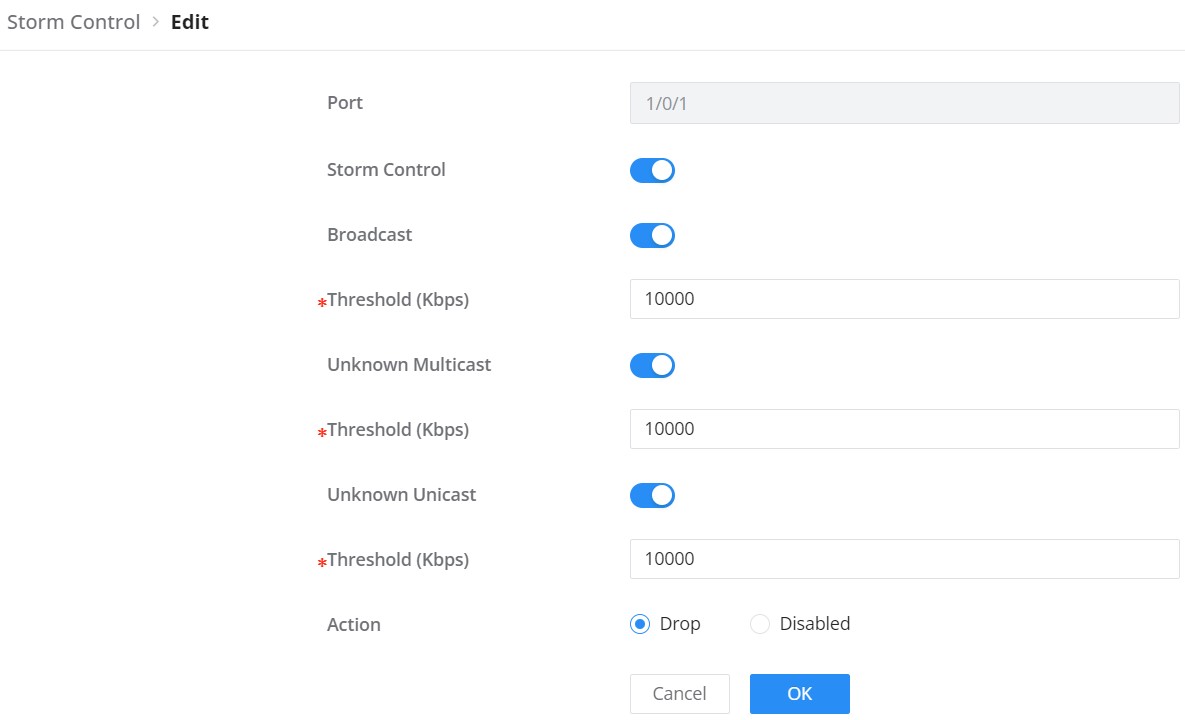
Unit | Select Unit:
|
IFG | Select IFG ( Inter Frame Gap ):
|
Storm Control → Edit | |
Port | Displays the selected port. |
Storm Control | Select whether to enable Storm Control on the selected port or not. |
Broadcast | Set whether to enable the storm threshold setting for broadcast packets. If Enabled Please enter a Treshhold (Kbps). Note: The valid range is 16~1000000, which must be a multiple of 16. Default is 10000. |
Unknown Multicast | Set whether to enable the storm threshold setting for the Unknown Multicast packets If Enabled Please enter a Treshhold (Kbps). Note: The valid range is 16~1000000, which must be a multiple of 16. Default is 10000. |
Unknown Unicast | Set whether to enable the storm threshold setting for the Unknown Unicast packets. If Enabled Please enter a Treshhold (Kbps). Note: The valid range is 16~1000000, which must be a multiple of 16. Default is 10000. |
Action | Select the state of setting
|
Storm Control
Port Security
By converting the MAC address learned by the interface into secure MAC addresses ( including secure dynamic MAC address, secure static MAC address and Sticky MAC) , port security prevents illegal users from communicating with the switch through this interface, thereby enhancing the security of the device.
On the Secure MAC Addresses tab, use VLAN/MAC Address/Port to filter entries. The list shows VLAN, MAC Address, Type, Port, and Operation.
Security MAC addresses are divided into: Secure Dynamic MAC, Secure Static MAC and Sticky MAC.
Secure Dynamic MAC Address | If enabled but the Sticky MAC function is not enabled. | If the device is restarted, the entries will be lost and need to be relearned. |
Secure Static MAC Address | Static MAC address manually configured when port security is enabled. | The entries will not be aged, and will not be lost after a reboot. |
Sticky MAC Address | The MAC address converted after the port security is enabled and the Sticky MAC function is enabled at the same time | The entries will not be aged , and the addresses will not be lost after restarting the device. |
Secure MAC Address Types
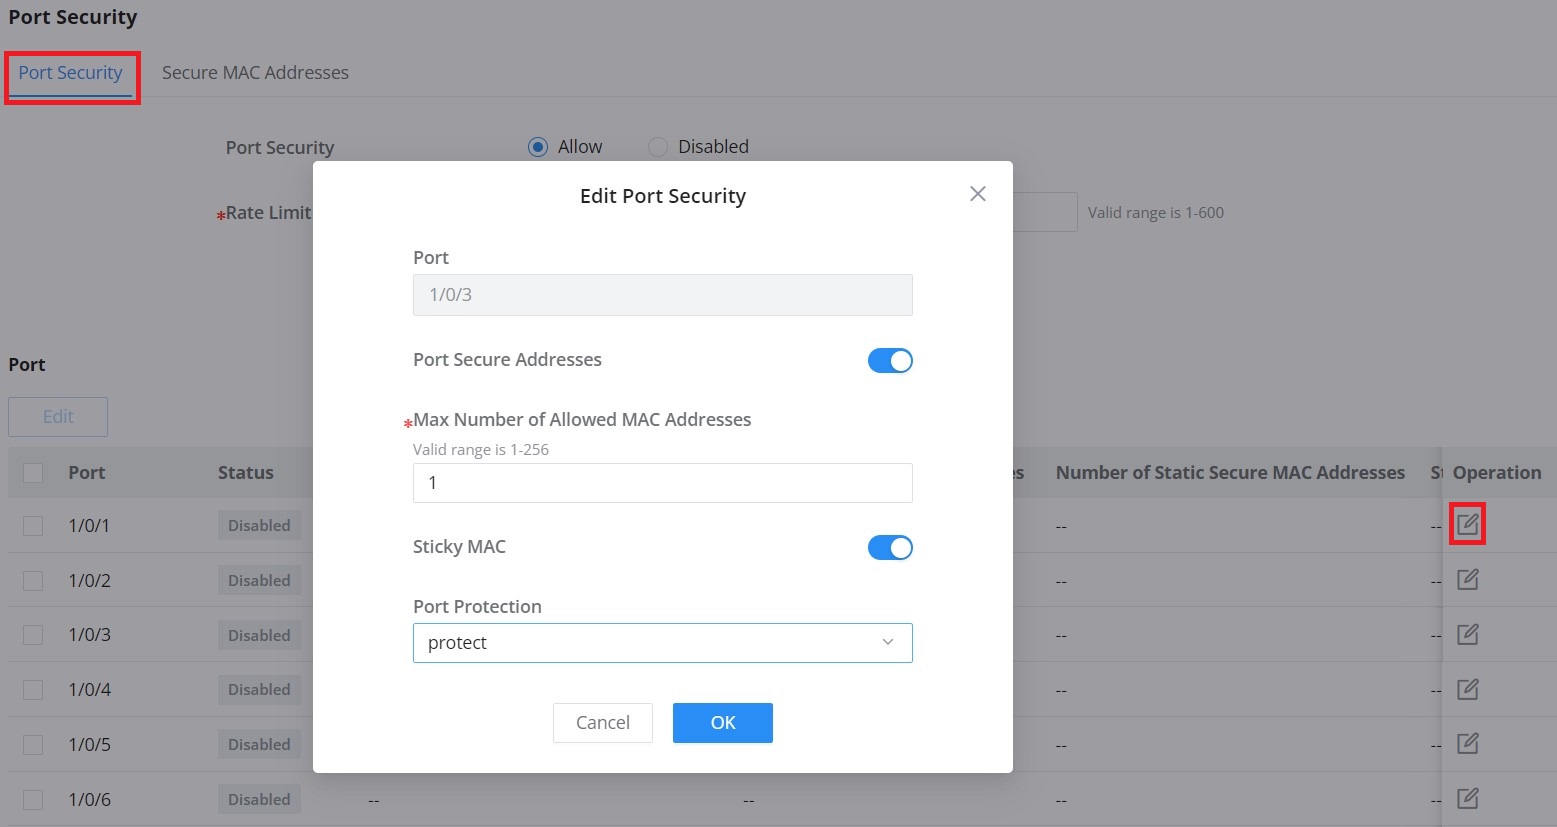
Port Security | Click Allow to set the port security function to be enabled globally , by default is disabled. |
Rate Limit (packet/s) | Set the rate at which the port MAC address is learned. The value is an integer from 1 to 600, the default is 100. |
Edit Port Security | |
Port | Displays the selected ports. |
Port Security Address | Click to enable Port Security Address, by default is disabled. |
Maximum MAC Number | Set the maximum number of MAC addresses to be learned by the interface , the value range is an integer from 1 to 256 , and the default is 1 . After the maximum number is reached , if the switch receives a packet whose source MAC address does not exist, regardless of whether the destination MAC address exists, the switch considers that there is an attack by an illegal user, and will protect the interface according to the port protection configuration (Protect, Restrict or Shutdown). |
Sticky MAC | When the port security is enabled, the Sticky MAC function can be enabled, by default it’s disabled . When enabled, the interface will convert the learned secure dynamic MAC address into a Sticky MAC. If the maximum number of MAC addresses has been reached, the MAC address in the non-sticky MAC entry learned by the interface will be discarded , and a trap alarm will be reported according to the interface protection mode configuration. |
Port Protection | Set the protection action when the number of MAC addresses learned by the interface reaches the maximum number or static MAC address flapping occurs . There are three modes (Protect, Restrict or Shutdown), the default is Protect.
|
Port Security
Port Isolation
With the port isolation function, the isolation between ports in the same VLAN can be realized. As long as the user adds the port to the isolation group, the Layer 2 data isolation between the ports in the isolation group can be realized. The port isolation function provides users with a safer and more flexible networking solution.
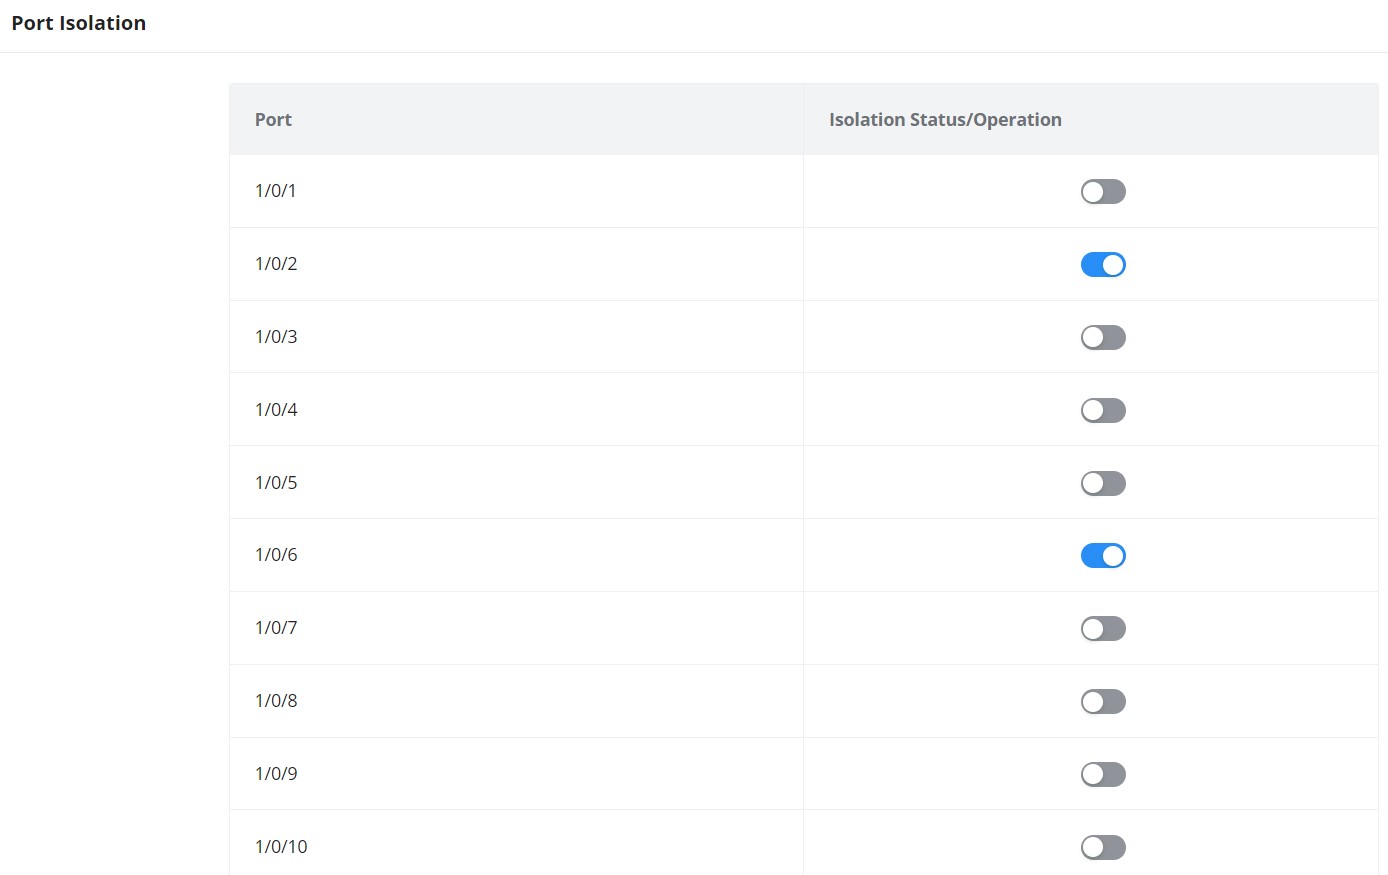
ACL
Access control list (ACL) is a collection of one or more rules. A rule is a judgment statement that describes the matching conditions of a packet. These conditions can be the source address, destination address, port number, etc. of the packet. ACL is essentially a packet filter, and the rule is the filter element of the filter. The device matches packets based on these rules, filters out specific packets , and allows or organizes the packets to pass through according to the processing policy of the service module that applies the ACL.
IPv4/IPv6 ACL
To add an IPv4 or IPv6 ACL rule, navigate to Security → ACL → IPv4 tab or IPv6 tab, then click on “Add” button to add an IPv4/IPv6 based ACL rule.

The rules action can be defined in one of the four ways below:
- Drop: This action denies or blocks traffic that matches the specified ACL rule, which prevents the packet from being forwarded through the network.
- Allow: This action permits traffic that matches the ACL rule, allowing the packet to pass through and continue to its destination.
- Shut Down: This action disables the interface or port that the traffic is passing through if the ACL rule is triggered, effectively stopping all traffic on that interface.
- Redirect to Interface: This action forwards the traffic matching the ACL rule to a different interface than it was originally destined for, often used for traffic monitoring, load balancing, or security purposes.

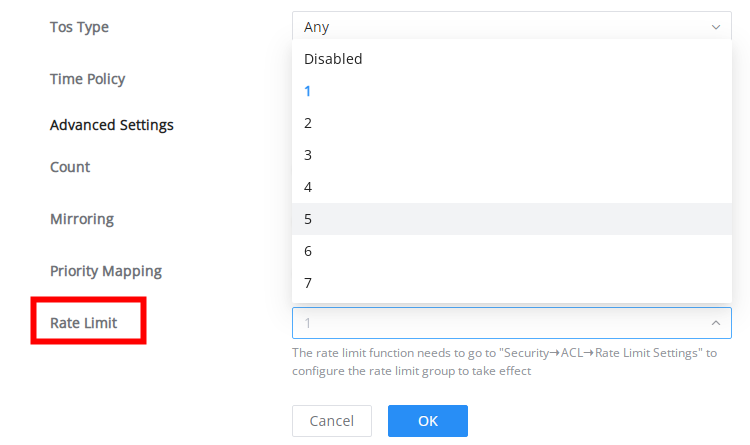
Configuring an ACL-based RSPAN
To perform an ACL-based RSPAN, please follow the below steps:
- Select an image group in ACL Image
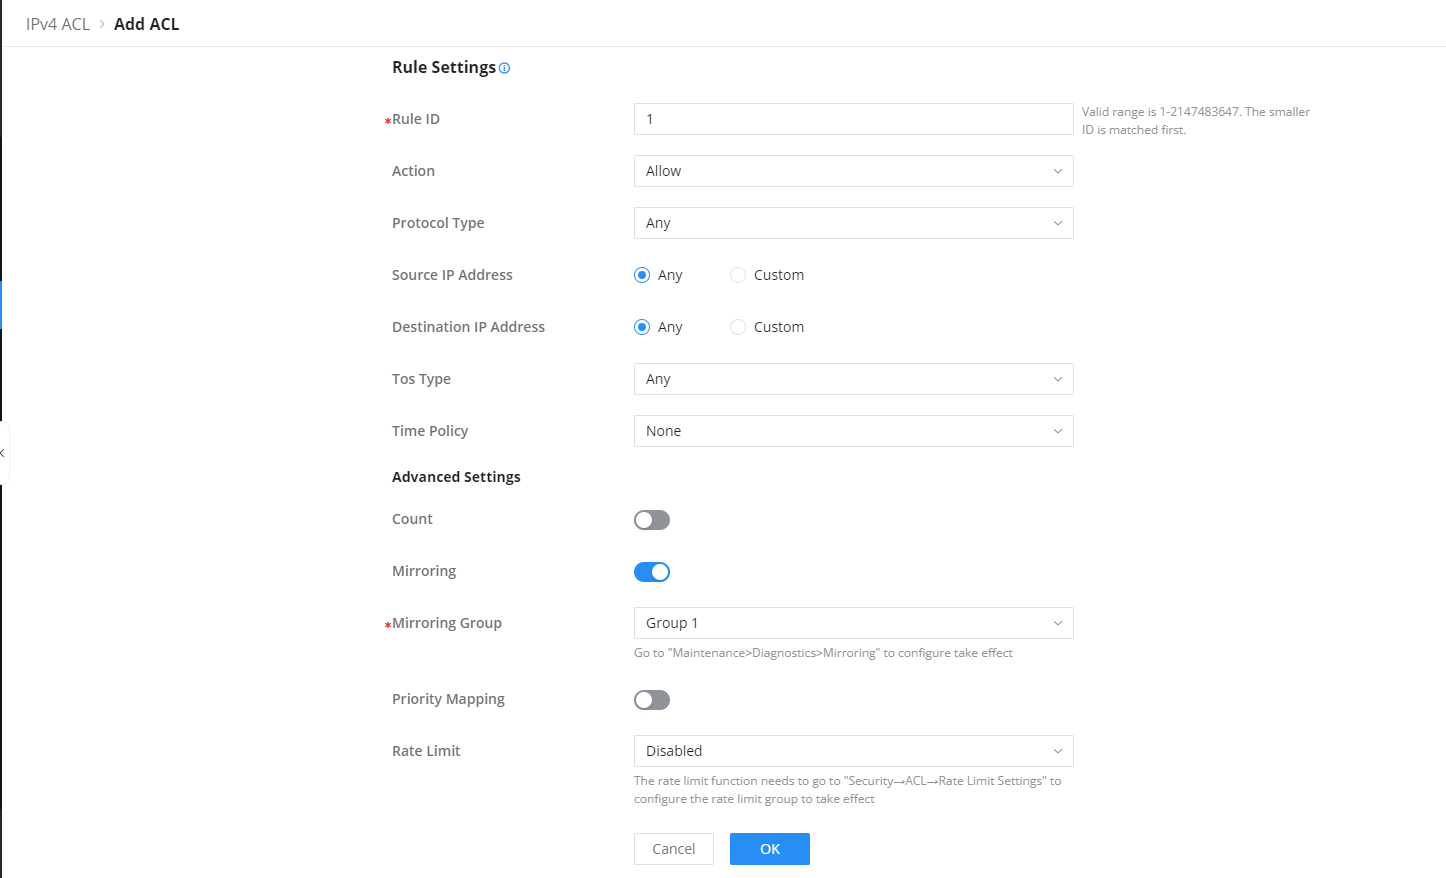
- Then, under ACL →VLAN Binding ACL, select the corresponding port/VLAN binding ACL.
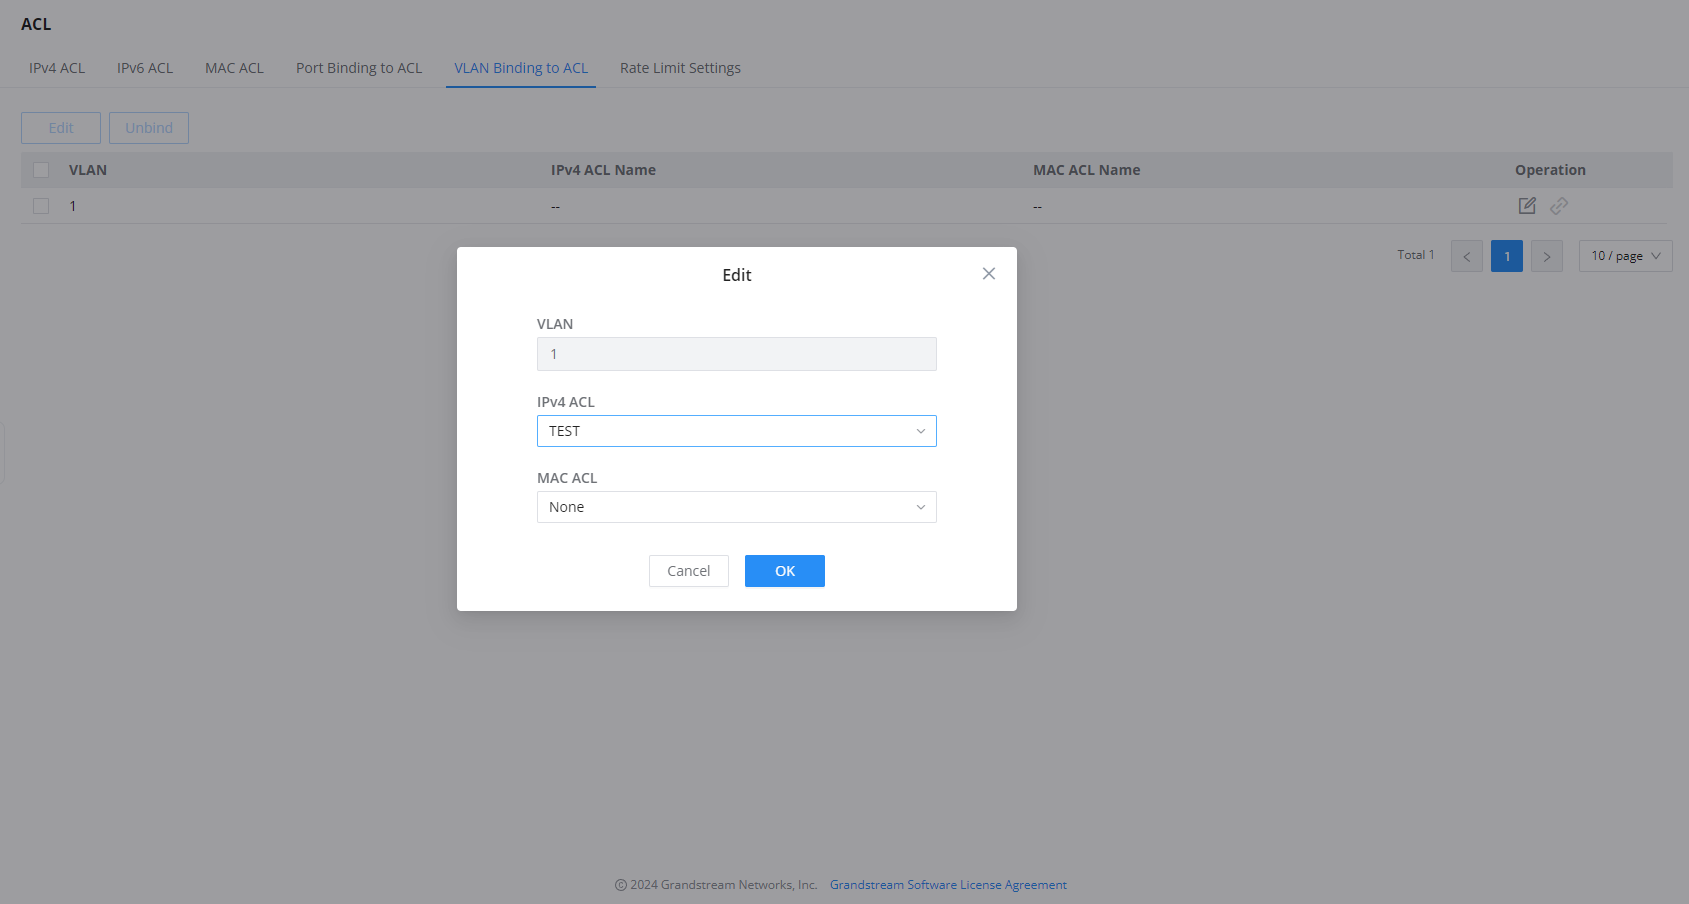
- Then go to Diagnostics → Mirroring → Setup Mirroring Group. If you select RSPAN, you can only use it as a source switch and you need to set the output port and remote VLAN.
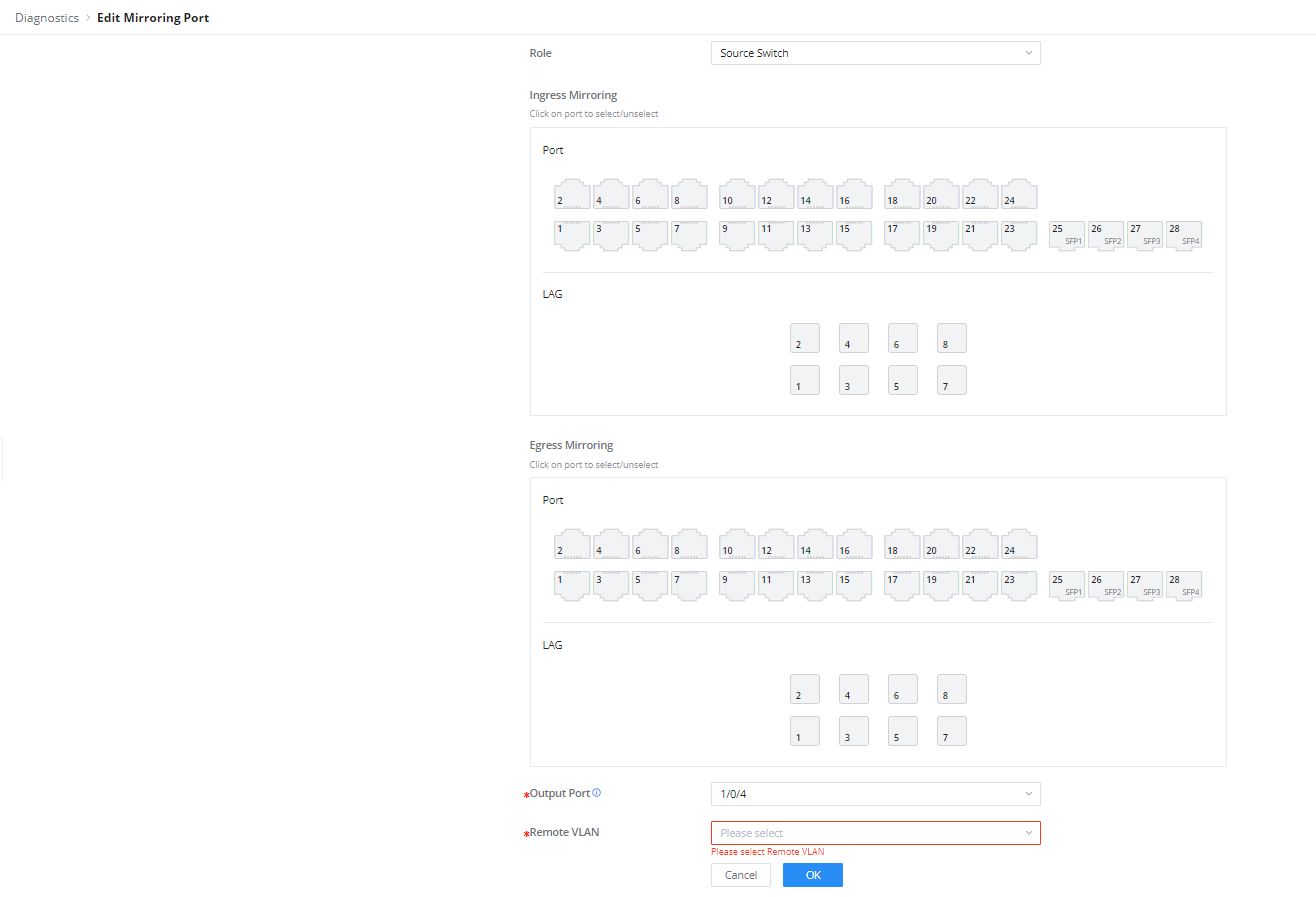
MAC ACL
To add an ACL based on the MAC address, on the MAC ACL tab, click on the “Add” button to add an ACL rule, then configure the Source MAC Address and the Destination MAC Address accordingly. Please refer to the figure below:

Port Binding to ACL
ACL Binding lets the user bind MAC ACL or IP ACL to certain ports GE/LAG.
To apply IP/MAC ACL rules on multiple ports, select the ports first then click on the “Edit” button, then select the IP and MAC ACL rule from the drop-down list.
To apply the ACL rule on a specific port, click on the “Edit icon” on the right side of the page as shown below:

VLAN Binding to ACL
On this page, the users can bind the IP/MAC ACL rule to a VLAN(s), to apply the ACL rules to multiple VLANs, first check the VLANs from the list then click on the “Edit” button, select the ACL rule from the drop-down list under IP/MAC ACL.
For example: if the IP/MAC ACL rule is configured with a rate limit, and then bound to a VLAN, the bandwidth limit will be applied to the specified VLAN.
refer to the figure below:

Rate Limit Settings
The Rate Limit Settings section in ACL (Access Control List) allows users to configure rate limiting for up to 128 groups. Rate limiting helps manage and control the amount of traffic sent or received on the network, preventing congestion and ensuring fair usage. This feature is crucial for maintaining optimal network performance and avoiding overloads.
| Field or action | Description |
|---|---|
| By packet | Burst Packet (pps): 1 to 65535, default 10. Rate Threshold (pps): 1 to 262143. |
| By byte | Burst Byte (Bps): 1024 to 8388480 in multiples of 128. Rate Threshold (KBps): 2 to 125000 in multiples of 2. |

The users can configure up to 128 groups, by clicking on the “Edit icon” under the operation column.
- Click on the “Edit icon” under the Operation column to configure a group.
- Select the Rate Limit Type to determine if the limit will be by packet or byte.
- Specify the Burst Packet/Byte, which sets the maximum number of packets or bytes allowed to be sent in a burst.
- Set the Rate Threshold, which defines the maximum rate of packets or bytes per second.

IP Source Guard
IP source guard is a source IP address filtering technology based on the Layer 2 interface. It can prevent malicious hosts from forging IP addresses of legitimate hosts to impersonate legitimate hosts, and also ensure that unauthorized hosts cannot access by specifying their IP addresses. network or attack the network. IPSG uses the binding table (source IP address, source MAC address, VLAN to which it belongs, and the binding of the inbound interface ) to match and check the IP packets received on the Layer 2 interface. Only the packets matching the binding table are allowed to pass through.
To enable IP Source Guard, first navigate to the Security → IP Source Guard page, then select the port and click on “Edit” to configure the port.

Then, select the Verification Type where either the verification will be based on IP addresses or both IP and MAC addresses. Max Entries limits the number of IP/MAC addresses (e.g. devices) where 0 indicates no limit.

This page displays the dynamic binding (port, IP, MAC, VLAN) generated when DHCP Snooping is enabled on the switches, also the user can add static binding by clicking on the “Add” button as shown below:
To import or export the list click on the import or export button respectively.

The binding requires specifying the port, IP Address and its mask, MAC address and its mask, and the VLAN ID. This information will be used to verify the traffic and make sure all the traffic is generated by legitimate users.
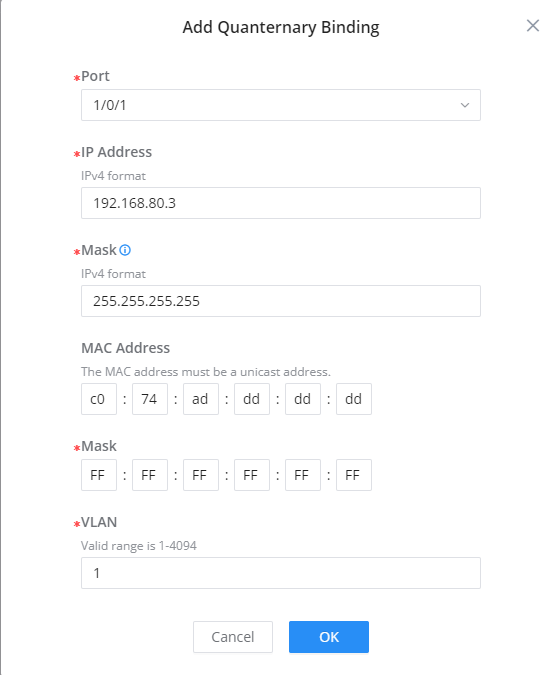
IPv6 Source Guard
IPv6 Source Guard is similar to IP Source Guard (based on IPv4), the only difference is that IPv6 Source Guard filters IPv6 addresses.

To enable IPv6 Source Guard on a port, select the port and click on the “Edit” button under the operation column, then select the Verification Type and specify the Max Entries.
On this tab, the user can see the list of binding both static and dynamic (DHCP Snooping must enabled).
To add a static entry, click on the “Add” button, it’s also possible to import or export the list as shown below:

Specify the binding (port, IP address, MAC Address, and VLAN), then click on the “OK” button to save.
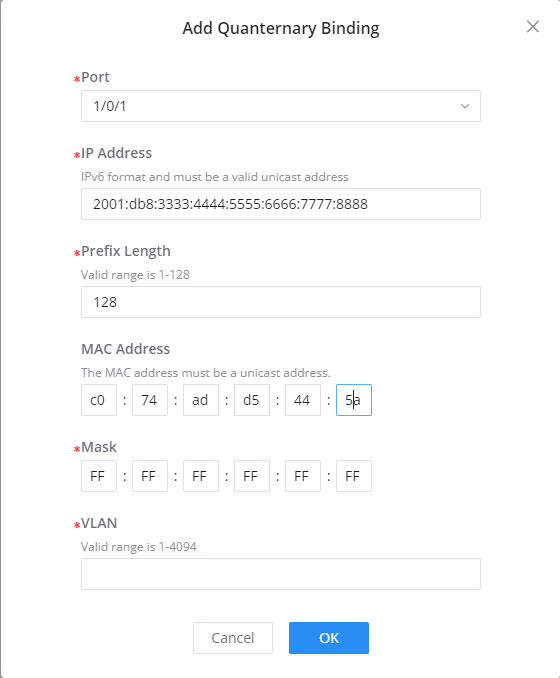
Anti Attack
| Field or action | Description |
|---|---|
| Attack checks | TCP Attack: TCP SYN-RST, SYN-FIN, X-Mass Scan, SYN Nonack Sport, Null Scan, TCP Fragment, and TCP Min Hdr. Other checks include Land, SMAC=DMAC, ICMP Ping for IPv4 and IPv6, IPv4 Ping of Death, ICMP Fragment, and IPv6 Min Fragment. |
| Minimum Fragment (Byte) | Displayed when IPv6 Min Fragment is enabled. Accepts 0 to 65535 bytes; default 1240. |
| Minimum Hdr (Byte) | Displayed when TCP Min Hdr is enabled. Accepts 0 to 31 bytes; default 20. |
In the network, there are a large number of malicious attack packets targeting the CPU and various types of packets that need to be normally sent to the CPU. Malicious attack packets targeting the CPU will cause the CPU to be busy processing attack packets for a long time, thereby causing interruption of other services or even system interruption; a large number of normal packets will also lead to high CPU usage and performance degradation, thus affecting the normal business.
In order to protect the CPU and ensure that the CPU can process and respond to normal services, the switch provides a local attack defense function, which is aimed at the packets sent to the CPU. It operates normally to avoid the mutual influence of various services when the device is attacked.
Attack defense is an important network security feature. It analyzes the content and behavior of the packets sent to the CPU for processing, determines whether the packets have attack characteristics, and configures certain preventive measures against the packets with attack characteristics. Defense attacks are mainly divided into malformed packet attack defense, fragmented packet attack defense, and flood attack defense.

Dynamic ARP Inspection (DAI)
To defend against man-in-the-middle attacks and prevent data of legitimate users from being stolen by the man-in-the-middle, you can enable dynamic ARP inspection. The device compares the source IP, source MAC, interface, and VLAN information corresponding to the ARP packet with the information in the binding table. If the information matches, it means that the user who sent the ARP packet is legitimate, and the user is allowed. If the ARP packet passes, otherwise it is considered an attack and the ARP packet is discarded.
Dynamic ARP inspection can be enabled in the interface view, or VLAN view. When enabled in the interface view, the binding table matching check is performed on all ARP packets received by the interface; when enabled in the VLAN view. Then, the binding table matching check is performed on the ARP packets belonging to the VLAN received by the interface that joins the VLAN.
When the device discards a large number of ARP packets that do not match the binding table, if you want the device to alert the network administrator in the form of an alarm, you can enable the dynamic ARP inspection discarded packet alarm function. When the number of discarded ARP packets exceeds the alarm threshold, the device generates an alarm.
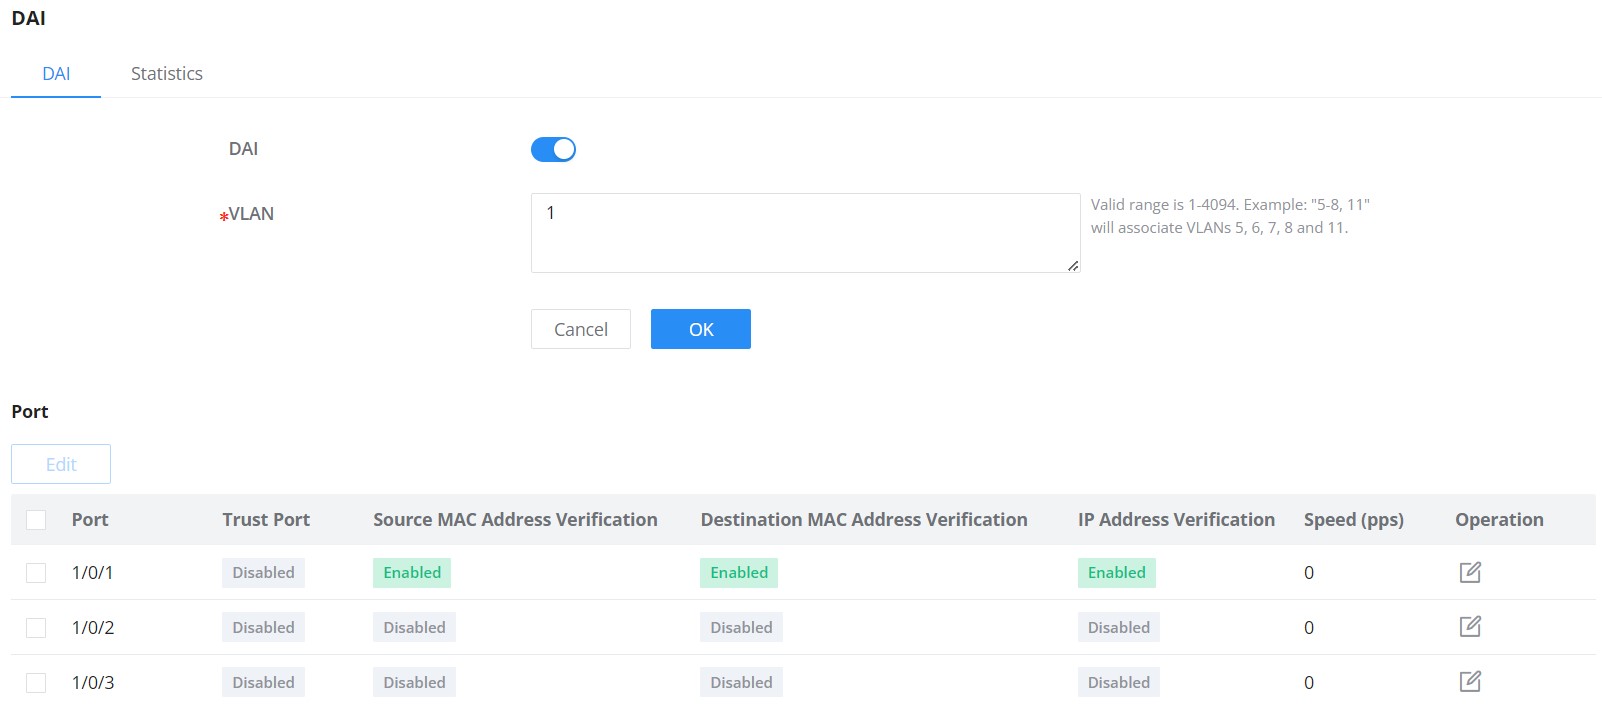
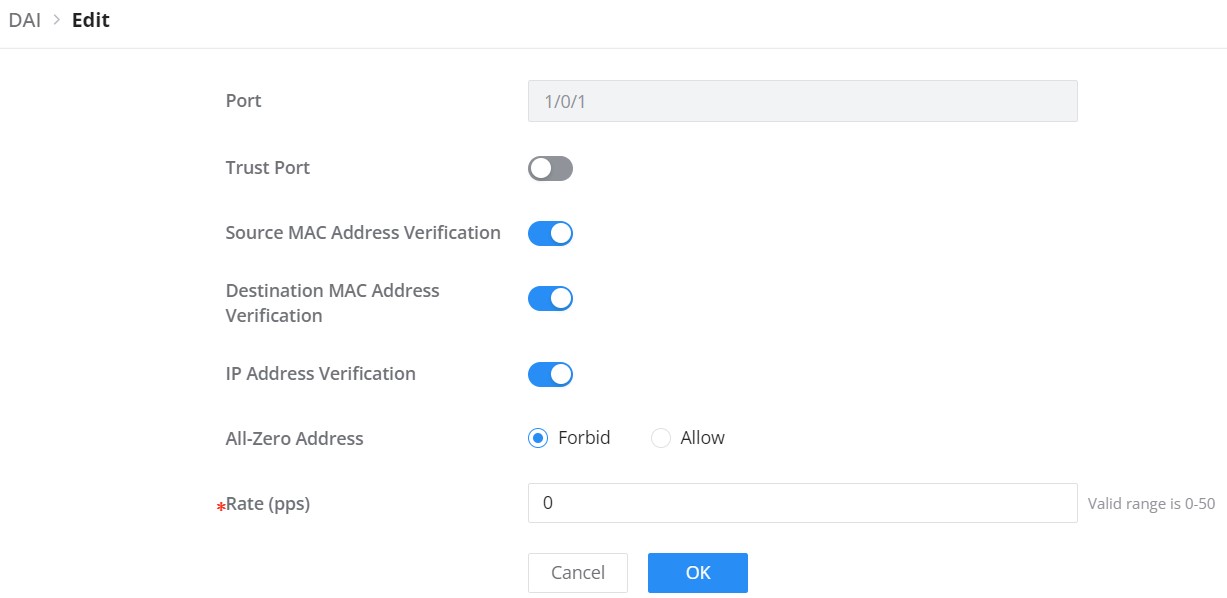
The statistics about DAI activities will be listed here for each port GE/LAG with the options of refreshing the statistics or clearing specified port data.
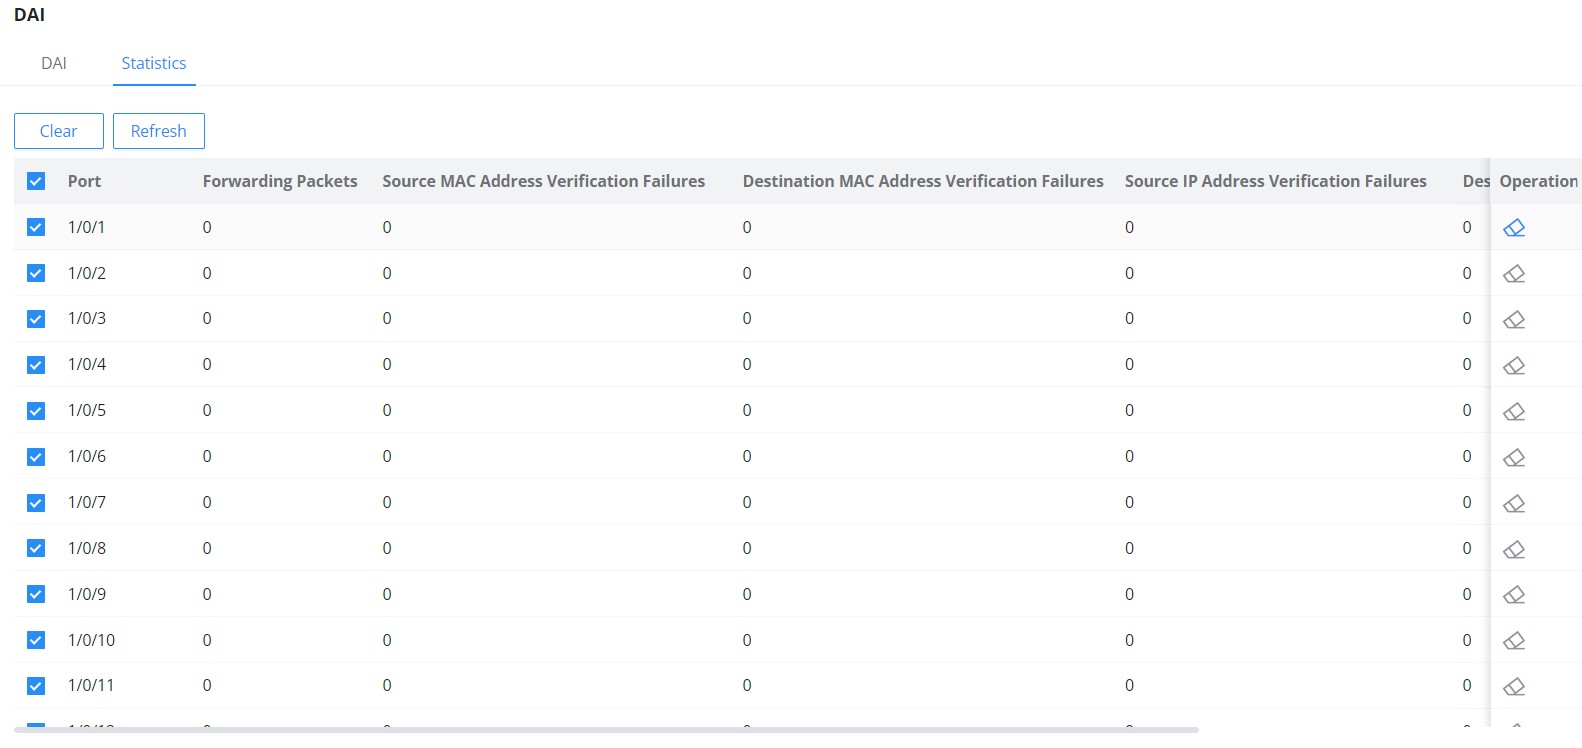
RADIUS
RADIUS is a distributed, client /server information exchange protocol that can protect the network from unauthorized access. It is often used in various network environments that require high security and allow remote users to access it. This protocol defines the UDP-based RADIUS packet format and its transmission mechanism and specifies destination UDP ports 1812 and 1813 as the default authentication and accounting port numbers, respectively.
Radius provides access services through authentication and authorization and collects and records the use of network resources by users through accounting. The main features of RADIUS protocol are client/server mode, secure message exchange mechanism, and good expansibility.
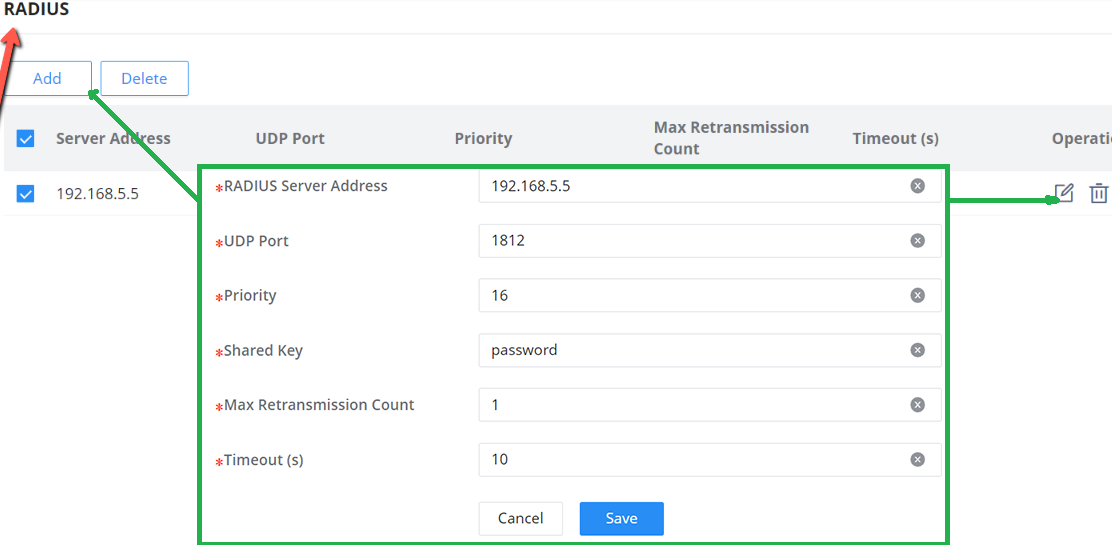
TACACS+
TACACS+ (Terminal Access Controller Control System Protocol) is a security protocol with enhanced functions based on the TACACS protocol. This protocol is similar in function to the RADIUS protocol and uses the client/server mode to implement the communication between the NAS and the TACACS+ server.
TACACS+ is a centralized, client /server structure information exchange protocol, which uses TCP protocol for transmission, and the TCP port number is 49. The authentication, authorization, and accounting servers provided by TACACS+ are independent of each other and can be implemented on different servers. It is mainly used for authentication, authorization, and accounting of access users who access the Internet through point-to-point protocol PPP or virtual private dial-up network VPDN and management users who perform operations.
TACACS+ is similar to RADIUS protocol : ( 1 ) both adopt client /server mode in structure; (2) both use shared keys to encrypt the transmitted user information ; ( 3 ) both have better flexibility and expansibility. TACACS+ has more reliable transmission and encryption characteristics and is more suitable for security control.
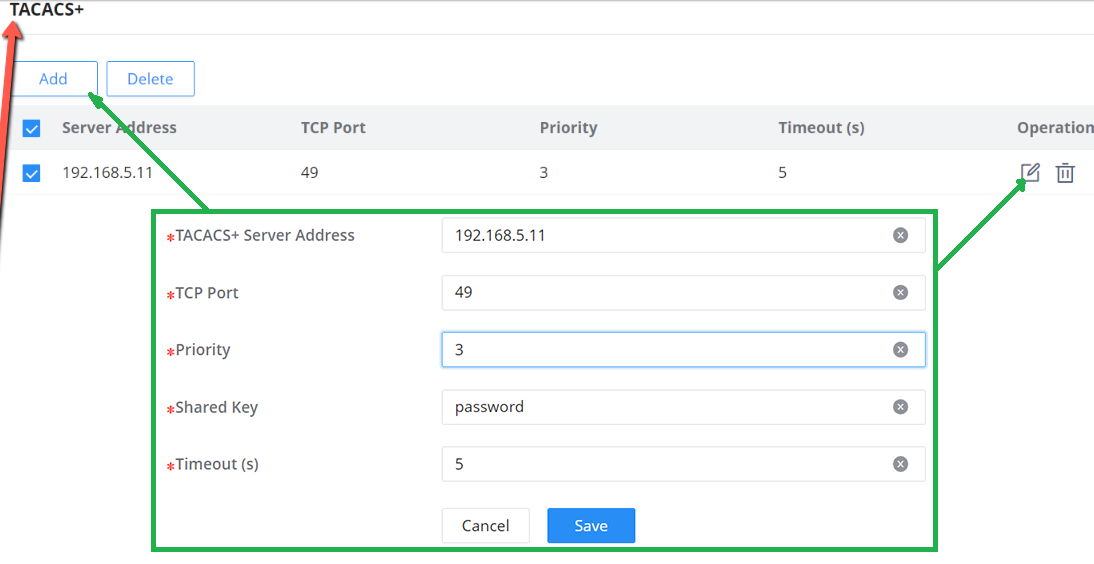
AAA
Access control is used to control which users can access the network and which network resources can be accessed. AAA is short for Authentication, Authorization, and Accounting, and provides a management framework for configuring access control on NAS ( Network Access Server) devices.
As a management mechanism of network security, AAA provides services in a modular manner:
- Authentication , confirming the identity of users accessing the network , and judging whether the visitor is a legitimate network user;
- Authorization , giving different users Different permissions limit the services that the user can use;
- Billing , record all operations during the user’s use of network services, including the type of service used, start time, data flow, etc., to collect and record the user’s The usage of network resources, and can realize the charging requirements for events and traffic, and also monitor the network.
AAA adopts a client /server structure. The AAA client runs on the access device, usually referred to as a NAS device, and is responsible for verifying user identity and managing user access; the AAA server is a collective name for the authentication server, authorization server, and accounting server. Responsible for centralized management of user information. AAA can be implemented through a variety of protocols. Currently, devices support AAA based on RADIUS or TACACS + protocol. In practical applications, the RADIUS protocol is most commonly used.

To add a method click on the “Add” button and to modify a method click on the “Modify“ icon as shown above:

Method | Description | Applicability |
None | No authentication is performed. Users can log in without a username or password. This setting should generally be avoided due to security risks. | Console, Telnet, SSH, Web UI |
Local | Uses the local user database on the switch for authentication. User credentials are stored directly on the switch. | Console, Telnet, SSH, Web UI |
Enable | Requires users to enter an enable password to gain elevated privileges (admin access). This provides an additional layer of security after initial authentication. Note: The password for user mode to enter privileged mode must be set using CLI. | Console, Telnet, SSH |
RADIUS | Utilizes a RADIUS server for authentication. RADIUS (Remote Authentication Dial-In User Service) is used for centralized Authentication, Authorization, and Accounting management. | Console, Telnet, SSH, Web UI |
TACACS+ | Utilizes a TACACS+ server for authentication. TACACS+ (Terminal Access Controller Access-Control System Plus) offers more granular control over authorization and is used for centralized AAA management. | Console, Telnet, SSH, Web UI |
AAA Methods
Identity Authentication Management
The Identity Authentication Management feature on Grandstream GWN switches provides a robust method for securing network access through 802.1X and MAC-based authentication. It allows administrators to configure and manage user authentication settings, ensuring only authorized devices can connect to the network, thereby enhancing overall network security and control.
The 802.1X protocol is a port-based network access control protocol. Port-based network access control refers to verifying user identities and controlling their access rights at the port level of LAN access devices. The 802.1X protocol is a Layer 2 protocol and does not need to reach Layer 3. It does not require high overall performance of the access device, which can effectively reduce network construction costs. Authentication packets and data packets are separated by logical interfaces to improve security.
Port Mode
To enable 802.1x and MAC authentication, please navigate to Security → Identity Authentication Management, then Toggle on “802.1X Authentication” and “MAC Authentication“, and click on the “OK” button to save.
| Field or action | Description |
|---|---|
| Authentication Type / Method | Selects the authentication type and method applied to the port. |
| User ID format of MAC-based | Displayed when MAC Authentication is enabled. It controls the MAC-address format used as the authentication user ID; the observed format was XXXXXXXXXXXX. |
| Authentication Sessions | The session list includes Session ID, Port, and MAC Address. |
| AAA methods | AAA method lists expose Method 1 through Method 4. |
On this page also, you can specify a user ID format for MAC-based and enable a Guest VLAN. This ensures these devices remain isolated from the main network while still maintaining limited network connectivity through the Guest VLAN. The Guest VLAN ID directs unauthenticated users to a designated network segment, providing controlled and secure access.

To enable it on a port, select port(s) from the list then click on “Edit” button or click on “Edit icon” on the right side under operation column.
Note: a RADIUS server must first be added under Security → RADIUS.

Port | The specific port being configured. This field shows the port number (e.g. |
User Authentication Mode | The mode of user authentication to be used on this port. Options include: MAC-Based |
Guest VLAN | Enables or disables the Guest VLAN for this port. If enabled |
Authorized VLAN | Specifies the VLAN ID that authenticated users will be assigned to. This ensures that authorized devices are placed in the correct network segment. |
Authentication Methods(x) Note: click on “Add+” to add another method. | |
Authentication Method1 | Select the authentication method, two options:
|
Method | • If MAC Authentication is selected, the user can add two methods: Radius and Local. • If 802.1x is selected, the user can only select radius. Note: When Radius is selected, the switch includes the Calling-Station-Id attribute in the Access-Request message, containing the MAC address of the connected device. This allows RADIUS servers to apply identity-based policies and track client devices using their hardware address. |
Port Mode – Edit port
Port
On this tab, the users can enable on which ports the authentication will take effect, select the port(s) and then click on “Edit” button or icon to configure the port(s) as shown below:

To enable the authentication on the port(s), under Port Control (Disable, Force authentication, Force unauthentication, Auto) select Auto or Force authentication and then save the configuration.

Example of 802.1X configuration on GXV3480 IP Video phone.
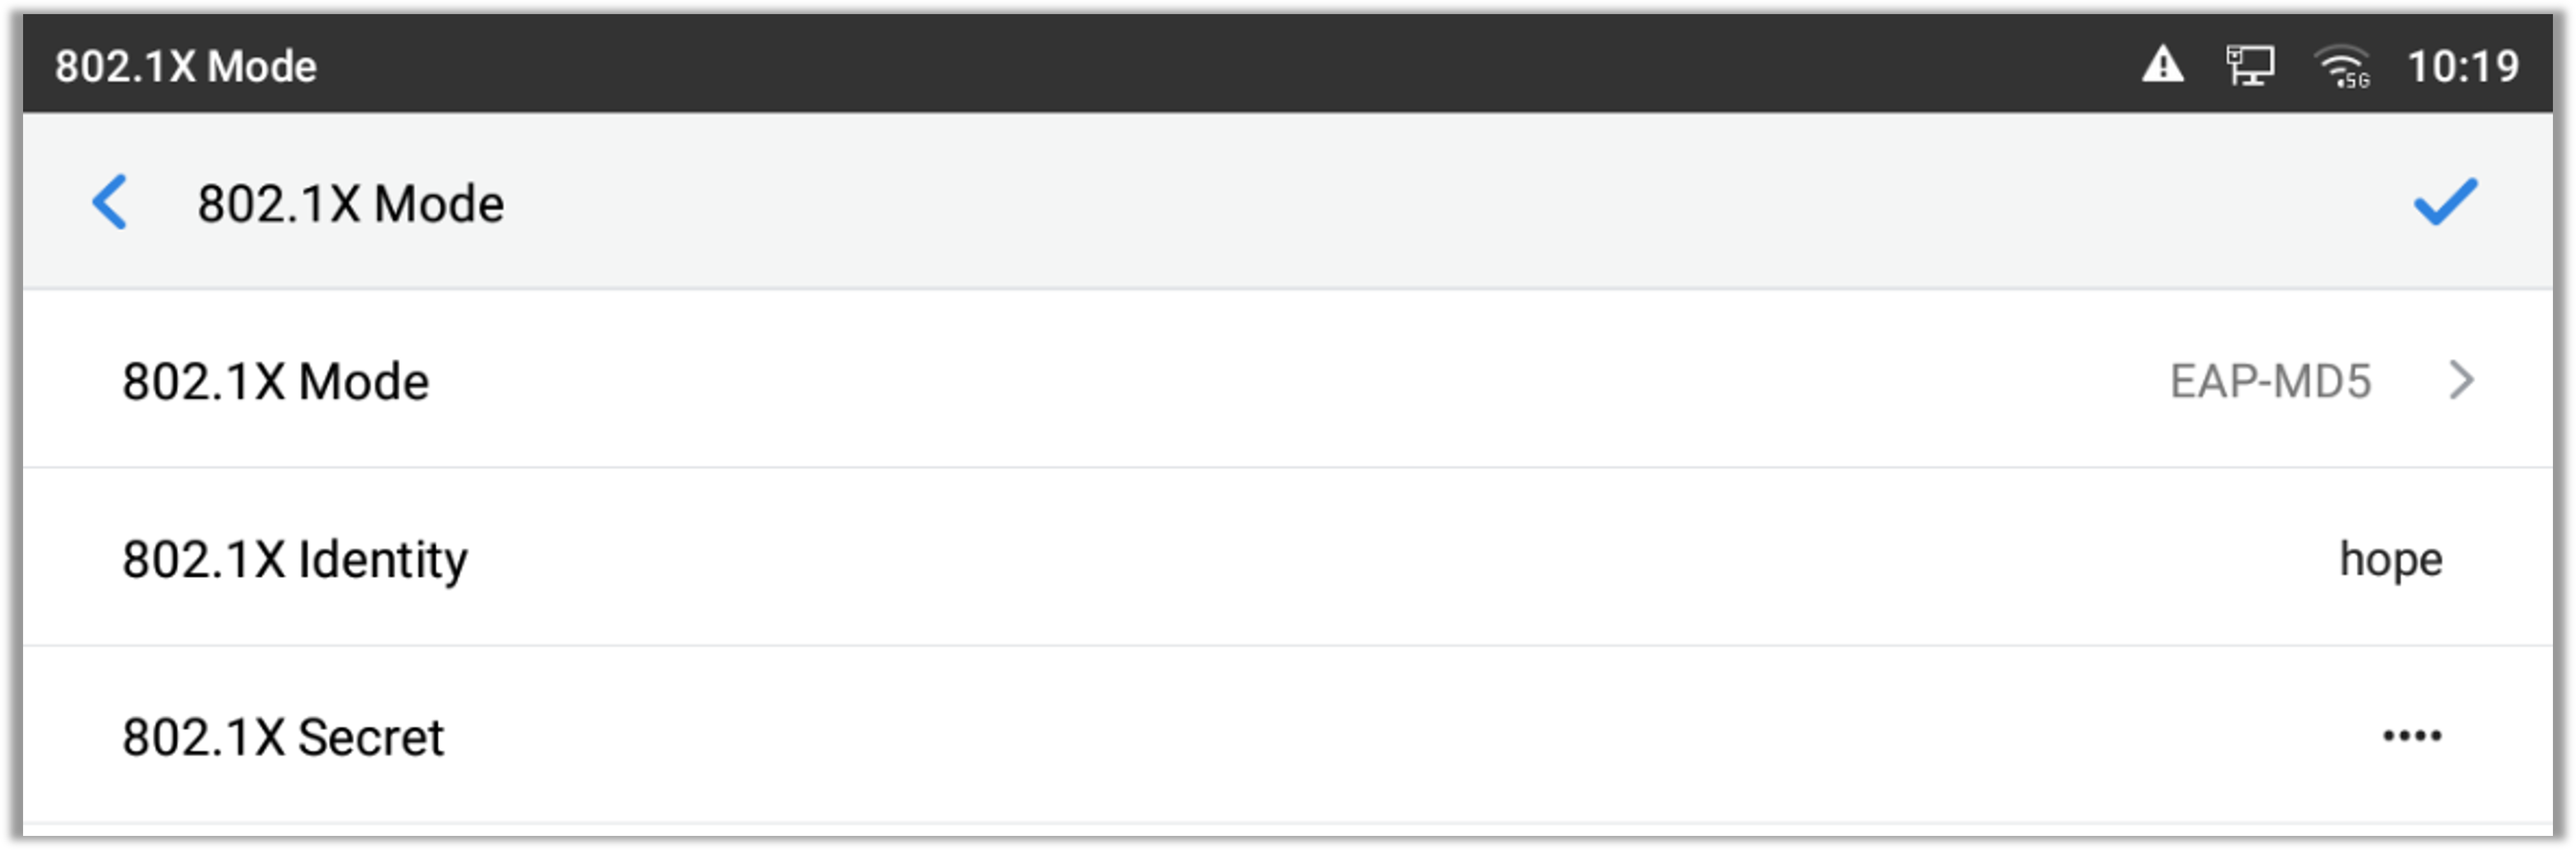
Authentication Sessions
On this tab, the authenticated devices will be listed here with more details. Please refer to the figures below:

There are three status (Authorized, Locked, Guest):

Local User of MAC-based
The “Local User of MAC-based” feature in Grandstream GWN switches provides a way to add and manage users based on their MAC addresses. This feature ensures that only devices with specified MAC addresses are granted network access, enhancing security and control over network resources.


MAC Address | The MAC address of the local user must be a unicast one. |
Port Control | • Force Authorized: Forces the port to authorize the device with the specified MAC address, allowing it access to the network. • Force Unauthorized: Forces the port to not authorize the device, preventing it from accessing the network. |
VLAN | Valid range is 1-4094. |
Reauthentication Time (s) | Valid range is 300-2147483647. |
Inactive Time (s) | Valid range is 60-65535. |
Add local User of MAC-based
DHCP Snooping
DHCP snooping ensures that DHCP clients obtain IP addresses from legitimate DHCP servers, and records the correspondence between IP addresses and MAC addresses of DHCP clients to prevent DHCP attacks on the network.
In order to ensure the security of network communication services, the DHCP Snooping technology is introduced, and a firewall is established between the DHCP Client and the DHCP Server to defend against various attacks against DHCP in the network.
When the device reboots, the dynamic binding table for the IP source guard is automatically restored.
Note: Associated with the “Entries Fixed for DHCPv6 Snooping” option of DHCPv6 Snooping.
Users can configure fixed entries for DHCP Snooping, ensuring that when the device reboots, the dynamic binding table for IP source guard is automatically restored after a fixed duration defined in seconds. Note that this is linked to the ‘Entries Fixed for DHCPv6 Snooping’ option in DHCPv6 Snooping.
Enable Entries Fixed for DHCP Snooping to preserve eligible learned bindings for restoration after reboot. When enabled, Fixed Duration (s) accepts 15 to 86400 seconds and defaults to 300 seconds.
To enable the DHCP Snooping feature on the switch, navigate to Security → DHCP Snooping, then enable DHCP Snooping, to make the DHCP snooping enabled on a VLAN, specify the VLANs or a VLAN range for example 5-8 means VLANs from 5 to 8, click “OK” button to save. Please refer to the figure below:
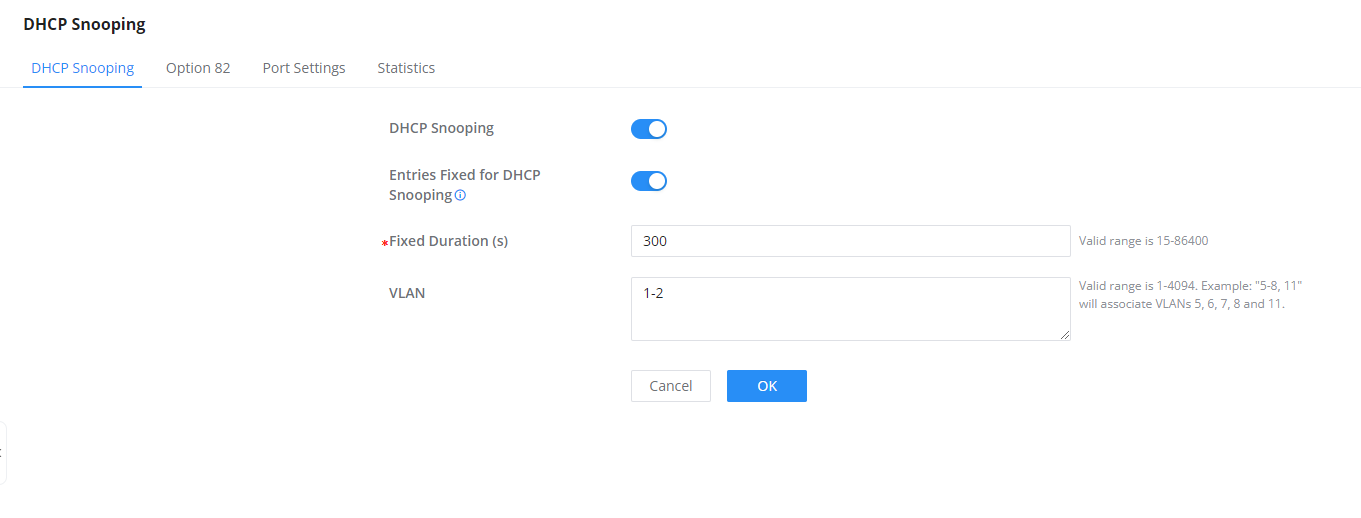
DHCP Snooping Option 82
Option 82 is called the relay agent information option and is inserted by the DHCP relay agent when forwarding client-originated DHCP packets to a DHCP server.
To identify the device accessed by the client, the user specifies the Remote ID, the format can be either Normal (standard) or Private:
- Normal Format: is generally used when interoperability with equipment from other vendors is required. By default, the switch’s MAC address is used, but a custom value containing 1 to 63 characters can be configured.
- Private Format: is specific to the vendor’s ecosystem and may not be compatible with other vendors’ equipment (check the vendor-specific format).
Option 82 is used to identify both the Circuit ID and Remote ID of the specific port, this can be used to identify the VLAN, interface, and other information where the client is located. To define this information, go to DHCP Snooping → Option 82, choose a specific port:
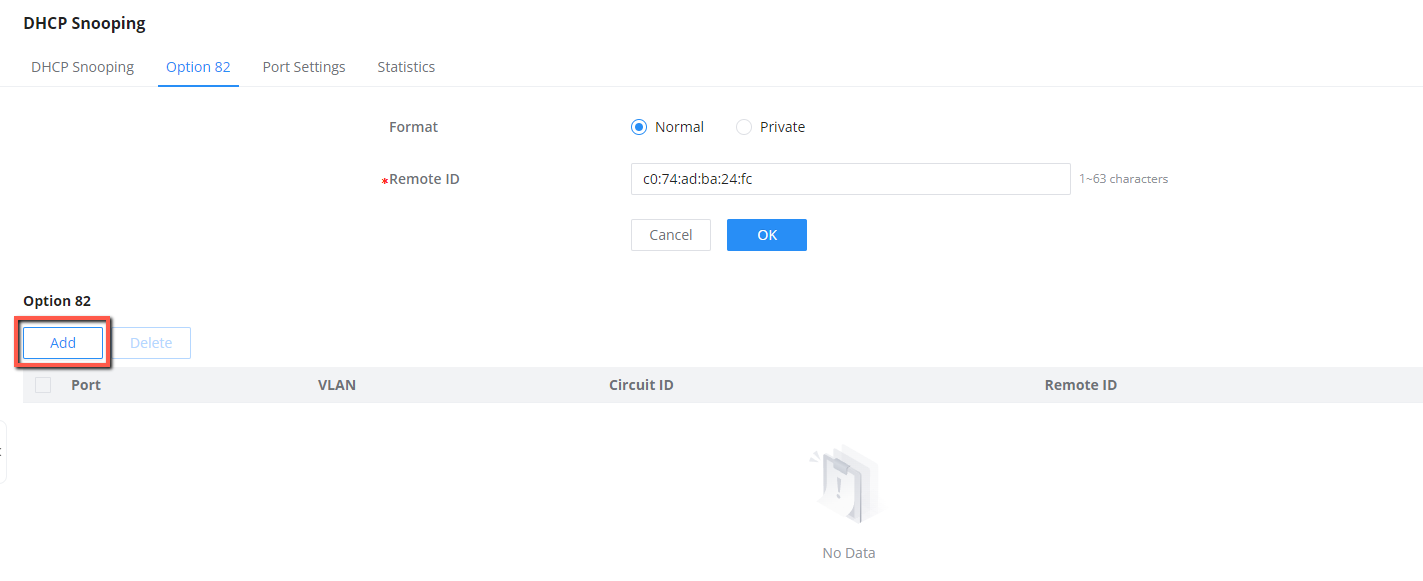
Then, select a port, VLAN and Format, and specify the Circuit ID and Remote ID:
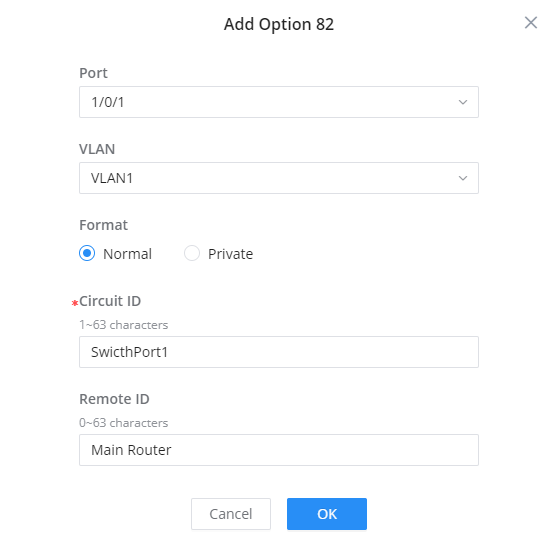
DHCP Snooping Port Settings
On this page, the user can configure the trusted port(s) that will allow DHCP messages, all other ports that are not trusted will discard the DHCP messages. This protects users from rogue DHCP servers that are plugged into untrusted ports.
To configure a port(s), either select the port(s) and click on the “Edit” button or click on the “Edit icon” under the operation column as seen below:

To make a port trusted, Toggle ON Trust Mode, more security parameters can be enabled too like Chaddr Verification, Rate (pps = packet per seconds) to limit the number of DHCP packets, and enable Option 82 for this port with three modes (keep, drop, replace). Please refer to the figure below:

DHCP Snooping Statistics
This page displays all statistics recorded by DHCP snooping function including Forwarding packets, Untrusted Port Drops, etc.
To clear the statistics, select the ports and click on “Clear” button as shown below:

DHCPv6 Snooping
DHCPv6 snooping is a security feature in IPv6 networks that safeguards against unauthorized DHCPv6 server messages and controls IPv6 address assignments, similar to how DHCPv4 snooping operates in IPv4 networks.
To enable the DHCPv6 Snooping feature on the switch, navigate to Security → DHCPv6 Snooping, then enable DHCPv6 Snooping, to make the DHCPv6 snooping enabled on a VLAN, specify the VLANs or a VLAN range for example 5-8 that means VLANs from 5 to 8, click “OK” button to save. Please refer to the figure below:
Enable Entries Fixed for DHCPv6 Snooping to preserve eligible learned bindings for restoration after reboot. When enabled, Fixed Duration (s) accepts 15 to 86400 seconds and defaults to 300 seconds. This behavior is associated with the corresponding DHCP Snooping setting.

DHCPv6 Snooping Option 18
On this page, the user can configure the Remote ID (Option 37), by default, the switch uses its own MAC address.
The DHCPv6 Relay-Option, encompassing Option 18 and Option 37, enables a DHCPv6 relay agent to embed circuit-specific and remote information as a TLV (type-length-value) within the relay message sent to the DHCPv6 server. In this scenario, the managed device functions as a DHCPv6 relay agent.
To add option 18 for a port, click on the “Add” button as shown below:

Then, select the port, Format (Standard, Extended), when the Standard format is selected then the user can select the VLAN and if the Extended Format is selected the user can interface ID (3~63 characters), click on “OK” to save.

DHCPv6 Snooping Port Settings
On this page, the user can configure the trusted port(s) that will allow DHCP messages, all other ports that are not trusted will discard the DHCP messages. This protects users from rogue DHCP servers that are plugged into untrusted ports.
To configure a port(s), either select the port(s) and click on the “Edit” button or click on the “Edit icon” under the operation column as seen below:

To make a port trusted, Toggle ON Trust Mode, more security parameters can be enabled too like Rate (pps = packet per seconds) to limit the number of DHCPv6 packets, and enable Option 18 and 37 for this port with three modes (keep, drop, replace). Please refer to the figure below:

DHCPv6 Snooping Statistics
This page displays all statistics recorded by DHCPv6 snooping function including Forwarding packets, Untrusted Port Drops, etc.
To clear the statistics, select the ports and click on “Clear” button as shown below:

MAINTENANCE
Upgrade
The switches support manual firmware upgrades using a BIN file downloaded from the Grandstream Firmware page: https://www.grandstream.com/support/firmware.
| Field or action | Description |
|---|---|
| Upload Firmware File to Update | Selects a local firmware BIN file for a manual upgrade. |
| Allow DHCP Option 43/160/66 to Override Server | Allows DHCP-provided provisioning information to override the configured server. |
| Firmware Upgrade Protocol | Selects the protocol used to retrieve firmware. |
| Check/Download New Firmware at Bootup | Checks for and downloads available firmware during startup when enabled. |
| Scheduled Upgrade | Runs a firmware upgrade according to the configured schedule. |
Upgrading via network is also possible using 5 of these protocols:
- TFTP
- HTTP
- HTTPS
- FTP
- Explicit FTPS
Once the protocol is selected, then the user needs to specify the firmware Server Path (For example: firmware.grandstream.com).
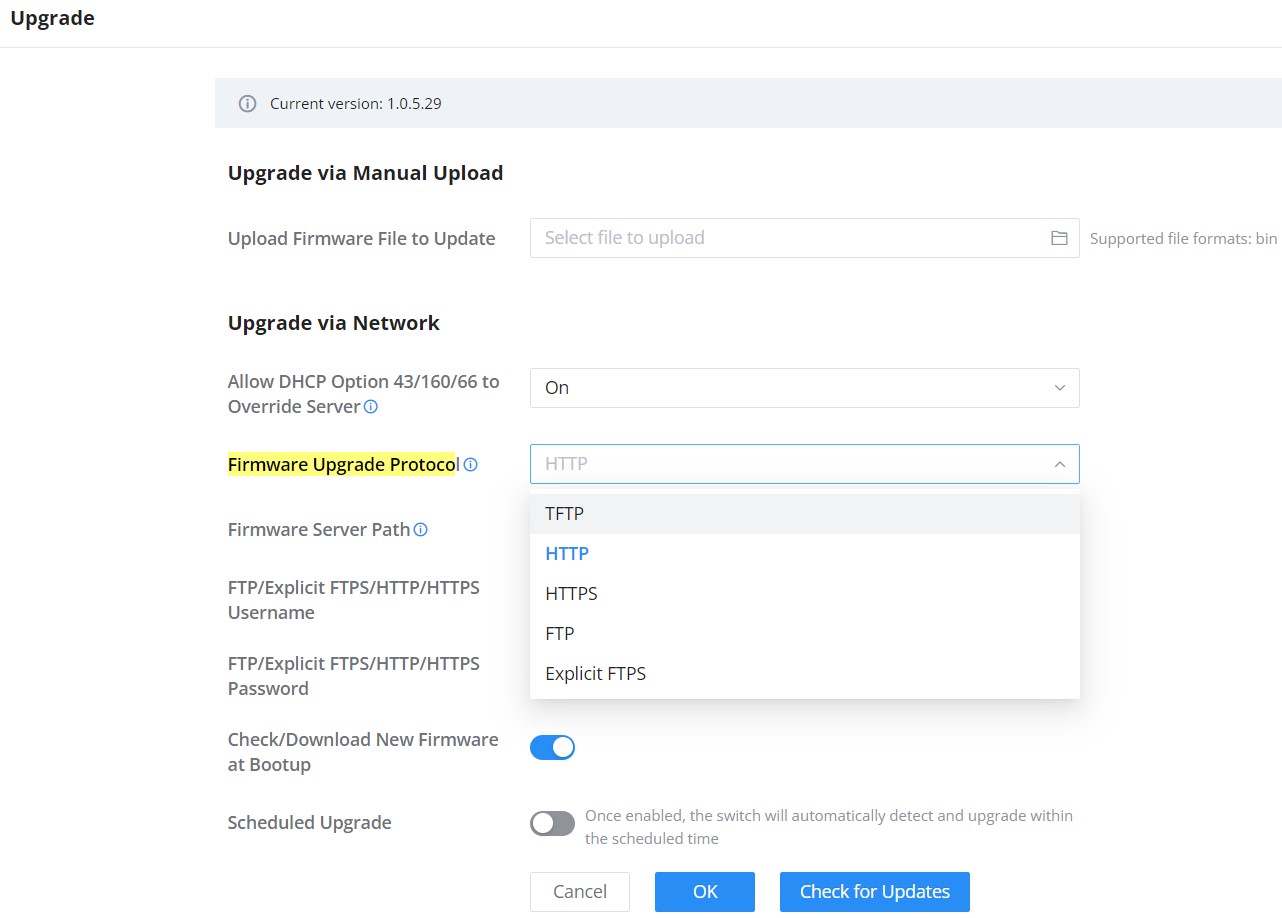
Diagnostics
The switches support many diagnostics tools that can help the user troubleshoot the issue and resolve it. These tools include Logs, Ping, Traceroute, Mirroring, Fiber Module, Copper Test, and One-Click Debugging.
Logs
This page lists all the generated Logs with details level and generated time, also an option to export the list is available.

Adding a Log Server Address to the logs to be sent to is also supported on these switches.
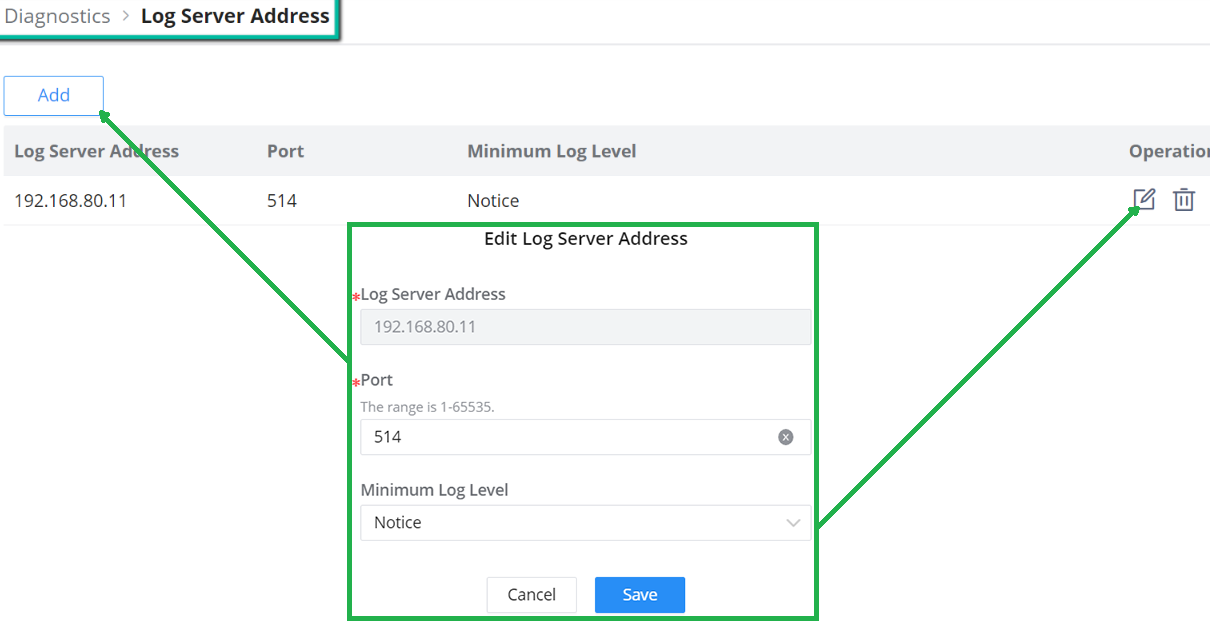
Users can Configure the following elements in the logs settings:
- Minimum log level: This defines the lowest severity of events that will be logged. “Debug” means all messages, including detailed diagnostic information, will be recorded. Other log levels (e.g., Info, Warning, Error) would filter out lower-priority messages.
- Log Aggregation: This option allows you to merge multiple logs from various sources or components into a centralized location for easier monitoring, analysis, and management.
- Timeout: This setting defines the time, in seconds, before the logging operation times out. In the example shown, the timeout is set to 60 seconds. The valid range for the timeout is between 15 and 3600 seconds.
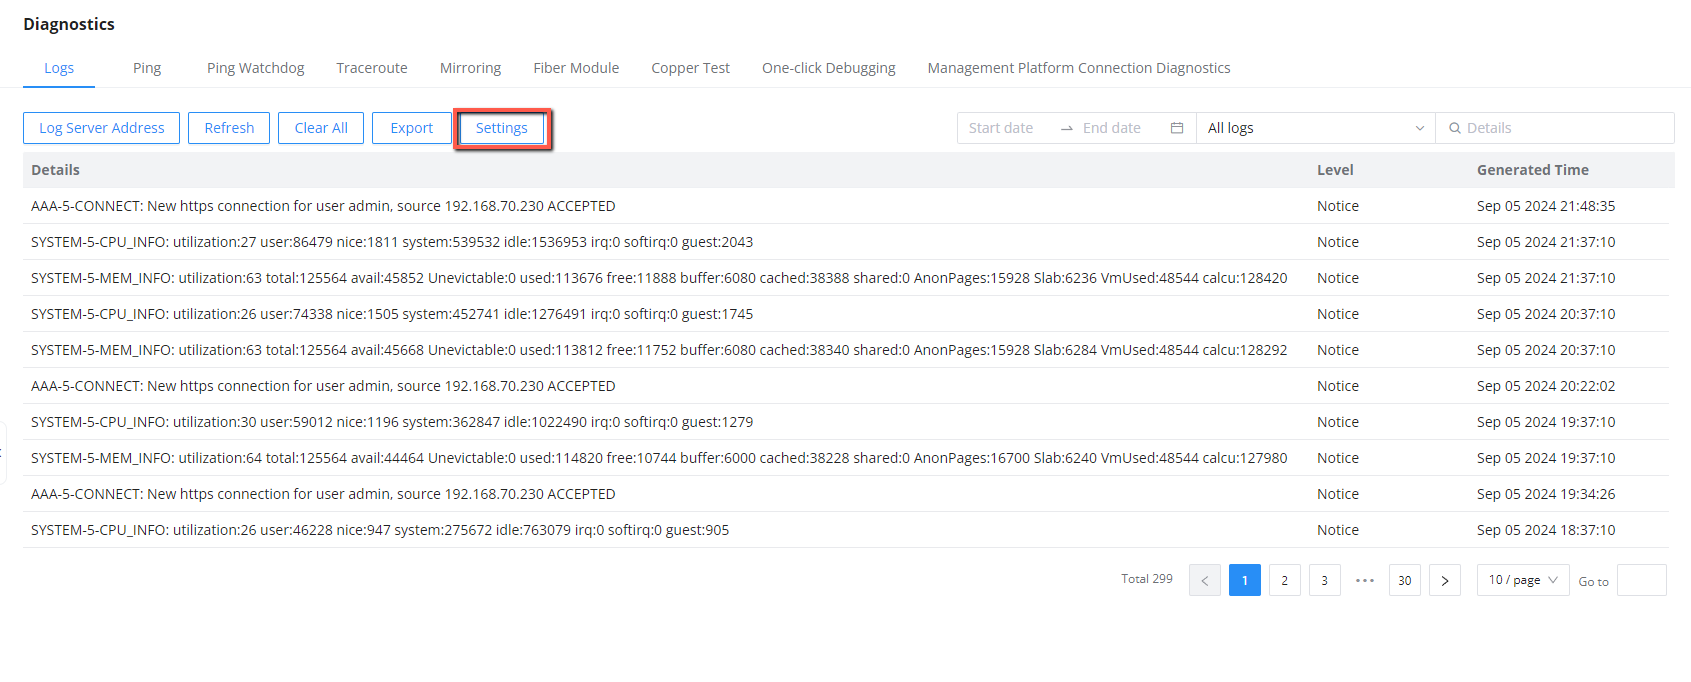
Ping
| Field or action | Description |
|---|---|
| IP Address/Hostname | Enter the destination IPv4 address or host name. |
| Packet Count | Accepts 1 to 65535 packets. |
| Packet Size | Accepts 0 to 65500 bytes. |
| VLAN Interface | Selects the source Layer 3 interface used for the test. |
| Start | Starts the ping test with the configured values. |
The user in this page can enter the IP Address or Hostname then click “Start“, the results of the ping command will be shown below.

Ping Watchdog
Ping Watchdog is a feature designed to monitor the connectivity of a device by continuously pinging a specified IP address. If the device becomes unresponsive to pings, then corrective actions can be triggered based on the configuration settings.
Port: Specifies the port on the device that will be monitored or managed by Ping Watchdog.
Enable: Toggles the Ping Watchdog feature on or off for the selected port.
IP Address: The target IP address to which the device will send ping requests.
Packet Sending Interval (s): Defines how frequently (in seconds) ping packets are sent to the specified IP address.
Delay Time (s): This sets a delay before the Ping Watchdog starts monitoring the device after it’s enabled or after a reboot.
Retry Times: Specifies how many failed ping attempts are allowed before the watchdog takes action.
Shutdown Interval (s): how long the switch keeps the port shutdown before bringing it back up after a Ping Watchdog failure.
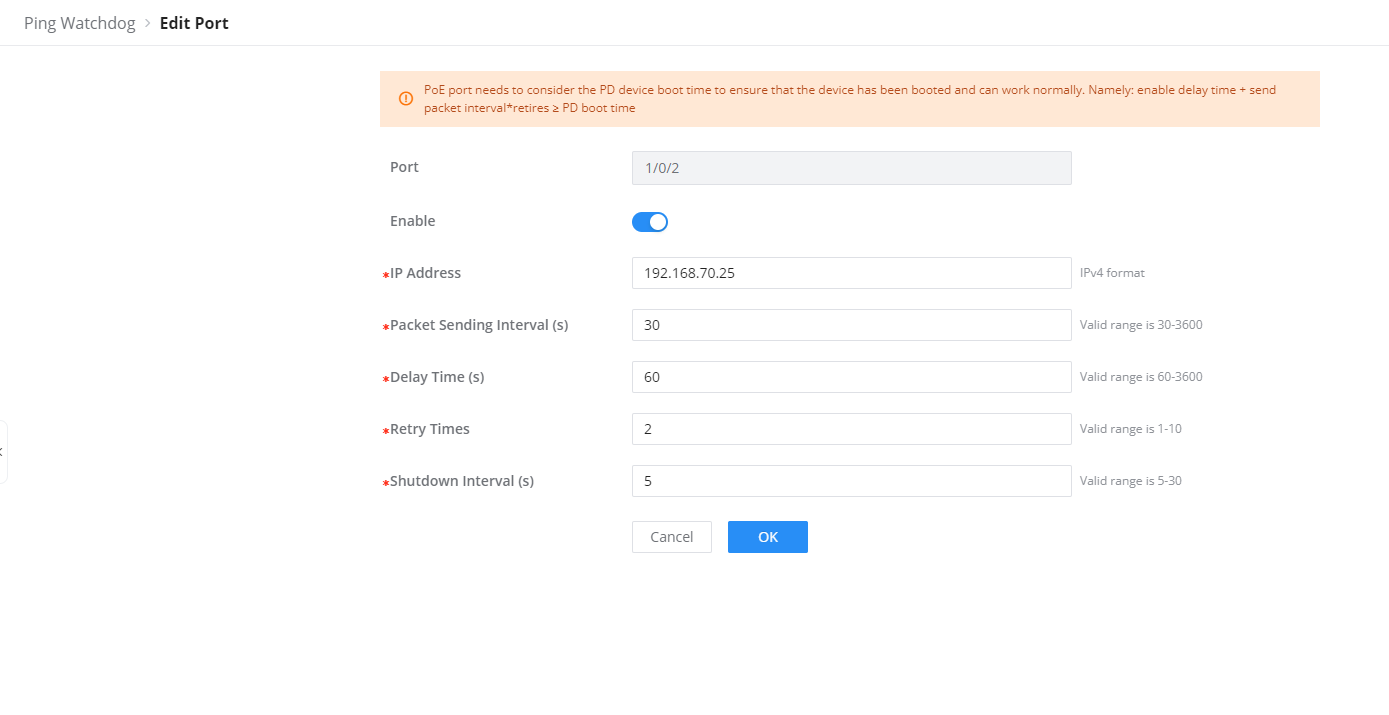
Traceroute
Another tool is Traceroute which shows the number of hops, and the switch allows the user to run traceroute commands directly from its web UI.
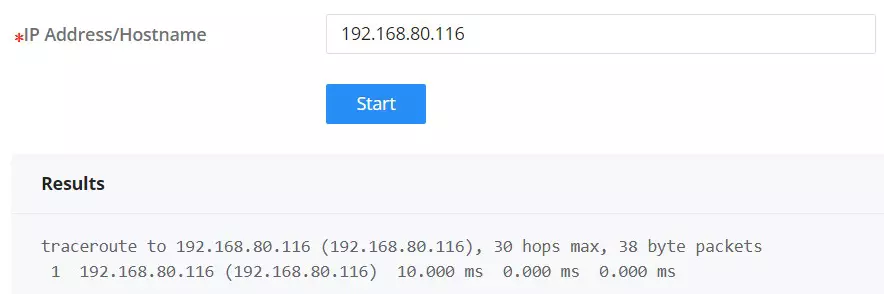
Mirroring
Mirroring refers to copying the packets from the specified source to the destination port. The specified source is called the mirroring source, the destination port is called the observing port, and the copied packet is called the mirroring packet.
Mirroring can make a copy of the original packet without affecting the normal processing of the original packet by the device, and send it to the monitoring device through the observation port to determine whether the service running on the network is normal.
The switches support two modes of Port Mirroring: SPAN and RSPAN:
- SPAN (Local): Traffic is mirrored locally within the same switch.
- RSPAN (Remote): Traffic is mirrored remotely across a network using a Remote VLAN.
SPAN
The traffic mirroring occurs locally within the same switch. SPAN allows you to capture traffic from one or more ports and send a copy of it to another port, typically connected to a network analyzer or monitoring tool.
- Ingress Mirroring: Captures incoming traffic on the source port(s).
- Egress Mirroring: Captures outgoing traffic from the source port(s).
- Source Port: Where the traffic originates (the port being monitored).
- Tx/Rx Regular Data Messages: defines what type of traffic (transmit, receive, or both) is monitored on the destination switch.
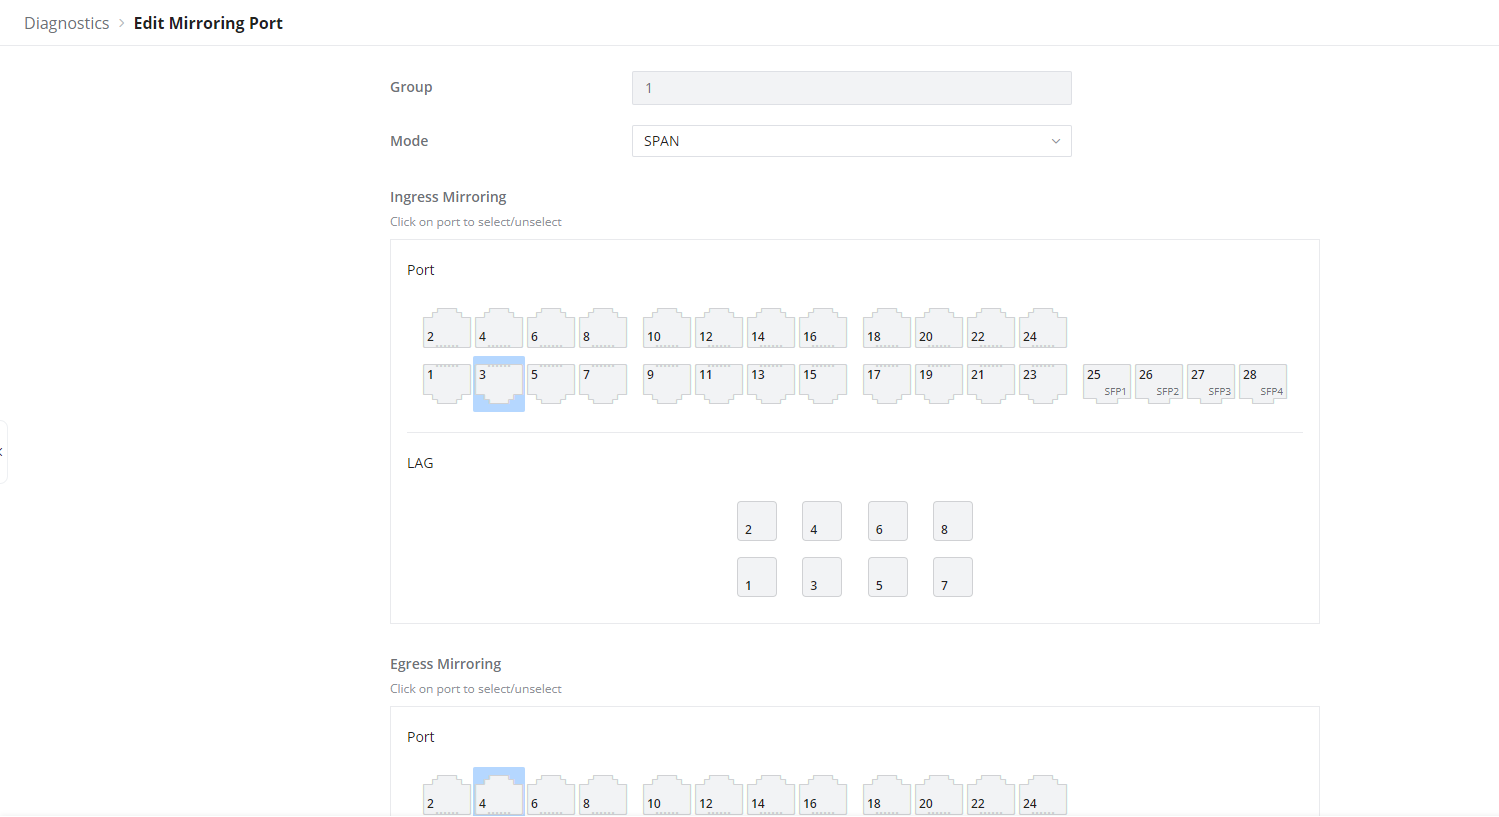
RSPAN
RSPAN (Remote Switched Port Analyzer) allows traffic to be mirrored from one switch to another over a network. Unlike SPAN, which is limited to mirroring traffic locally within the same switch, RSPAN uses a Remote VLAN to transport mirrored traffic across multiple switches, enabling centralized monitoring.
Source Switch Role (RSPAN)
- Ingress Mirroring: This captures incoming traffic on the specified source port(s). It mirrors the packets received by the port before they are processed by the switch, forwarding them to the designated destination for monitoring or analysis.
- Egress Mirroring: This captures outgoing traffic from the specified source port(s). It mirrors the packets leaving the port after the switch processes them, forwarding these packets to the monitoring destination.
- Output Port: This is the port on the source switch where the mirrored traffic is sent. In SPAN, it’s usually a local port that connects to the monitoring device, but in RSPAN, this traffic is forwarded across a network using the Remote VLAN to the destination switch.
- Remote VLAN: This is the VLAN used to transport mirrored traffic between the source switch and the destination switch in an RSPAN configuration. The source switch forwards mirrored traffic to this VLAN, which allows it to be sent across the network to the destination switch for analysis.
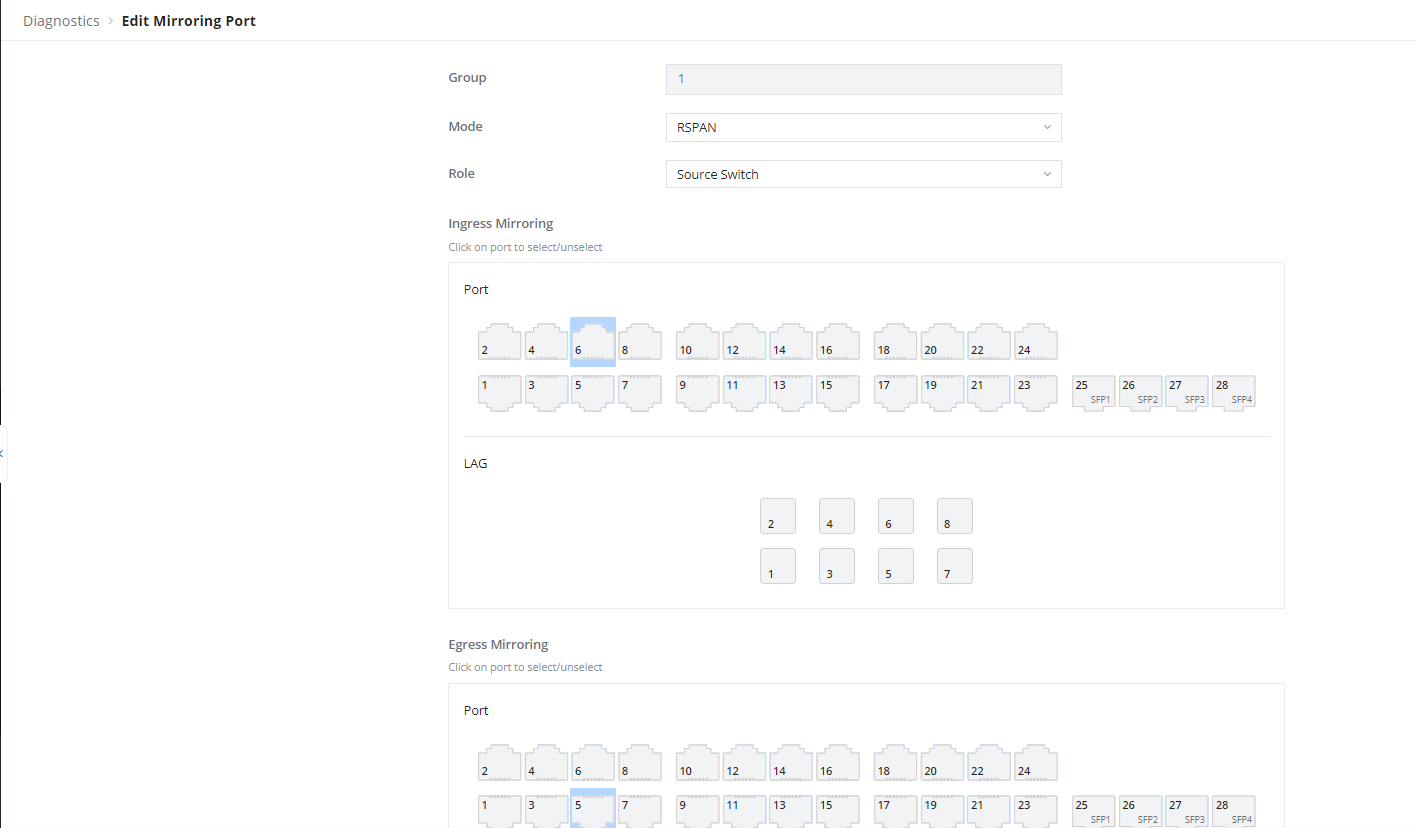
Destination Switch Role (RSPAN)
- Source Port: This is the remote VLAN where the mirrored traffic from the source switch arrives. The destination switch receives the mirrored packets via this VLAN and forwards them to the appropriate monitoring port.
- Monitor Port TX/RX: This defines what type of traffic (transmit, receive, or both) is monitored on the destination switch.
- Remote VLAN: The VLAN used to receive mirrored traffic from the source switch. It’s the same VLAN that the source switch uses to forward the mirrored traffic over the network to the destination switch.
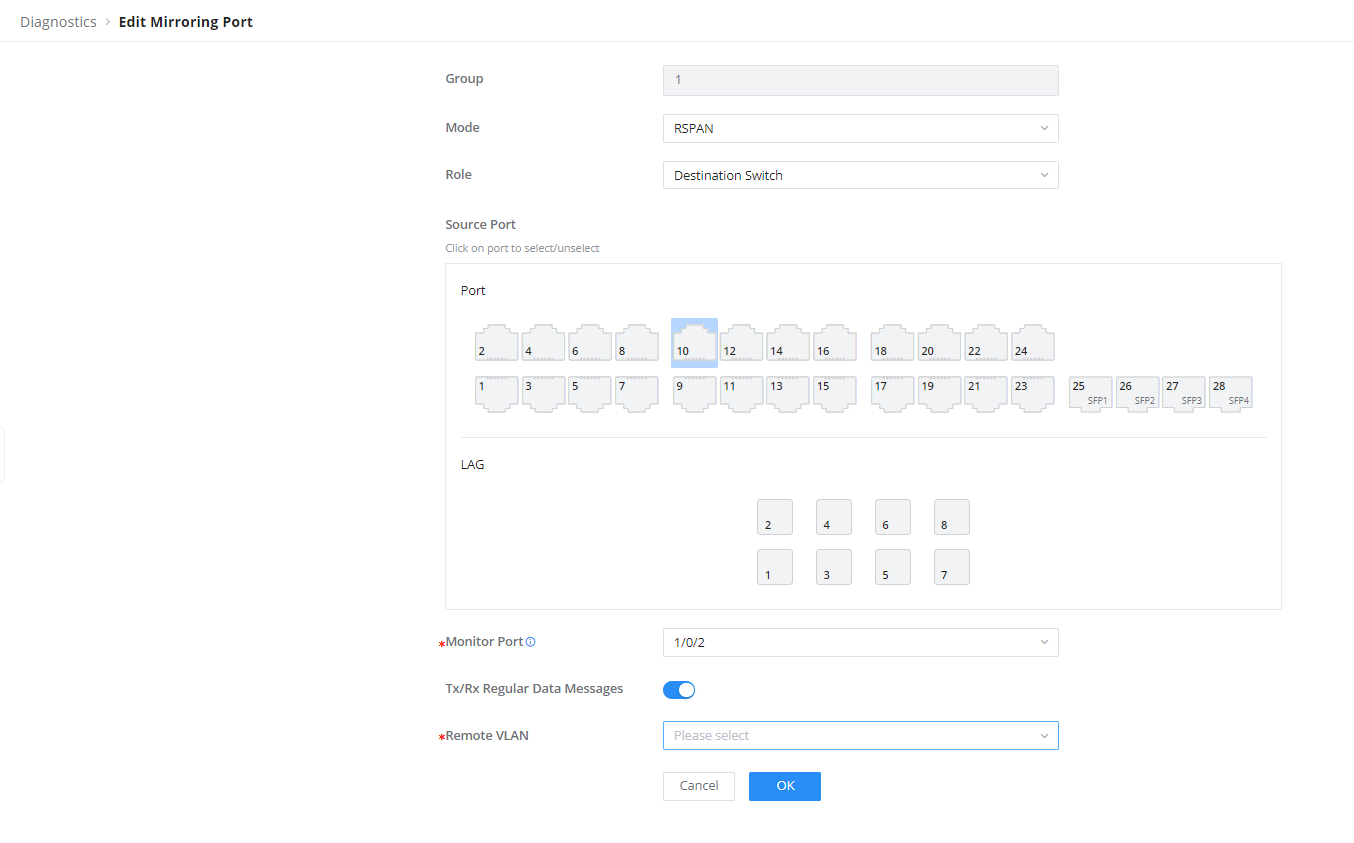
Fiber Module
This pages provides the user with the information about the fiber module for each Port that supports it. Select the port from the drop-down list and click refresh icon.
Note: The information displayed on the optical module of each manufacturer is different.

Copper Test
Copper test can detect whether the cable connected to the switch is faulty and the location of the fault. Using this function can assist in the daily engineering installation diagnosis .
Please navigate to Web UI → Maintenance → Diagnostics page → Copper Test Tab.
To perform the test simply click on the port, please refer to the figure below:

After the detection, the cable detection result is displayed as follows:
Cable Status: OK (normal), Open (open circuit), Short (short circuit ), Crosstalk (crosstalk), Unknown (unknown).
Cable Length:
- When there is a fault: it is the length from the port to the fault location.
- When there is no fault: it is the actual length of the cable.
One-click Debugging
The One-click Debugging feature can help administrators or technical support staff to quickly and easily get debugging information about the GWN switch in a matter of few minutes.
Please navigate to Web UI → Maintenance → Diagnostics page → One-click Debugging tab, then click on “Debug” button to start the debugging process.

It’s also possible to delete the generated file or download it locally to share it with tech-support for example. The folder contains many logs files and even a tech-support file that containing valuable information like the switch configuration etc.
Management Platform Connection Diagnostics
If the switch is added to the GDMS networking ,GWN Manager, or a GWN Router, it will display a Cloud icon with a green check mark (as shown in the figure below) indicating it’s added to a GDMS Networking account, GWN Manage, or to a GWN Router.
In case there is an issue with the connection, then the user can navigate to Maintenance → System Diagnosis → Cloud/Manager Connection Diagnostics and then click on “Detection” or “Redetection” button to see in what stage/step the connection has failed. Refer to the figure below:
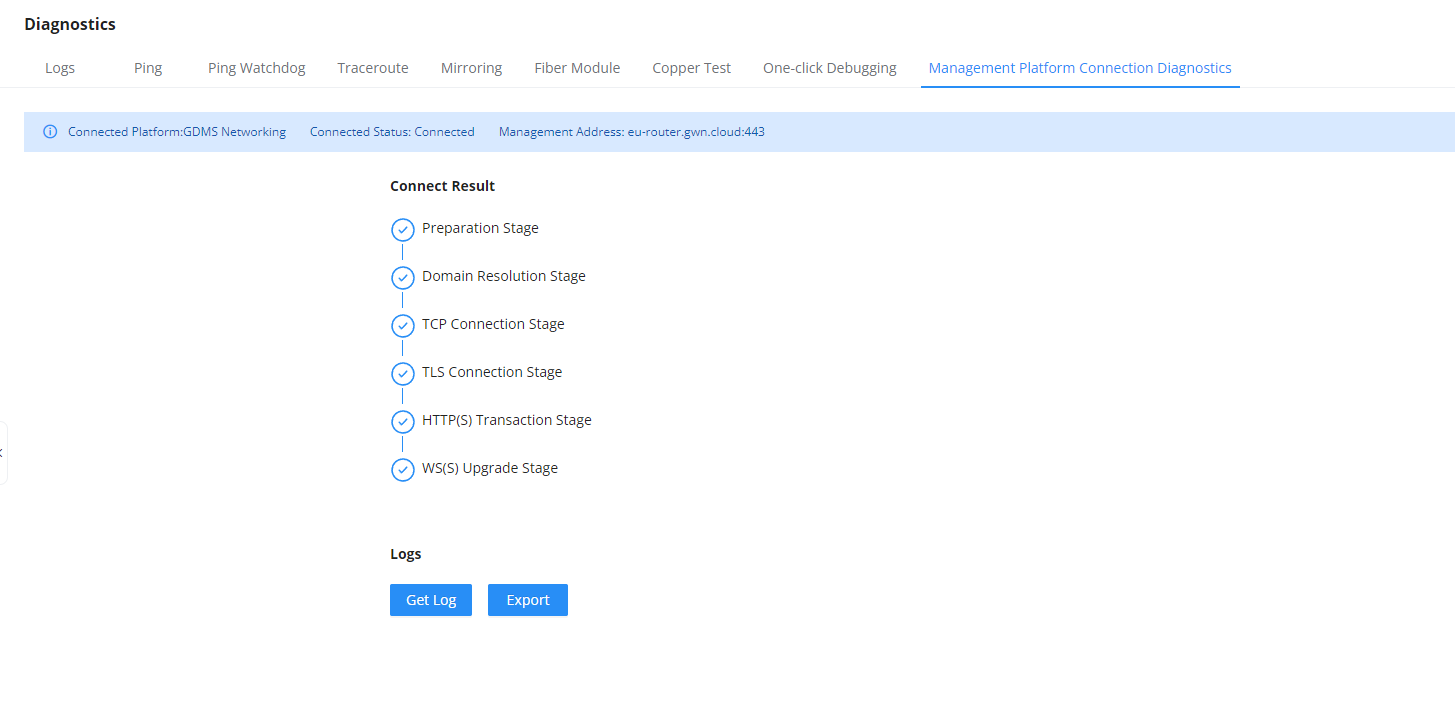
Backup and Restore
Click on “Factory Reset” button to reset the switch back to default settings, or restore to previously saved backup by uploading a configuration file, these configuration files can be used as a way to back up the device running configuration or saved configuration.
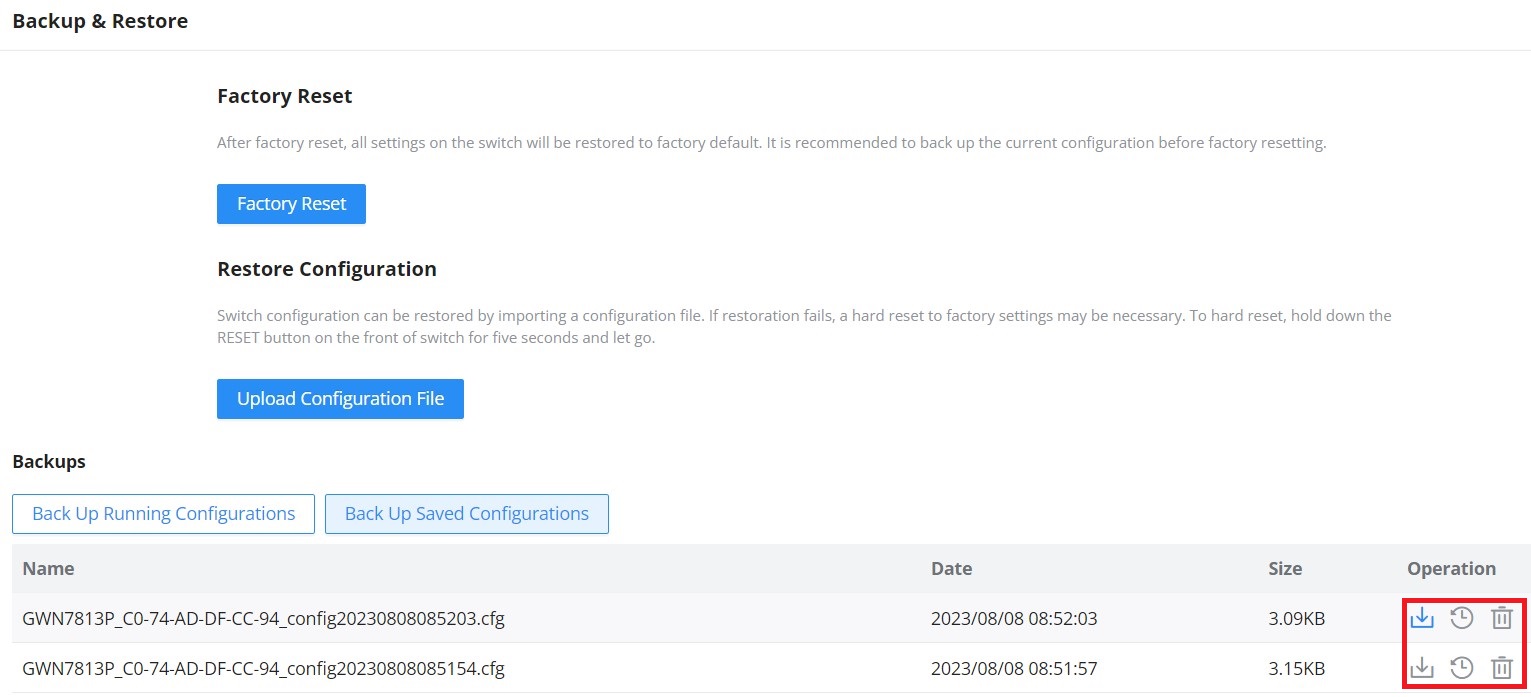
SNMP
Network Management Protocol (SNMP) is an “Internet-standard protocol for managing devices on IP networks”. Devices that typically support SNMP include routers, switches, servers, workstations, printers, modem racks and more. SNMP is used mostly in network management systems to monitor network-attached devices for conditions that warrant administrative attention. SNMP is a component of the Internet Protocol Suite as defined by the Internet Engineering Task Force (IETF). It consists of a set of standards for network management, including an application layer protocol, a database schema, and a set of data objects. An SNMP-managed network consists of three key components:
- Managed device
- Agent – software which runs on managed devices
- Network management station (NMS) – software which runs on the manager
A managed device is a network node that implements an SNMP interface that allows unidirectional (read-only) or bidirectional (read and write) access to node-specific information. Managed devices exchange node-specific information with the NMSs. Sometimes called network elements, the managed devices can be any type of device, including, but not limited to, routers, access servers, switches, bridges, hubs, IP telephones, IP video cameras, computer hosts, and printers. An agent is a network-management software module that resides on a managed device. An agent has local knowledge of management information and translates that information to or from an SNMP-specific form. A network management station (NMS) executes applications that monitor and control managed devices. NMSs provide the bulk of the processing and memory resources required for network management. One or more NMSs may exist on any managed network.
The global settings page allows the user to enable the SNMP function with the Local Engine ID or add a Remote Engine ID.
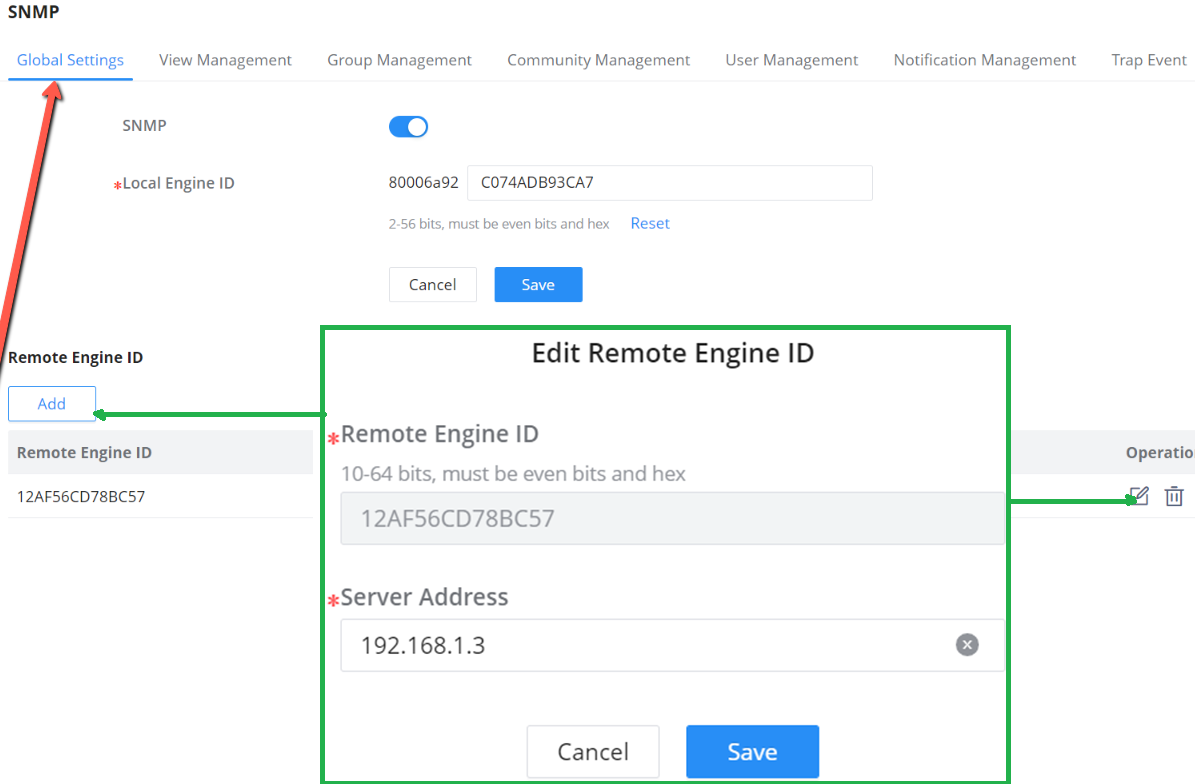
SNMP | Select whether to enable SNMP. |
Local Engine ID | Set the engine ID of the local SNMP entity or click “Reset” to restore to the initial value. Note: The default is 8000 A59Dxxxxxxxx, where xxxxxxxx is the device MAC address by default, which can be modified by the user . It is expressed in hexadecimal , and the length is limited between 2 and 56 characters. The number of characters must be an even number . |
Edit Remote Engine ID | |
Remote Engine ID | Set the engine ID of the SNMP management side , and the remote user is established under the remote engine. The input length is limited to 10-64 characters, expressed in hexadecimal , and the number of characters must be an even number. |
Server Address | Set the address of the network management station server, support input of Hostname and IP address (including IPv4 and IPv6), and need to meet the requirements of various types of address formats, otherwise an error message is required. |
SNMP Global Settings
View Management
This page allows the network administrator to create MIB views (Management information
base) and then include or exclude OID (Object Identifier) in a view.
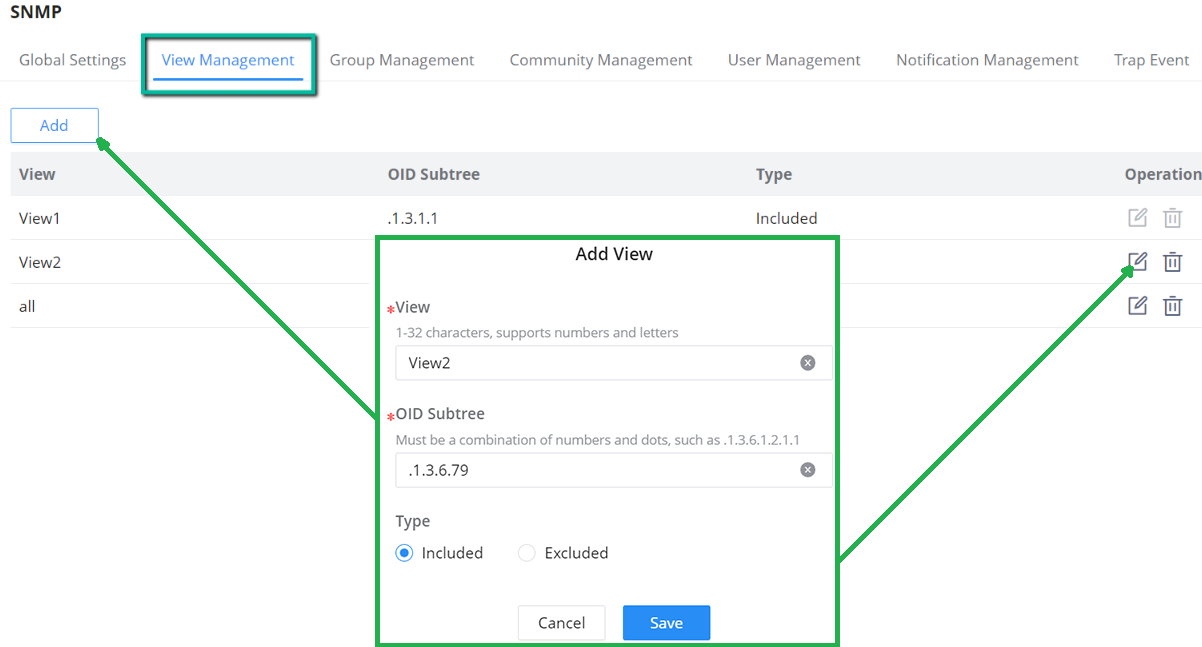
Group Management
When adding an SNMP group, configure the access views with the exact fields Read-Only View, Read-Write View, and Notification View.
This page allows the network administrator to group SNMP users and assign different authorization and access privileges.

Community Management
This page allows a user to add/remove multiple communities of SNMP.
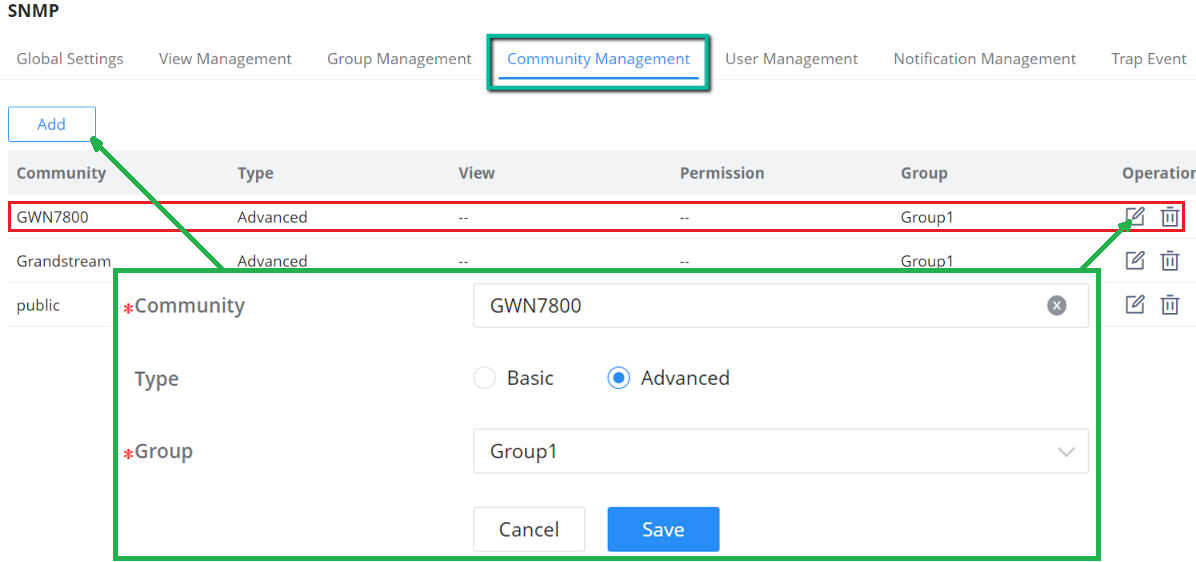
SNMP User Management
This page allows a user to configure the SNMPv3 user profile.

Notification Management
This page allows a user to configure a host to receive SNMPv1/v2/v3 notification.

Trap Event
a Trap event refers to an alert or notification that is automatically sent by a device or system when a specific event occurs. These events, shown in the SNMP configuration, are various types of conditions that the system is monitoring. When enabled, the device sends a trap to the SNMP manager, notifying it of occurrences like:
- Authentication failed: When there is an unauthorized login attempt.
- Port Up/Down: When a network port goes offline or comes online.
- Cold Start/Warm Start: When the system or device reboots (cold or warm restart).
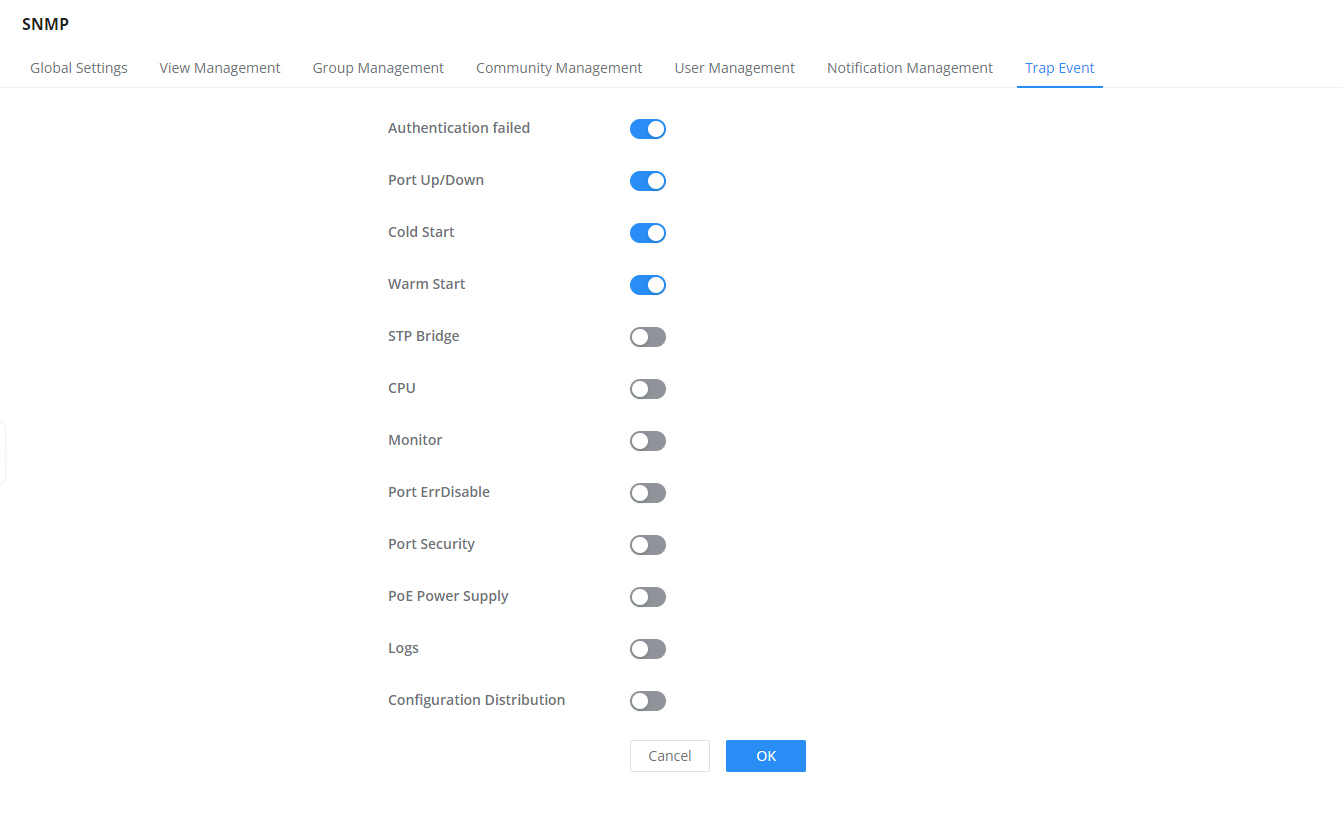
RMON
RMON (Remote Monitoring) based on SNMP (Simple Network Management Protocol) architecture, functions to monitor the network. RMON is currently a commonly used network management standard defined by the Internet Engineering Task Force (IETF), which is mainly used to monitor the data traffic across a network segment or even the entire network to enable the network administrator to take protection measures in time to avoid any network malfunction. In addition, RMON MIB records network statistics information on network performance and malfunction periodically, based on which the management station can monitor the network at any time effectively. RMON is helpful for network administrators to manage the large-scale network since it reduces the communication traffic between the management station and the managed agent.

RMON Statistics
Ethernet statistics function ( corresponding to the statistics group in the RMON MIB): The system collects basic statistics of each network being monitored. The system will continuously count the traffic of a certain network segment and the distribution of various types of packets, the number of error frames of various types, the number of collisions, etc. The number of data packets, the number of broadcast and multicast packets, the number of received bytes, the number of received packets, etc.
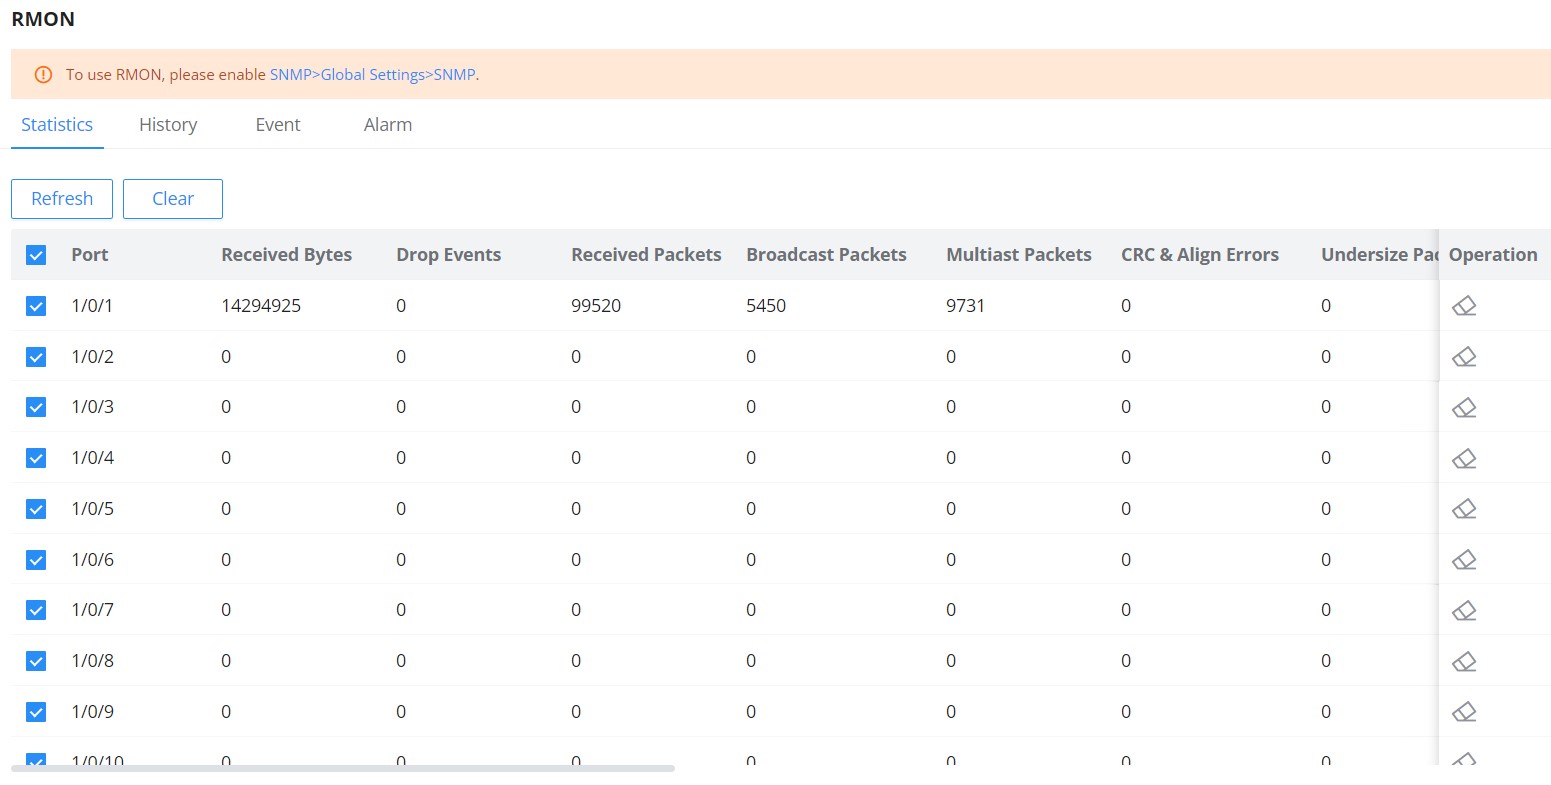
RMON History
The RMON History list shows History ID, Port, Sampling Interval, Owner, Maximum Samples, Current Samples, and Operation. The current UI label is Sampling Interval, without “(s)”.
The system will periodically collect statistics on various traffic information, including bandwidth utilization, number of error packets, and total number of packets based on the History ID.
Click on the “Add” button to create a History ID specifying the Port as well.
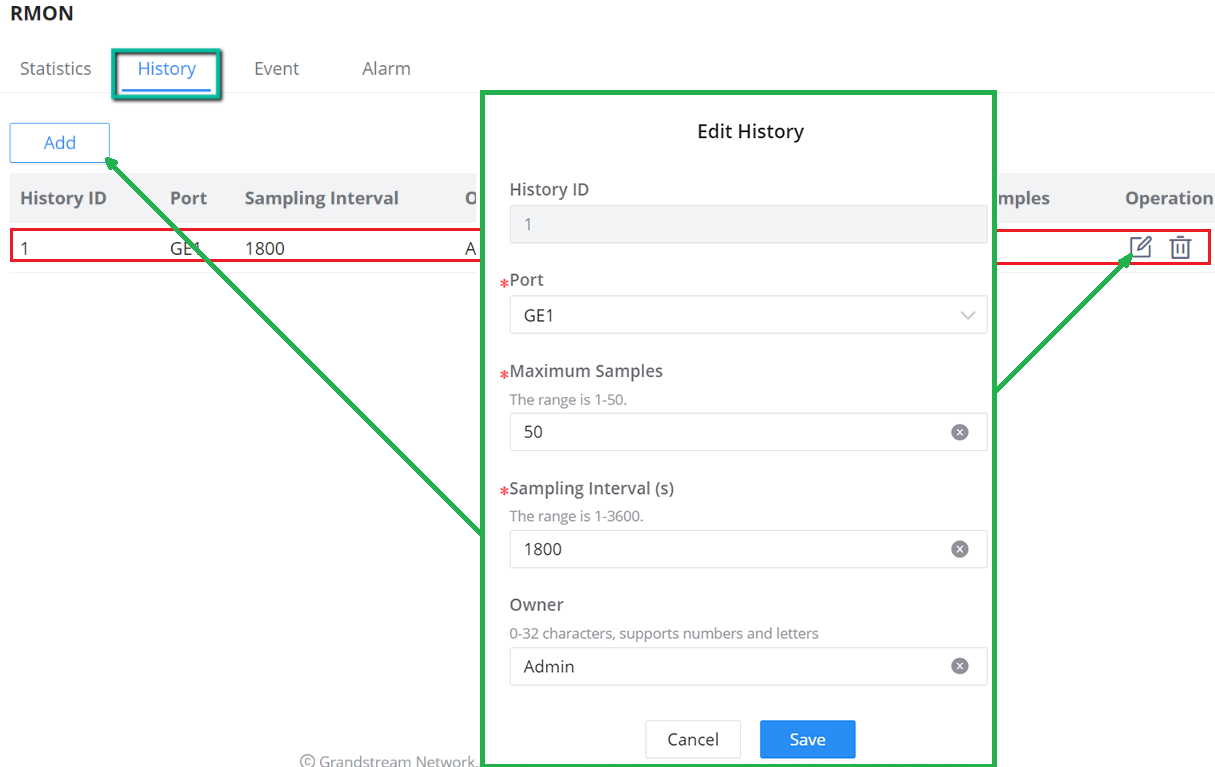
RMON Event
The RMON Event list shows Event ID, Detail, Type, Community, Owner, Event Logs, and Operation.
The event group controls the events and prompts from the device and provides all events generated by the RMON Agent. When an event occurs, it can record logs or send Trap to the network management station.
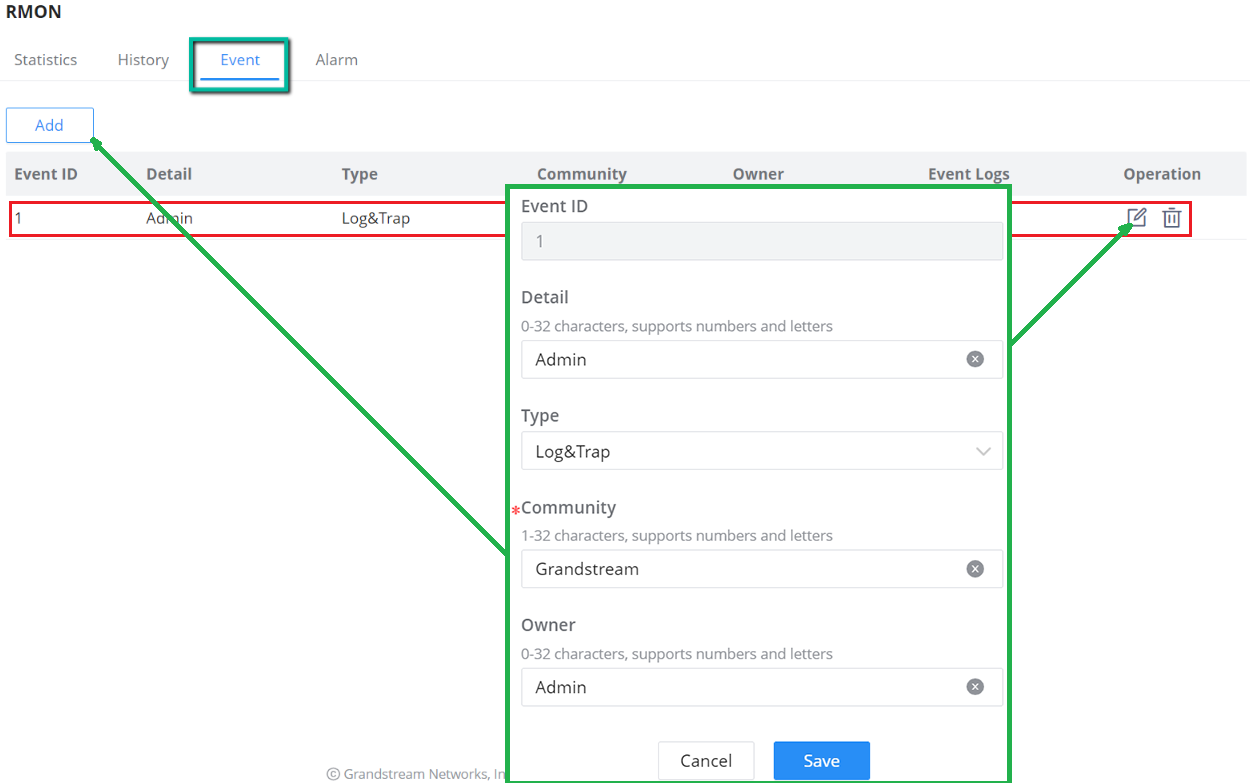
RMON Alarm
The system monitors the specified alarm variable. After pre-defining a set of thresholds and sampling time for the specified alarm, the system will obtain the value of the specified alarm variable according to the defined time period. When the value of the alarm variable is greater than or equal to the upper threshold, an upper alarm event will be triggered. When the value of the alarm variable is less than or equal to the lower threshold, a lower alarm event is triggered.
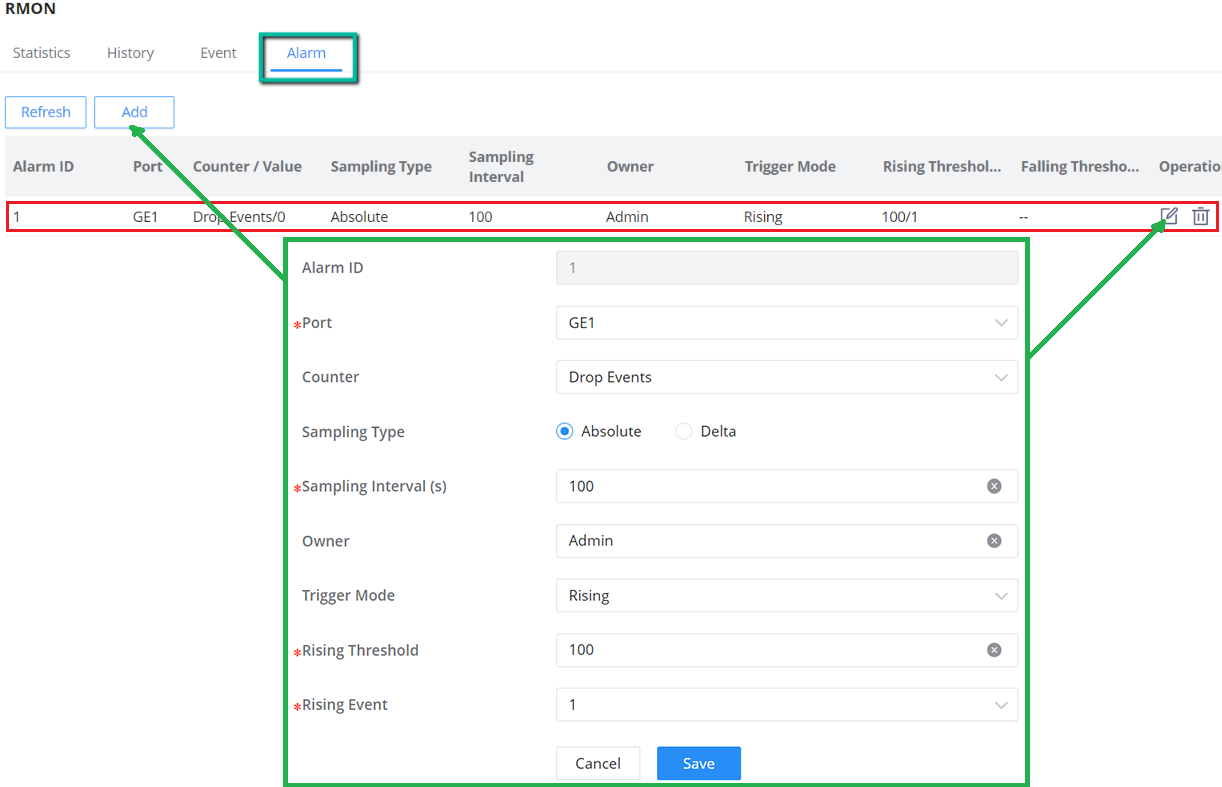
LLDP/LLDP MED
LLDP/LLDP MED is a one-way protocol, there are no request/response sequences. Information is
advertised by stations implementing the transmit function, and is received and processed by
stations implementing the receive function.
LLDP MED is an enhancement to LLDP that provides additional functionality to support media devices. LLDP MED features include: enabling network policy advertisement and discovery for real-time applications (such as voice and/or video);
LLDP Global Settings
This page allows a user to set general settings for LLDP including enabling LLDP and other parameters.
| Field or action | Description |
|---|---|
| TLV Advertise Interval (s) | Accepts 5 to 32767 seconds. |
| TTL Multiplier | Accepts 2 to 10. |
| Port Reinitializing Delay Time (s) | Accepts 1 to 10 seconds. |
| LLDPDU Transmit Delay Time (s) | Accepts 1 to 8191 seconds. |
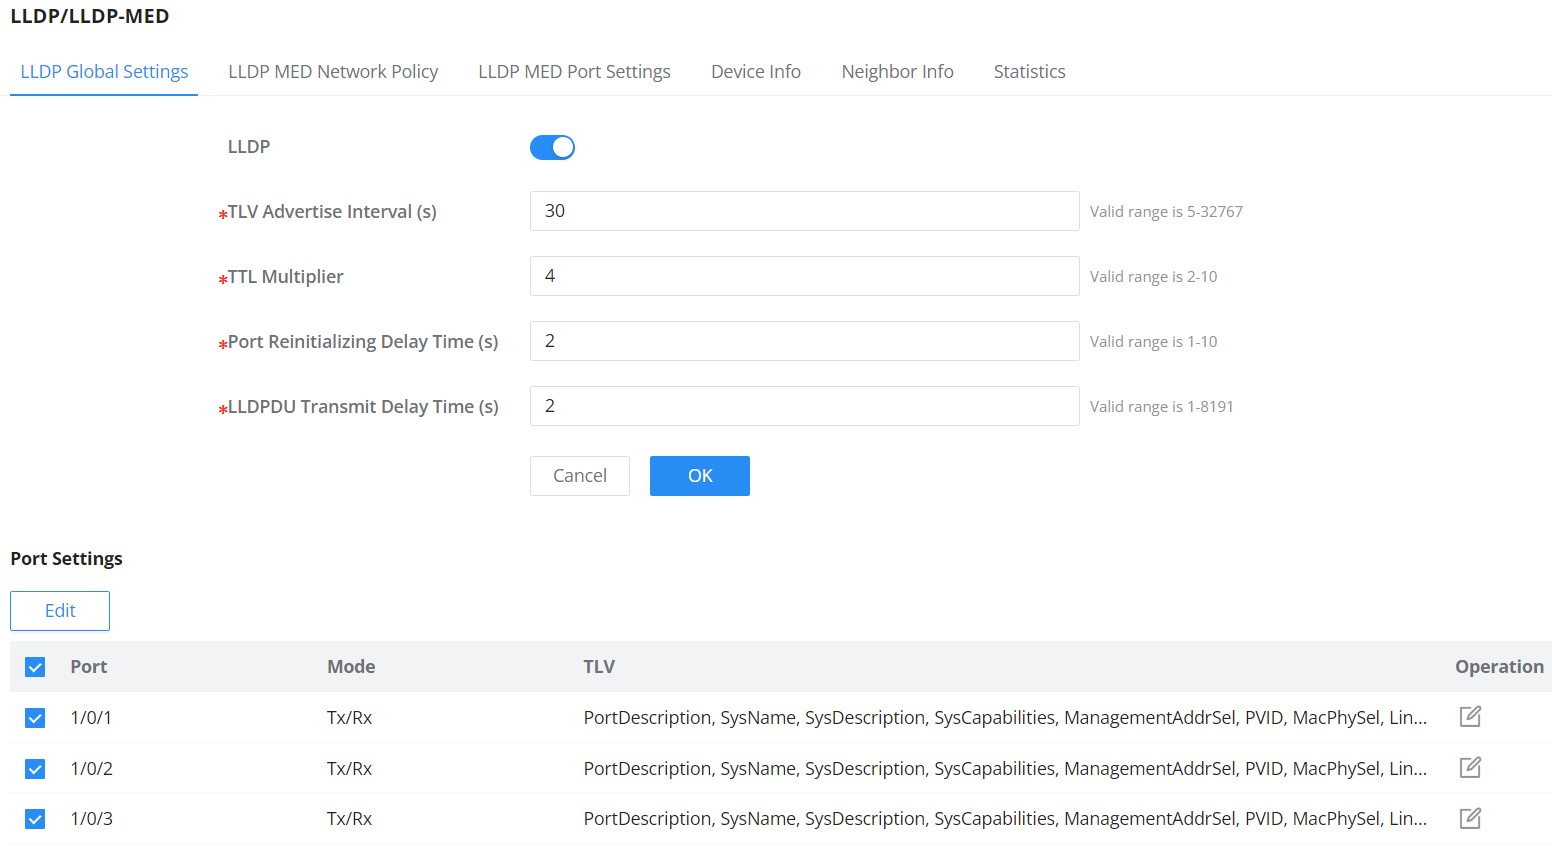
More configurations can adjusted per port (GE1 to GE10).
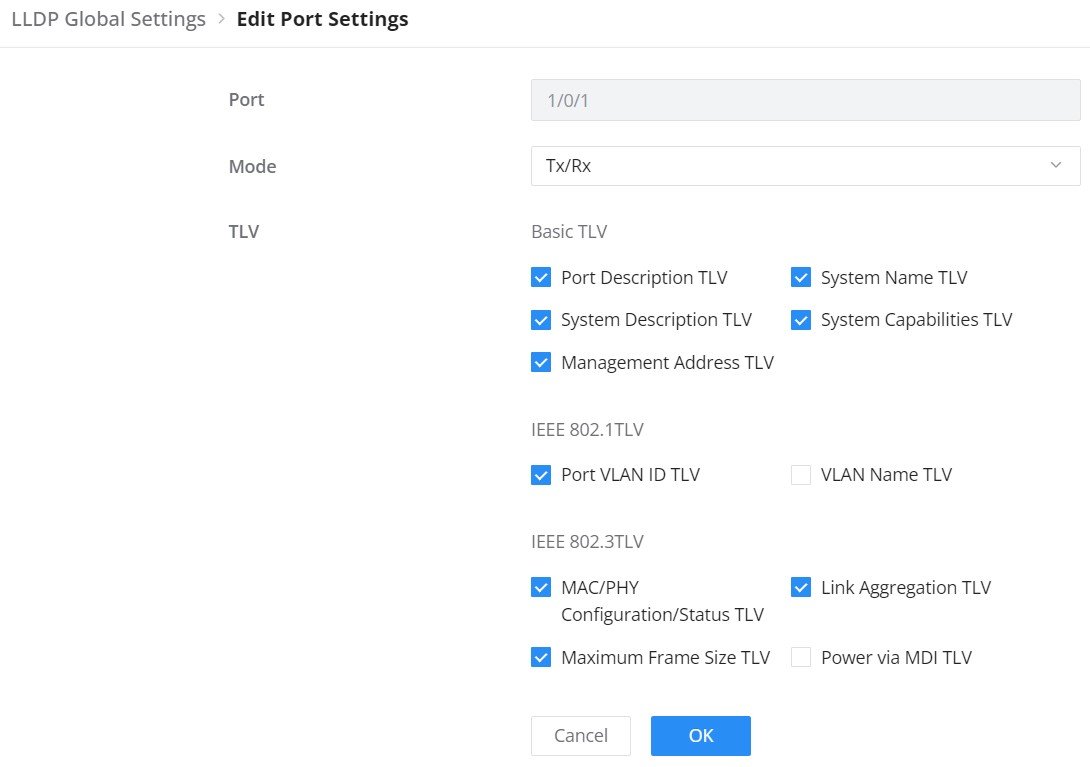
LLDP MED Network Policy
This page allows the network administrator to set the MED (Media Endpoint Discovery) network
policy. Click on the “Add” button to add a Network Policy or toggle ON Auto Voice Network Policy (Voice VLAN has to be configured as well).

To add a Network Policy, click on the “Add” button or click on the “Edit” icon under the Operation column to edit.

LLDP MED Port Settings
The user can configure LLDP MED Settings for each port on this page.
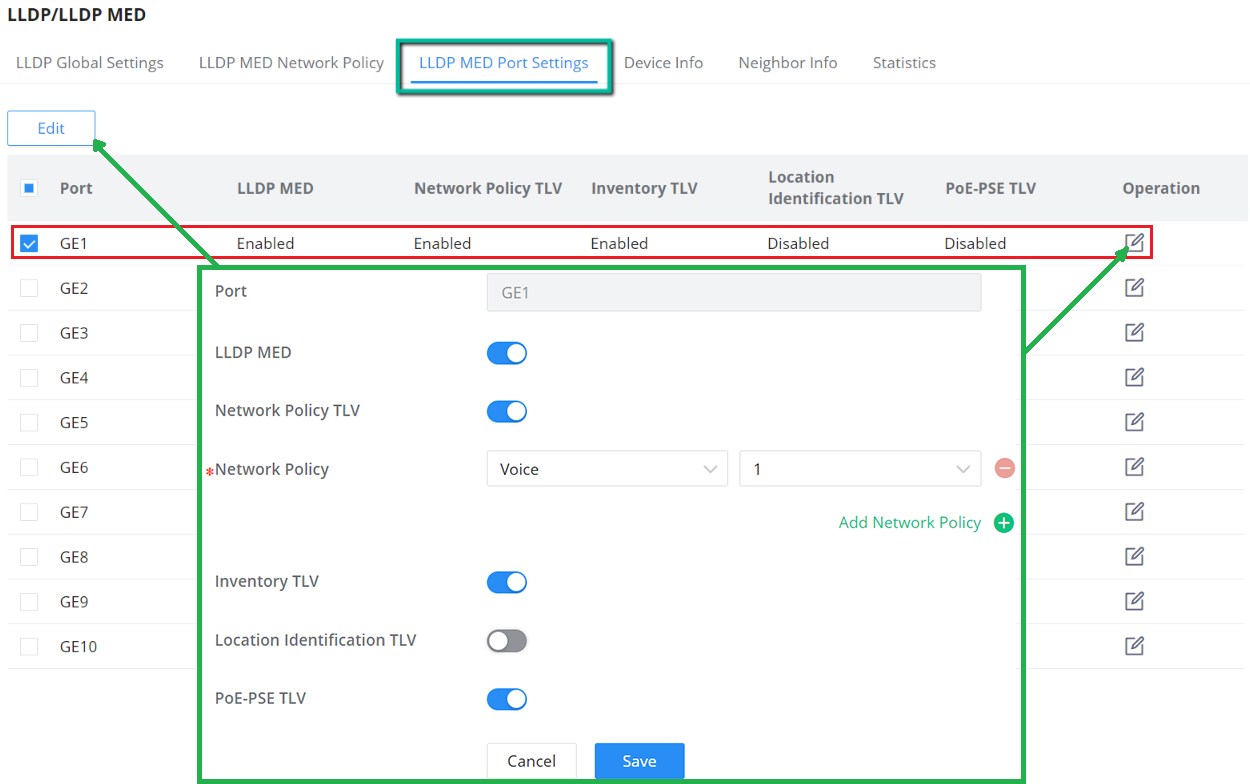
LLDP Device Info
This page displays information for LLDP Local Device connected to each port. Click on the port to view related LLDP information about that port, the information includes: Basic Info, IEEE 802.1 TLVs information, IEEE 802.3 TLVs (802.3 bt) information, MED Details, Network Policy…

Neighbor Info
This page lists the neighbors obtained on the switch ports. Click on the “Refresh” button to update the list.

LLDP Statistics
View the LLDP statistics of the local device through this feature. Click on “Refresh” to update the list.
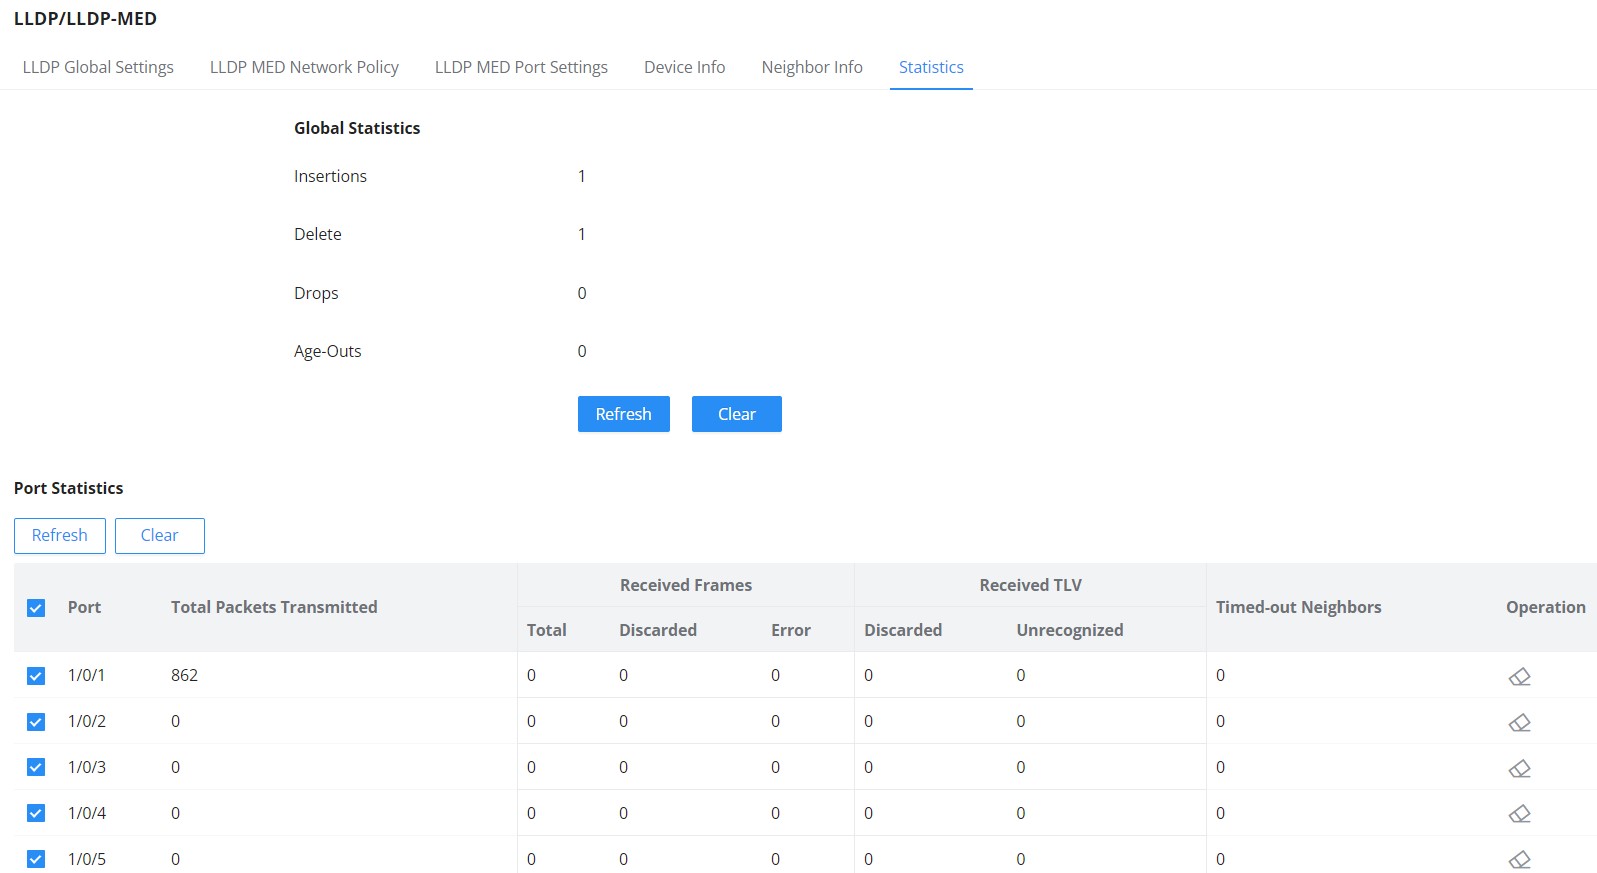
Energy Efficient Ethernet
EEE or Energy Efficient Ethernet helps on reducing the power consumption on interfaces like the switch’s Ethernet ports, it achieves this by using power only during data transmission.
Navigate to Maintenance → Energy Saving Management, select a port to edit then enable 802.3 EEE.
- Configuration Status: shows if the configuration is enabled.
- Status: if a supported device is connected to the switch, it will show if it’s enabled or not.

To enable EEE on a port, select a port then click on “Edit” button then toggle ON 802.3 EEE as shown below:
Alert
The Alerts section allows administrators to set up alert statuses for different types of system reactions for hardware components, this can be configured based on the component’s performance, this can include factors such as CPU Usage, Memory Usage, PoE Power, MAC Address Exceeds Limit, Temperature, Fan Malfunctioning, PoE Chip Malfunctioning…
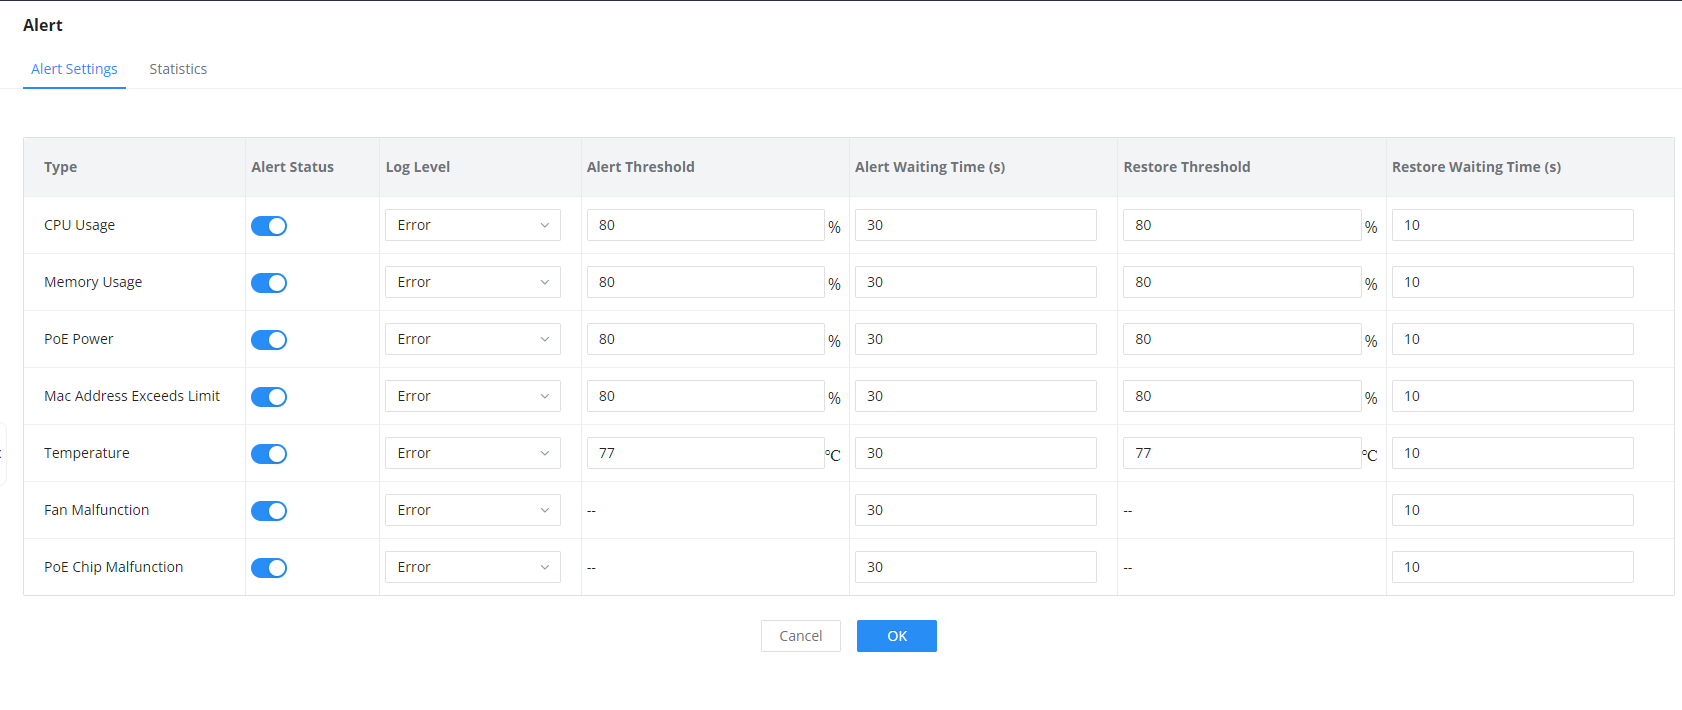
Alert Statistics
The statistics section shows the current status of the Hardware components, in addition to some other hardware information, it also displays the last alert time and last restore time of the service
SYSTEM
Basic Settings
The basic settings page is split into three categories:
- Basic Info: first section, the user can specify a name for the switch with a system location and contact.
- Time Settings: In this section, the users can configure the time either manually, or using an NTP Server, it’s also possible to configure Daylight Saving (DST) Mode according to the location or recurrence.
- Scheduled Reboot: the users can enable scheduled reboot by adding a schedule under the Time Policy.
Please navigate to the System → Basic Settings page.
Under Time Settings, DayLight Saving (DST) Mode controls daylight-saving adjustment. Recurring mode exposes Offset (Min), Starting Time, and Ending Time.
Basic Info | |
Device Name | Specify a name for the device. |
System Location | Enter system location. |
System Contact | Specify the system contact. |
Time Settings | |
Date & Time | Select time synchronization method: Manual or Automatic (NTP Server).
Note: if the device is added to the GDMS Networking and Auto Sync Time feature (under Settings → System) is enabled then the local NTP setting on the device will be disabled. All managed devices will synchronize the time from GDMS Networking. |
System Time |
|
NTP Server | If Date & Time is set to Automatic (NTP Server), please specify the NTP Server address, by default is set to “pool.ntp.org” . |
Time Zone | Select the time zone from the drop-down list. |
DayLight Saving (DST) Mode |
|
Offset (Min) | Specify the Offset by minutes, range from 1 to 1440. |
Starting Time | Specify the starting date and time. |
Ending Time | Specify the ending date and time. |
Scheduled Reboot | |
Reboot Time | Select a reboot time from the drop-down list or click on “+” button to add a schedule. By default is disabled. |
Basic Settings
Access Control
In this section, the user can configure access to the switch.
Please navigate to System → Access Control.
Web Service Management
On the first tab, the user can configure the following:
- Inactive Session Timeout (min): (the range is from 15 seconds to 1440) which is how much time before the switch logs out automatically.
- HTTPS: the HTTPS port, by default, is 443, It can be changed if necessary. (it’s recommended to keep it 443).
- Telnet: can be enabled, but by default is disabled (it’s recommended to keep it disabled, it’s not secure, and use instead SSH).
- SSH: SSH is enabled by default, and it’s a better alternative to Telnet, the default port is 22, It can be changed if necessary. (it’s recommended to keep it to 22)
SSH Remote Access

Enter the password, then click on the “SSH Remote Access” button, it will be automatically disabled in 48 hours.

Passwordless Remote Access
Passwordless Remote Access lets GDMS Networking (or GWN Manager) open the switch Web UI remotely without prompting for the switch’s local username and password. It’s meant to simplify remote support and day-to-day management, especially in environments where access is handled through the management platform rather than by sharing device credentials.
To enable it on the switch, log in to the switch Web UI and go to System → Access Control. Open the Passwordless Remote Access tab, enable the option, then click OK to apply the change.
From GDMS Networking, open the Devices page, locate the target switch, and click the Remote Access icon in the Operation column to launch a proxied Web UI session.
GDMS will begin establishing the remote access session and display a connection page while the proxy is being created.
Once the session is ready, the switch Web UI opens directly through GDMS without asking for the device password.
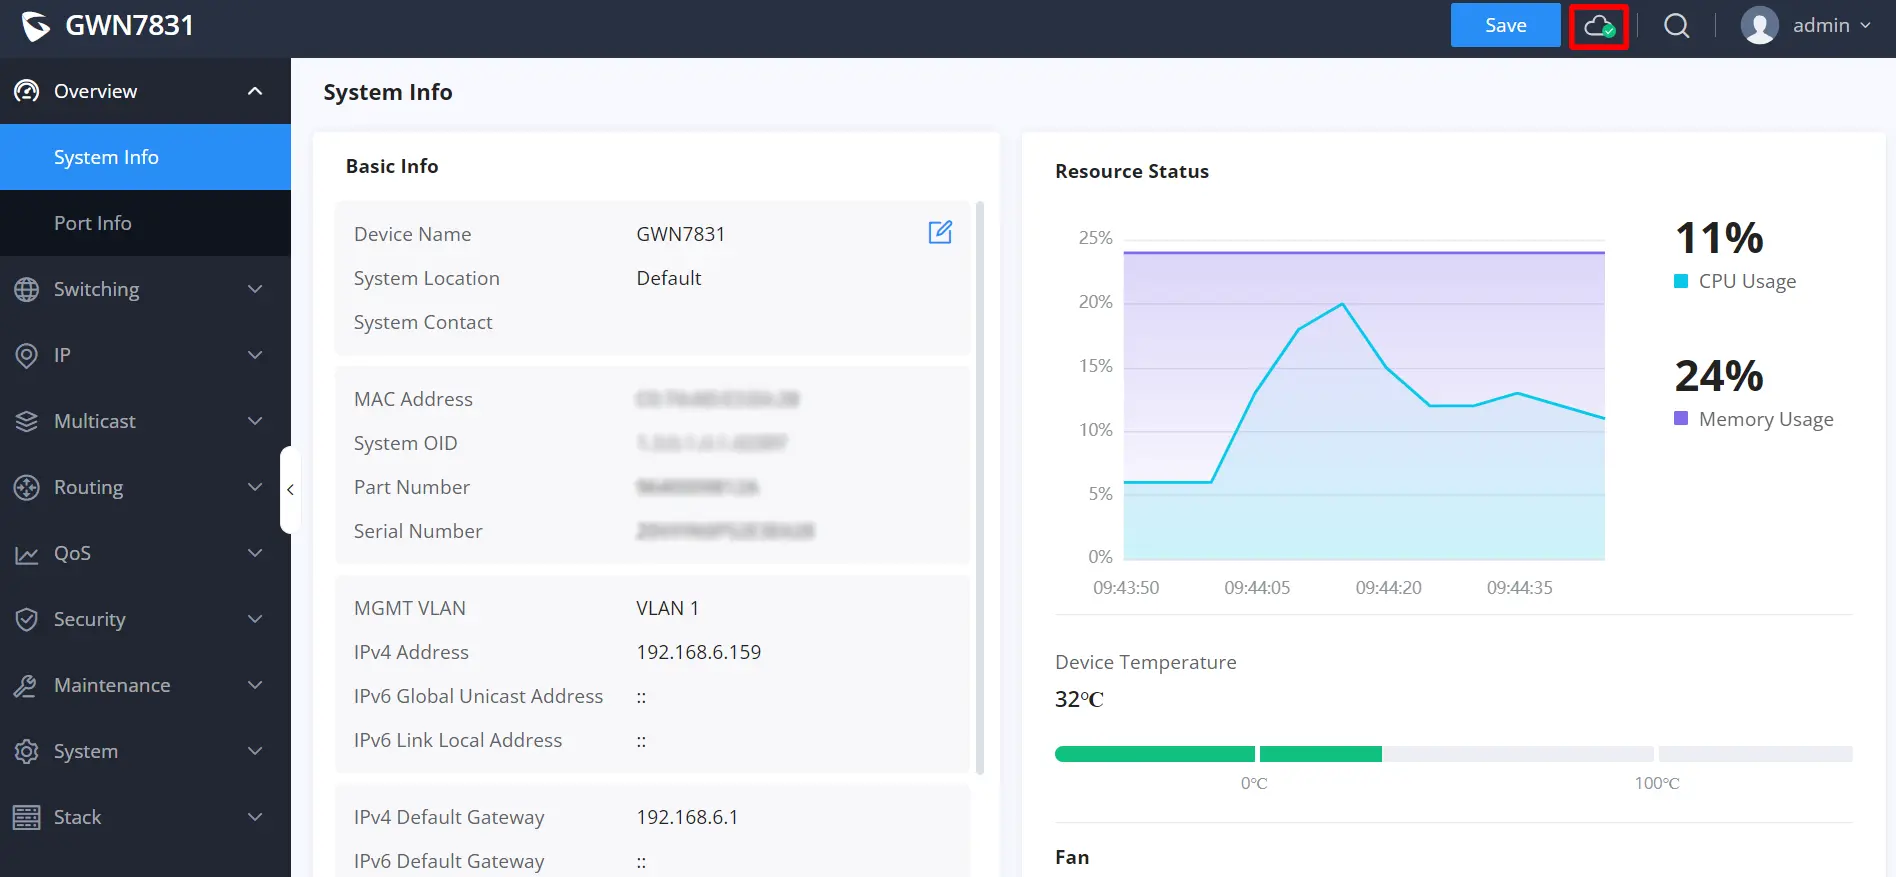
Warning: For security, only enable this feature for devices managed under trusted GDMS/GWN Manager accounts, and disable it when you don’t need passwordless access.
Management Platform Settings
The Management Platform Settings tab controls centralized management. Allow DHCP Option 43 to Override Management Server gives a DHCP-provided server address priority over the manually configured address. Enable Management Server Settings, select GWN Manager or GWN Router, enter the Management Server Address, and set the Management Server Port from 1 to 65535. The default port is 8443.
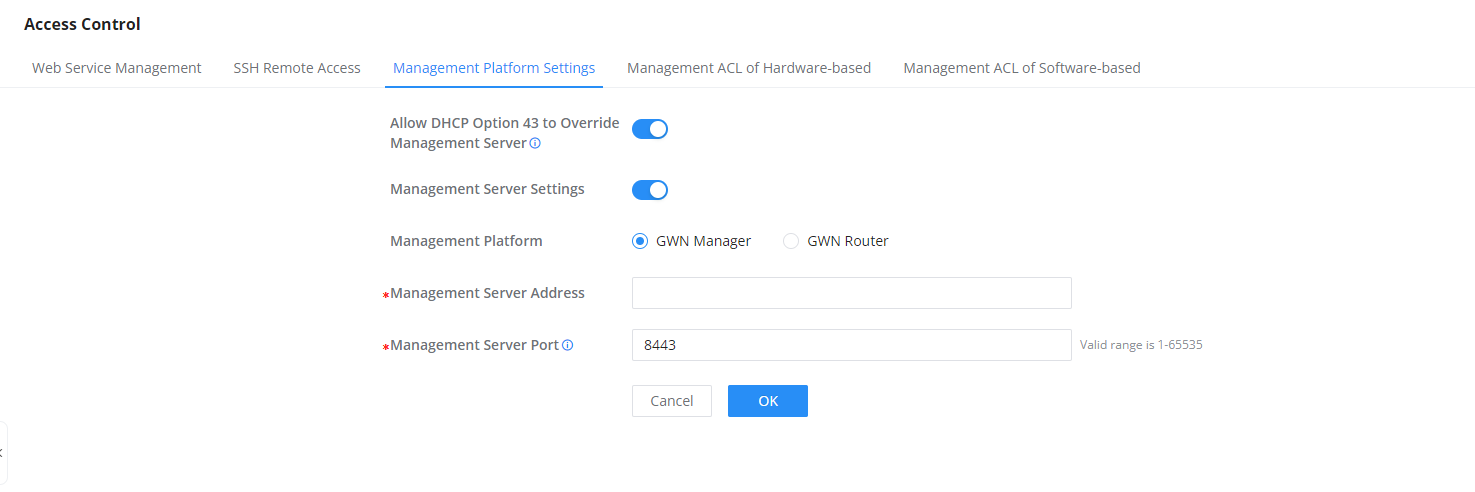
Management ACL of Hardware-based
On the switch, the hardware management Access Control List (ACL) is designed to optimize resource efficiency by filtering traffic directly at the hardware level before it reaches the CPU. This pre-processing step ensures that only traffic matching the defined security rules is forwarded for further handling, effectively reducing unnecessary CPU load and enhancing overall performance. By offloading the initial traffic validation to the switch hardware, the switch improves both network efficiency and security.
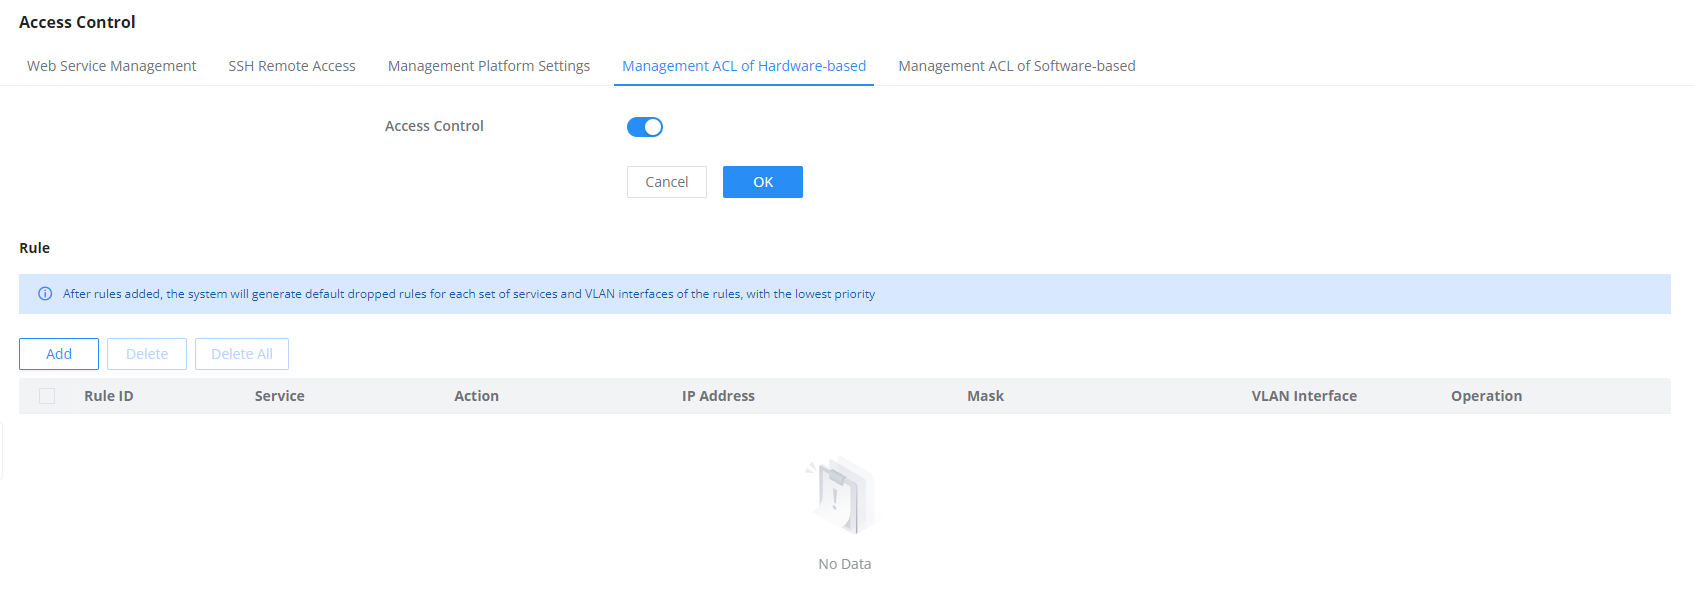
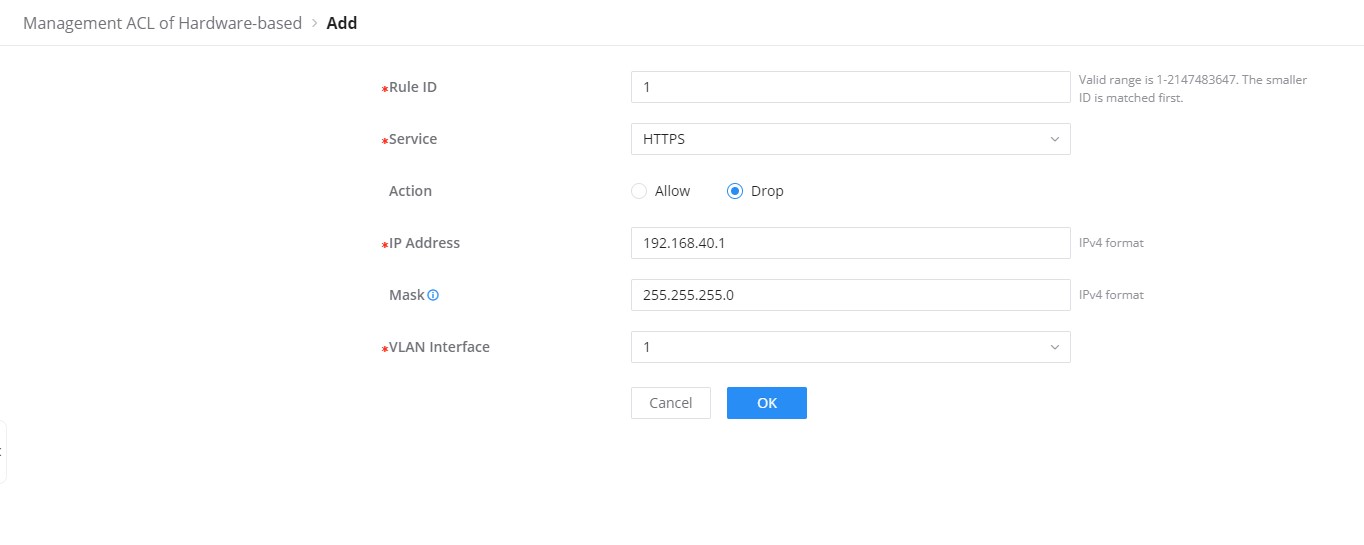
Management ACL of Software-based
On the switch, the software-based Management ACL uses firewall-like rules to control who can access the network and its management features. This means it sets up restrictions to make sure that only authorized users and devices can access important parts of the switch, helping to keep the network secure and well-managed.
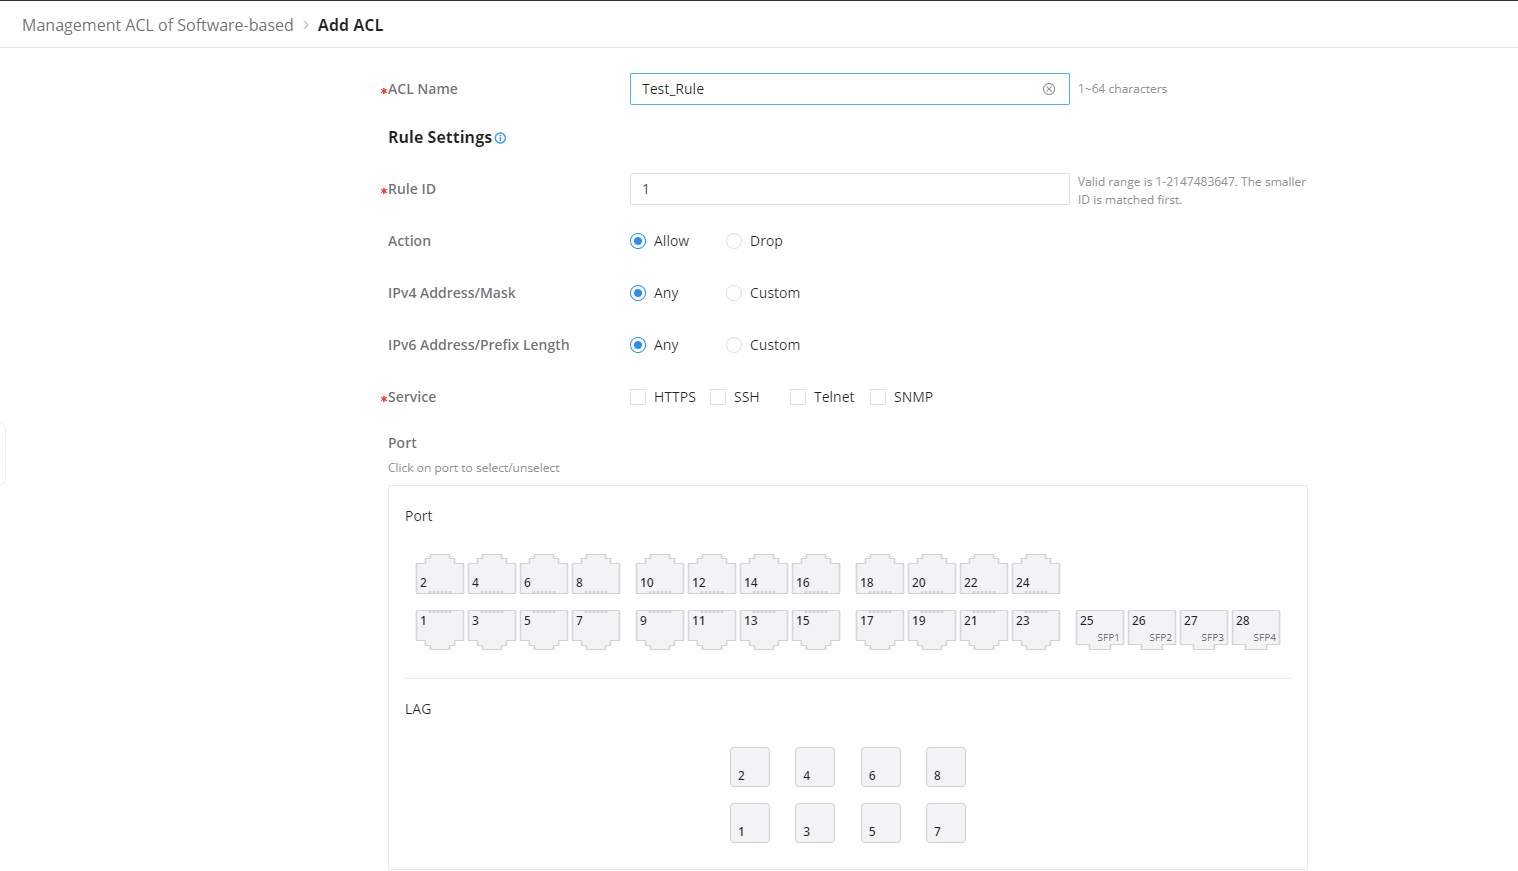
User Management
There are three levels of users, namely administrator, operator and monitor. The administrator authenticates and authorizes users who log in to the switch according to management need where each user has different permissions and passwords.
When adding a local user, enter Username, Password, and Confirm Password, then select the User Level as Operator or Monitor. The confirmation field prevents saving a mistyped password.
- Administrator
- Each device has one and only one administrator.
- The highest privileges can execute any command.
- The username admin cannot be changed, only the password can be changed.
- Support adding, and deleting operator and monitor.
- Operator
- Added by an administrator, there can be multiple accounts as Operators.
- The second highest authority can execute all commands except the administrator’s key operations and important mandatory commands
- Can’t change the username, only the password.
- Support adding, and deleting Monitor users.
- Monitor
- Multiple Monitors are possible with the permission of an Administrator or Operator.
- The lowest authority can only view switch status and statistics without any execution and configuration authority.
- Can’t change the username, only the password.
Click on the “Add” button to add a new user then specify the password and the user level (Operator or Monitor).
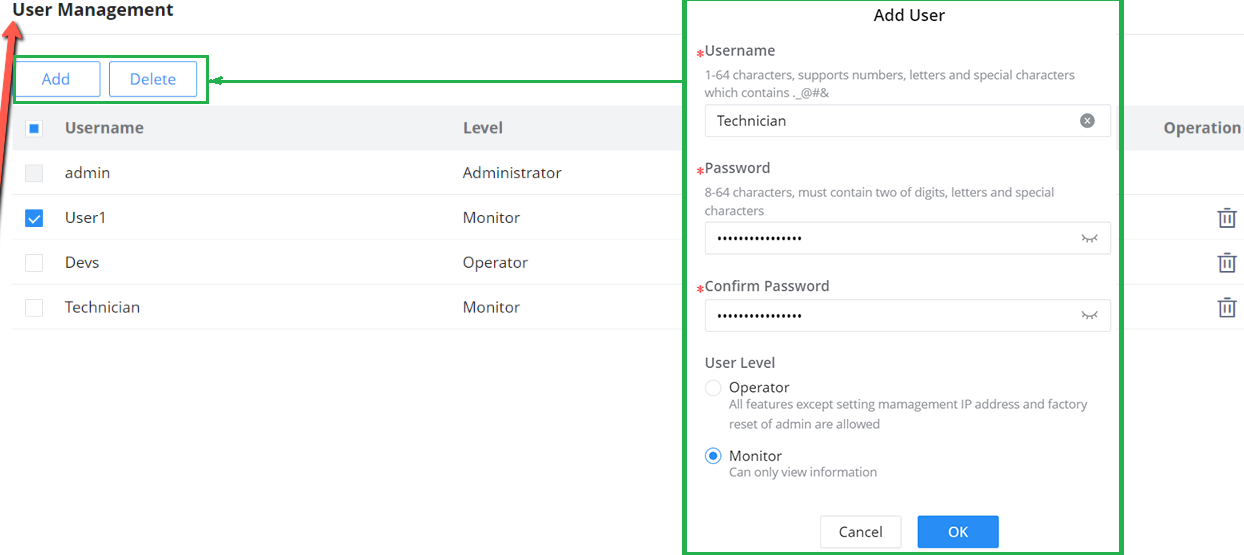
Time Policy
The time policy page helps to create schedules, for example, Office working hours, Upgrade schedules or Reboot schedules.
To create a schedule, Please navigate to Web UI → System → Time Policy page, then click on “Create Policy” button, there are weekly schedules or absolute Date/Time schedules, for weekly schedules please select from the table the hours and days and as for absolute Date/Time select the days from the drop-down calendars and times from the drop-down menu. Please refer to the figure below.
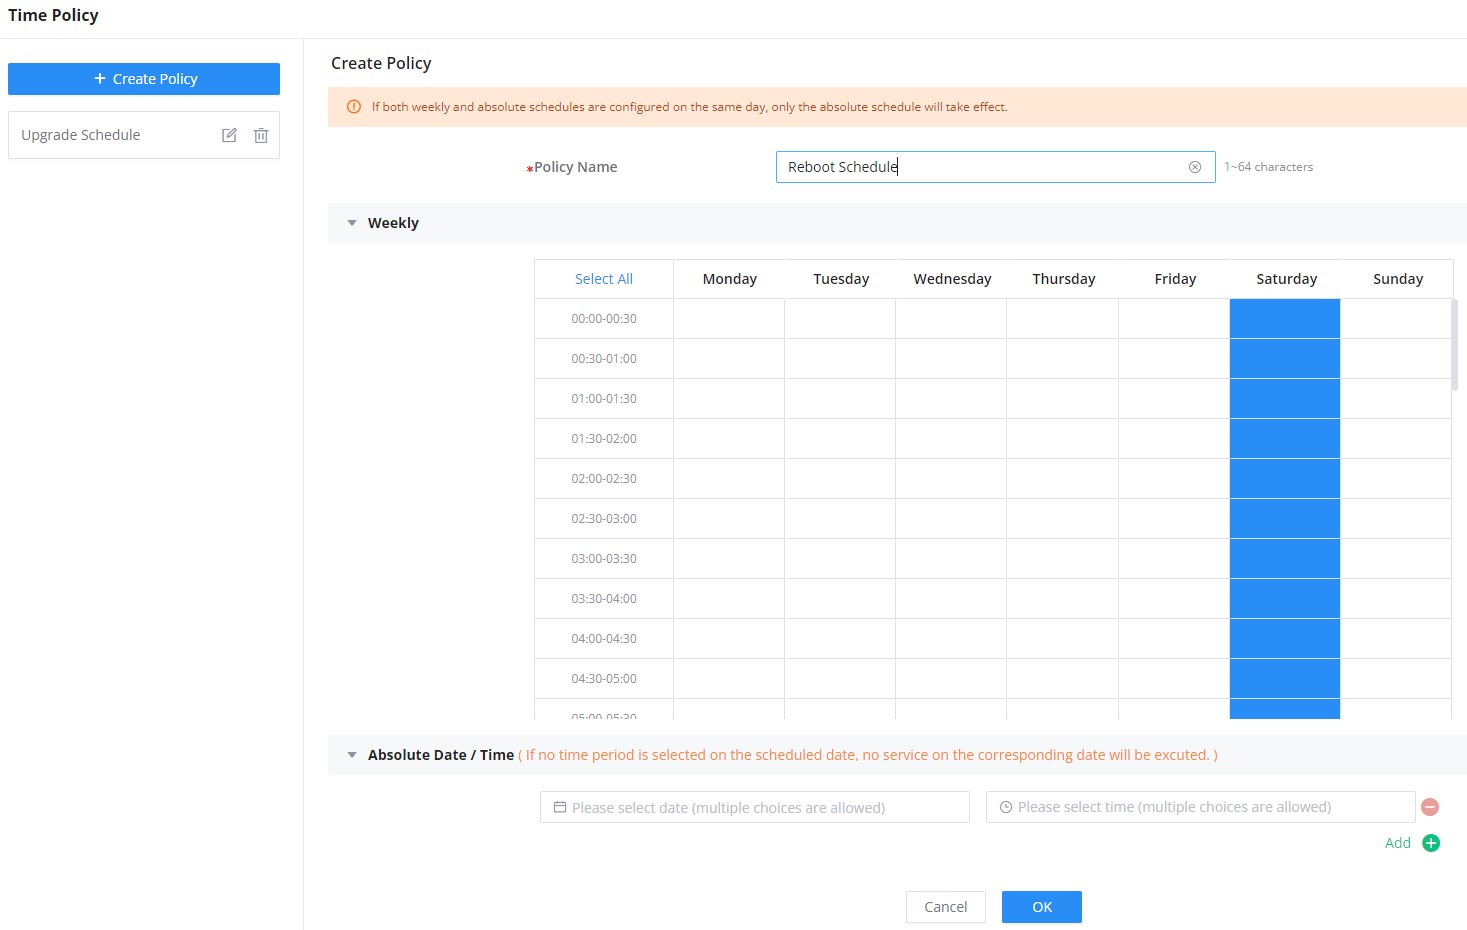
1588v2 TC
IEEE 1588v2 is a protocol for synchronizing clocks, enabling accurate time between nodes in a network.
A transparent clock or TC is a type of clock used in IEEE 1588v2 networks and it uses a Precision Time Protocol (PTP) messages to accurately calculate the time.
E2E or (End-to-End) transparent clock measures the delay at each network element between the master and slave clocks.
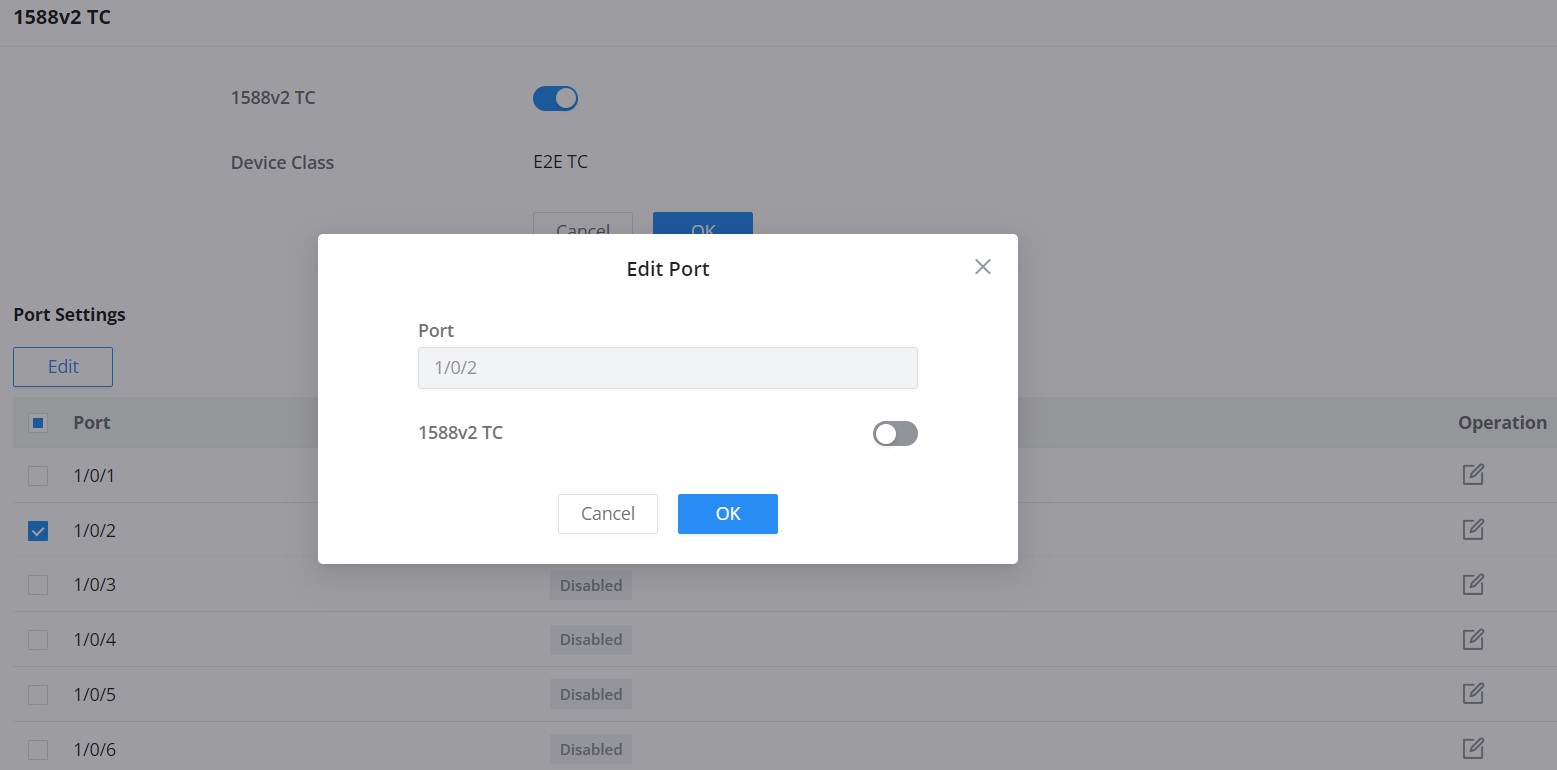
STACK
Stacking allows multiple supported switches to operate as a single logical unit, simplifying network management, increasing redundancy, and expanding port density. This feature is available only on the following models:
To access this feature, navigate to:
Web UI → Stack → Stack Settings
💡 For full configuration examples, topology use cases, and best practices, please refer to the GWN78xx Stacking Feature Guide.
Stack Settings
In this section, you can enable stack mode, assign a device ID and priority, and define the physical ports used for stacking.
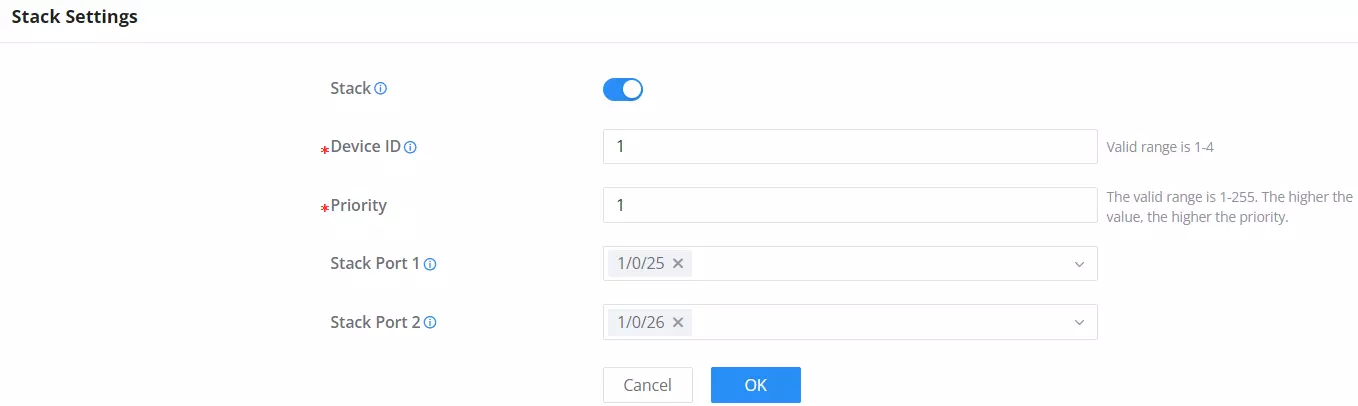
- Stack
Enable or disable stacking functionality.
- When enabled, this device becomes part of a stack group.
- Make sure the ports used are in shutdown status before configuration.
- Only 10G fiber modules are supported.
- Device ID
Unique identifier for the device in the stack.
- Range: 1–4
- Must be unique across all devices in the same stack.
- Priority
Sets the priority level for master election during stack formation.
- Range: 1–255
- Higher value = higher priority
- Stack Port 1 & Stack Port 2
Select the two physical ports to use for stacking interconnection.
- Must be 10G ports
- Ensure that these ports are correctly cross-connected between switches
Stack Info
This page displays the current stack topology and status, including member switches and their roles (Master/Member), device IDs, priorities, and port mappings.
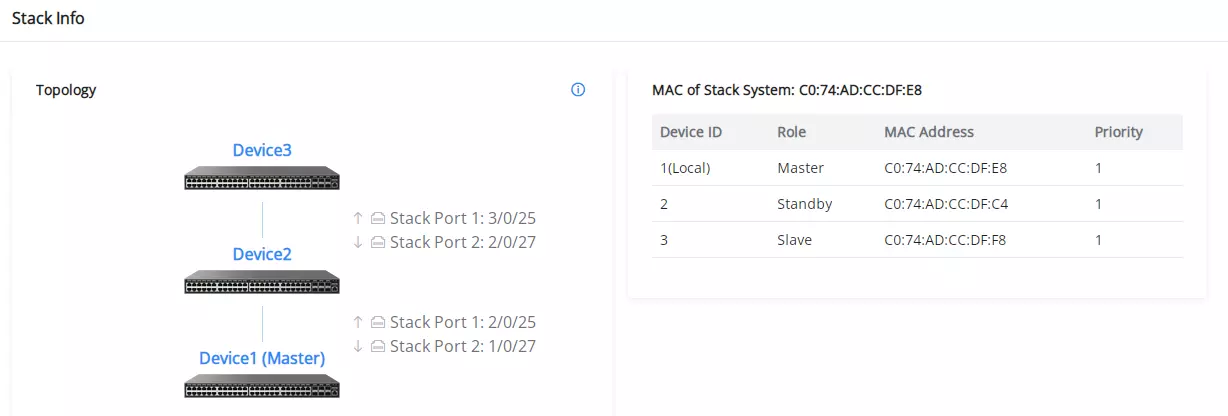
- If no data appears, ensure stack settings are properly configured and devices are connected.
- All stacked switches must be running the same firmware version.
CHANGE LOG
This section documents significant changes from previous versions of this user manual. Only major new features or major document updates are listed here. Minor updates for corrections or editing are not documented here.
Version 1.0.15.137
Product Name: GWN7811(P), GWN7812P, GWN7813(P), GWN7816(P), GWN7821P, GWN7822P, GWN7830, GWN7831, GWN7832.
- Added Passwordless Remote Access option that allows GDMS Networking / GWN Manager to open the device Web UI remotely without requiring the device username or password. [Passwordless Remote Access]
Version 1.0.15.135
Product Name: GWN7811(P), GWN7812P, GWN7813(P), GWN7816(P), GWN7821P, GWN7822P, GWN7830, GWN7831, GWN7832.
- No major changes
Version 1.0.15.132
Product Name: GWN7811(P), GWN7812P, GWN7813(P), GWN7816(P), GWN7821P, GWN7822P, GWN7830, GWN7831, GWN7832.
- Added support for ignoring credentials during SSH authentication. [SSH] [CLI Access]
- Added key for “encrypted” field to configuration files for Radius and TACACS+. [RADIUS] [TACACS+] [CLI Access]
Version 1.0.15.126
Product Name: GWN7811(P), GWN7812P, GWN7813(P), GWN7816(P), GWN7821P, GWN7822P, GWN7830, GWN7831, GWN7832.
- Added support for switch stacking feature. [Stack]
- Added the Ability to disable the native VLAN. [VLAN Port Setting]
- Added support for PVLAN. [PVLAN]
- Added the option to set the Web GUI language on the configuration. [Web GUI Languages]
- Added support to use encrypted strings in password fields in CLI. [RADIUS]
- Added support for “Calling-Station-Id” in RADIUS Access-Request. [Identity Authentication Management]
Version 1.0.13.18
Product Name: GWN7811(P), GWN7812P, GWN7813(P), GWN7816(P), GWN7821P, GWN7822P, GWN7830, GWN7831, GWN7832.
- No major changes
Version 1.0.13.6
Product Name: GWN7811(P), GWN7812P, GWN7813(P), GWN7816(P), GWN7821P, GWN7822P, GWN7830, GWN7831, GWN7832.
- Added support for BGP & Route Policy on L3 Switch. [BGP] [Route Policy]
- Added LED status change during the start-up process. [LED Indicators]
- Removed PTP settings from Web UI.
- This is the initial release for GWN7821P/GWN7822P Switches.
Version 1.0.9.15
Product Name: GWN7832
- Added port groups. [Port Group]
- Added LLDP-based automatic configuration for Auto Voice VLAN mode.
- Added more features for STP, including ignore VLAN in BPDU, root protection and loopback protection. [Ignore VLAN in BPDU] [Root Protection] [Loop Protection]
- Added more OUI in Voice VLAN. [OUI]
- Added IP configuration for MGMT VLAN. [MGMT VLAN]
- Added redirect to interface for ACL. [Redirect to Interface]
- Added VLAN binding to ACL function.[VLAN Binding to ACL]
- Optimized the rate limit groups from 32 to128 in ACL. [Rate Limit Settings]
- Added mask for IPSG/IPv6SG. [IP Source Guard]
- Added remote-ID configuration based on port for DHCP Snooping. [DHCP Option 82]
- Changed DHCP’s Option 82 Circuit ID/Remote ID. [DHCP Option 82]
- Added entries fixed for DHCP/DHCPv6 Snooping. [DHCP Snooping]
- Added flow upgrade via manual upgrade. [Upgrade Flow]
- Added more settings for logs, including minimum log level and log aggregation. [Log Aggregation]
- Added Ping watchdog in diagnostics. [Ping Watchdog]
- Added connection diagnostics of GWN router. [GWN Router]
- Added RSPAN, including port-based and ACL-based remotely mirroring. [RSPAN] [Configuring an ACL based RSPAN]
- Added new SNMP Traps. [Trap Event]
- Added 802.3bt info in LLDP. [IEEE 802.3 TLV]
- Added Maintenance Alerts. [Alert]
- Added management ACL, including hardware-based and software-based management ACL. [Management ACL of Hardware-based] [Management ACL of Software-based]
- Added Layer 3 discovery and management by GWN router.[Management Platform Settings]
- Added ACL for VTY (SSH and telnet). [Web Service Management]
- Added additional Radius Access-Request Attributes. [Identity Authentication Management]
- Removed Commited Burst Configuration from Queue Shaping. [Queue Shaping]
- Added 1588v2 P2P TC. [1588v2 P2P TC]
- Added NAS-Port-Type value 15 with alternate management VLAN. [MGMT VLAN]
- Added ability to shutdown port by profile group. [Port Group]
- Added more port details such as neighbor and PoE power history info. [Port Info]
- Added more port statistics info. [Port Statistics]
- Added loopback detection. [Loopback Detection]
- Added support for QinQ. [QinQ]
- Added MAC-based VLAN. [MAC VLAN]
- Added protocol-based VLAN. [Protocol VLAN]
- Added VLAN translation. [VLAN translation]
- Added untagged OUI mode for voice VLAN. [Voice VLAN]
- Added gateway priority when using DHCP to get VLAN IP address [VLAN IP Interface]
- Added import/export IPSG binding table for IP Source Guard. [IP Source Guard]
- Added IPv6 Source Guard. [IPv6 Source Guard]
- Added MAC bypass authentication. [Identity Authentication Management]
- Added upgrade by FTP and Explicit FTPS. [FTP] [Explicit FTPS]
- Added DST mode for time settings. [DST]
- Added HTTPS/SSH port customization. [Web Service Management]
- Added GWN Manager takeover function. [Management Platform Settings]
- Optimized DHCP option 43 settings for DHCP server. [DHCP Server]
- Optimized routing table. [Routing Forwarding]
- Added port scheduled enabling feature. [Scheduled enabled]
- Added DHCPv6 Snooping. [DHCPv6 Snooping]
- Optimized CPU and memory usage in Web GUI. [System Info]
- Optimized search for Web GUI. [Search]
Product Name: GWN7830/GWN7831
- Added port groups. [Port Group]
- Added LLDP-based automatic configuration for Auto Voice VLAN mode.
- Added more features for STP, including ignore VLAN in BPDU, root protection and loopback protection. [Ignore VLAN in BPDU] [Root Protection] [Loop Protection]
- Added more OUI in Voice VLAN. [OUI]
- Added IP configuration for MGMT VLAN. [MGMT VLAN]
- Added redirect to interface for ACL. [Redirect to Interface]
- Added VLAN binding to ACL function.[VLAN Binding to ACL]
- Optimized the rate limit groups from 32 to128 in ACL. [Rate Limit Settings]
- Added mask for IPSG/IPv6SG. [IP Source Guard]
- Added remote-ID configuration based on port for DHCP Snooping. [DHCP Option 82]
- Changed DHCP’s Option 82 Circuit ID/Remote ID. [DHCP Option 82]
- Added entries fixed for DHCP/DHCPv6 Snooping. [DHCP Snooping]
- Added flow upgrade via manual upgrade. [Upgrade Flow]
- Added more settings for logs, including minimum log level and log aggregation. [Log Aggregation]
- Added Ping watchdog in diagnostics. [Ping Watchdog]
- Added connection diagnostics of GWN router. [GWN Router]
- Added RSPAN, including port-based and ACL-based remotely mirroring. [RSPAN] [Configuring an ACL based RSPAN]
- Added new SNMP Traps. [Trap Event]
- Added 802.3bt info in LLDP. [IEEE 802.3 TLV]
- Added Maintenance Alerts. [Alert]
- Added management ACL, including hardware-based and software-based management ACL. [Management ACL of Hardware-based] [Management ACL of Software-based]
- Added Layer 3 discovery and management by GWN router.[Management Platform Settings]
- Added ACL for VTY (SSH and telnet). [Web Service Management]
- Added additional Radius Access-Request Attributes. [Identity Authentication Management]
- Removed Commited Burst Configuration from Queue Shaping. [Queue Shaping]
Version 1.0.7.71
Product Name: GWN7830/GWN7831
- Optimized search for Web GUI [Search]
- Optimized CPU and memory usage in Web GUI [System Info]
- Optimized device IP address display [System Info]
- Added more port details such as neighbor, PoE power history info [Port Info]
- Added port scheduled enabling feature [Port Basic Settings]
- Added more port statistics info [Port Statistics]
- Added loopback detection feature [Loopback Detection]
- Added QinQ [VLAN]
- Optimized trunk port settings [VLAN Port Members]
- Added MAC-based VLAN [MAC VLAN]
- Added protocol-based VLAN [Protocol VLAN]
- Added VLAN translation [VLAN Port Settings]
- Added default gateway configuration under MGMT VLAN [VLAN IP Interface]
- Added gateway priority when using DHCP to get VLAN IP address [VLAN IP Interface]
- Optimized DHCP option 43 configuration for DHCP server [DHCP Server]
- Added advanced ACL settings, including mirroring, statistics, and priority remapping for a rule [ACL]
- Added import/export IPSG binding table for IP Source Guard [IP Source Guard]
- Added IPv6 Source Guard [IPv6 Source Guard]
- Optimized remote ID and Circuit ID for DHCP Snooping [DHCP Snooping option 82]
- Added DHCPv6 Snooping [DHCPv6 Snooping]
- Added upgrade by FTP and Explicit FTPS [Upgrade]
- Added connection diagnostics with GWN.Cloud/Manager [Cloud/Manager Connection Diagnostics]
- Optimized EEE [Energy Efficient Ethernet]
- Added DST mode for time settings [Basic Settings]
- Added HTTPS/SSH port customization [Web Service Management]
- Optimized Manager settings [Manager Settings]
- Added rate limit by ACL binding to VLAN. [VLAN Binding to ACL]
- Added MAC bypass authentication. [Local User of MAC-based]
- Add GWN Manager takeover function [Manager Settings]
- Expanded DHCP leases range up to 11520 min [DHCP Server]
- Added refresh IP address when using DHCP to get VLAN IP address. [VLAN IP Interface]
- Added support for OSPFv3. [OSPFv3]
- Added support for 12 VTY (SSH or telnet) sessions. [Access Control]
- Added support to see switch clients and other information. [Port Info]
Version 1.0.3.1
Product Name: GWN7830, GWN7831, GWN7832
- This is the initial release.
Version 1.0.9.15
Product Name: GWN7816(P)
- Added port groups. [Port Group]
- Added LLDP-based automatic configuration for Auto Voice VLAN mode.
- Added more features for STP, including ignore VLAN in BPDU, root protection and loopback protection. [Ignore VLAN in BPDU] [Root Protection] [Loop Protection]
- Added more OUI in Voice VLAN. [OUI]
- Added IP configuration for MGMT VLAN. [MGMT VLAN]
- Added redirect to interface for ACL. [Redirect to Interface]
- Added VLAN binding to ACL function.[VLAN Binding to ACL]
- Optimized the rate limit groups from 32 to128 in ACL. [Rate Limit Settings]
- Added mask for IPSG/IPv6SG. [IP Source Guard]
- Added remote-ID configuration based on port for DHCP Snooping. [DHCP Option 82]
- Changed DHCP’s Option 82 Circuit ID/Remote ID. [DHCP Option 82]
- Added entries fixed for DHCP/DHCPv6 Snooping. [DHCP Snooping]
- Added flow upgrade via manual upgrade. [Upgrade Flow]
- Added more settings for logs, including minimum log level and log aggregation. [Log Aggregation]
- Added Ping watchdog in diagnostics. [Ping Watchdog]
- Added connection diagnostics of GWN router. [GWN Router]
- Added RSPAN, including port-based and ACL-based remotely mirroring. [RSPAN] [Configuring an ACL based RSPAN]
- Added new SNMP Traps. [Trap Event]
- Added 802.3bt info in LLDP. [IEEE 802.3 TLV]
- Added Maintenance Alerts. [Alert]
- Added management ACL, including hardware-based and software-based management ACL. [Management ACL of Hardware-based] [Management ACL of Software-based]
- Added Layer 3 discovery and management by GWN router.[Management Platform Settings]
- Added ACL for VTY (SSH and telnet). [Web Service Management]
- Added additional Radius Access-Request Attributes. [Identity Authentication Management]
- Removed Commited Burst Configuration from Queue Shaping. [Queue Shaping]
- Added 1588v2 P2P TC. [1588v2 P2P TC]
- Added NAS-Port-Type value 15 with alternate management VLAN. [MGMT VLAN]
- Added ability to shutdown port by profile group. [Port Group]
- Added more port details such as neighbor and PoE power history info. [Port Info]
- Added more port statistics info. [Port Statistics]
- Added loopback detection. [Loopback Detection]
- Added support for QinQ. [QinQ]
- Added MAC-based VLAN. [MAC VLAN]
- Added protocol-based VLAN. [Protocol VLAN]
- Added VLAN translation. [VLAN translation]
- Added untagged OUI mode for voice VLAN. [Voice VLAN]
- Added gateway priority when using DHCP to get VLAN IP address. [VLAN IP Interface]
- Added import/export IPSG binding table for IP Source Guard. [IP Source Guard]
- Added IPv6 Source Guard. [IPv6 Source Guard]
- Added MAC bypass authentication. [Identity Authentication Management]
- Added upgrade by FTP and Explicit FTPS. [FTP] [Explicit FTPS]
- Added DST mode for time settings. [DST]
- Added HTTPS/SSH port customization. [Web Service Management]
- Added GWN Manager takeover function. [Management Platform Settings]
- Optimized DHCP option 43 settings for DHCP server. [DHCP Server]
- Optimized routing table. [Routing Forwarding]
- Added port scheduled enabling feature. [Scheduled enabled]
- Added DHCPv6 Snooping. [DHCPv6 Snooping]
- Optimized CPU and memory usage in Web GUI. [System Info]
- Optimized search for Web GUI. [Search]
Product Name: GWN7811(P)/GWN7812P/GWN7813(P)
- Added port groups. [Port Group]
- Added LLDP-based automatic configuration for Auto Voice VLAN mode.
- Added more features for STP, including ignore VLAN in BPDU, root protection and loopback protection. [Ignore VLAN in BPDU] [Root Protection] [Loop Protection]
- Added more OUI in Voice VLAN. [OUI]
- Added IP configuration for MGMT VLAN. [MGMT VLAN]
- Added redirect to interface for ACL. [Redirect to Interface]
- Added VLAN binding to ACL function.[VLAN Binding to ACL]
- Optimized the rate limit groups from 32 to128 in ACL. [Rate Limit Settings]
- Added mask for IPSG/IPv6SG. [IP Source Guard]
- Added remote-ID configuration based on port for DHCP Snooping. [DHCP Option 82]
- Changed DHCP’s Option 82 Circuit ID/Remote ID. [DHCP Option 82]
- Added entries fixed for DHCP/DHCPv6 Snooping. [DHCP Snooping]
- Added flow upgrade via manual upgrade. [Upgrade Flow]
- Added more settings for logs, including minimum log level and log aggregation. [Log Aggregation]
- Added Ping watchdog in diagnostics. [Ping Watchdog]
- Added connection diagnostics of GWN router. [GWN Router]
- Added RSPAN, including port-based and ACL-based remotely mirroring. [RSPAN] [Configuring an ACL based RSPAN]
- Added new SNMP Traps. [Trap Event]
- Added 802.3bt info in LLDP. [IEEE 802.3 TLV]
- Added Maintenance Alerts. [Alert]
- Added management ACL, including hardware-based and software-based management ACL. [Management ACL of Hardware-based] [Management ACL of Software-based]
- Added Layer 3 discovery and management by GWN router.[Management Platform Settings]
- Added ACL for VTY (SSH and telnet). [Web Service Management]
- Added additional Radius Access-Request Attributes. [Identity Authentication Management]
- Removed Commited Burst Configuration from Queue Shaping. [Queue Shaping]
Version 1.0.7.71
Product Name: GWN7811(P)/GWN7812P/GWN7813(P)
- Optimized search for Web GUI. [Search]
- Optimized CPU and memory usage in Web GUI. [System Info]
- Optimized device IP address display. [System Info]
- Added more port details such as neighbor, PoE power history info. [Port Info]
- Added port scheduled enabling feature. [Port Basic Settings]
- Added more port statistics info. [Port Statistics]
- Added loopback detection. [Loopback Detection]
- Added support for QinQ. [VLAN]
- Optimized trunk port settings. [VLAN Port Members]
- Added MAC-based VLAN. [MAC VLAN]
- Added protocol-based VLAN. [Protocol VLAN]
- Added VLAN translation. [VLAN Port Settings]
- Added default gateway configuration under MGMT VLAN. [VLAN IP Interface]
- Added gateway priority when using DHCP to get VLAN IP address. [VLAN IP Interface]
- Optimized DHCP option 43 configuration for DHCP server. [DHCP Server]
- Added advanced ACL settings, including mirroring, statistics, and priority remapping for a rule. [ACL]
- Added import/export IPSG binding table for IP Source Guard. [IP Source Guard]
- Added IPv6 Source Guard. [IPv6 Source Guard]
- Optimized remote ID and Circuit ID for DHCP Snooping. [DHCP Snooping option 82]
- Added DHCPv6 Snooping. [DHCPv6 Snooping]
- Added upgrade by FTP and Explicit FTPS. [Upgrade]
- Added connection diagnostics with GWN.Cloud/Manager. [Cloud/Manager Connection Diagnostics]
- Optimized EEE. [Energy Efficient Ethernet]
- Added DST mode for time settings. [Basic Settings]
- Added HTTPS/SSH port customization. [Web Service Management]
- Optimized Manager settings. [Manager Settings]
- Added rate limit by ACL binding to VLAN. [VLAN Binding to ACL]
- Added MAC bypass authentication. [Local User of MAC-based]
- Add GWN Manager takeover function [Manager Settings]
- Expanded DHCP leases range up to 11520 min. [DHCP Server]
- Added refresh IP address when using DHCP to get VLAN IP address. [VLAN IP Interface]
- Added support for OSPFv3. [OSPFv3]
- Added support for 12 VTY (SSH or telnet) sessions. [Access Control]
- Added support to see switch clients and other information. [Port Info]
Version 1.0.3.8
Product Name: GWN7816(P)
- This is the initial release.
Version 1.0.1.20
Product Name: GWN7811(P)/GWN7812P/GWN7813(P)
- Added support for GWN Cloud 1.1.25.23. [GWN.Cloud]
- Added support of SSH and TELNET in #mode. [Login Remotely using SSH]
- Added support of Auto Voice VLAN (Dynamic Voice VLAN). [Voice VLAN]
- Added support of voice VLAN OUI Untagged mode. [Voice VLAN]
- Added SNTP GWN Cloud interface. [Time Settings]
- Added support of EXEC CLI config commands by GWN Cloud. [GWN Cloud – Web CLI]
Version 1.0.1.8
Product Name: GWN7811(P)/GWN7812P/GWN7813(P)
- This is the initial release.